cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2505 articles

Threat Research · huntress.com

Researchers Demonstrate Data Exfiltration Using Splunk Universal Forwarder Configurations

A Huntress researcher demonstrated how custom Splunk Universal Forwarder configurations can route selected files to an attacker-controlled syslog server for exfiltration, and recommended controls to reduce the risk.
Apr 11, 2023
Threat Research · blog.talosintelligence.com

Typhon Reborn V2 Stealer Adds Anti-Analysis and Evasion Capabilities

Cisco Talos analyzes Typhon Reborn V2, an information stealer with expanded sandbox and VM evasion, broad data collection, and Telegram-based exfiltration. Samples were observed in the wild, and multiple purchases suggest future use in attacks.

Apr 4, 2023
Threat Research · huntress.com

Compromised 3CX Desktop Updates Delivered Malware Through a Multi-Stage Supply-Chain Attack

Huntress traced malicious 3CX DesktopApp updates for Windows and macOS through a multi-stage loader to encrypted payloads and command-and-control servers. DPRK attribution remained unconfirmed; users were urged to uninstall the client.

Mar 30, 2023
Threat Research · wiz.io

Wiz Researchers Show How Azure AD Misconfiguration Enabled Bing Content Changes and XSS

Wiz researchers found that poorly validated multi-tenant Azure AD apps exposed Microsoft applications, including Bing Trivia. They demonstrated search-result manipulation and an XSS attack that accessed Office 365 data from their test account.

Mar 29, 2023
Threat Research · blog.talosintelligence.com

Emotet Resumes Spam Campaign, Shifts from Word Documents to OneNote

Emotet resumed spam operations in March 2023, first using oversized Word documents to evade analysis, then switching to OneNote files that execute VBScript or JavaScript downloaders to install the malware.

Mar 22, 2023
Threat Research · blog.talosintelligence.com

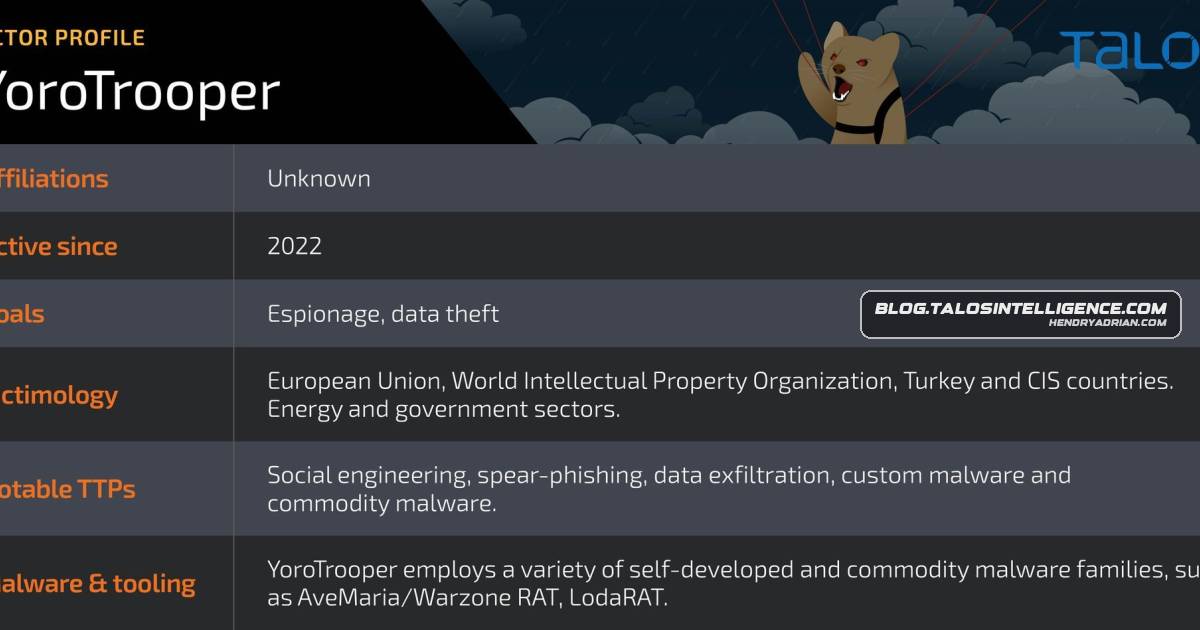
Talos Details YoroTrooper Espionage Campaigns Targeting CIS Governments, Embassies and EU Health Agency

Talos details YoroTrooper espionage campaigns active since June 2022, targeting CIS governments and other organizations. The actor used phishing, custom and commodity malware to steal credentials, browser data, screenshots and documents.

Mar 14, 2023
Threat Research · threatfabric.com

Xenomorph V3 Adds Automated Transfer Fraud and Targets More Than 400 Institutions

ThreatFabric analyzes Xenomorph.C, an Android banking trojan with an Accessibility-powered engine for automated transfers, MFA-code and cookie theft. A test configuration listed more than 400 banking and cryptocurrency targets.

Mar 10, 2023
Threat Research · blog.talosintelligence.com

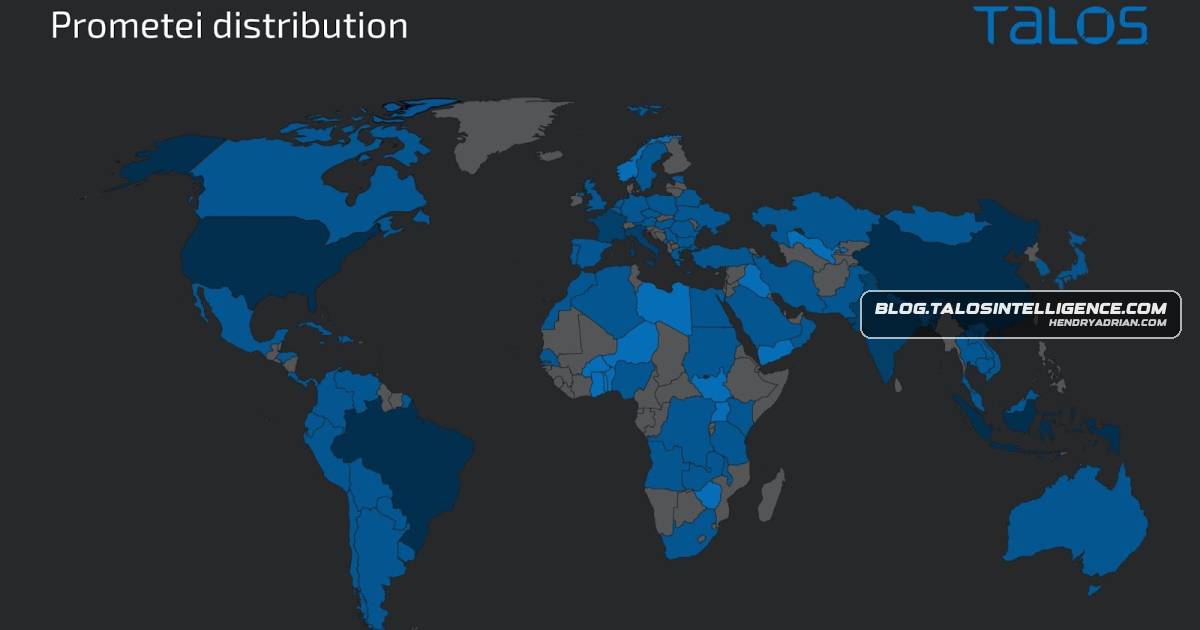
Prometei Botnet Adds Self-Updating, C2 and Web Shell Capabilities

Cisco Talos details Prometei v3 updates observed since November 2022, including a new domain-generation algorithm, self-updating mechanism and bundled web shell. Sinkhole data indicated more than 10,000 infected systems worldwide.

Mar 9, 2023
Threat Research · wiz.io

Wiz Details Campaign Hijacking Thousands of Websites to Redirect East Asian Visitors

Wiz researchers estimated that an unknown actor compromised at least 10,000 websites, mainly targeting East Asian audiences, and used injected JavaScript to redirect some visitors. The initial access method and the actor’s precise motives remain unknown.

Mar 2, 2023
Threat Research · blog.talosintelligence.com

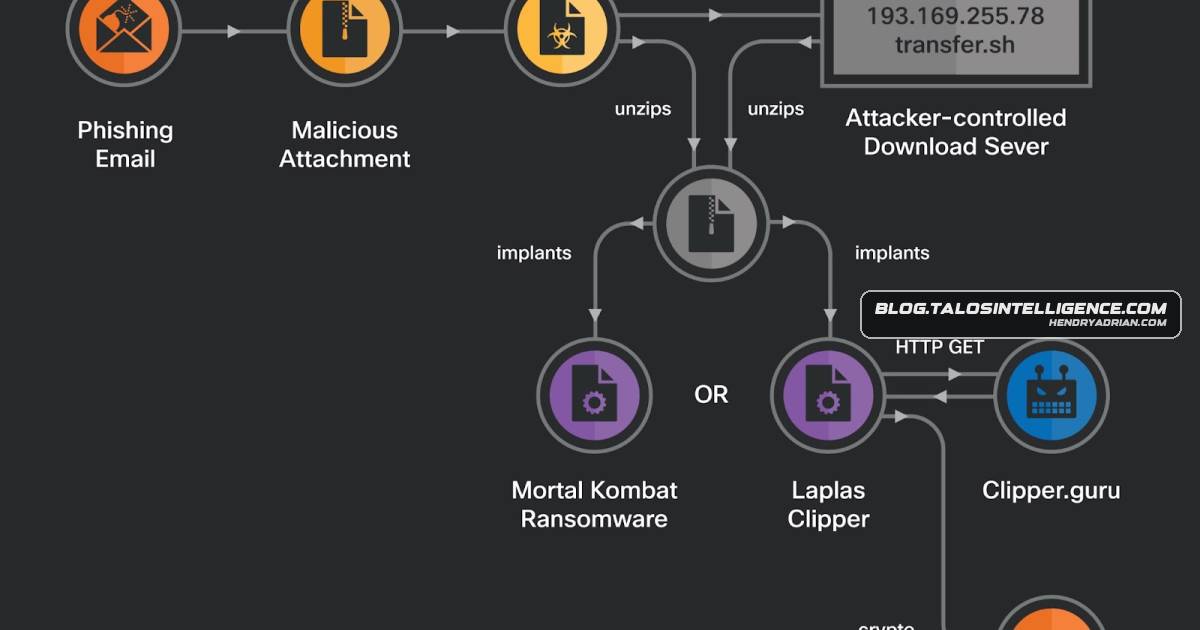
Talos Details MortalKombat Ransomware and Laplas Clipper Campaign

Talos says an unidentified actor used phishing emails and exposed RDP services to deploy MortalKombat ransomware or Laplas Clipper, stealing cryptocurrency. The report links MortalKombat to Xorist and analyzes both malware strains.

Feb 14, 2023
Threat Research · huntress.com

Huntress Investigates GoAnywhere MFT Intrusion and Finds Likely Truebot Malware

Huntress traced activity on two GoAnywhere MFT servers to likely exploitation of a zero-day vulnerability and a DLL resembling Truebot. The intrusion was contained before further activity, with a likely ransomware attempt assessed but not confirmed.

Feb 8, 2023
Threat Research · huntress.com

Huntress Traces Multi-Stage PowerShell Malware to a Cobalt Strike Beacon

Huntress analysts traced a phishing-delivered maldocx through PowerShell environment-variable persistence, encoded and encrypted scripts, and .NET/RunPE stages to a Cobalt Strike beacon running under Notepad.

Jan 31, 2023
Threat Research · blog.talosintelligence.com

Talos Uses LNK Metadata to Track Malware Campaigns and Link Threat Actors

Cisco Talos analyzed LNK file metadata to track Qakbot and Gamaredon activity and link Bumblebee with IcedID and Qakbot, showing how metadata can reveal campaign relationships and help defenders improve detection.

Jan 19, 2023
Threat Research · threatfabric.com

Hook Android Malware Adds Remote Control, File Access and Spyware Features

ThreatFabric analyzes Hook, an Ermac-based Android banking malware linked to its original author, DukeEugene. It adds remote device control, file access, messaging and location surveillance, alongside banking-fraud capabilities.

Jan 19, 2023
Threat Research · huntress.com

Huntress Analyzes OWASSRF Microsoft Exchange Exploit Chain and Its Post-Exploitation Activity

Huntress analyzed OWASSRF, a Microsoft Exchange exploit chain involving CVE-2022-41080 and CVE-2022-41082. It demonstrated SYSTEM-level code execution using unprivileged OWA credentials and reported observed post-exploitation activity and detections.

Dec 29, 2022
Threat Research · blog.talosintelligence.com

Threat Actors Increasingly Use Malicious Excel XLL Add-Ins to Deliver Malware

Cisco Talos traces malicious Excel XLL add-ins from early use in 2017 to wider adoption by APT groups and commodity malware, detailing how they execute code and deliver payloads as VBA macro protections expand.

Dec 20, 2022
Threat Research · huntress.com

Shodan Images Reveal Ransomware Activity on Exposed VNC Systems

Huntress researchers used Shodan images to examine exposed, unauthenticated VNC systems, finding attempted GandCrab/REvil payload delivery using PowerShell, bitsadmin and FTP, plus a separate unidentified campaign.

Dec 20, 2022
Threat Research · huntress.com

Huntress Details Host-Header Technique for Running Code Through ConnectWise Control

Huntress found that Host-header manipulation could make a signed ConnectWise Control installer fetch and run a separate ClickOnce application on on-premises systems. The technique requires user approval and social engineering; cloud instances are not affected.

Dec 14, 2022
Threat Research · wiz.io

Wiz Details IBM Cloud PostgreSQL Flaw That Could Enable a Supply-Chain Attack

Wiz disclosed a PostgreSQL privilege-escalation and exposed-credentials chain in IBM Cloud Databases that enabled access to internal build repositories and a potential supply-chain attack path. IBM patched the issues; it reported no indication of further exploitation.

Dec 1, 2022
Threat Research · blog.talosintelligence.com

LodaRAT Variants Add Removable-Drive Propagation and Appear Alongside Other Malware

Cisco Talos analyzes altered LodaRAT variants, including removable-drive propagation and changed string decoding, and reports deployments alongside S500, RedLine and Neshta.

Nov 17, 2022
Threat Research · blog.talosintelligence.com

Talos Details Phishing and Malware Campaigns Abusing IPFS

Cisco Talos analyzes phishing and malware campaigns using IPFS to host credential-harvesting pages and payloads, including Agent Tesla, reverse shells, destructive malware, and the Hannabi information stealer.

Nov 9, 2022
Threat Research · huntress.com

Huntress Makes a macOS Ransomware Script Operational in a Test

Huntress modified and tested a circulating macOS ransomware script, which creates an encrypted APFS drive, moves files onto it and sends the decryption password to an attacker-controlled machine. The script was last known to work on macOS Monterey.

Nov 8, 2022
Threat Research · huntress.com

Huntress Details R1Soft CVE-2022-36537 Exploit Chain Enabling Root RCE

Huntress researchers chained CVE-2022-36537’s ZK authentication bypass in R1Soft Server Backup Manager SE to root-level RCE and code execution on managed agents. A Feb. 2023 update, citing Fox-IT and SecurityWeek, reports exploitation on hundreds of servers.

Oct 31, 2022
Threat Research · wiz.io

Wiz Finds OCI Flaw That Allowed Unauthorized Cross-Tenant Storage Access

Wiz found that attackers who knew a volume’s OCID could attach some OCI storage volumes to instances in another tenant, enabling unauthorized read/write access. Oracle fixed the flaw within 24 hours of being notified; no customer action was required.

Sep 20, 2022
PreviousPage 102 of 105 Next
© 2026 cyber.hendryadrian.com