Threat Actors Increasingly Use Malicious Excel XLL Add-Ins to Deliver Malware
Summary
Cisco Talos traces malicious Excel XLL add-ins from early use in 2017 to wider adoption by APT groups and commodity malware, detailing how they execute code and deliver payloads as VBA macro protections expand.
Key points
- XLL files are Windows DLLs that Excel loads as add-ins; functions such as xlAutoOpen can run code when an add-in loads.
- Talos found malicious XLL use beginning in 2017, with adoption rising notably from late 2021 as commodity malware families began using the technique.
- APT10, TA410, DoNot and FIN7 are among the actors linked to XLLs; observed malware includes Dridex, FormBook, Warzone and Ducktail.
- Some XLLs arrive as email attachments or lures and download or load additional malware; Excel-DNA lets developers build .NET-based XLLs.
- Talos describes VirusTotal search methods and YARA rules for hunting native and Excel-DNA-based XLL files.
- Blocking VBA macros in downloaded Office documents does not prevent XLL-based code execution; Talos recommends its security products and provides applicable Snort SIDs and ClamAV signatures.
Article Details
- Attack Vectors
- Malicious XLL add-ins are delivered as email attachments; opening an XLL causes Excel to load and execute its code.
- XLL add-ins use xlAutoOpen, xlAutoClose, or other exported functions to run code when Excel loads the add-in or handles an event.
- FIN7 used XLL email attachments as downloaders for additional components.
- A Warzone campaign used an XLL attachment in an email impersonating the Hungarian police.
- A Ducktail XLL decoded and decrypted an embedded Base32 data blob, loaded it into Explorer through reflection, then downloaded the stealer payload from Discord.
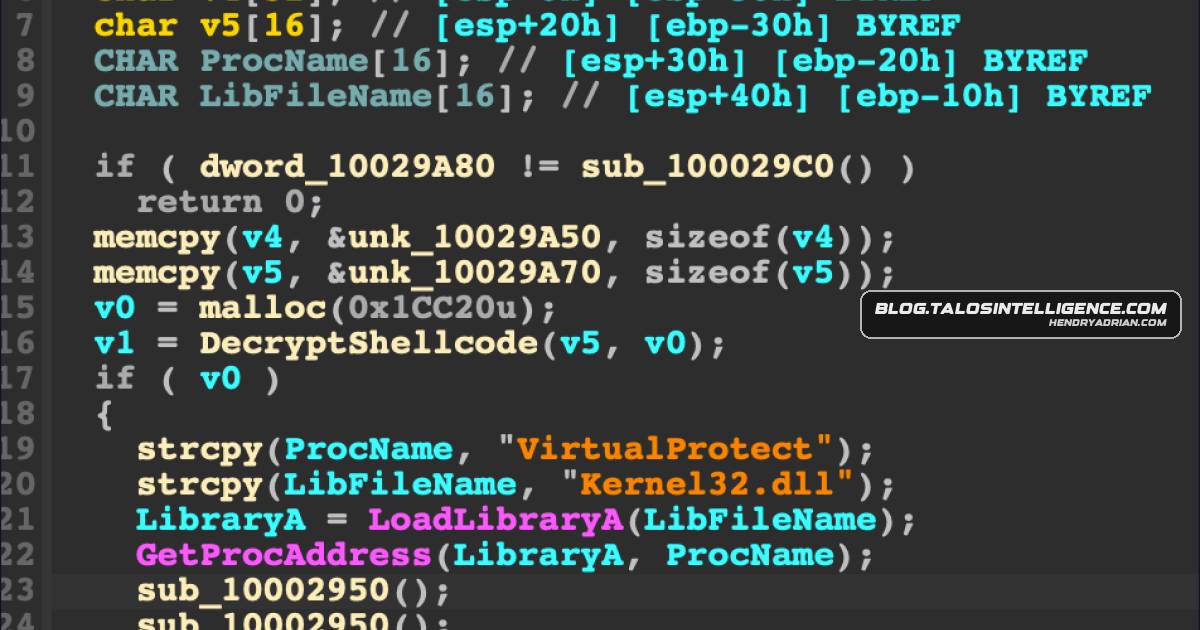
- XLL samples used process injection, including an APT10 sample that injected Anel into svchost.exe.
- The article reports that FormBook can record keystrokes, steal locally stored and web-form passwords, and take screenshots.
- Defensive Notes
- Microsoft began rolling out Office versions that block VBA macros by default in documents marked as downloaded from the internet, but this does not prevent malicious XLL add-ins.
- The article warns that users may disregard Excel's warning about potentially malicious XLL code.
- Cisco lists endpoint, email, firewall, network analytics, malware analysis, web, and DNS-security products as available protections for the described threat.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 09271afc6f7ac254b4942a14559a0015fb4893d9bb478844ced2f78c0695929e | XLL test sample used to launch calc.exe. |
| SHA256 | 55228eec31193a900e8216ab245391f1e40feb742d780caa91fdb1000d8434c2 | FormBook XLL downloader delivered as an email attachment. |
| SHA256 | 7a234d1a2415834290a3a9c7274aadb7253dcfe24edb10b22f1a4a33fd027a08 | FIN7 XLL attachment used as a downloader for the next stage. |
| SHA256 | 90205826eb40d5d4b454c2cfde44abe49f6c3b471681c700e30b45eb5078eee2 | Warzone payload hosted at the URL used by the XLL downloader. |
| SHA256 | 9dd2425c1a40b8899b2a4ac0a85b047bede642c5dfd3b5a2a2f066a853b49e2d | TA410 process-injection DLL identified as an XLL-stage component. |
| SHA256 | a5d46912f0767ae30bc169a85c5bcb309d93c3802a2e32e04165fa25740afac1 | APT10-associated XLL sample that injects the Anel backdoor payload into svchost.exe. |
| SHA256 | d7c3dd8bc55649b2a77dc921e70f5f208946f64aedfdaabd7b02a247669a73aa | Ducktail XLL downloader containing an encoded and encrypted data blob. |
| SHA256 | d8286133d3d21b7e2b83a6c071147b8ef993e963ad6bdb0f95d665869557a444 | DoNot-associated DLL named 1.xll, identified as a native-based XLL payload. |
| SHA256 | f2c5327b7bf88c65d0552d8664aca2ac542c8d37ae19582ba56690f1df420b53 | Dridex XLL downloader. |
| SHA256 | f5c27b7bdea3861a9414a0dc6b08556ea50423d63297e08eedff69ae9c240cae | Warzone XLL attachment that downloads the payload. |
| SHA256 | fdfdfc8878f39424920d469bcd05060a6f7c95794aaa2422941913553d3dd01f | Meterpreter reverse-shell XLL sample. |
| URL | hxxp[:]//172[.]245[.]120[.]8/pdfreader[.]exe | URL used by the Warzone XLL to download the payload; the article says it hosted Warzone and later AgentTesla and Lokibot samples. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe Ducktail downloader contains a Base32-encoded, AES-encrypted data blob that it decodes and loads.T1055 · Process InjectionAn APT10-associated XLL injects Anel into svchost.exe; the Ducktail downloader also loads its decoded blob into Explorer's process space.T1056.001 · KeyloggingThe article says FormBook samples can record keystrokes.T1059.001 · PowerShellThe article states that FIN7 uses PowerShell among its infection techniques.T1105 · Ingress Tool TransferXLL downloaders retrieve additional malware, including Warzone from the stated URL and Ducktail from a publicly accessible Discord URL.T1113 · Screen CaptureThe article says FormBook samples can take screenshots.T1204.002 · Malicious FileUsers open emailed XLL attachments, causing Excel to load and execute the malicious add-in.T1539 · Steal Web Session CookieDucktail attempts to steal browser-stored cookies.T1555.003 · Credentials from Web BrowsersThe article says FormBook can steal passwords stored locally and in web forms.T1566.001 · Spearphishing AttachmentFIN7 and the Warzone campaign delivered malicious XLL files as email attachments.
People
Threat Actors
APT10The article lists menuPass, Chessmaster, and Potassium as alternative names; it associates APT10 with an XLL sample that injects Anel into svchost.exe.ChessmasterListed in the article as an alternative name for APT10.DoNotThe article describes the DoNot team as targeting Kashmiri non-profit organizations and Pakistani government officials and identifies a DoNot-associated XLL payload.FIN7Financially motivated group that the article says used XLL email attachments as downloaders.menuPassListed in the article as an alternative name for APT10.PotassiumListed in the article as an alternative name for APT10.TA410Cyberespionage group associated in the article with an XLL-stage component.
Malware
AgentTeslafamilies that use XLLs as the infection vector and are not specifically described in this post include AgentTesla, Ransomware Stop, Vidar, Buer Loader, Nanocore, IceID, Arkei, AsyncRat, BazarLoader and others.Anelwas submitted to VirusTotal in December 2017 and it contains functionality to inject the Backdoor Anel payload into the process space of svchost.exe.Arkeidescribed in this post include AgentTesla, Ransomware Stop, Vidar, Buer Loader, Nanocore, IceID, Arkei, AsyncRat, BazarLoader and others.AsyncRATdescribed in this post include AgentTesla, Ransomware Stop, Vidar, Buer Loader, Nanocore, IceID, Arkei, AsyncRat, BazarLoader and others.AveMariaWarzone (Avemaria) RATBazarLoaderthis post include AgentTesla, Ransomware Stop, Vidar, Buer Loader, Nanocore, IceID, Arkei, AsyncRat, BazarLoader and others.Buer Loadervector and are not specifically described in this post include AgentTesla, Ransomware Stop, Vidar, Buer Loader, Nanocore, IceID, Arkei, AsyncRat, BazarLoader and others.CarbanakPowerShell. The main goal of FIN7 is obtaining financial gain for the group. FIN7 most commonly uses Carbanak malware.CerbuWin.Malware.Cerbu-9980304-0DridexFor quite some time after that, the usage of XLL files is only sporadic and it does not increase significantly until the end of 2021, when commodity malware families such as Dridex and Formbook started using it.DuckTailDucktail is an information stealer malware targeting users in the digital advertising sector, attributed to a threat actor operating in Vietnam. Ducktail attempts to steal browser stored credentials and cookies with theFormBookFor quite some time after that, the usage of XLL files is only sporadic and it does not increase significantly until the end of 2021, when commodity malware families such as Dridex and Formbook started using it.IceIDspecifically described in this post include AgentTesla, Ransomware Stop, Vidar, Buer Loader, Nanocore, IceID, Arkei, AsyncRat, BazarLoader and others.KoobickWin.Malware.Koobick-9980509-0LokiBotAt the time of analysis, the URL hosted the Warzone payload 90205826eb40d5d4b454c2cfde44abe49f6c3b471681c700e30b45eb5078eee2, and later hosted samples of AgentTesla and Lokibot.MeterpreterIn the same month, a Meterpreter reverse shell sample, fdfdfc8878f39424920d469bcd05060a6f7c95794aaa2422941913553d3dd01f, was submitted.NanoCoreand are not specifically described in this post include AgentTesla, Ransomware Stop, Vidar, Buer Loader, Nanocore, IceID, Arkei, AsyncRat, BazarLoader and others.StopUnfortunately, it would be naive to assume that Office will stop being targeted, now that VBA macros have been blocked.Vidarthe infection vector and are not specifically described in this post include AgentTesla, Ransomware Stop, Vidar, Buer Loader, Nanocore, IceID, Arkei, AsyncRat, BazarLoader and others.WarzoneWarzone (Avemaria) RATZusyWin.Malware.Zusy-9980503-0
Vendors
Products
Cisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network.Cisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign.Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post.Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Cisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.Cisco Secure Network/Cloud AnalyticsCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device.Cisco Secure Web ApplianceCisco Secure Web Appliance (formerly Web Security Appliance) automatically blocks potentially dangerous sites and tests suspicious sites before users access them.ClamAVThe following ClamAV signatures are applicable to this threat:ExcelThreat Spotlight: XLLing in Excel - threat actors using malicious add-insMicrosoft OfficeFor decades, Microsoft Office applications have served as one of the most significant entry points for malicious code.SecureXSecureXSnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.UmbrellaTA410 is a cyberespionage umbrella group loosely linked to APT10, known mostly for targeting US-based organizations in the utilities sector, and diplomatic organizations in the Middle East and Africa. TA410 has been
Tools
Excel-DNAExcel-DNA based XLLsMicrosoft Excel XLL SDKPowerShellFIN7 is using a number of payloads and different infection techniques, including .NET assemblies and PowerShell. The main goal of FIN7 is obtaining financial gain for the group. FIN7 most commonly uses CarbanakVirusTotalHunting for XLLs in VirusTotalYARAThe searches can easily be converted into YARA rules for hunting:
Countries
ChinaAPT10 is a threat group originating in China with specific interest in the education, manufacturing and pharmaceutical sectors. The group is known to target organizations in Japan and other countries. It has been activeHungaryJapanin the education, manufacturing and pharmaceutical sectors. The group is known to target organizations in Japan and other countries. It has been active from at least the beginning of 2017. PakistanPakistani government officials. The region of Kashmir is under ongoing disputes from India, China and Pakistan about its ownership. The DoNot team has used mobile implants as well as some custom desktop payloadsUnited StatesVietnammalware targeting users in the digital advertising sector, attributed to a threat actor operating in Vietnam. Ducktail attempts to steal browser stored credentials and cookies with the specific intent to steal the
Industries
digital advertisingDucktail is an information stealer malware targeting users in the digital advertising sector, attributed to a threat actor operating in Vietnam. Ducktail attempts to steal browser stored credentials and cookies with theDiplomatic organizationslinked to APT10, known mostly for targeting US-based organizations in the utilities sector, and diplomatic organizations in the Middle East and Africa. TA410 has been active since at least 2018 and was first publiclyEducationAPT10 is a threat group originating in China with specific interest in the education, manufacturing and pharmaceutical sectors. The group is known to target organizations in Japan and other countries. It has been activeGovernmentThe DoNot team is known for targeting Kashmiri non-profit organizations and Pakistani government officials. The region of Kashmir is under ongoing disputes from India, China and Pakistan about its ownership. The DoNotManufacturingAPT10 is a threat group originating in China with specific interest in the education, manufacturing and pharmaceutical sectors. The group is known to target organizations in Japan and other countries. It has been activePharmaceuticalsUtilitiesumbrella group loosely linked to APT10, known mostly for targeting US-based organizations in the utilities sector, and diplomatic organizations in the Middle East and Africa. TA410 has been active since at least