Talos Details MortalKombat Ransomware and Laplas Clipper Campaign
Summary
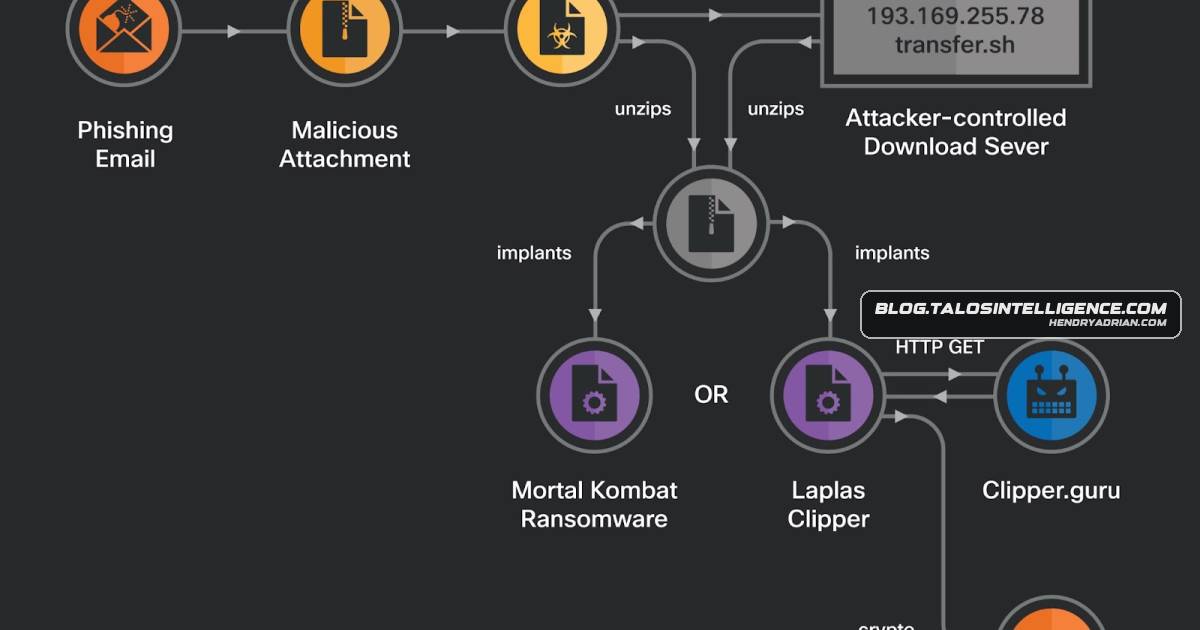
Talos says an unidentified actor used phishing emails and exposed RDP services to deploy MortalKombat ransomware or Laplas Clipper, stealing cryptocurrency. The report links MortalKombat to Xorist and analyzes both malware strains.
Key points
- The campaign targets individuals and organizations; Talos observed victims mainly in the United States, with others in the United Kingdom, Turkey, and the Philippines.
- Phishing emails carry ZIP attachments containing a BAT loader. The loader uses bitsadmin to download and run either payload, then deletes the downloaded and dropped files.
- Talos observed the actor scanning for machines with exposed RDP on port 3389 using a server that also facilitates ransomware delivery.
- MortalKombat encrypts files on local and mapped drives, alters the victim’s desktop, and disrupts some Windows functions. Talos assesses with high confidence that it belongs to the Xorist family.
- Laplas Clipper monitors the clipboard for cryptocurrency wallet addresses and replaces a detected address with an attacker-controlled lookalike, potentially redirecting transactions.
- Laplas establishes persistence with a scheduled task that runs every minute. Talos recommends checking wallet addresses carefully, applying security updates, using endpoint protection, and keeping tested offline backups.
Article Details
- Attack Vectors
- Phishing emails impersonating CoinPayments carried ZIP attachments containing a BAT loader.
- The BAT loader used bitsadmin to download a ZIP file from an attacker-controlled server, extracted it, and executed either Laplas Clipper or MortalKombat.
- The actor scanned for victim machines with exposed RDP port 3389.
- Laplas Clipper monitored victims’ clipboard for cryptocurrency wallet addresses and replaced detected addresses with attacker-controlled lookalikes.
- Defensive Notes
- Talos recommends verifying cryptocurrency wallet addresses before transactions.
- Talos recommends installing the latest security updates, using endpoint protection with behavioral detection, and maintaining tested offline backups.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | clipper[.]guru | Attacker-controlled Clipper bot domain used for command-and-control and wallet-address exchange. |
| DOMAIN | laplas[.]app | Site identified as offering Laplas Clipper malware for purchase. |
| IPV4 | 193[.]169[.]255[.]78 | Attacker-controlled download server used to deliver MortalKombat; Talos observed it running an RDP crawler. |
MITRE ATT&CK
T1012 · Query RegistryMortalKombat modifies registry entries and removes installed-application registry keys.T1048.003 · Exfiltration Over Unencrypted Non-C2 ProtocolLaplas Clipper sends clipboard wallet addresses to its bot over HTTP GET requests.T1059 · Command and Scripting InterpreterThe campaign’s BAT loader and command-line commands execute and manage the malware.T1060 · Registry Run Keys / Startup FolderMortalKombat creates a Run registry key named Alcmeter for persistence.T1064 · ScriptingThe BAT loader and embedded VB script perform malware download and extraction.T1082 · System Information DiscoveryLaplas Clipper registers the victim machine by sending its desktop name and user ID to its bot.T1083 · File and Directory DiscoveryMortalKombat recursively searches victim drives and folders for files to encrypt.T1106 · Native APIMortalKombat uses the RegDeletekeyA API while deleting registry keys during cleanup.T1112 · Modify RegistryMortalKombat creates and deletes registry keys, including persistence and file-association keys.T1120 · Peripheral Device DiscoveryThe article lists this technique among the campaign’s observed techniques but provides no specific behavior in its technical description.T1197 · BITS JobsThe BAT loader uses bitsadmin to download a malicious ZIP file.T1486 · Data Encrypted for ImpactMortalKombat encrypts files on victim machines and appends a new extension to encrypted files.
Malware
Laplas ClipperNew MortalKombat ransomware and Laplas Clipper malware threats deployed in financially motivated campaignMortalKombatNew MortalKombat ransomware and Laplas Clipper malware threats deployed in financially motivated campaignXoristBased on Talos’ analysis of similarities in code, class name, and registry key strings, we assess with high confidence that the MortalKombat ransomware belongs to the Xorist family.
Vendors
Products
Cisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network.Cisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here.Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Cisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.Cisco Secure Web ApplianceCisco Secure Web Appliance web scanning prevents access to malicious websites and detects malware used in these attacks.ClamAVClamAV detections are also available for this threat:qToxThe attacker uses qTOX, an instant messaging application available on the GitHub repository, to communicate with the victim. qTOX’s developer claims the application offers users a secure channel without any monitoring,Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here.SnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org. Snort SIDs for this threat are 61261-61265, 300397.UmbrellaUmbrella, Cisco's secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network. Sign up for a free trial of Umbrella here.
Tools
Countries
PhilippinesTalos observed that victims of this campaign are predominantly located in the United States, with a smaller percentage of victims in the United Kingdom, Turkey, and the Philippines.Polandcampaign. One of them reaches an attacker-controlled server via IP address 193[.]169[.]255[.]78, based in Poland, to download the MortalKombat ransomware. According to Talos’ analysis, 193[.]169[.]255[.]78 is runningTurkeyTalos observed that victims of this campaign are predominantly located in the United States, with a smaller percentage of victims in the United Kingdom, Turkey, and the Philippines.United KingdomTalos observed that victims of this campaign are predominantly located in the United States, with a smaller percentage of victims in the United Kingdom, Turkey, and the Philippines.United StatesTalos observed that victims of this campaign are predominantly located in the United States, with a smaller percentage of victims in the United Kingdom, Turkey, and the Philippines.