Talos Details YoroTrooper Espionage Campaigns Targeting CIS Governments, Embassies and EU Health Agency
Summary
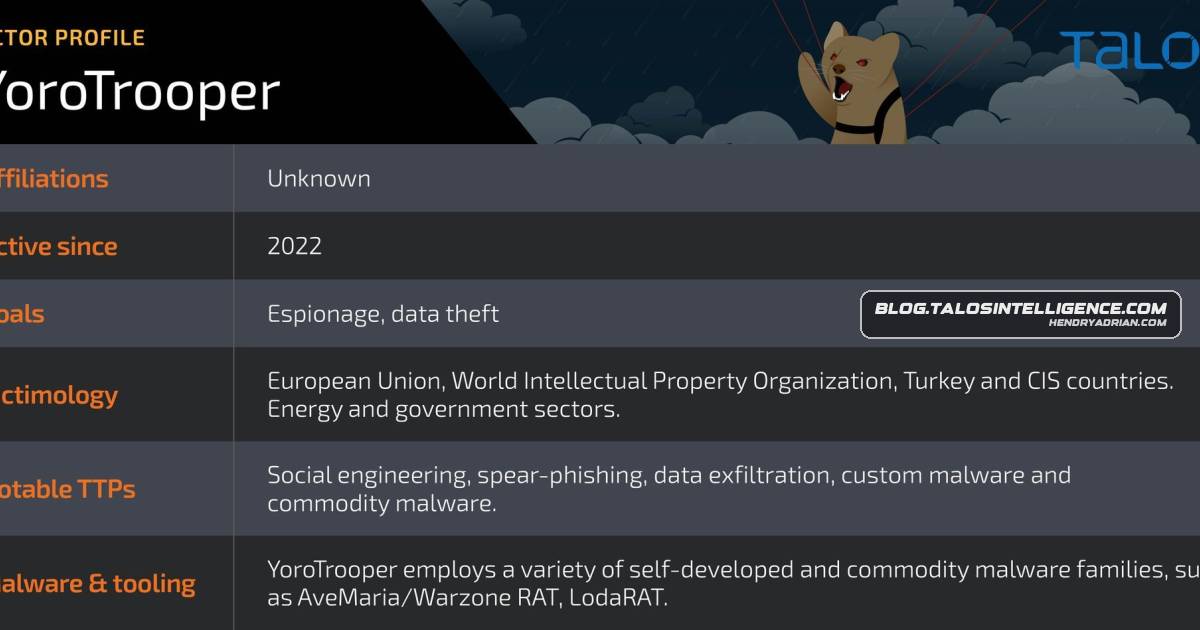
Talos details YoroTrooper espionage campaigns active since June 2022, targeting CIS governments and other organizations. The actor used phishing, custom and commodity malware to steal credentials, browser data, screenshots and documents.
Key points
- Talos links three activity clusters to YoroTrooper, which has targeted governments and energy organizations across CIS countries, as well as embassies and international organizations.
- Talos found stolen credentials from accounts at an EU health care agency and WIPO, and reports compromised embassies of Azerbaijan and Turkmenistan.
- Phishing emails delivered RAR or ZIP archives containing malicious LNK shortcuts, sometimes with decoy documents. Shortcuts launched HTA downloaders and subsequent payloads.
- The toolset included custom Python stealers and RATs, Stink stealer, AveMaria/Warzone RAT, LodaRAT and Meterpreter; some implants used Telegram bots for commands or data exfiltration.
- Stolen information included application credentials, browser histories and cookies, screenshots, system details and documents.
- Talos assesses the actor may be Russian-speaking but found insufficient evidence to link YoroTrooper to the PoetRAT team; LodaRAT use alone does not establish attribution to Kasablanka.
Article Details
- Attack Vectors
- Phishing emails deliver malicious archives containing LNK shortcut files and, sometimes, decoy documents.
- LNK files use mshta.exe to download and execute remote HTA files; HTAs use PowerShell commands to retrieve and run subsequent payloads.
- Typo-squatted and attacker-registered domains host malicious artifacts and imitate legitimate CIS government and organization domains.
- Some campaigns use VHDX files containing archives and LNKs, or LNK files that download implants directly using curl.
- Payloads include credential stealers, RATs, reverse shells, and a keylogger.
- Defensive Notes
- The article recommends blocking malicious emails, websites, domains, IPs, and URLs, and detecting or blocking the associated malware and activity using Cisco security products and Snort rules.
- Cisco Duo multi-factor authentication is cited as a measure to help ensure only authorized users access the network.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | account[.]nail[.]ru[.]inro[.]link | Malicious subdomain masquerading as a Russian entity in the September 2022 campaign. |
| DOMAIN | akipress[.]news | Typosquatted malicious domain used to imitate AKI Press News Agency. |
| DOMAIN | belaes[.]by[.]authentication[.]becloud[.]cc | Malicious subdomain identified as attacker infrastructure impersonating Belarusian Nuclear Power Plant. |
| DOMAIN | belstat[.]gov[.]by[.]attachment-posts[.]cc | Malicious subdomain identified as attacker infrastructure impersonating Belarus’s National Statistical Committee. |
| DOMAIN | industry[.]tj[.]mypolicy[.]top | Malicious subdomain identified as attacker-registered infrastructure impersonating Tajikistan’s Ministry of Industry and New Technologies. |
| DOMAIN | mail[.]belaes[.]by[.]authentication[.]becloud[.]cc | Malicious domain masquerading as a Belarusian domain in the October 2022 campaign. |
| DOMAIN | mail[.]hse[.]ru[.]attachment-posts[.]cc | Malicious subdomain masquerading as a Russian domain in the August 2022 campaign. |
| DOMAIN | mail[.]mfa[.]az-link[.]email | Malicious domain used in the campaign to impersonate Azerbaijan’s Ministry of Foreign Affairs. |
| DOMAIN | mail[.]mfa[.]gov[.]kg[.]openingfile[.]net | Malicious subdomain identified as attacker-registered infrastructure impersonating Kyrgyzstan’s Ministry of Foreign Affairs. |
| DOMAIN | maileecommission[.]inro[.]link | Malicious domain impersonating European Commission email infrastructure. |
| DOMAIN | minsk[.]gov[.]by[.]attachment-posts[.]cc | Malicious subdomain identified as attacker infrastructure impersonating the Government of Minsk. |
| DOMAIN | rnail[.]iterrf[.]ru[.]inro[.]link | Malicious subdomain masquerading as a Russian government entity in the September 2022 campaign. |
| DOMAIN | rnail[.]mintrans[.]gov[.]ru[.]inro[.]link | Malicious subdomain masquerading as a Russian government entity in the September 2022 campaign. |
| DOMAIN | rnail[.]rnid[.]ru[.]inro[.]link | Malicious subdomain masquerading as a Russian government entity in the September 2022 campaign. |
| DOMAIN | sts[.]mfa[.]gov[.]tr[.]mypolicy[.]top | Malicious subdomain identified as attacker-registered infrastructure impersonating Turkey’s Ministry of Foreign Affairs. |
| DOMAIN | true[.]az-link[.]email | Malicious domain used in the campaign targeting Azerbaijan. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelCustom implants and stealers exfiltrate collected information through Telegram bots.T1056.001 · KeyloggingA custom C-based keylogger records keystrokes and saves them to a file.T1059.001 · PowerShellHTA files run PowerShell-based commands to download and execute later payloads.T1059.003 · Windows Command ShellLNK files use curl to download implants directly in the September 2022 campaign.T1071.001 · Web ProtocolsCustom implants and the Stink stealer use Telegram bots to communicate with operators and exfiltrate information.T1204.002 · Malicious FileThe infection chain is triggered when a target opens a malicious LNK shortcut contained in an archive.T1218.005 · MshtaLNK downloaders use mshta.exe to download and execute remote HTA files.T1547.001 · Registry Run Keys / Startup FolderStink Stealer 2.1.1 can create a link in the victim profile’s startup folder for autostart.T1566.001 · Spearphishing AttachmentPhishing emails deliver archives containing malicious shortcut files and decoy documents to targets.
People
Threat Actors
KasablankaThreat actor that Talos attributes with developing LodaRAT; the article says Kasablanka is not the sole operator of LodaRAT.PoetRAT teamThreat actor team previously observed by Talos compromising Azerbaijan embassies and government agencies; the article notes similarities with YoroTrooper but no concrete link.YoroTrooperActor named by Cisco Talos as responsible for espionage campaigns targeting CIS countries and other organizations since at least June 2022.
Malware
AveMariaFor remote access, YoroTrooper has also deployed commodity malware, such as AveMaria/Warzone RAT, LodaRAT and Meterpreter.LodaRATFor remote access, YoroTrooper has also deployed commodity malware, such as AveMaria/Warzone RAT, LodaRAT and Meterpreter.MeterpreterFor remote access, YoroTrooper has also deployed commodity malware, such as AveMaria/Warzone RAT, LodaRAT and Meterpreter.PoetRATThe overlaps with the PoetRAT team are stronger, especially on non-technical aspects of the campaigns but there are not enough for us to link them even with a low confidence level. Cisco Talos discovered the PoetRATRedLineby Yoro Trooper are based on versions we’ve seen being deployed in other crimeware campaigns alongside RedLine and VenomRAT, indicating LodaRAT’s availability to multiple threat actors.StinkYoroTrooper’s main tools include Python-based, custom-built and open-source information stealers, such as the Stink stealer wrapped into executables via the Nuitka framework and PyInstaller.VenomRATare based on versions we’ve seen being deployed in other crimeware campaigns alongside RedLine and VenomRAT, indicating LodaRAT’s availability to multiple threat actors.Warzone RATFor remote access, YoroTrooper has also deployed commodity malware, such as AveMaria/Warzone RAT, LodaRAT and Meterpreter.
Vendors
Products
Cisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network.Cisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here.Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here.Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Cisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.Cisco Secure Web ApplianceCisco Secure Web Appliance web scanning prevents access to malicious websites and detects malware used in these attacks.DiscordIt harvests Filezilla credentials and authentication cookies from Discord and Telegram.FileZillaIt harvests Filezilla credentials and authentication cookies from Discord and Telegram.Google ChromeCustom Python-based information stealers: Custom scripts for stealing Google Chrome browser credentials.NuitkaYoroTrooper’s main tools include Python-based, custom-built and open-source information stealers, such as the Stink stealer wrapped into executables via the Nuitka framework and PyInstaller.PyInstallerYoroTrooper’s main tools include Python-based, custom-built and open-source information stealers, such as the Stink stealer wrapped into executables via the Nuitka framework and PyInstaller.SnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.TelegramThe custom implants (stealers and RATs) use Telegram bots to exfiltrate information or receive commands from the operator.UmbrellaUmbrella, Cisco's secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network. Sign up for a free trial of Umbrella here.
Tools
curl• No HTAs employed - LNKs download .NET based implants directly using curl.LaZagneCredential stealers used by YoroTrooper are either custom scripts, which in some cases are based on the open-sourced Lazagne project or commodity stealers such as the Stink Stealer.mshta.exeThe malicious LNK files are simple downloaders that employ mshta.exe to download and execute a remote HTA file on the infected endpoint.
Countries
AzerbaijanYoroTrooper’s main targets are government or energy organizations in Azerbaijan, Tajikistan, Kyrgyzstan and other Commonwealth of Independent States (CIS), based on our analysis.BelarusNational Statistical Committee of BelarusKyrgyzstanYoroTrooper’s main targets are government or energy organizations in Azerbaijan, Tajikistan, Kyrgyzstan and other Commonwealth of Independent States (CIS), based on our analysis.Russiais that the operators of this threat actor are Russian language speakers, but not necessarily living in Russia or Russian nationals since their victimology consists mostly of countries in the Commonwealth ofTajikistanYoroTrooper’s main targets are government or energy organizations in Azerbaijan, Tajikistan, Kyrgyzstan and other Commonwealth of Independent States (CIS), based on our analysis.TürkiyeWe assess the actor also likely targets other organizations across Europe and Turkish (Türkiye) government agencies.TurkmenistanSuccessful compromises also included Embassies of European countries including Azerbaijan and Turkmenistan.UzbekistanUzbekistan
Industries
EnergyYoroTrooper’s main targets are government or energy organizations in Azerbaijan, Tajikistan, Kyrgyzstan and other Commonwealth of Independent States (CIS), based on our analysis.GovernmentYoroTrooper’s main targets are government or energy organizations in Azerbaijan, Tajikistan, Kyrgyzstan and other Commonwealth of Independent States (CIS), based on our analysis.Healthcare