cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2504 articles

Threat Research · huntress.com

Huntress Details Raspberry Robin’s USB Infection Chain and Persistence

Huntress describes Raspberry Robin’s USB-based infection chain, command variations, and RunOnce persistence, drawing on an August 2023 infection attempt that Microsoft Defender detected and removed before it completed.
Sep 7, 2023
Threat Research · wiz.io

Wiz Details Seven Summer 2023 Cryptomining Incidents Targeting Cloud Workloads

Wiz Research analyzed seven cloud cryptomining incidents from summer 2023, tracing access through exposed Jupyter notebooks and vulnerable Apache Solr and documenting miners, persistence, spreading, and detection opportunities.

Sep 6, 2023
Threat Research · blog.talosintelligence.com

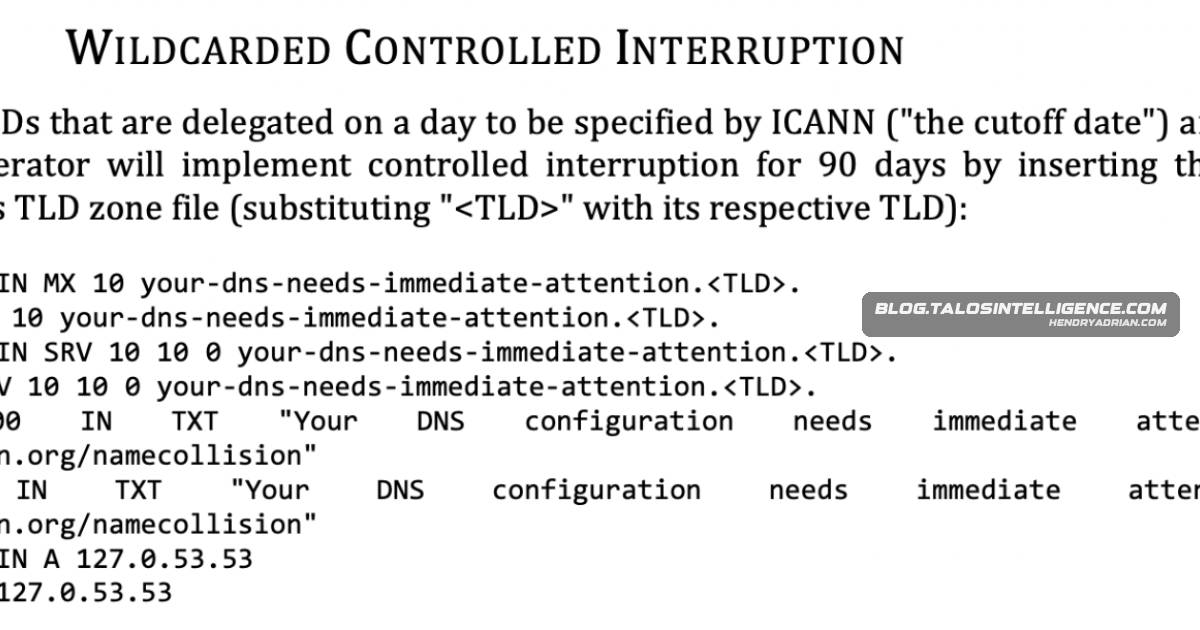
Talos Finds DNS Misconfigurations in .kids and Other Domains That Could Enable Abuse

Talos found that .kids allowed registration of a controlled-interruption name used by SCCM clients, while several other domains return DNS records for nonexistent names, creating risks including misdirected email.

Aug 29, 2023
Threat Research · blog.talosintelligence.com

Lazarus Group Uses CollectionRAT and DeimosC2 in Enterprise Campaign

Talos details a Lazarus Group campaign exploiting a ManageEngine ServiceDesk vulnerability and reusing infrastructure to deploy CollectionRAT, DeimosC2 on Linux, and a malicious Plink tool.

Aug 24, 2023
Threat Research · blog.talosintelligence.com

Lazarus Uses ManageEngine Flaw to Deploy QuiteRAT in European Infrastructure Breach

Cisco Talos reports that Lazarus exploited ManageEngine ServiceDesk CVE-2022-47966 to compromise a European internet backbone provider and deploy QuiteRAT, a compact Qt-based remote access trojan related to MagicRAT.

Aug 24, 2023
Threat Research · huntress.com

Huntress Traces Targeted Phishing Attack to XWorm Malware

Huntress traced a likely phishing infection from a tax-themed archive and Windows shortcut to an XWorm loader. The attack used a decoy W-2 PDF while downloading and launching malware, which established persistence with a scheduled task.

Aug 17, 2023
Threat Research · huntress.com

Huntress Reconstructs a Week-Long Intrusion Linked to INC Ransomware

Huntress traced a week of activity indicative of an INC ransomware attack, from compromised-account RDP access and data staging to lateral movement and attempted encryption. The initial access method was undetermined.

Aug 11, 2023
Threat Research · blog.talosintelligence.com

New Yashma Ransomware Campaign Targets Victims in Multiple Countries

Cisco Talos analyzed a Yashma ransomware campaign active since at least June 2023. The customized variant downloads ransom notes from GitHub, mimics WannaCry, persists through a startup-folder URL file, and wipes original files after encryption.

Aug 7, 2023
Threat Research · huntress.com

BEC Attackers Abused Azure Admin Privileges to Take Over Multiple Accounts

Huntress describes a BEC attack in which a compromised Azure administrator reset passwords, created additional admin accounts, and accessed multiple Microsoft 365 inboxes. The organization regained control after remediation.

Jul 27, 2023
Threat Research · wiz.io

Wiz Finds Storm-0558 Key Could Have Forged Tokens for More Microsoft Apps

Wiz researchers found Storm-0558’s compromised Microsoft key could have enabled forged tokens for more Azure applications than initially disclosed. Microsoft revoked the key, but detection remains difficult because many applications lack detailed logs.

Jul 21, 2023
Threat Research · blog.talosintelligence.com

Talos Details Malware Campaigns Targeting Ukraine and Poland

Cisco Talos analyzed campaigns targeting government, military, business, and civilian users in Ukraine and Poland. Malicious Office files launch downloaders that extract payloads hidden in images, including AgentTesla, Cobalt Strike, and njRAT.

Jul 13, 2023
Threat Research · huntress.com

Huntress Disrupts Microsoft 365 BEC Attack Using Hidden Inbox Rules

Huntress says it detected and stopped a suspected BEC attack on a U.S. logistics company, where an intruder used Microsoft 365 inbox rules to hide vendor emails and redirect payment discussions.

Jul 13, 2023
Threat Research · wiz.io

PyLoose Uses Python and Linux memfd to Run XMRig in Cloud Workloads

Wiz reports nearly 200 instances of PyLoose, a fileless attack that used exposed Jupyter Notebook services to run an XMRig miner in cloud workloads. The Python script loaded the miner into memory using Linux memfd.

Jul 11, 2023
Threat Research · threatfabric.com

Letscall Android Malware Combines Spyware with Vishing and Call Redirection

ThreatFabric describes Letscall, a three-stage Android malware toolset targeting South Koreans. It steals personal data, enables spyware and call interception, and connects victims with criminal call operators through VoIP.

Jul 7, 2023
Threat Research · threatfabric.com

Anatsa Banking Trojan Campaign Targets US, UK and DACH Banks

ThreatFabric reports Anatsa dropper campaigns on Google Play with over 30,000 installations, targeting banks in the US, UK and DACH. The Trojan steals financial data and enables device-takeover fraud.

Jun 26, 2023
Threat Research · wiz.io

Wiz Details Privilege-Escalation Risks in Managed Kubernetes Middleware

Wiz assesses managed Kubernetes middleware in AKS, EKS and GKE, finding risky host access and describing privilege-escalation paths through Node Problem Detector and Fluent Bit, alongside mitigations and gaps in standard controls.

Jun 12, 2023
Threat Research · blog.talosintelligence.com

Horabot Campaign Uses PowerShell and DLL Sideloading to Steal Data and Spread Phishing

Cisco Talos detailed a campaign targeting Spanish-speaking users in the Americas that uses phishing, PowerShell, and DLL sideloading to deploy Horabot, a banking trojan, and a spam tool.

Jun 1, 2023
Threat Research · huntress.com

Huntress Recreates MOVEit Transfer Exploit Chain, Demonstrating Arbitrary Code Execution

Huntress reconstructed exploitation of MOVEit Transfer’s SQL injection flaw, showing how it could lead to arbitrary code execution. The article details observed artifacts, hunting guidance and patches; Microsoft attributed the threat to Lace Tempest.

Jun 1, 2023
Threat Research · huntress.com

Huntress Traces XMRig Mining Infections to TeamViewer Access

Huntress traced XMRig infections on multiple endpoints to TeamViewer access, followed by PowerShell scripts that downloaded and installed the miner. The team alerted affected customers and added detections.

May 30, 2023
Threat Research · blog.talosintelligence.com

Cisco Talos Details How Intellexa’s ALIEN and PREDATOR Spyware Target Android

Cisco Talos analyzes Intellexa’s Android spyware components ALIEN and PREDATOR, describing how they work together to evade Android protections, execute code, record audio, and collect device data.

May 25, 2023
Threat Research · blog.talosintelligence.com

RA Group Ransomware Uses Leaked Babuk Code in Attacks on U.S. and South Korean Organizations

Cisco Talos reports that RA Group, active since April 2023, used ransomware derived from leaked Babuk source code in attacks on organizations in the U.S. and South Korea, combining file encryption with threats to leak stolen data.

May 15, 2023
Threat Research · huntress.com

Huntress Details PaperCut Zero-Day Exploitation and Remote Code Execution Chain

Huntress details active exploitation of PaperCut MF/NG flaws CVE-2023-27351 and CVE-2023-27350, explaining an authentication-bypass-to-SYSTEM RCE chain and observed post-exploitation payloads, including RMM tools and a crypto miner; it urges patching.

Apr 21, 2023
Threat Research · wiz.io

BrokenSesame: Alibaba Cloud Registry Write Permissions Enabled Potential Database Supply-Chain Attacks

Wiz researchers chained container isolation flaws and excessive permissions in two Alibaba Cloud PostgreSQL services, exposing potential cross-tenant access and supply-chain attacks. Alibaba says all issues were mitigated and no customer data was compromised.

Apr 19, 2023
Threat Research · huntress.com

Researchers Demonstrate Data Exfiltration Using Splunk Universal Forwarder Configurations

A Huntress researcher demonstrated how custom Splunk Universal Forwarder configurations can route selected files to an attacker-controlled syslog server for exfiltration, and recommended controls to reduce the risk.

Apr 11, 2023
PreviousPage 101 of 105 Next
© 2026 cyber.hendryadrian.com