Malicious ISO Uses IronPython to Deliver StealC and NetSupport
Summary
An analysis traces an ISO-based infection chain that uses bundled IronPython and in-memory stages to deliver StealC v2 and NetSupport. Researchers explain the techniques, sandbox results, limitations, and defensive checks.
Key points
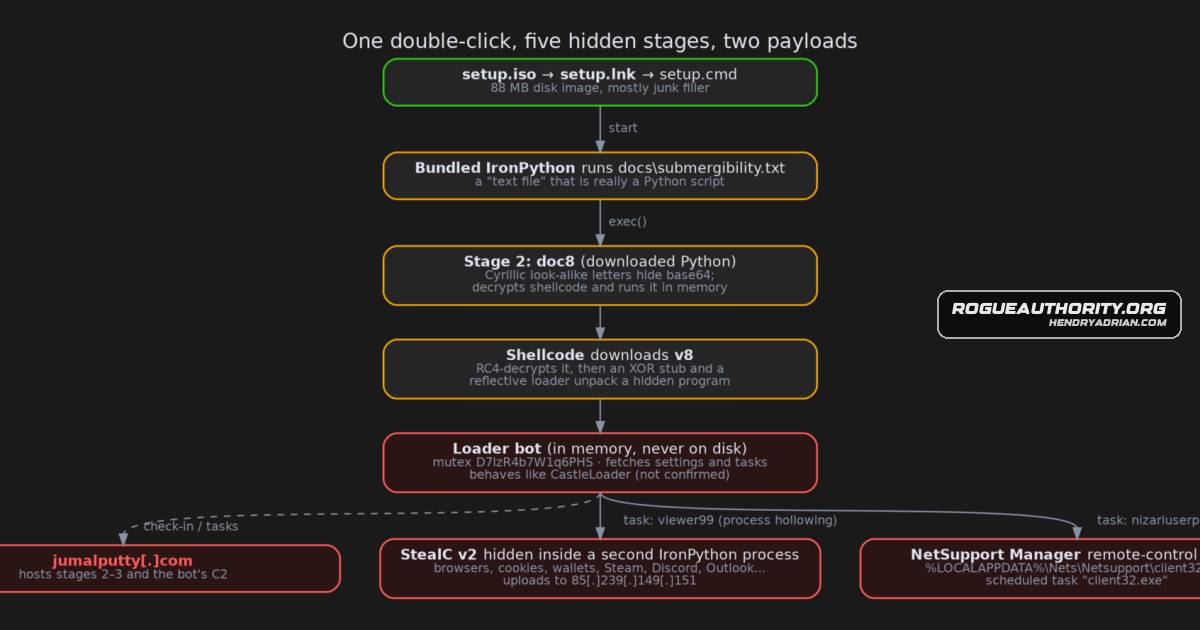
- The 88 MB ISO contains a shortcut that runs a disguised Python script with a bundled IronPython interpreter; much of the image is filler.
- The script downloads successive stages, uses obfuscation and shellcode, and loads a Windows program directly into memory.
- A loader bot delivers StealC v2, which targets browser credentials, cookies, payment data, crypto wallets, messaging tokens, email profiles, and other information.
- The bot also installs a NetSupport client under %LOCALAPPDATA%\Nets\Netsupport\ and creates a scheduled task for persistence.
- Researchers say the loader resembles CastleLoader/CastleBot, but treat that family identification as unconfirmed.
- Only one of three public sandbox runs executed the shortcut and observed the full chain; the others did not click it, illustrating the need to verify that sandbox tests run ISO contents.
- The article recommends avoiding unexpected ISO installers and checking for the NetSupport path and scheduled task; it also provides indicators including jumalputty[.]com and nizariuserp[.]com.
Article Details
- Attack Vectors
- A software-installer lure distributed as an ISO contains a setup.lnk shortcut that starts bundled IronPython and executes a Python script disguised as docs\submergibility.txt.
- The script disables HTTPS certificate checks, downloads further stages, and uses base64 encoding with Cyrillic look-alike substitutions to obscure the payload.
- Downloaded shellcode is XOR-decrypted, copied into executable memory, and run; later stages use RC4 decryption and a reflective loader to load a Windows program directly in memory.
- The loader bot downloads and executes StealC v2 and a NetSupport Manager client; StealC is injected into a suspended IronPython process using process hollowing.
- The NetSupport client is installed under %LOCALAPPDATA%\Nets\Netsupport\ and configured to persist through a scheduled task named client32.exe.
- Defensive Notes
- Treat unexpected .iso, .img, or .vhd installers—especially those containing shortcuts—as suspicious.
- For sandbox analysis of disk images and archives, verify that the shortcut or other entry point was actually executed before trusting a clean verdict.
- Alert when ipyw32.exe or ipy.exe starts from a mounted ISO or removable drive, or is given a .txt argument; also alert on a child ipyw32.exe with no arguments.
- Check for %LOCALAPPDATA%\Nets\Netsupport\ and a scheduled task named client32.exe; the article advises assuming remote access if these are present.
- If infection is suspected, change passwords from a clean device, revoke active sessions, and move cryptocurrency funds to a new wallet.
- The article recommends blocking the listed network indicators. It reports that StealC v2 uses plain-HTTP POST / with JSON and no User-Agent.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | crataga[.]site | Contacted by a Python process during the infection; its role is unknown. |
| DOMAIN | jumalputty[.]com | Reported attacker-controlled domain serving stages and used for loader C2. |
| DOMAIN | nizariuserp[.]com | Reported attacker-used domain serving the NetSupport package. |
| IPV4 | 85[.]239[.]149[.]151 | StealC v2 C2 address receiving the stealer's uploads. |
| SHA256 | 0d65239438fb18bdd4a80e1a2b071eed3215ac0615d4f62854aeeefde98e69ba | SHA-256 of the loader bot, which the article says exists only in memory. |
| SHA256 | 36805ebcc0c295751c9b858fc9bbe75ba46362c672f860eafb73ec67f7ce8a4b | SHA-256 of the malicious setup.iso lure. |
| SHA256 | 61dac869de65880377d4f398175b6c17d703a29b01483bd52fc3954e5876f9e3 | SHA-256 of doc8, the downloaded second-stage payload. |
| SHA256 | 63e5e40ea1abc1a4df7d5881a86332705f19f51510b9d09e5d6f725fc653dfcc | SHA-256 of v8, a downloaded third-stage payload. |
| SHA256 | 7114bf57f09c0bb24e6d7e895afc33721187b06969c3454db749c1c0e11cfb10 | SHA-256 of the StealC v2 payload. |
| SHA256 | 9666964ef36a9a4a5585d10d3337cfa07472b002083df885639812f2178b5676 | SHA-256 of the StealC App-Bound helper. |
| URL | hxxps[:]//jumalputty[.]com/473070fa-6f82-5c2a-9dee-3db4be57110f/ | Reported malicious stage-download URL for doc8, v8, and viewer99. |
| URL | hxxps[:]//jumalputty[.]com/70cadffb-604e-5ebd-845d-79a123ed1f74 | Loader bot C2 URL. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe article describes base64-encoded content, Cyrillic look-alike substitutions, XOR/RC4 encryption, and stack-string obfuscation across the stages.T1053.005 · Scheduled TaskA scheduled task named client32.exe is used to restart the NetSupport client.T1055.012 · Process HollowingThe loader hollows a suspended ipyw32.exe process and replaces its contents with StealC v2.T1059.006 · PythonThe bundled IronPython interpreter executes Python code disguised as docs\submergibility.txt.T1105 · Ingress Tool TransferThe Python script and loader download successive payload stages, including doc8, v8, and viewer99.T1113 · Screen CaptureThe stealer collects a screenshot.T1140 · Deobfuscate/Decode Files or InformationThe stages decode or decrypt downloaded content using base64, XOR, and RC4 before execution.T1204.002 · Malicious FileThe infection begins when a victim double-clicks setup.lnk inside the ISO.T1539 · Steal Web Session CookieStealC v2 targets browser cookies, which the article notes can be used to bypass passwords.T1555.003 · Credentials from Web BrowsersStealC v2 collects saved browser passwords, cookies, autofill data, and credit-card data from named browsers.T1573.001 · Symmetric CryptographyThe loader bot's C2 traffic is described as using ChaCha20 encryption.T1620 · Reflective Code LoadingThe reflective loader loads a Windows program directly from memory so it does not exist as a file on disk.
Malware
CastleBotIts design matches public descriptions of CastleLoader / CastleBot: a shellcode stager, then a PE loader, then a core bot with ChaCha20 traffic that delivers NetSupport and StealC.CastleLoaderIts design matches public descriptions of CastleLoader / CastleBot: a shellcode stager, then a PE loader, then a core bot with ChaCha20 traffic that delivers NetSupport and StealC.StealC v2The last of them is a loader bot that installs StealC v2, an information stealer, and the NetSupport Manager remote-control client.
Products
Bravesaved passwords, cookies, autofill and credit cards from Chrome, Edge, Brave and Firefox (with a small helper for Chrome’s newer "App-Bound" protection)DiscordPayloads: StealC v2 (passwords, cookies, cards, crypto wallets, Steam/Discord tokens, Outlook, WinSCP, screenshots) and a NetSupport RAT client with a scheduled task.Edgesaved passwords, cookies, autofill and credit cards from Chrome, Edge, Brave and Firefox (with a small helper for Chrome’s newer "App-Bound" protection)FoxmailSteam login files, Discord tokens, Outlook and Foxmail profiles, WinSCP saved sessionsGoogle Chromesaved passwords, cookies, autofill and credit cards from Chrome, Edge, Brave and Firefox (with a small helper for Chrome’s newer "App-Bound" protection)IronPythonDouble-clicking the shortcut inside starts a genuine copy of IronPython, a .NET version of Python that the attackers ship with the image, and has it run a "text file" that is really a Python script.Mozilla Firefoxsaved passwords, cookies, autofill and credit cards from Chrome, Edge, Brave and Firefox (with a small helper for Chrome’s newer "App-Bound" protection)NetSupport ManagerThe last of them is a loader bot that installs StealC v2, an information stealer, and the NetSupport Manager remote-control client.OutlookPayloads: StealC v2 (passwords, cookies, cards, crypto wallets, Steam/Discord tokens, Outlook, WinSCP, screenshots) and a NetSupport RAT client with a scheduled task.SteamPayloads: StealC v2 (passwords, cookies, cards, crypto wallets, Steam/Discord tokens, Outlook, WinSCP, screenshots) and a NetSupport RAT client with a scheduled task.WinSCPPayloads: StealC v2 (passwords, cookies, cards, crypto wallets, Steam/Discord tokens, Outlook, WinSCP, screenshots) and a NetSupport RAT client with a scheduled task.
Tools
7-ZipTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.ANY.RUNTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.Binary RefineryTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.capaTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.MalcatTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.PythonTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.REMnuxThis analysis and write-up were produced by Claude (Opus 5.5), working as an agent in Claude Code on a REMnux analysis VM.speakeasyTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.TriageTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.tsharkTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.VirusTotalTools used: Malcat, speakeasy, capa, Binary Refinery, 7-Zip, tshark, Python, VirusTotal (file store, sandbox report and PCAP), ANY.RUN and Triage.