
Over 900 Sangoma FreePBX Instances Remain Infected in Ongoing Attacks
Summary
Shadowserver found more than 900 FreePBX instances still infected after attacks exploiting CVE-2025-64328 began in December 2025. Fortinet attributes EncystPHP deployments to INJ3CTOR3; FreePBX 17.0.3 and access controls are recommended.
Key points
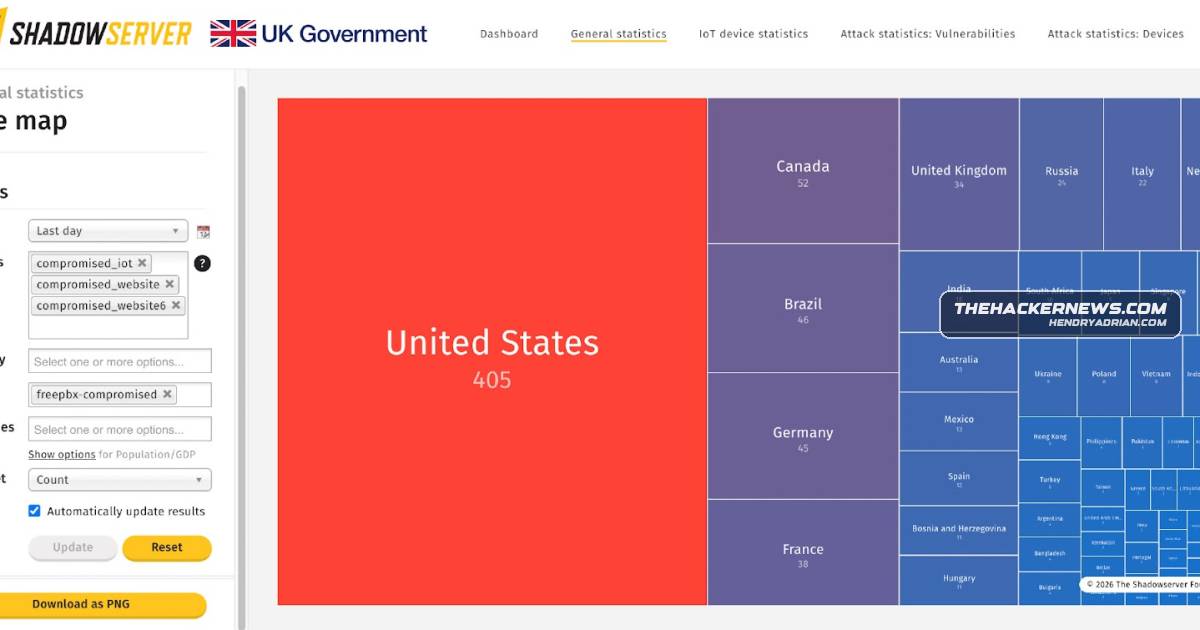
- Shadowserver reported more than 900 Sangoma FreePBX instances remain infected; 401 are in the United States.
- The attacks exploit CVE-2025-64328, a post-authentication command injection flaw affecting FreePBX versions 17.0.2.36 and later; version 17.0.3 fixes it.
- Fortinet attributes EncystPHP web shell deployments to the INJ3CTOR3 threat actor.
- The web shell can enable arbitrary command execution and outbound call activity through the PBX environment, according to Fortinet.
- Recommended mitigations include upgrading to FreePBX 17.0.3, updating the filestore module, and restricting access to the Administration Control Panel.
Article Details
- Event Type
- Ongoing exploitation and compromise of Sangoma FreePBX instances using a post-authentication command injection vulnerability.
- Impact
- More than 900 instances reportedly remain infected with web shells. The flaw can enable arbitrary shell command execution on compromised hosts, and the deployed web shell can initiate outbound calls through the PBX environment. The article recommends updating FreePBX to 17.0.3, updating the filestore module, and restricting access to the administration panel.
MITRE ATT&CK
CVE
Threat Actors
Malware
Vendors
Products
Countries
Brazil401 compromised hosts are in the United States, with Brazil (51), Canada (43), Germany (40), and France (36) also affected.Canada401 compromised hosts are in the United States, with Brazil (51), Canada (43), Germany (40), and France (36) also affected.France401 compromised hosts are in the United States, with Brazil (51), Canada (43), Germany (40), and France (36) also affected.Germany401 compromised hosts are in the United States, with Brazil (51), Canada (43), Germany (40), and France (36) also affected.United States401 compromised hosts are in the United States, with Brazil (51), Canada (43), Germany (40), and France (36) also affected.