
Public Google Cloud API Keys Could Expose Gemini Data and Enable Unauthorized Charges
Summary
Truffle Security found 2,863 live public Google API keys, while Quokka identified over 35,000 in Android apps. Researchers say enabling the Generative Language API can give existing keys Gemini access; Google says it is blocking leaked keys. Exploitation is unknown.
Key points
- Truffle Security reported 2,863 live public keys; Quokka found over 35,000 keys in a scan of 250,000 Android apps.
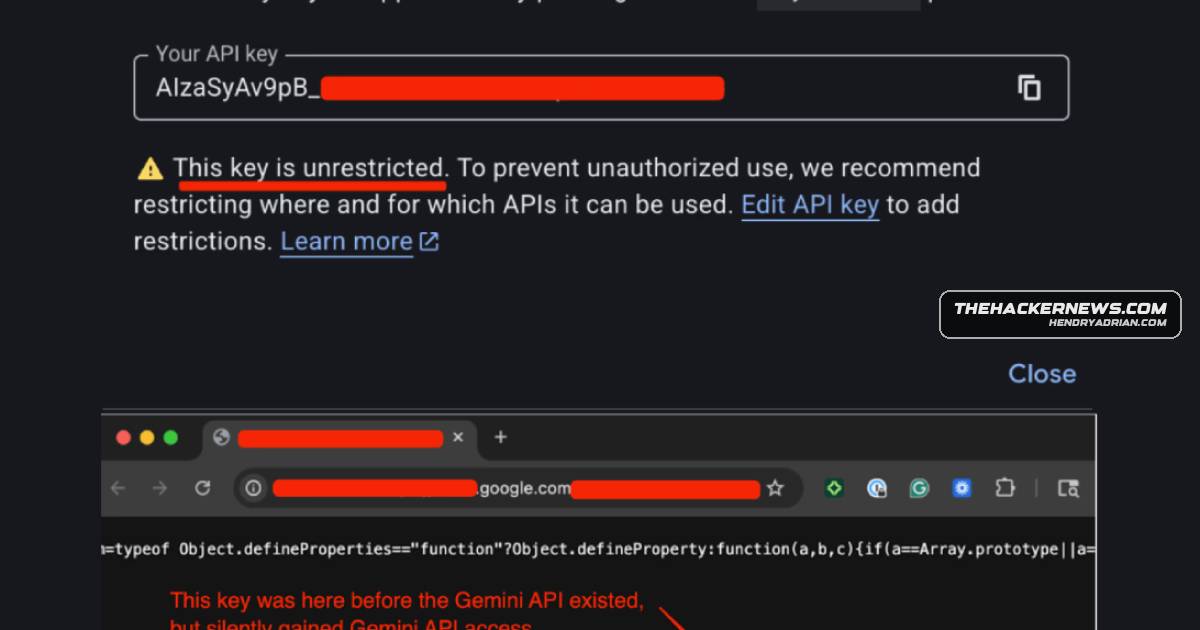
- Researchers say enabling the Generative Language API can give existing project keys Gemini access without warning; newly created keys default to unrestricted.
- The keys could allow access to Gemini's /files and /cachedContents endpoints, Gemini API calls, and unauthorized usage charges.
- Google said it has implemented measures to detect and block leaked keys attempting to access the Gemini API.
- Whether the issue was exploited in the wild is unknown. A Reddit user claimed a stolen key led to $82,314.44 in charges over two days.
- Organizations are advised to review enabled APIs, rotate publicly accessible keys—starting with older keys—and continuously monitor API security.
Article Details
- Event Type
- Exposure of public Google Cloud API keys that can gain access to Gemini endpoints when the Generative Language API is enabled.
- Impact
- Exposed keys may allow attackers to access uploaded files and cached data, make Gemini API calls, and consume quota or incur charges. Truffle Security reported finding 2,863 live public keys, while Quokka reported over 35,000 keys in Android apps. Exploitation in the wild is unknown; a Reddit user claimed a stolen key led to $82,314.44 in charges, but that claim is unverified. Google said it implemented measures to detect and block leaked keys attempting to access the Gemini API.
People
Vendors
Products
GeminiResearchers found that Google Cloud API keys, many embedded in client-side code as billing identifiers, can be abused to authenticate to Gemini endpoints and expose uploaded files and cached data.Gemini APIQuokka reported thousands of exposed keys that become unrestricted Gemini credentials when the Generative Language API is enabled, enabling quota theft and large billing charges; Google has implemented measures toGoogle CloudResearchers found that Google Cloud API keys, many embedded in client-side code as billing identifiers, can be abused to authenticate to Gemini endpoints and expose uploaded files and cached data.