
Prophet Security Describes AI Investigations of Cloud Credential Abuse and TOAD Phishing
Summary
Prophet Security describes two customer investigations by its AI SOC platform: a compromised AWS credential used for reconnaissance and a TOAD phishing email. The vendor says the investigations correlated telemetry across multiple sources and exposed their queries for,
Key points
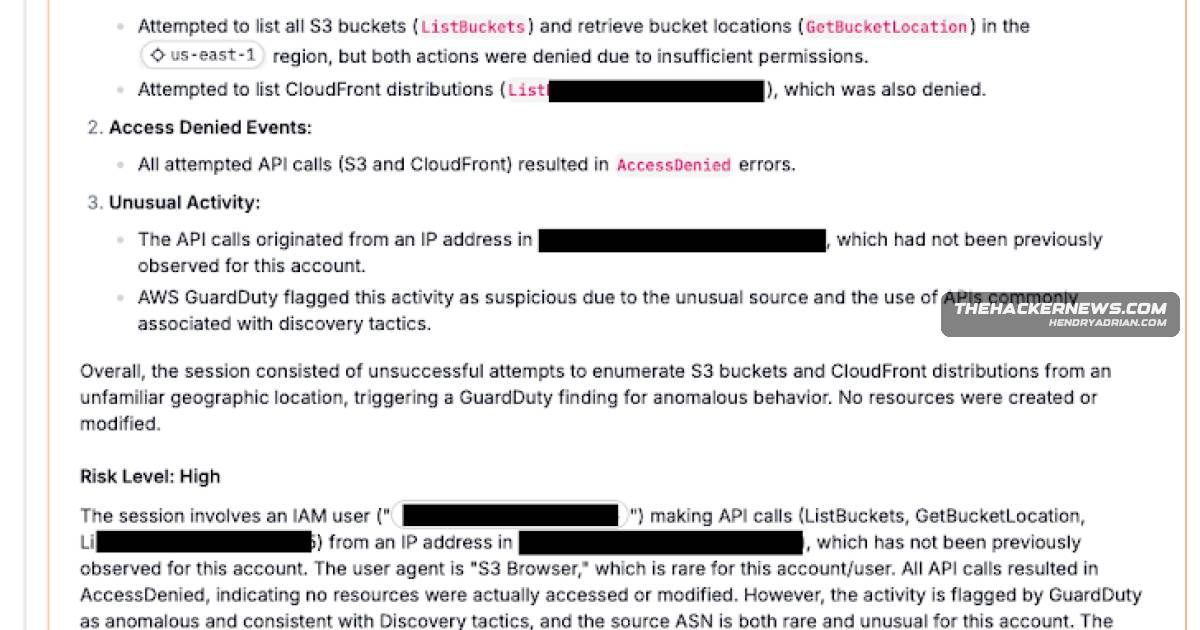
- In a vendor-described case, a dormant AWS IAM key was used for discovery API calls from an unfamiliar Turkish IP; the article says the investigation confirmed credential compromise.
- The vendor says least-privilege controls prevented data access, the key was revoked, and the incident prompted an audit that found additional stale credentials.
- A second investigation identified a TOAD phishing attempt: a genuine Zoom one-time-password email carried a fraudulent PayPal auto-debit notice and phone number.
- The article says the Zoom email passed SPF and DKIM checks and contained no malicious links or malware; its deceptive intent was in the message text.
- Prophet Security says its platform queried six data sources and ran 265 queries in the credential case, and queried 11 sources in the phishing case.
- The vendor presents query-level transparency and evidence review as features intended to help analysts validate AI investigation findings.
Article Details
- Event Type
- Prophet Security reported two production SOC investigations using its agentic AI platform: a cloud credential compromise investigation and detection of a TOAD-style phishing email.
- Impact
- In the first case, a compromised AWS credential was used for cloud reconnaissance. The article reports that least-privilege controls prevented data access, the key was revoked, and the incident prompted an audit that found additional stale credentials. In the second case, an attacker used a Zoom account to send a legitimate-looking email impersonating a PayPal auto-debit notification and urging the recipient to call a fraudulent support line. The article reports no malicious links or malware in the email.
MITRE ATT&CK
T1078.004 · Cloud AccountsThe reported cloud reconnaissance used a compromised AWS access key associated with an IAM user, consistent with Valid Accounts: Cloud Accounts.T1580 · Cloud Infrastructure DiscoveryThe compromised account listed S3 buckets and enumerated CloudFront distributions, activities consistent with Cloud Infrastructure Discovery.
Vendors
Amazon Web Services#ProphetSecurity #AWSCrowdStrikeThe AI executed hundreds of queries across tools like SIEM, GuardDuty, Wiz, CrowdStrike, IPINFO, and Spur to build evidence chains.Prophet SecurityProduction cases at Prophet Security show the AI reconstructing a cloud credential compromise and detecting intent in a legitimate-appearing phishing email with full query-level transparency.WizThe AI executed hundreds of queries across tools like SIEM, GuardDuty, Wiz, CrowdStrike, IPINFO, and Spur to build evidence chains.ZoomAn attacker registered a Zoom account, set the display name to a fraudulent PayPal auto-debit notification (including a phone number to call), and triggered a standard Zoom One-Time Password email that was
Products
Amazon GuardDutyTo reach that conclusion, the system queried six different data sources: the customer’s SIEM, AWS GuardDuty, Wiz, CrowdStrike (checking endpoint telemetry for the source IP), IPINFO, and Spur.CrowdStrikeThe AI executed hundreds of queries across tools like SIEM, GuardDuty, Wiz, CrowdStrike, IPINFO, and Spur to build evidence chains.Prophet AIRather than scoring alerts and handing them off, Prophet AI autonomously queries across the security stack, correlates findings from multiple telemetry sources, and delivers complete investigations with fullWizThe AI executed hundreds of queries across tools like SIEM, GuardDuty, Wiz, CrowdStrike, IPINFO, and Spur to build evidence chains.ZoomAn attacker registered a Zoom account, set the display name to a fraudulent PayPal auto-debit notification (including a phone number to call), and triggered a standard Zoom One-Time Password email that was