cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3801 articles

Security News · securityweek.com

North Korean Hackers Target Node.js Maintainers With Fake Meeting Lures

Socket reports that a North Korean-linked campaign targeted prominent Node.js maintainers with weeks-long social engineering, fake meeting infrastructure and bogus Microsoft Teams updates to deliver a RAT. Targets reported attacks similar to the Axios maintainer case.

Apr 6, 2026
Security News · thecyberexpress.com

UAE Cyber Security Council Says Phishing Starts More Than 75% of Cyberattacks

The UAE Cyber Security Council told WAM that phishing or fraudulent messages start more than 75% of cyberattacks and estimated 3.4 billion phishing messages are sent daily worldwide. It advised users to verify messages, enable MFA, update systems, and report suspicious.

Apr 6, 2026
Security News · thehackernews.com

Germany’s BKA Names Two Suspects in 130 REvil Ransomware Attacks

Germany’s BKA identified REvil’s UNKN as Daniil Shchukin and added alleged developer Anatoly Kravchuk to its wanted list, suspecting them of 130 attacks. The cases reportedly caused over $40.8 million in damages, with $2.19 million in ransoms paid.

Apr 6, 2026
Security News · thecyberexpress.com

FCC Proposes $4.5 Million Fine Against Voxbeam Over Robocall Traffic

The FCC proposed a $4.5 million fine against Voxbeam, alleging it routed tens of thousands of calls from unregistered Czech provider Axfone, including calls spoofing bank fraud and customer-service numbers, to U.S. networks.

Apr 6, 2026
Security News · bleepingcomputer.com

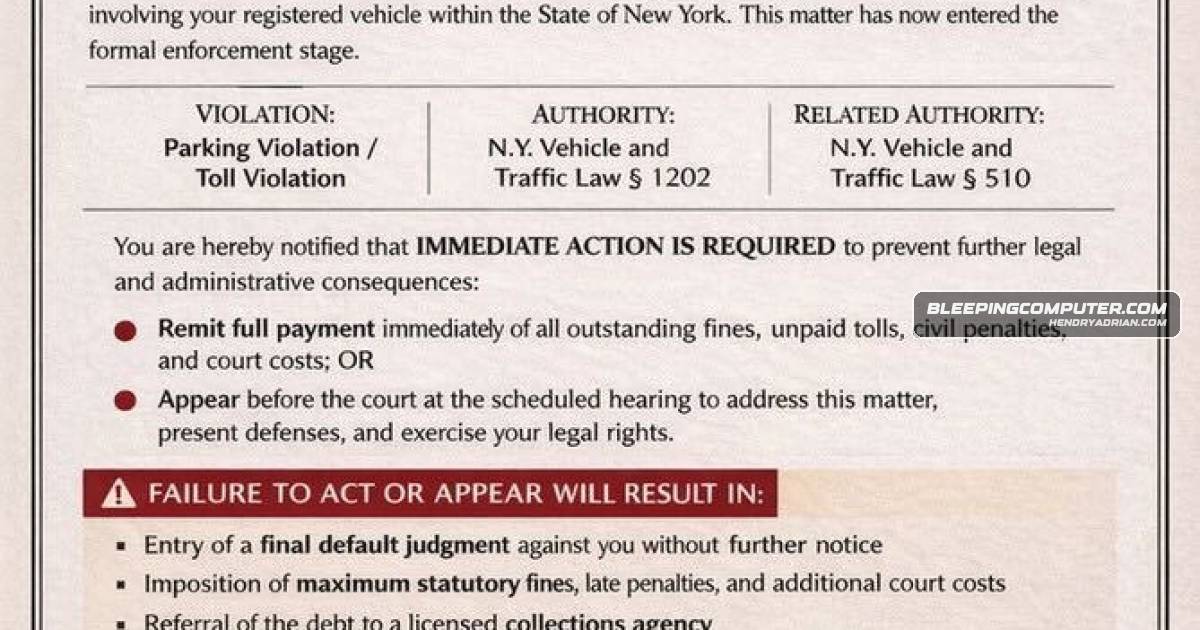
QR-Code Traffic Violation Scams Use Fake Court Notices to Steal Data

Fake court-violation texts send recipients through a QR code and CAPTCHA to phishing pages demanding $6.99 and harvesting personal and payment details. The campaign has been reported in multiple states.

Apr 5, 2026
Security News · keplernewsletter.substack.com

Privacy and Cybersecurity Roundup: New AI Rules and Foreign Router Restrictions

A roundup of regulatory developments covers Germany’s Data Act enforcement law, new UK automated-decision safeguards, AI oversight measures in Poland and California, Utah age-verification rules, New York frontier-AI requirements, and FCC restrictions on new foreign-made

Apr 5, 2026
Security News · bleepingcomputer.com

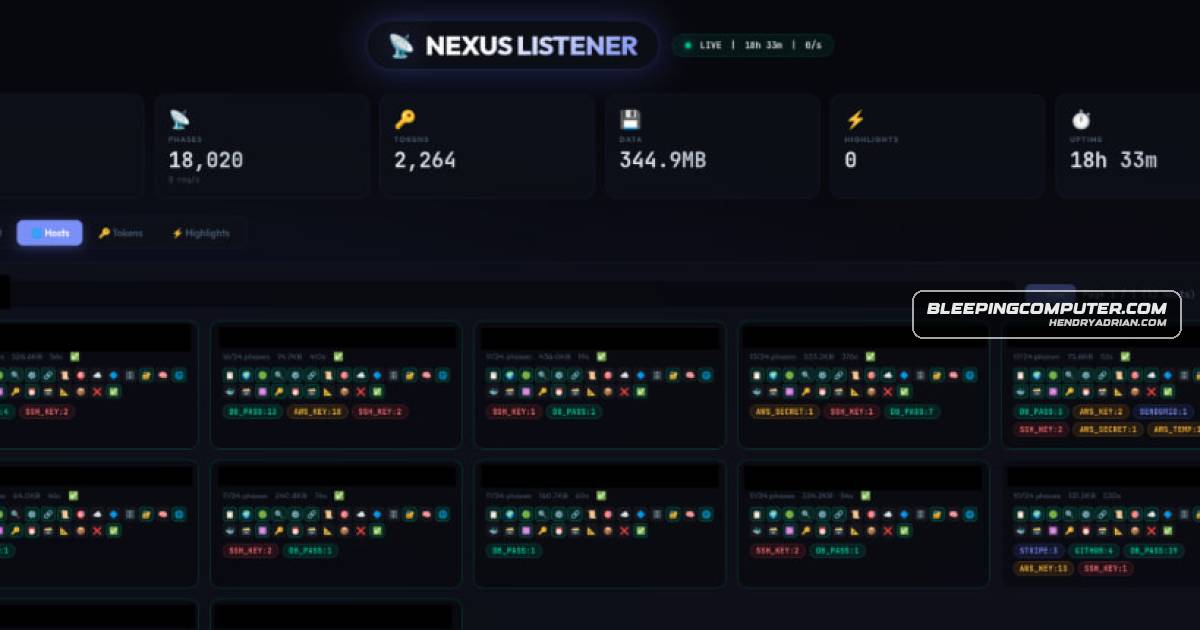
React2Shell Campaign Harvested Credentials from 766 Hosts, Cisco Talos Says

Cisco Talos says attackers exploited React2Shell in Next.js apps, using NEXUS Listener to harvest secrets from at least 766 hosts in 24 hours. The researchers attribute the campaign to UAT-10608 and recommend patching and credential rotation.

Apr 5, 2026
Security News · bleepingcomputer.com

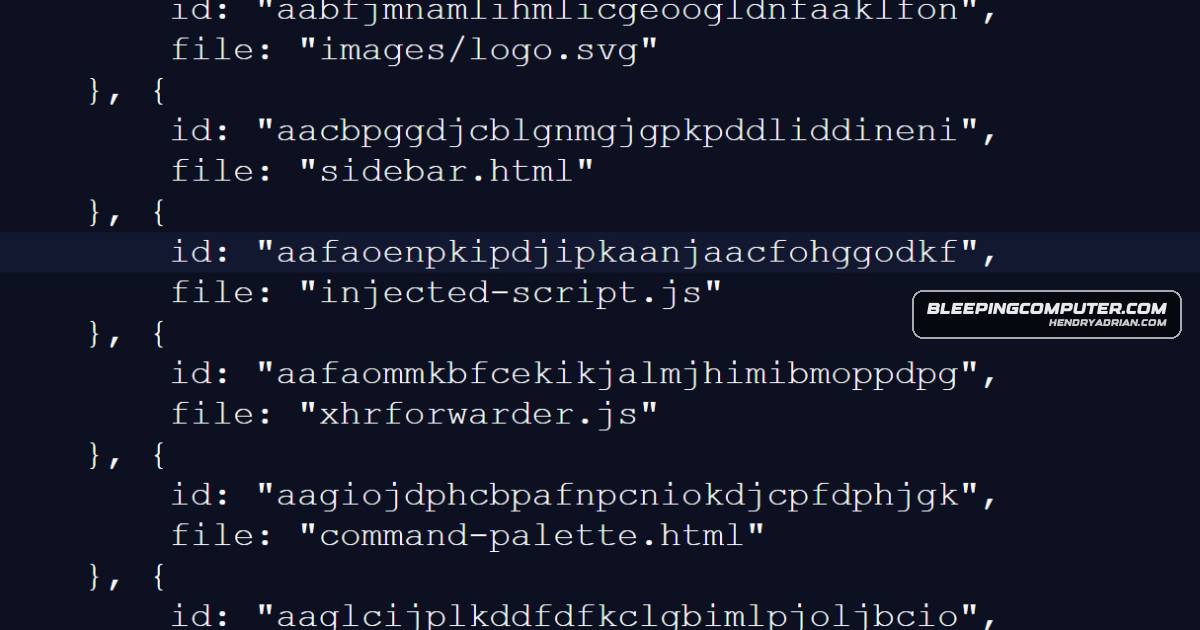
LinkedIn Script Scans for 6,236 Browser Extensions and Collects Device Data

BleepingComputer confirmed LinkedIn loads a script that checks for 6,236 browser extensions and gathers device and browser data. Fairlinked alleges the data is used to profile users; LinkedIn says detection supports anti-scraping defenses and denies sensitive inference.

Apr 4, 2026
Security News · bleepingcomputer.com

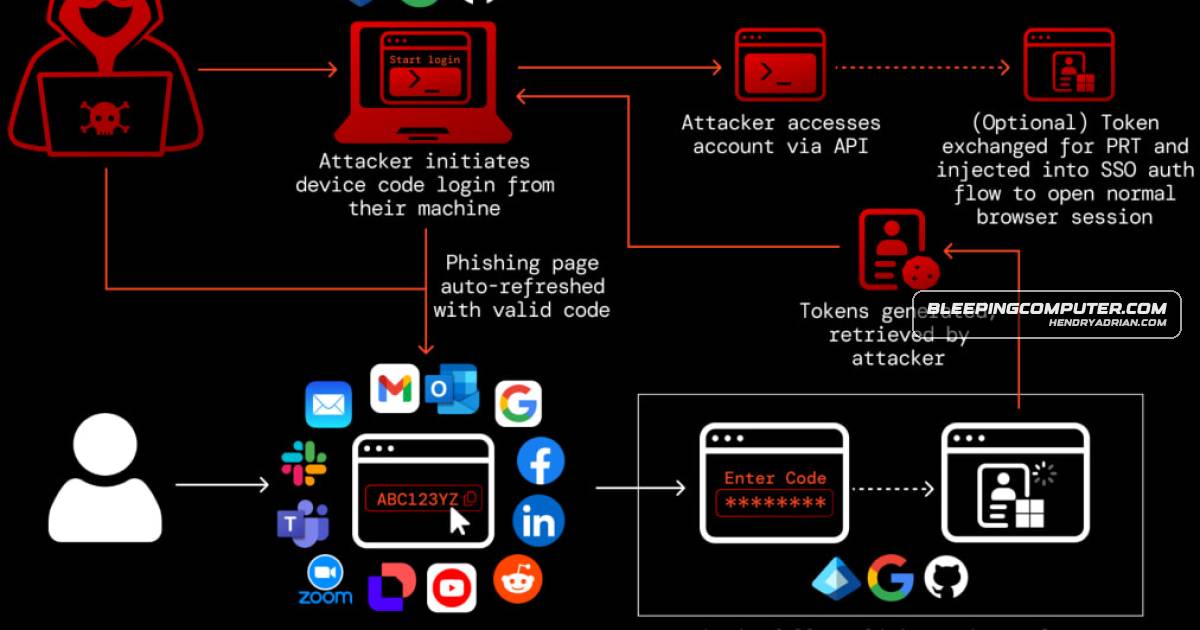
Device Code Phishing Surges 37.5x as New Kits Spread

Push Security reports a 37.5x increase in device code phishing this year, with at least 11 kits using SaaS-themed lures. It recommends disabling the flow when unnecessary and monitoring authentication logs.

Apr 4, 2026
Security News · elastic.co

Elastic Announces Nine Security Integrations for Q1 2026

Elastic announced nine security integrations with prebuilt ingest pipelines and dashboards, adding visibility across macOS, SIEM, email, cloud, identity, browser, and data-security sources.

Apr 4, 2026
Security News · generalstaatsanwaltschaft-karlsruhe.justiz-bw.de

German Authorities Identify Suspected GandCrab and REvil Leaders, Obtain Arrest Warrants

German investigators say they identified the suspected leader of GandCrab and REvil and a suspected malware programmer, securing national and European arrest warrants. The suspects are also accused of involvement in a 2019 theater attack.

Apr 4, 2026
Security News · thehackernews.com

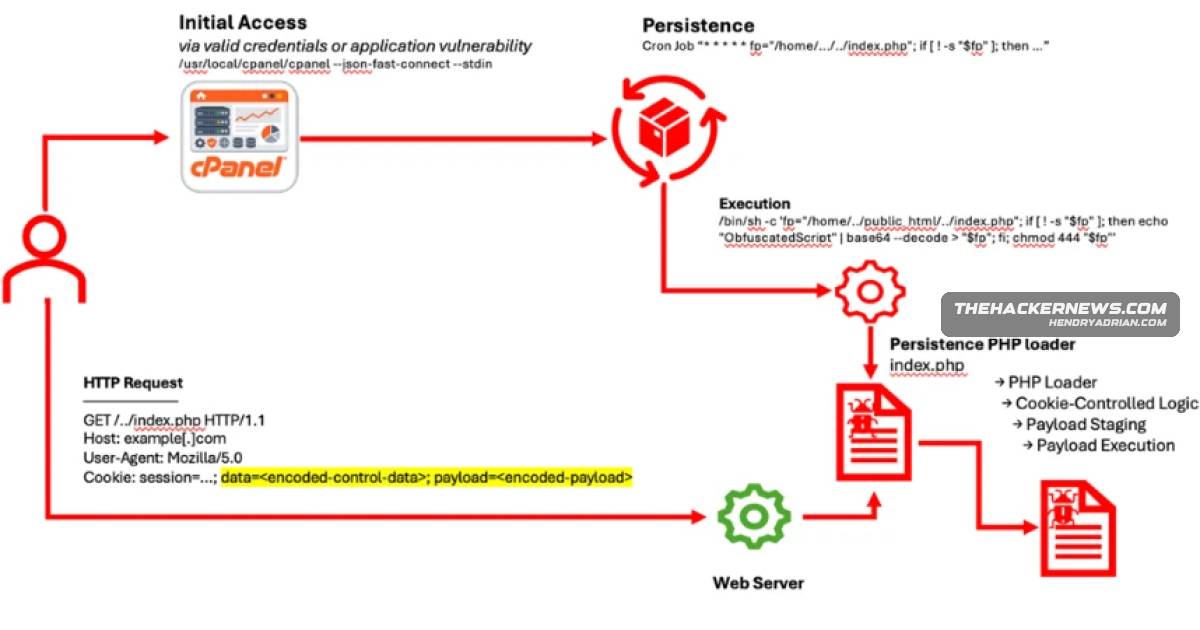
Microsoft Details Cookie-Controlled PHP Web Shells Using Cron for Linux Persistence

Microsoft says threat actors use HTTP cookies to activate PHP web shells on Linux servers and cron jobs to recreate loaders. It recommends stronger authentication, cron and web-directory audits, and restricting shell execution.

Apr 4, 2026
Security News · bleepingcomputer.com

LinkedIn script scans for 6,236 browser extensions and collects device signals

BleepingComputer observed LinkedIn loading a script that probes 6,236 Chrome extensions and collects device signals. LinkedIn says scans support anti-scraping and site stability; claims that data is used to profile users or identify customers remain unverified.

Apr 3, 2026
Security News · therecord.media

FCC Proposes $4.5 Million Fine Against Voxbeam Over Robocall Traffic

The FCC proposed a $4.5 million fine against Voxbeam for allegedly carrying tens of thousands of financial impersonation robocalls from unauthorized provider Axfone. Voxbeam can respond before the agency makes a final decision.

Apr 3, 2026
Security News · securityweek.com

Weekly Cybersecurity Roundup Covers Android Malware, ChatGPT Flaw and Ransomware Incidents

This weekly roundup covers Mirax and Operation NoVoice Android malware, a patched ChatGPT data-leak flaw, Apple’s ClickFix warning, a Symantec DLP patch, a Minot water-plant ransomware incident, the FBI wiretap-system breach and supplier-linked Nissan data theft.

Apr 3, 2026
Security News · thecyberexpress.com

Weekly Cyber Roundup Covers Hasbro, Supply-Chain Attacks and Breaches

The roundup covers Hasbro’s reported unauthorized access, Mercor’s LiteLLM supply-chain breach, a Lazarus-attributed Axios attack, an email breach attributed to Iran-linked Handala, and a CareCloud EHR intrusion.

Apr 3, 2026
Security News · bleepingcomputer.com

Microsoft Begins Forcing Unmanaged Windows 11 24H2 PCs to Upgrade to 25H2

Microsoft has begun using an intelligent rollout to upgrade unmanaged Windows 11 24H2 Home and Pro devices to 25H2. Remaining on 24H2 after support ends means missing security updates; users can install 25H2 manually or pause updates temporarily.

Apr 3, 2026
Security News · thehackernews.com

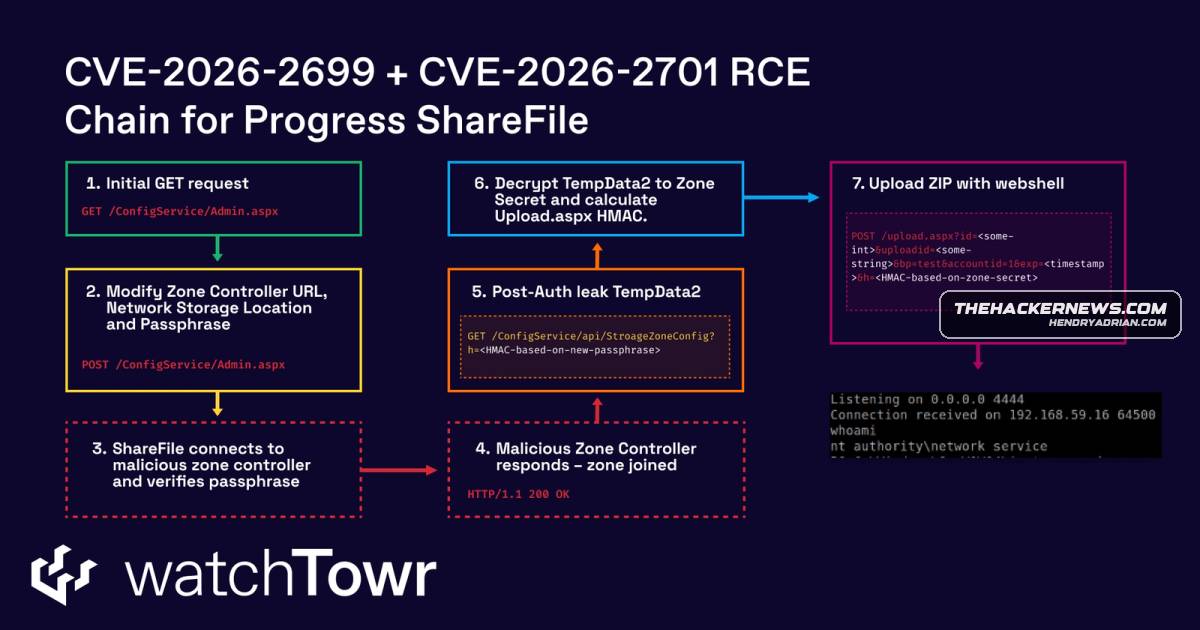
ThreatsDay Roundup Covers ShareFile RCE Flaws, Android Rootkit and CloudTrail Evasion

The roundup reports ShareFile RCE flaws, Android NoVoice, researchers’ findings of unpatched ImageMagick RCE flaws and CloudTrail evasion, alongside supply-chain abuse, phishing, ransomware defenses and malware updates.

Apr 3, 2026
Security News · thehackernews.com

Cisco Talos Reports UAT-10608 Used React2Shell to Compromise 766 Next.js Hosts

Cisco Talos attributes a credential-harvesting campaign to UAT-10608, reporting exploitation of CVE-2025-55182 against at least 766 Next.js hosts and theft of credentials and other secrets.

Apr 3, 2026
Security News · cybersecuritypulse.net

TeamPCP Supply-Chain Campaign and AI Security Launches Lead Cybersecurity Roundup

TeamPCP’s cascading supply-chain campaign compromised security tools; reports link it to Mercor, where Lapsus$ claims to auction data including biometrics. The issue also covers AI-agent flaws and launches, other incidents, and mitigations.

Apr 3, 2026
Security News · matthewrosenquist.substack.com

Gmail Username Changes Could Weaken Address-Based Spam and Phishing Blocks

Google lets users change their primary Gmail username while keeping the account and turning the old address into an alias. The author warns this could let spammers and phishers evade address-based blocks; Google limits changes to once per year, up to three times.

Apr 3, 2026
Security News · varonis.com

Claude Code Source Exposed Through npm Package Debug Files

A debug source map in Anthropic’s Claude Code 2.1.88 npm package reportedly exposed about 1,900 files and 512,000 lines. The article describes the agent’s permissions and guardrails, ways to loosen them, and concerns about community mirrors.

Apr 3, 2026
Security News · zscaler.com

Zscaler Reports March 2026 Supply-Chain Attacks Affecting Axios and LiteLLM

Zscaler reports supply-chain compromises involving Axios and LiteLLM, lists related malware detections and indicators of compromise, and says it has added coverage to detect downloads of compromised packages.

Apr 3, 2026
Security News · bleepingcomputer.com

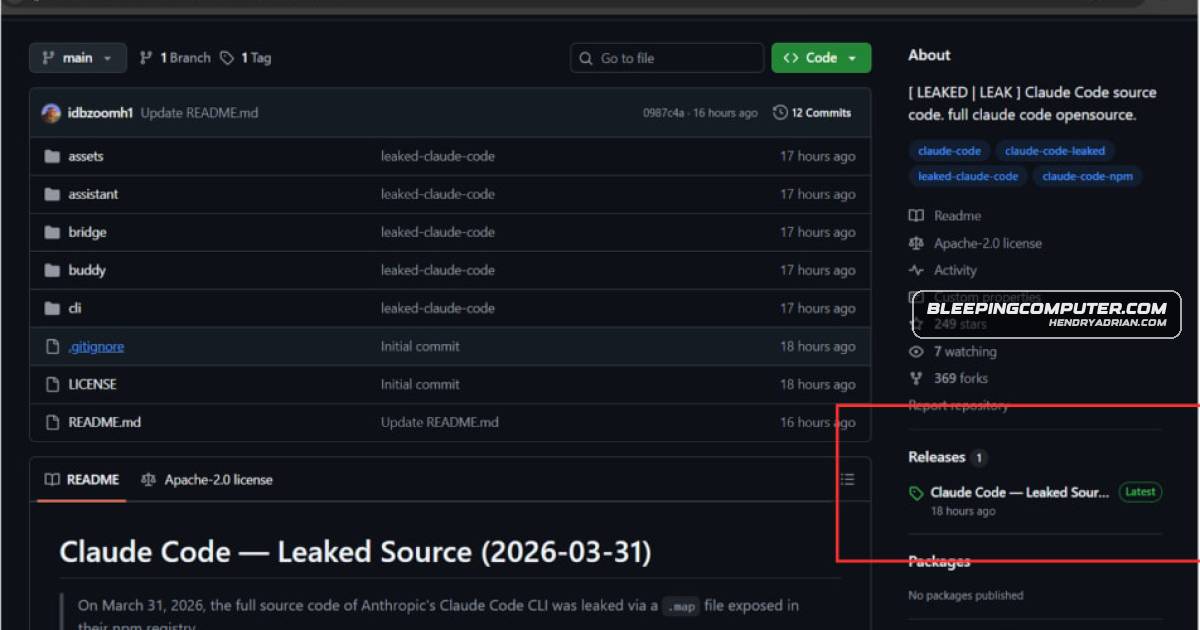
Fake Claude Code Leak Repositories Deliver Vidar Infostealer

Zscaler researchers found fake GitHub repositories posing as Claude Code leaks that use a Rust dropper to deliver Vidar and GhostSocks. They observed frequent archive updates and a second repository likely run by the same actor.

Apr 2, 2026
PreviousPage 122 of 159 Next
© 2026 cyber.hendryadrian.com