
Fake Claude Code Leak Repositories Deliver Vidar Infostealer
Summary
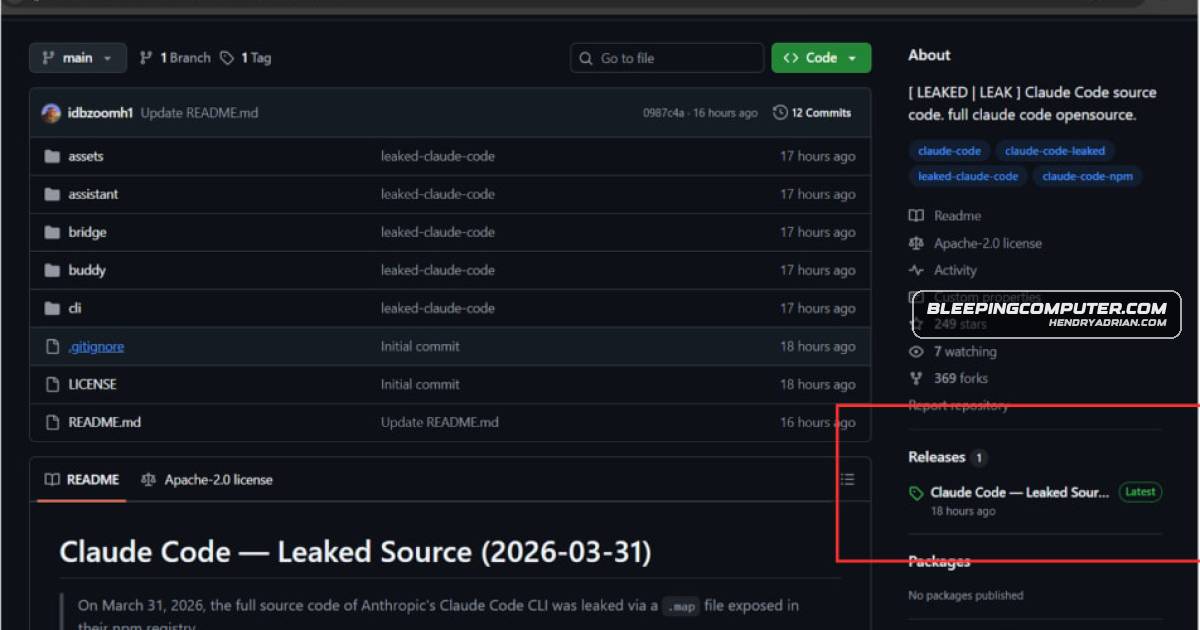
Zscaler researchers found fake GitHub repositories posing as Claude Code leaks that use a Rust dropper to deliver Vidar and GhostSocks. They observed frequent archive updates and a second repository likely run by the same actor.
Key points
- Anthropic accidentally exposed 513,000 lines of Claude Code TypeScript through a source map in an npm package.
- A fake GitHub repository by user “idbzoomh” used search-engine optimization to attract people looking for the leak.
- The repository offered a 7-Zip archive containing the Rust executable ClaudeCode_x64.exe.
- When launched, the executable deploys Vidar, an information stealer, and the GhostSocks traffic-proxying tool.
- Zscaler observed frequent updates to the malicious archive, suggesting payloads could change.
- Researchers found a second repository with identical code and assessed it as likely operated by the same actor.
Article Details
- Event Type
- Malware distribution using fake GitHub repositories that exploit interest in the Claude Code source code leak
- Impact
- Zscaler reported that a repository attributed to the GitHub user idbzoomh distributed an archive containing a Rust executable that deploys Vidar and GhostSocks. The leak exposed 513,000 lines of Claude Code source code; users seeking the leak risk downloading the malware. Zscaler also observed frequent archive updates and a second repository it believed was likely operated by the same threat actor.
MITRE ATT&CK
Threat Actors
Malware
Vendors
AnthropicAnthropic accidentally exposed 513,000 lines of unobfuscated TypeScript via a 59.8 MB source map in an npm package.GitHubThreat actors are exploiting the Claude Code source code leak by posting fake GitHub repositories that deliver the Vidar information-stealing malware to users seeking the leak.
Products
Claude CodeThreat actors are exploiting the Claude Code source code leak by posting fake GitHub repositories that deliver the Vidar information-stealing malware to users seeking the leak.GitHubThreat actors are exploiting the Claude Code source code leak by posting fake GitHub repositories that deliver the Vidar information-stealing malware to users seeking the leak.