cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3801 articles

Security News · infostealers.com

Hudson Rock Offers Free Infostealer Monitoring Dashboard

Hudson Rock says its free dashboard can monitor up to three emails, usernames and domains for active infostealer infections, with real-time alerts that omit personally identifiable information.

Apr 2, 2026
Security News · elastic.co

AI-Assisted Monitor Flags Malicious Axios npm Releases

An Elastic engineer says an AI-assisted package-release monitor flagged malicious Axios npm releases that used a phantom dependency and postinstall hook to deploy malware. The article describes the response and recommends package monitoring and release delays.

Apr 2, 2026
Security News · securityweek.com

Cybersecurity M&A Roundup: 38 Deals Announced in March 2026

The roundup covers 38 cybersecurity-related M&A deals announced in March 2026, including acquisitions involving Ultra Cyber, Eos, Promptfoo and Kenzo Security, and the completion of Google’s $32 billion acquisition of Wiz.

Apr 2, 2026
Security News · bleepingcomputer.com

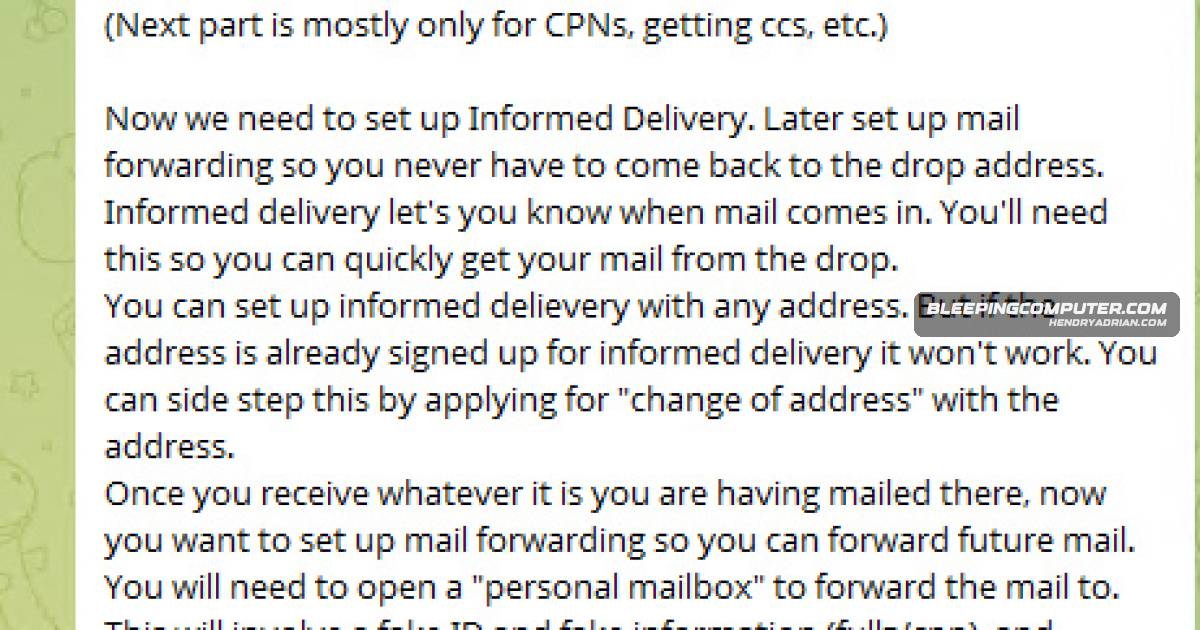
Fraud Tutorial Details Use of Vacant Homes to Intercept and Redirect Mail

Flare analysts describe a tutorial for using vacant homes, postal services, and fake identities to monitor and redirect mail for potential identity and financial fraud. The article recommends correlating address, forwarding, and identity signals to detect abuse.

Apr 2, 2026
Security News · thecyberexpress.com

FBI Warns Foreign-Developed Apps May Collect Extensive Data and Contain Malware

The FBI warns that some foreign-developed mobile apps may collect extensive device data, store it in jurisdictions with government-access laws, or contain malware. It recommends limiting permissions, using official app stores, updating devices and passwords, and alertly

Apr 2, 2026
Security News · securityonline.info

Researchers Say “ChatGPT Ad Blocker” Extension Harvested Conversations

A DomainTools investigation reported that a malicious Chrome extension copied ChatGPT conversation pages and sent prompts and metadata to a private Discord channel. The developer’s links to other AI services raise concerns, but do not establish those services also stole

Apr 2, 2026
Security News · dailydarkweb.net

313 Team Claims CVE-Based DDoS Disrupted Microsoft 365 for Five Hours

In an interview, 313 Team claimed it disrupted Microsoft 365 for over five hours using a CVE-based DDoS method. The group also claimed it is developing RATs, ransomware and stealers, and plans supply-chain operations; these assertions are not independently verified.

Apr 2, 2026
Security News · darkowl.com

Threat Intelligence Roundup Highlights Phishing, Spyware and Wiper Attacks

A weekly threat intelligence roundup covers credential-stealing phishing, Predator spyware research, APT-linked malware campaigns, a claimed wiper attack on Stryker, help-desk vishing recruitment, and attacks targeting government organizations.

Apr 2, 2026
Security News · securityonline.info

Anthropic Says Manual Deployment Error Exposed Claude Code Source

MAP files included in a Claude Code production package exposed source code and internal details. Anthropic’s DMCA notices led GitHub to remove over 8,100 repositories, while a Claude Code architect said the company will add automation and sanity checks.

Apr 2, 2026
Security News · securityweek.com

Linx Security Raises $50 Million for Identity Security Platform

Identity security startup Linx Security raised $50 million in a Series B round led by Insight Partners. The company says it will use the funding to develop its platform, expand sales and grow internationally.

Apr 2, 2026
Security News · bleepingcomputer.com

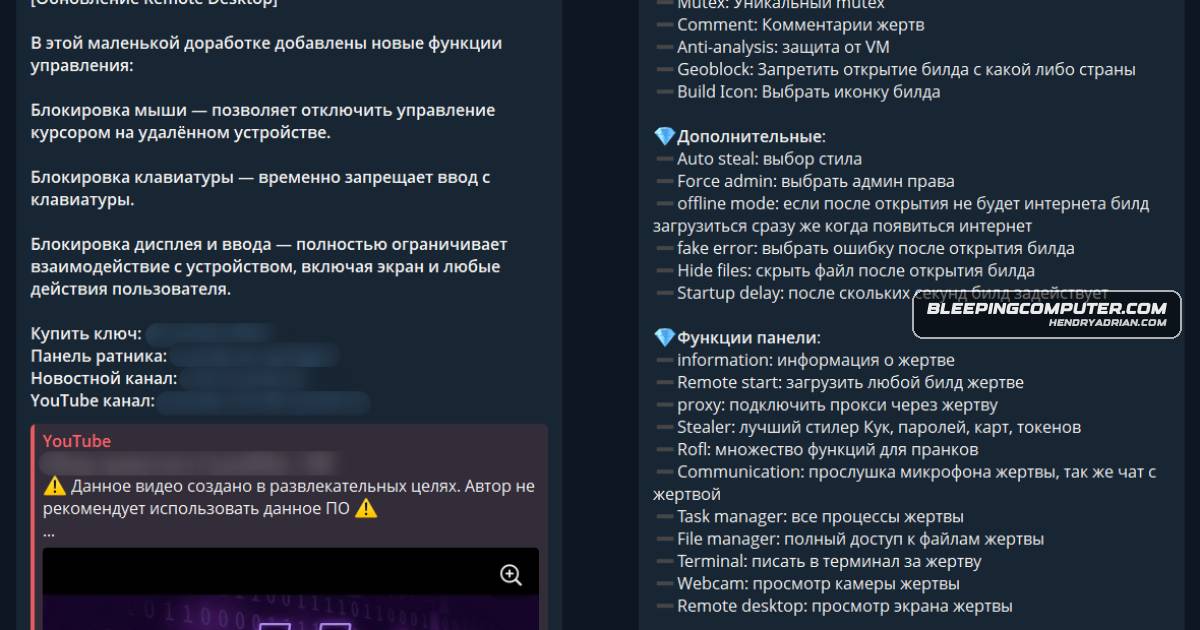
CrystalX MaaS Combines RAT, Stealer and Prankware Features

Kaspersky says CrystalX is a Telegram- and YouTube-promoted MaaS with remote access, keylogging, clipboard theft and prankware features. Its infostealer targets browsers and apps, but was temporarily disabled pending an upgrade.

Apr 2, 2026
Security News · thehackernews.com

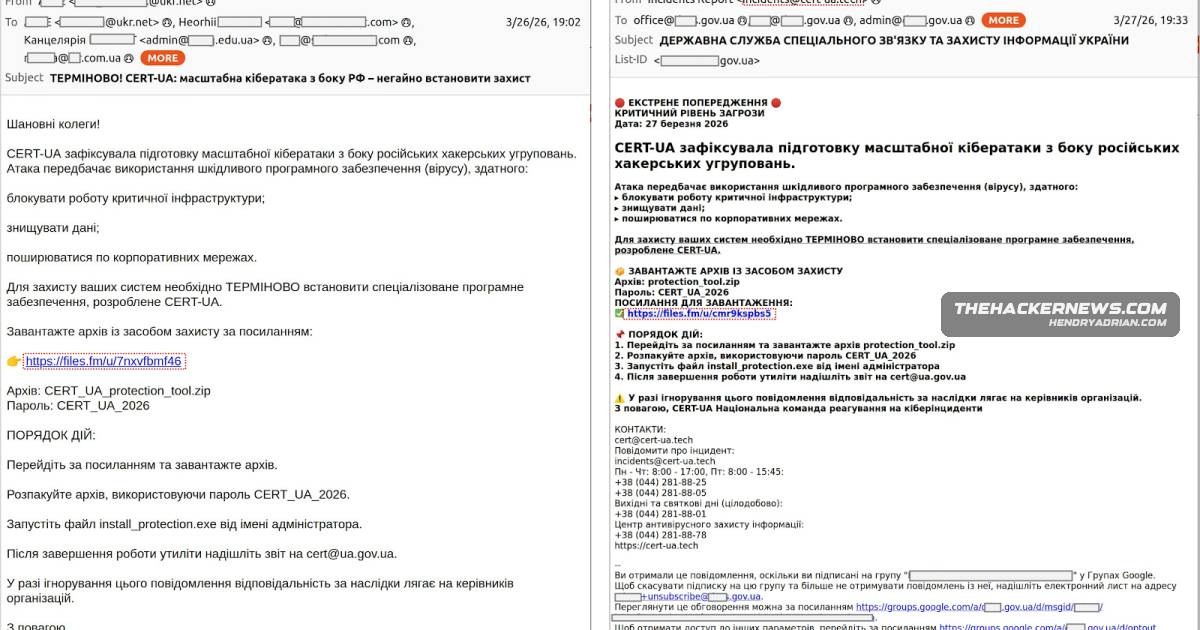
CERT-UA Reports Few Confirmed Infections in AGEWHEEZE Phishing Campaign

CERT-UA says a phishing campaign impersonating the agency used AGEWHEEZE malware, with only a few infections confirmed. Cyber Serp claimed far wider compromise, which the article does not independently verify.

Apr 2, 2026
Security News · team-cymru.com

Team Cymru Sees Increased Risknet Traffic Targeting Ivanti and Citrix Devices

Team Cymru reports increased traffic from Risknet-tagged IPs toward VPN and edge devices, with Ivanti and Citrix showing notable spikes. The activity signals elevated risk but does not confirm exploitation.

Apr 2, 2026
Security News · bleepingcomputer.com

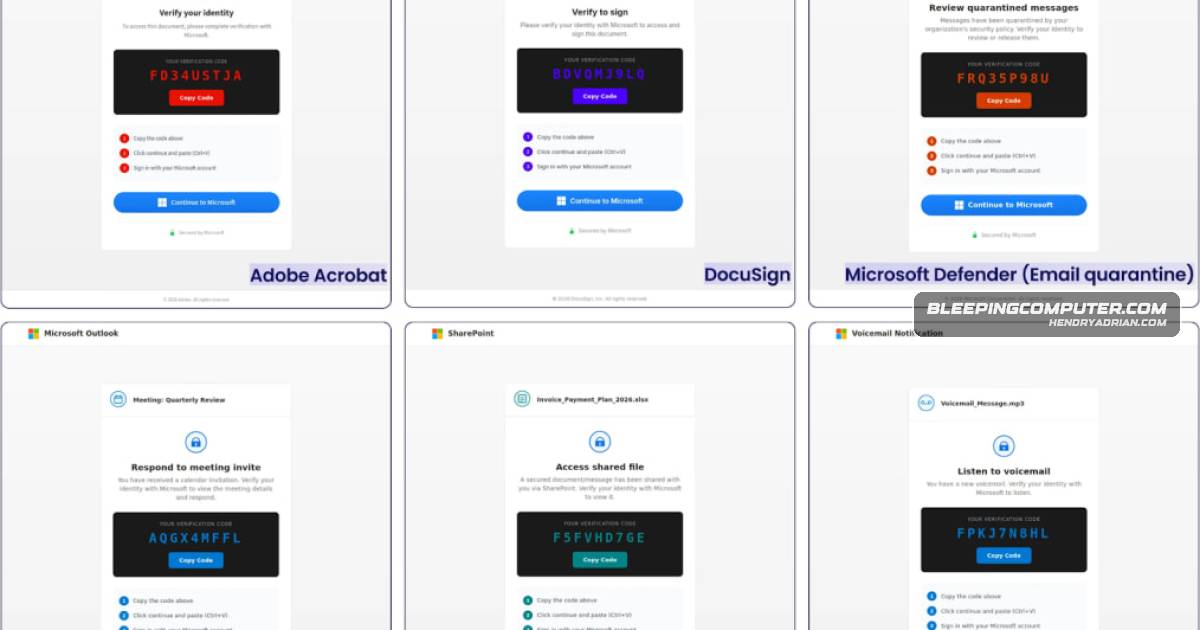
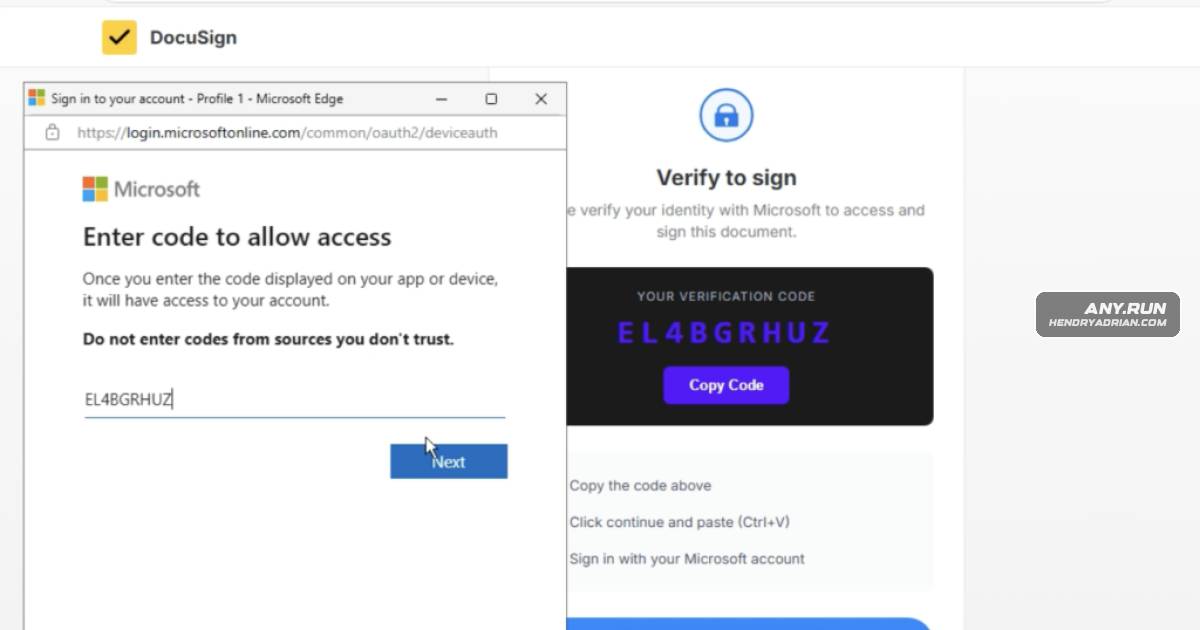
EvilTokens Phishing Kit Uses Microsoft Device Codes to Target Accounts

Sekoia observed EvilTokens campaigns using document-based lures and Microsoft’s device authorization flow to obtain account tokens. The phishing-as-a-service kit supports BEC automation, and Sekoia shared IoCs and YARA rules for defenders.

Apr 1, 2026
Security News · bleepingcomputer.com

Apple expands iOS 18.7.7 availability to protect more devices from DarkSword

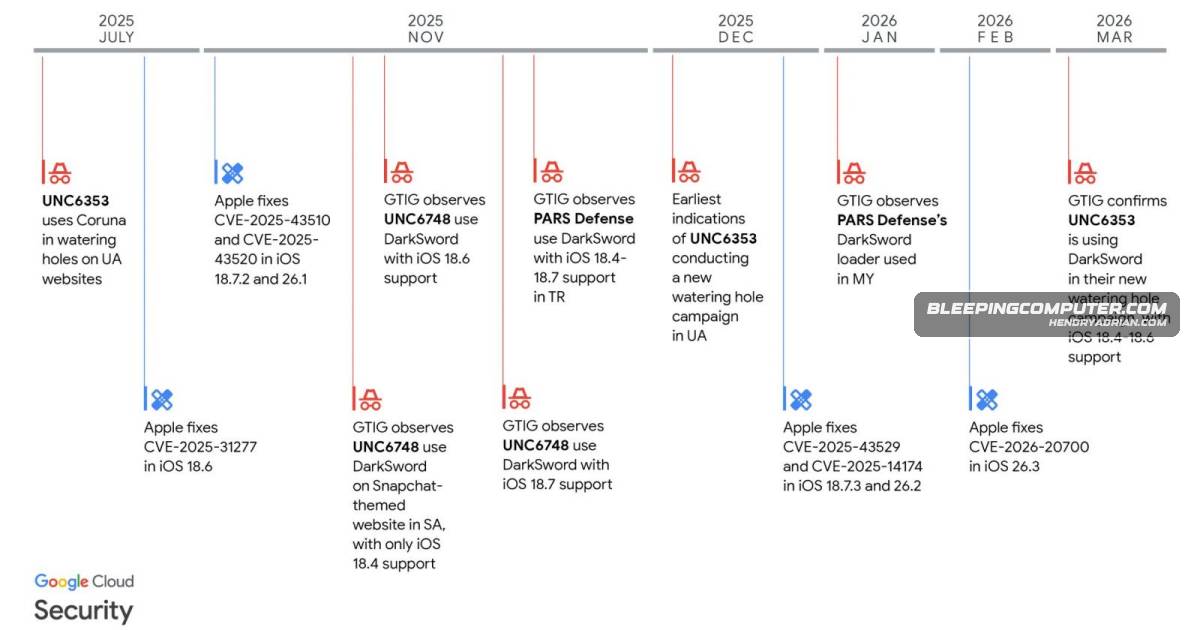
Apple expanded iOS 18.7.7 availability so more devices staying on iOS 18 can receive protections against the actively exploited DarkSword kit. Researchers linked the kit to six CVEs and deployments of infostealers and backdoors.

Apr 1, 2026
Security News · securityweek.com

Depthfirst Raises $80 Million and Launches Smart-Contract Security Model

Depthfirst raised $80 million in Series B funding and launched Dfs-mini1, a security model focused on cryptocurrency smart contracts. The company says its training approach can generalize to other security domains.

Apr 1, 2026
Security News · securityweek.com

DeepLoad Malware Uses ClickFix to Target Windows Systems

ReliaQuest reports the first in-the-wild campaign distributing DeepLoad to Windows systems via ClickFix. The malware uses a PowerShell loader, process injection and credential-stealing components; USB spread was also observed, though its source is unclear.

Apr 1, 2026
Security News · securityweek.com

FBI Warns of Data Security Risks From Foreign-Developed Mobile Apps

The FBI warned that some foreign-developed mobile apps may collect personal information, store data in China or contain malware capable of exploiting OS vulnerabilities and enabling unauthorized access. It advised users to report suspicious activity to IC3.

Apr 1, 2026
Security News · securityweek.com

US Charges Jonathan Spalletta Over Alleged Uranium Finance Hacks

Jonathan Spalletta was charged over alleged 2021 exploits of Uranium Finance’s smart contracts, including a $53.3 million withdrawal across 26 pools. The indictment alleges laundering and extortion; authorities previously seized about $31 million.

Apr 1, 2026
Security News · therecord.media

Romania Faces More Than 10,000 Daily Cyberattack Attempts, Defense Minister Says

Romania’s defense minister says public institutions face more than 10,000 cyberattack attempts daily. Officials cite Russian-linked operations, ransomware incidents affecting water and energy sectors, and disinformation campaigns.

Apr 1, 2026
Security News · any.run

ANY.RUN’s March 2026 Roundup Details OAuth Phishing, ClickFix and More

ANY.RUN’s March 2026 roundup describes threats including OAuth token phishing, macOS ClickFix delivering AMOS Stealer and a backdoor, registry-staged OrcusRAT, Magecart skimming, SVG phishing, DDoS botnets and MicroStealer.

Apr 1, 2026
Security News · bleepingcomputer.com

FBI Warns of Privacy and Data-Security Risks in Foreign Mobile Apps

The FBI warned that some foreign-developed mobile apps may collect extensive personal data, including through default permissions, and urged users to limit data sharing, update devices, use verified apps, and report suspected compromises to IC3.

Apr 1, 2026
Security News · thehackernews.com

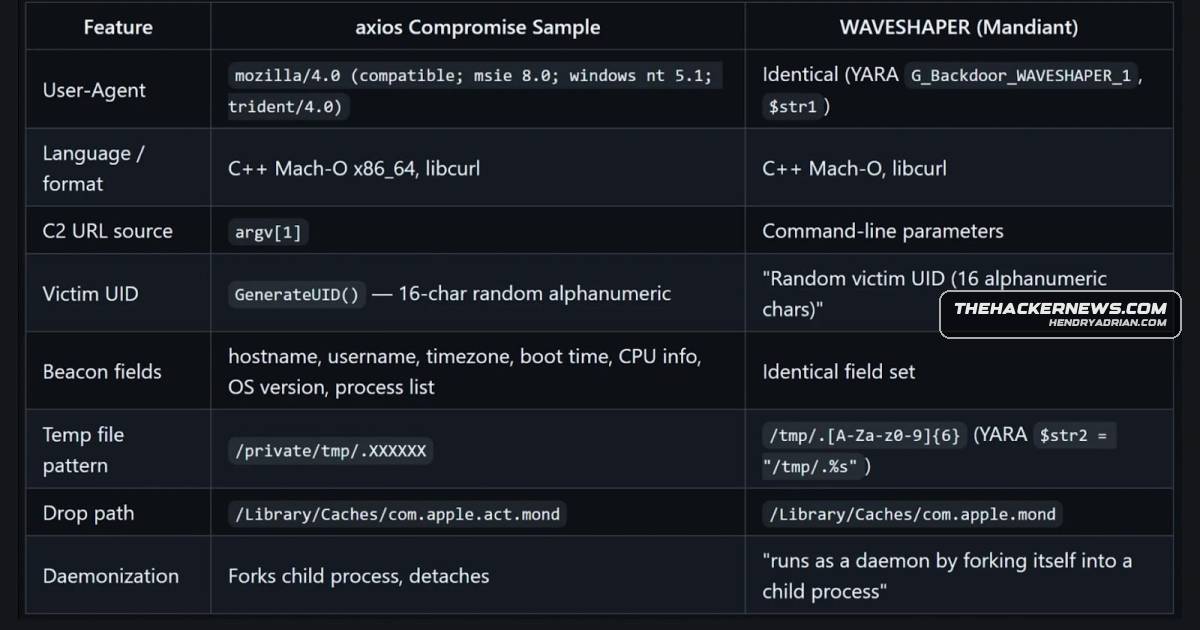
Google Attributes Axios npm Supply-Chain Attack to UNC1069

Google GTIG attributes the Axios npm supply-chain compromise to suspected North Korean cluster UNC1069. Trojanized releases added plain-crypto-js, which ran SILKBELL and delivered the WAVESHAPER.V2 backdoor to Windows, macOS, and Linux; Google says the impact remains [1

Apr 1, 2026
Security News · securityonline.info

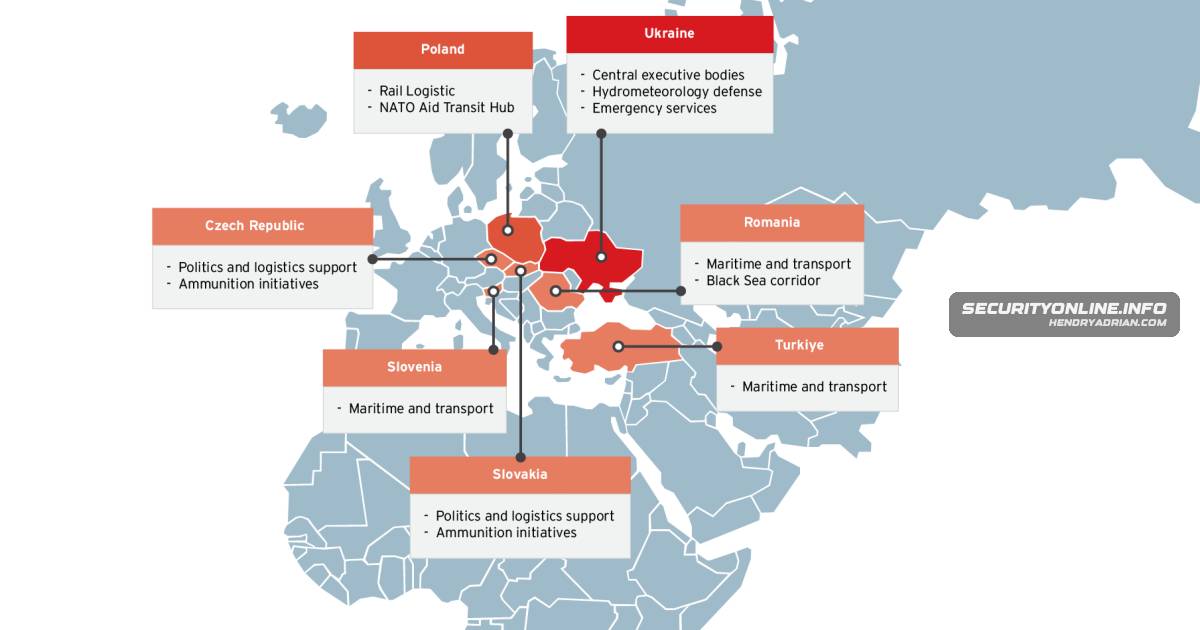
Trend Micro Reports Pawn Storm PRISMEX Campaign Targeting NATO Logistics

Trend Micro reports that Pawn Storm used the PRISMEX malware suite in early 2026 against Ukrainian defense and Western military-aid logistics, exploiting two Microsoft vulnerabilities and using steganography, COM hijacking, fileless execution and Filen[.]io for C2.

Apr 1, 2026
PreviousPage 123 of 159 Next
© 2026 cyber.hendryadrian.com