
ThreatsDay Roundup Covers ShareFile RCE Flaws, Android Rootkit and CloudTrail Evasion
Summary
The roundup reports ShareFile RCE flaws, Android NoVoice, researchers’ findings of unpatched ImageMagick RCE flaws and CloudTrail evasion, alongside supply-chain abuse, phishing, ransomware defenses and malware updates.
Key points
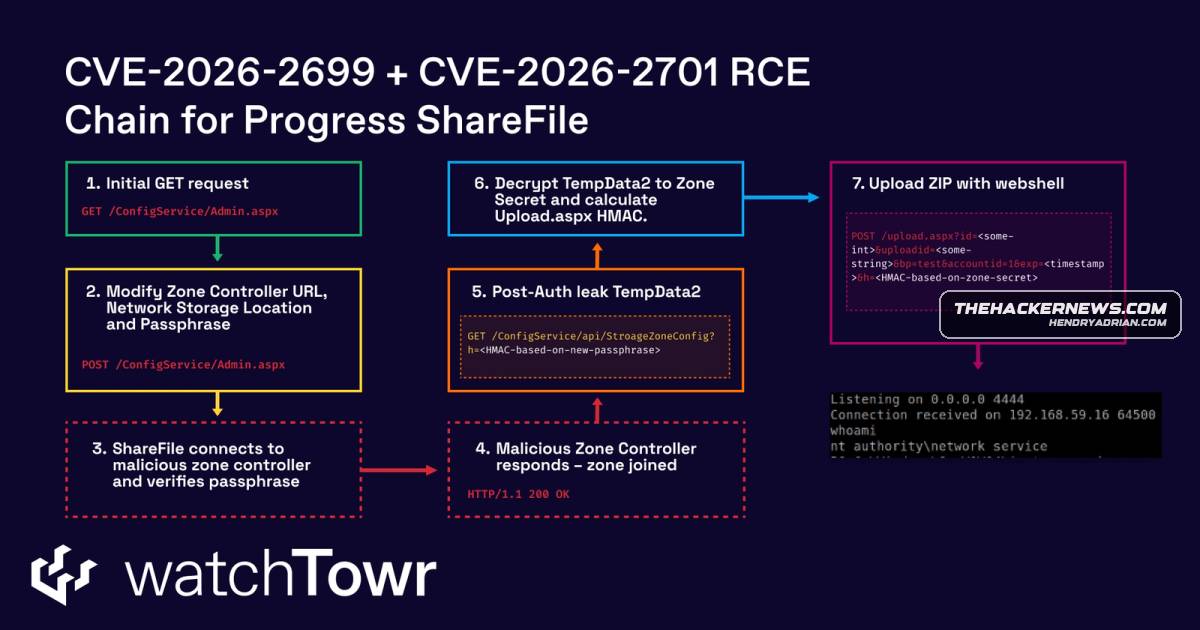
- WatchTower Labs disclosed ShareFile flaws CVE-2026-2699 and CVE-2026-2701 that can be chained for pre-authenticated RCE; Progress released fixes in Storage Zone Controller 5.12.4.
- McAfee Labs said NoVoice was distributed through more than 50 apps with at least 2.3 million downloads and attempted to exploit 22 older Android vulnerabilities for root access; Google removed the apps.
- Pwn.ai reported multiple unpatched ImageMagick zero-days that could be chained for RCE through a single image or PDF upload, affecting major Linux distributions and WordPress installations.
- Abstract Security described attackers chaining lesser-known AWS APIs to disrupt CloudTrail logging, halt or delete event data, and evade detection.
- Endor Labs reported a 13.6-fold increase in open-source malware advisories since January 2024; 930 of 1,011 npm account-takeover advisories in the OSV database were filed in 2025.
- Google made Drive ransomware detection and file restoration generally available; the company said its latest model detects 14 times more infections than the beta version.
- Darktrace reported continued GhostSocks activity, including a case in which it operated alongside Lumma Stealer; JFrog reported that LofyGang’s fake npm package undicy-http delivers a RAT and a Windows credential-stealing payload.
Article Details
- Event Type
- Cybersecurity threat roundup covering vulnerabilities, malware distribution, phishing, supply-chain abuse, cloud audit-log evasion, and cybercrime.
- Impact
- The reported threats include a pre-authentication remote-code-execution chain affecting Progress ShareFile, an Android rootkit distributed through apps downloaded more than 2.3 million times, credential theft and account takeover, malicious packages targeting software supply chains, and techniques to impair AWS CloudTrail visibility. Multiple ImageMagick zero-days were reported as enabling remote code execution and remaining unpatched at the time of writing.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | xss[.]is | Underground forum where GhostSocks was reportedly marketed as malware-as-a-service. |
MITRE ATT&CK
CVE
CVE-2026-2699Progress · ShareFile Storage Zones ControllerWatchTower Labs disclosed a pre-auth RCE chain in Progress ShareFile (CVE-2026-2699 and CVE-2026-2701) with fixes in Storage Zone Controller 5.12.4 affecting ~30,000 instances.CVE-2026-2701Progress · ShareFile Storage Zones ControllerWatchTower Labs disclosed a pre-auth RCE chain in Progress ShareFile (CVE-2026-2699 and CVE-2026-2701) with fixes in Storage Zone Controller 5.12.4 affecting ~30,000 instances.
People
Threat Actors
Chen ZhiAccording to Xinhua, Chen Zhi masterminded a transnational cybercrime syndicate. The article says he was indicted in the U.S. for operating forced-labor pig-butchering scam compounds; these are reported allegations, not independently confirmed findings in the article.Li XiongThe article says Li Xiong is accused of being a key member of the transnational cybercrime syndicate associated with Chen Zhi. He was extradited to China; the reported accusations are not presented as confirmed findings.LofyGangThe article reports that LofyGang resurfaced with a fake npm package, undicy-http, delivering a RAT and a Windows payload for credential theft and data exfiltration.
Malware
GhostSocksGhostSocks activity intensifiesLumma Stealer“In one notable case from December 2025, Darktrace detected GhostSocks operating alongside Lumma Stealer, reinforcing that the partnership between Lumma and GhostSocks remains active despite recent attempts to disruptNoVoiceQuick checks are advised because threats like the NoVoice Android rootkit and unpatched ImageMagick zero-days can silently escalate from small bugs into widescale compromises.TriadaNoVoice has been found to share some level of overlap with Triada.XLoaderXLoader boosts stealth tactics
Vendors
Amazon Web ServicesAttackers are bypassing AWS CloudTrail by chaining obscure APIs to erase evidence and create “invisible activity zones” that blind logging systems.Appleemails impersonating ChatGPT and Gemini to push users into downloading malicious iOS apps from the Apple App Store.GoogleGoogle has since removed the apps. The highest concentration of infections has been reported in Nigeria, Ethiopia, Algeria, India, and Kenya.MetaCybercriminals have set their sights on Android users through a new phishing scheme that disguises malicious applications as beta-testing opportunities for ChatGPT and Meta advertising tools.Progress SoftwareWatchTower Labs disclosed a pre-auth RCE chain in Progress ShareFile (CVE-2026-2699 and CVE-2026-2701) with fixes in Storage Zone Controller 5.12.4 affecting ~30,000 instances.
Products
AndroidQuick checks are advised because threats like the NoVoice Android rootkit and unpatched ImageMagick zero-days can silently escalate from small bugs into widescale compromises.App Storeemails impersonating ChatGPT and Gemini to push users into downloading malicious iOS apps from the Apple App Store.AWS CloudTrailAttackers are bypassing AWS CloudTrail by chaining obscure APIs to erase evidence and create “invisible activity zones” that blind logging systems.FacebookIn these attacks, what appears to be an invitation to advertising apps turns out to be a carefully planned attempt to steal Facebook credentials and hijack control of user accounts.Firebase App Distribution“These messages push malicious apps delivered through ‘[email protected]’ via Firebase App Distribution, a legitimate Google service for distributing pre-release apps to testers,” LevelBlue said.ImageMagickQuick checks are advised because threats like the NoVoice Android rootkit and unpatched ImageMagick zero-days can silently escalate from small bugs into widescale compromises.npmOpen-source supply chain abuse surged (13.6x increase), with npm account takeovers and malicious packages targeting widely used libraries and CI/CD pipelines.Progress ShareFileWatchTower Labs disclosed a pre-auth RCE chain in Progress ShareFile (CVE-2026-2699 and CVE-2026-2701) with fixes in Storage Zone Controller 5.12.4 affecting ~30,000 instances.ShareFile Storage Zone ControllerWatchTower Labs disclosed a pre-auth RCE chain in Progress ShareFile (CVE-2026-2699 and CVE-2026-2701) with fixes in Storage Zone Controller 5.12.4 affecting ~30,000 instances.WhatsAppOne of the targeted apps is WhatsApp, which enabled the malware to harvest data from the app as soon as it was launched.WordPressMultiple zero-days in ImageMagick can be chained for remote code execution via single image/PDF uploads, affecting major Linux distros and WordPress and remaining unpatched.
Countries
AlgeriaThe highest concentration of infections has been reported in Nigeria, Ethiopia, Algeria, India, and Kenya.Chinato their servers.” The malware avoids infecting devices in certain regions, like Beijing and Shenzhen in China, and implements more than a dozen checks for emulators, debuggers, and VPNs.EthiopiaThe highest concentration of infections has been reported in Nigeria, Ethiopia, Algeria, India, and Kenya.IndiaThe highest concentration of infections has been reported in Nigeria, Ethiopia, Algeria, India, and Kenya.KenyaThe highest concentration of infections has been reported in Nigeria, Ethiopia, Algeria, India, and Kenya.NigeriaThe highest concentration of infections has been reported in Nigeria, Ethiopia, Algeria, India, and Kenya.United StatesThe U.S. Federal Bureau of Investigation (FBI) is warning of the data security risks associated with foreign-developed mobile applications.