
React2Shell Campaign Harvested Credentials from 766 Hosts, Cisco Talos Says
Summary
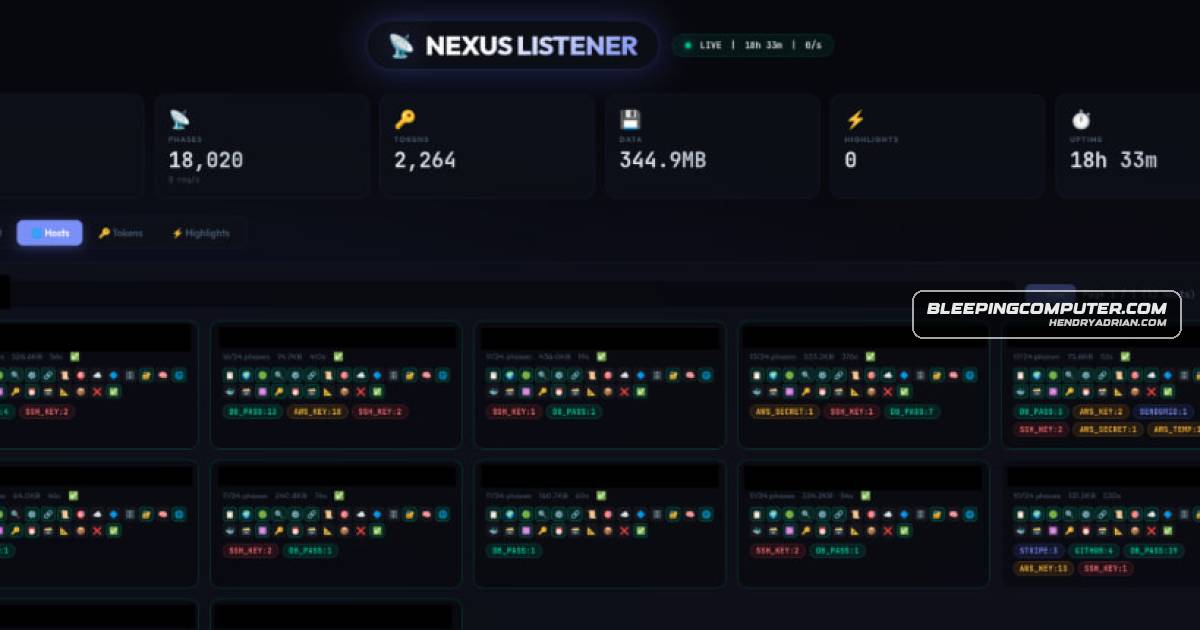
Cisco Talos says attackers exploited React2Shell in Next.js apps, using NEXUS Listener to harvest secrets from at least 766 hosts in 24 hours. The researchers attribute the campaign to UAT-10608 and recommend patching and credential rotation.
Key points
- Cisco Talos reports that the campaign exploited React2Shell (CVE-2025-55182) in vulnerable Next.js applications.
- The researchers say at least 766 cloud-hosted systems were compromised within 24 hours.
- Harvested data reportedly included environment secrets, SSH keys, API keys, cloud credentials, database credentials, and Kubernetes tokens.
- Attackers used an automated framework named NEXUS Listener to collect data and send it in chunks over HTTP to a command-and-control server.
- Cisco Talos attributes the activity to the UAT-10608 threat cluster after analyzing an exposed NEXUS Listener instance.
- Recommended defenses include applying React2Shell security updates, rotating credentials, enforcing AWS IMDSv2, enabling secret scanning, and using WAF/RASP and least-privilege controls.
Article Details
- Event Type
- Automated credential-theft campaign exploiting React2Shell in vulnerable Next.js applications
- Impact
- Cisco Talos reports that the campaign compromised at least 766 hosts within 24 hours and harvested environment secrets, SSH keys, API keys, cloud tokens, database credentials, and other sensitive data. The stolen credentials could enable cloud-account takeover, access to databases and other services, and lateral movement; the article also warns of potential supply-chain and privacy-law consequences.