
Device Code Phishing Surges 37.5x as New Kits Spread
Summary
Push Security reports a 37.5x increase in device code phishing this year, with at least 11 kits using SaaS-themed lures. It recommends disabling the flow when unnecessary and monitoring authentication logs.
Key points
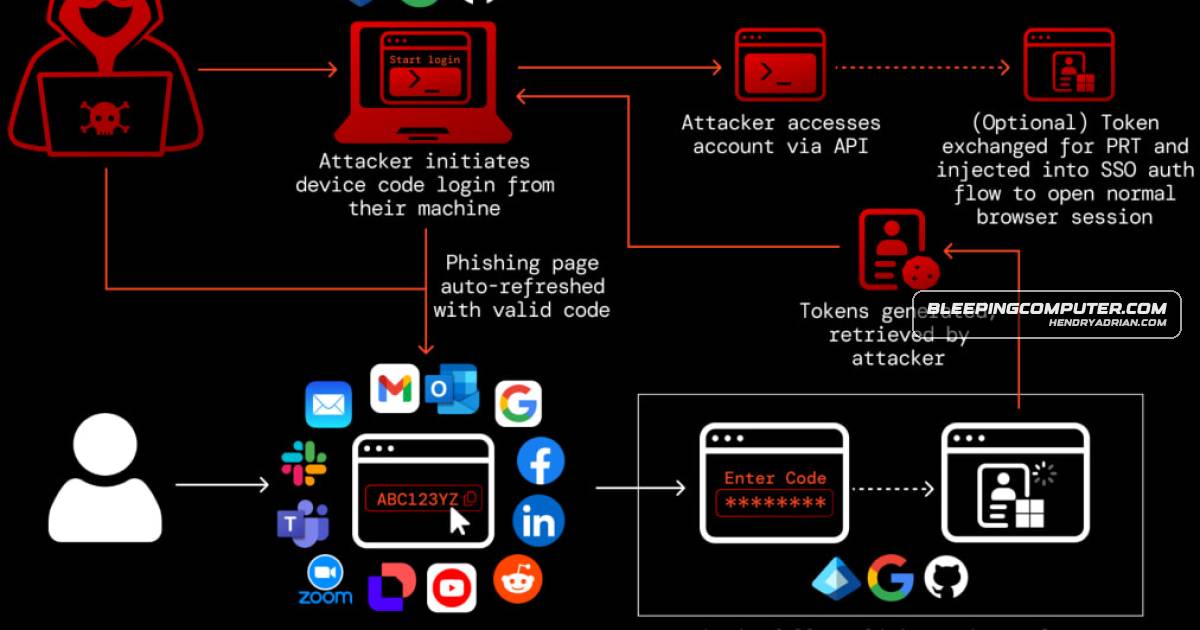
- Attackers trick victims into entering an attacker-requested device code on a legitimate login page, authorizing the attacker’s device with access and refresh tokens.
- Push Security says detected device code phishing pages rose 37.5x this year, up from a 15x increase reported at the start of March 2026.
- EvilTokens is described as the most prominent kit; the article identifies at least 10 other kits offering the technique.
- The kits use realistic SaaS-themed lures, anti-bot protections, and cloud-hosted infrastructure to scale their campaigns.
- Push Security recommends disabling device authorization when it is not needed and monitoring for unexpected device-code authentication events, unusual IP addresses, and sessions.
Article Details
- Event Type
- Reported surge in OAuth 2.0 Device Authorization Grant phishing, enabled by phishing-as-a-service kits.
- Impact
- Push Security reported that detected device-code phishing pages increased 37.5x in 2026. Victims who enter attacker-requested codes on legitimate login pages can authorize attackers to obtain access and refresh tokens, enabling persistent account access.
MITRE ATT&CK
Products
Tools
AUTHOVAUTHOV – A workers.dev-hosted kit using popup-based device code entry and Adobe document-sharing lures.CLURECLURE – A kit using rotating API endpoints and an anti-bot gate, with SharePoint-themed lures and backend infrastructure on DigitalOcean.DCSTATUSDCSTATUS – A minimal kit with generic Microsoft 365 “Secure Access” lures and limited visible infrastructure markers.DOCUPOLLDOCUPOLL – A kit hosted on GitHub Pages and workers.dev that mimics DocuSign workflows, including injected replicas of real pages.DOLCEDOLCE – A Microsoft PowerApps-hosted kit with Dolce & Gabbana–themed lures, likely a one-off or red-team-style implementation rather than widely used.EvilTokensPhishing-as-a-service kits—most notably EvilTokens—have democratized the technique with realistic SaaS-themed lures and cloud-hosted infrastructure, prompting recommendations to disable the flow when not needed and toFLOW_TOKENFLOW_TOKEN – A workers.dev-hosted kit using Tencent Cloud backend infrastructure, with HR and DocuSign-themed lures and popup-based flows.LINKIDLINKID – A kit leveraging Cloudflare challenge pages and self-hosted APIs, using Microsoft Teams and Adobe-themed lures.PAPRIKAPAPRIKA – An AWS S3–hosted kit using Microsoft login clone pages with Office 365 branding and a fake Okta footer.SHAREFILESHAREFILE – A kit themed around Citrix ShareFile document transfers, using node-based backend endpoints to simulate file sharing and trigger device code flows.VenomVENOM – A closed-source PhaaS kit offering both device code phishing and AiTM capabilities.