cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3800 articles

Security News · bleepingcomputer.com

CloudZ RAT Plugin Pheno Hijacks Microsoft Phone Link to Steal SMS and OTPs

Cisco Talos reports that CloudZ’s Pheno plugin can access Phone Link’s local SQLite database to steal SMS and OTP messages. A fake ScreenConnect update deploys loaders that install the RAT and establish persistence.
May 5, 2026
Security News · bleepingcomputer.com

Karakurt Extortion Negotiator Deniss Zolotarjovs Sentenced to 8.5 Years

Deniss Zolotarjovs was sentenced to 8.5 years in the U.S. after pleading guilty to wire-fraud and money-laundering conspiracy. The FBI linked him to at least six extortion cases, where stolen personal and children's health data was used to pressure victims.

May 5, 2026
Security News · infostealers.com

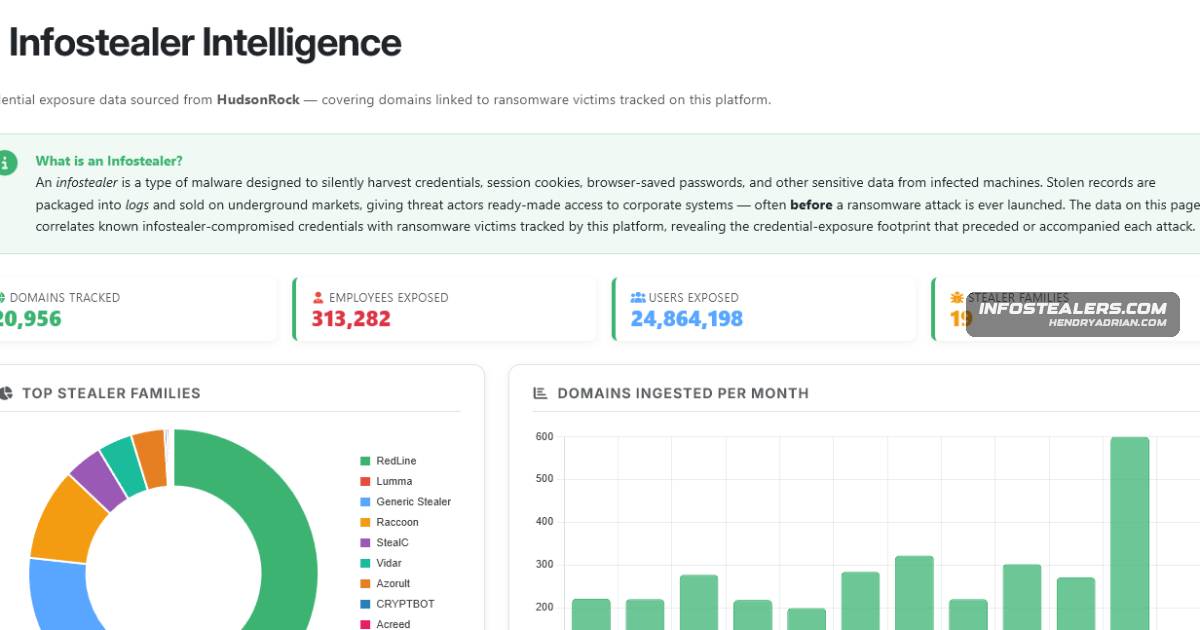
Hudson Rock and Ransomware.live Launch Dashboard Linking Infostealer Infections to Ransomware

Hudson Rock and Ransomware[.]live launched a dashboard correlating infostealer data with publicly claimed ransomware victims. Hudson Rock says its investigation linked stolen credentials to the “Coinbase Cartel” and ransomware deployments at more than 100 companies.

May 5, 2026
Security News · elastic.co

Elastic Workflows 9.4 Reaches General Availability With Security Automation Features

Elastic says Workflows is generally available in 9.4, adding 25 case-management steps, human approval checkpoints, AI-assisted YAML authoring, reusable workflows, event-driven triggers, execution history, and execution-based pricing.

May 5, 2026
Security News · thehackernews.com

Weekly Cybersecurity Recap: Active cPanel and Linux Exploits, Supply-Chain Attacks and New Malware

This weekly roundup covers active exploitation of cPanel CVE-2026-41940 and Linux Copy Fail (CVE-2026-31431), TeamPCP supply-chain attacks, SaaS-focused vishing, a GitHub RCE disclosure, new malware and other security developments.

May 4, 2026
Security News · bleepingcomputer.com

Kaspersky Reports Phishing Abuse of Amazon SES Using Exposed AWS Keys

Kaspersky reports that attackers are using exposed AWS keys to send convincing phishing through Amazon SES, with campaigns including DocuSign-themed lures and BEC scams. It recommends tighter IAM controls, MFA, key rotation, and IP restrictions.

May 4, 2026
Security News · cyberscoop.com

Meete Sued Over Alleged Misuse of TikTok Video in Geofenced Ads

A University of Tennessee student alleges Meete used her TikTok video in misleading ads targeted near her dorm. She is suing companies behind the app, seeking $750,000 and ad revenue, and says the ads harmed her reputation and safety.

May 4, 2026
Security News · cisecurity.org

More Than 5,000 SLTT Organizations Join Member-Funded MS-ISAC

Following the end of federal funding for SLTT cybersecurity efforts through MS-ISAC in 2025, more than 5,000 organizations have joined its member-funded model, while legacy members can stay connected through MS-ISAC Connect.

May 4, 2026
Security News · securityweek.com

Cisco Plans to Acquire Astrix Security to Address Non-Human Identity Risks

Cisco announced plans to acquire Astrix Security, whose technology is designed to discover and secure non-human identities and AI agents. Cisco plans to integrate its capabilities into its security platform; Calcalist reports a roughly $400 million deal value.

May 4, 2026
Security News · bleepingcomputer.com

Malicious PyTorch Lightning 2.6.3 Package Delivered Credential-Stealing Payload

PyTorch Lightning 2.6.3 on PyPI ran a credential-stealing payload on import. Microsoft Defender detected and blocked activity affecting a small number of devices; the package was reverted to 2.6.1, and users are advised to rotate secrets.

May 4, 2026
Security News · bleepingcomputer.com

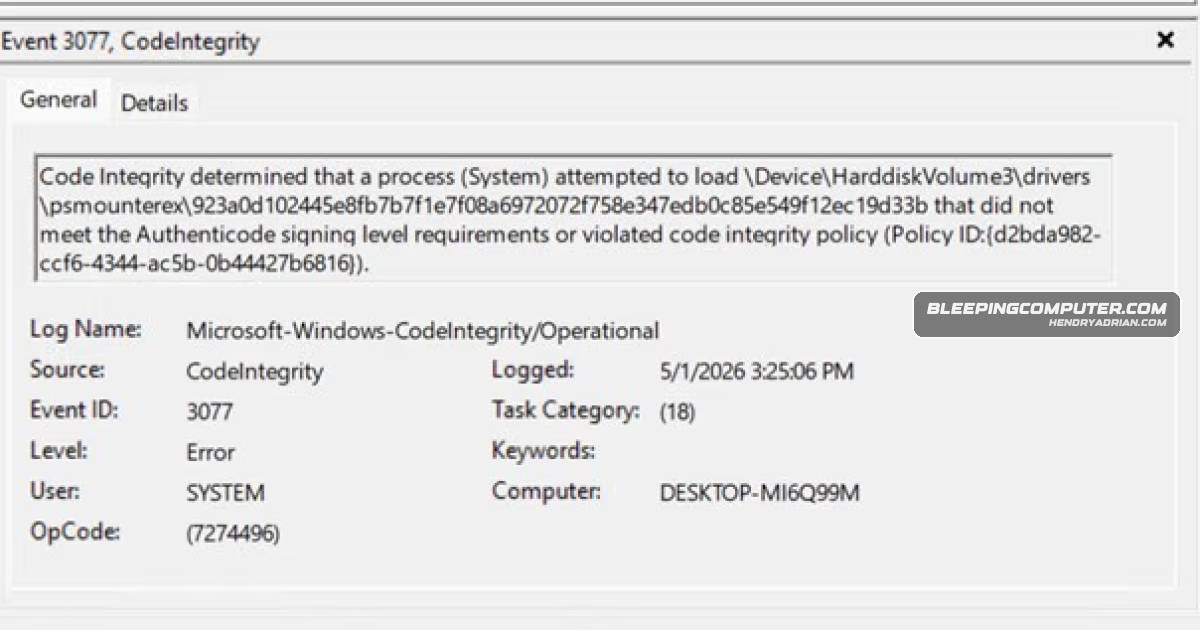
Microsoft Confirms April Windows Updates Block Driver Used by Backup Apps

Microsoft says April 2026 updates block psmounterex.sys to mitigate CVE-2023-43896, causing some VSS-based backup apps to fail when mounting or browsing images. It recommends updating affected apps rather than pausing the Windows update.

May 4, 2026
Security News · securityweek.com

33 Cybersecurity M&A Deals Announced in April 2026

Thirty-three cybersecurity M&A deals were announced in April 2026, including Airbus–Quarkslab, Cyera–Ryft, Palo Alto Networks–Portkey, and Socket–Secure Annex, expanding capabilities in AI security, OT monitoring, and software supply-chain protection.

May 4, 2026
Security News · wiz.io

Wiz for Microsoft 365 Reaches General Availability with SaaS Risk Visibility and Remediation

Wiz says its Microsoft 365 security capabilities are generally available, linking posture, access, and data risks to its Security Graph. The product supports risk prioritization and remediation; Copilot Studio coverage remains in preview.

May 4, 2026
Security News · darkowl.com

April Threat Intelligence Roundup Highlights PLC Disruptions, Data Breaches and Malware Campaigns

A roundup of eight cybersecurity stories covers attacks on critical infrastructure, email and data breaches, credential theft, crypto scams, and malware targeting energy and water systems.

May 4, 2026
Security News · keplernewsletter.substack.com

Privacy and Cybersecurity Policy Updates Span Cloud Sovereignty, Crisis Response and Data Protection

The roundup covers Germany’s C3A cloud-sovereignty framework, Belgium’s updated cyber-crisis plan, and privacy and AI policy developments in the UK, Poland, France and the U.S., including new bills, guidance and enforcement trends.

May 3, 2026
Security News · securityweek.com

Bluekit Phishing Kit Adds AI Assistant and Automated Domain Setup

Varonis reports that Bluekit combines phishing-page management, domain setup and session-data collection, with an AI assistant that produced only a placeholder-filled campaign draft when tested. The kit has not been used in a live campaign.

May 2, 2026
Security News · biv.com

B.C. Judge Certifies Class Action Over TransLink Ransomware Breach

A B.C. judge certified a class action covering 38,958 people whose personal data TransLink confirmed was accessed in a 2020 ransomware incident. Whether TransLink violated its duty to safeguard the data remains for trial.

May 2, 2026
Security News · therecord.media

Two Incident Responders Sentenced for Covert ALPHV/BlackCat Extortion Attacks

Two incident responders received four-year sentences after pleading guilty to an extortion conspiracy tied to covert ALPHV/BlackCat attacks. Prosecutors said the scheme yielded $1.2 million and led to a patient-data leak; DigitalMint added auditable negotiation controls

May 2, 2026
Security News · thehackernews.com

China-Linked Campaigns Target Asian Governments, Polish Organizations, Journalists and Activists

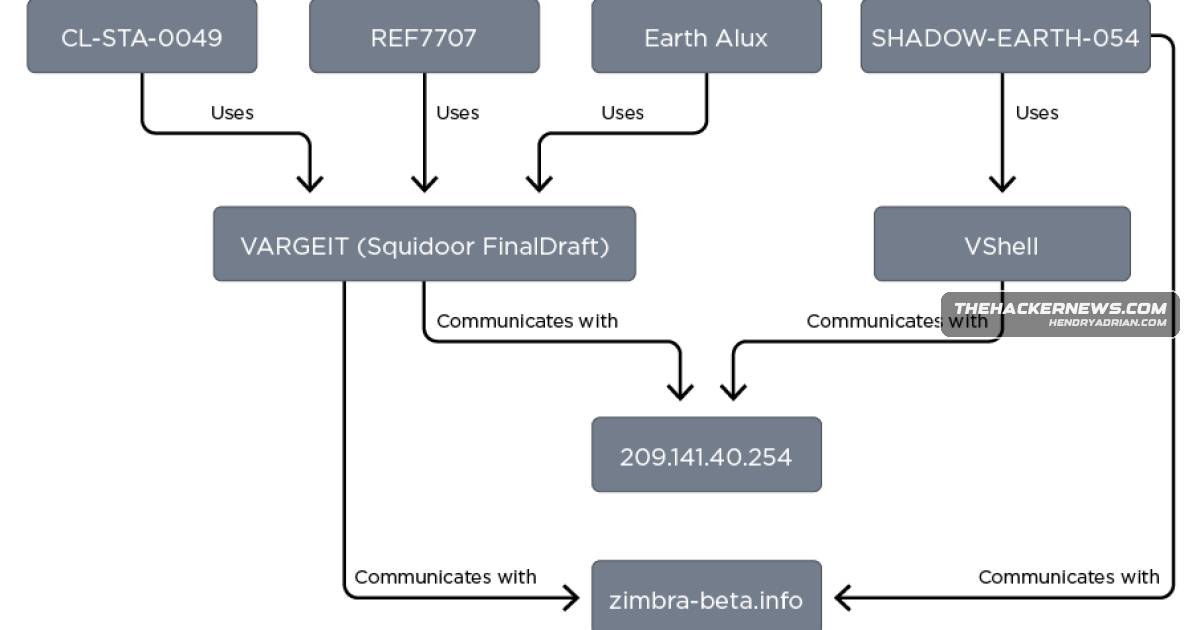
Trend Micro says SHADOW-EARTH-053 exploited Exchange and IIS flaws to target government and defense organizations across Asia and Poland. Citizen Lab separately documented China-linked phishing campaigns targeting journalists and activists.

May 1, 2026
Security News · thehackernews.com

AccountDumpling Phishing Campaign Reportedly Targets 30,000 Facebook Accounts

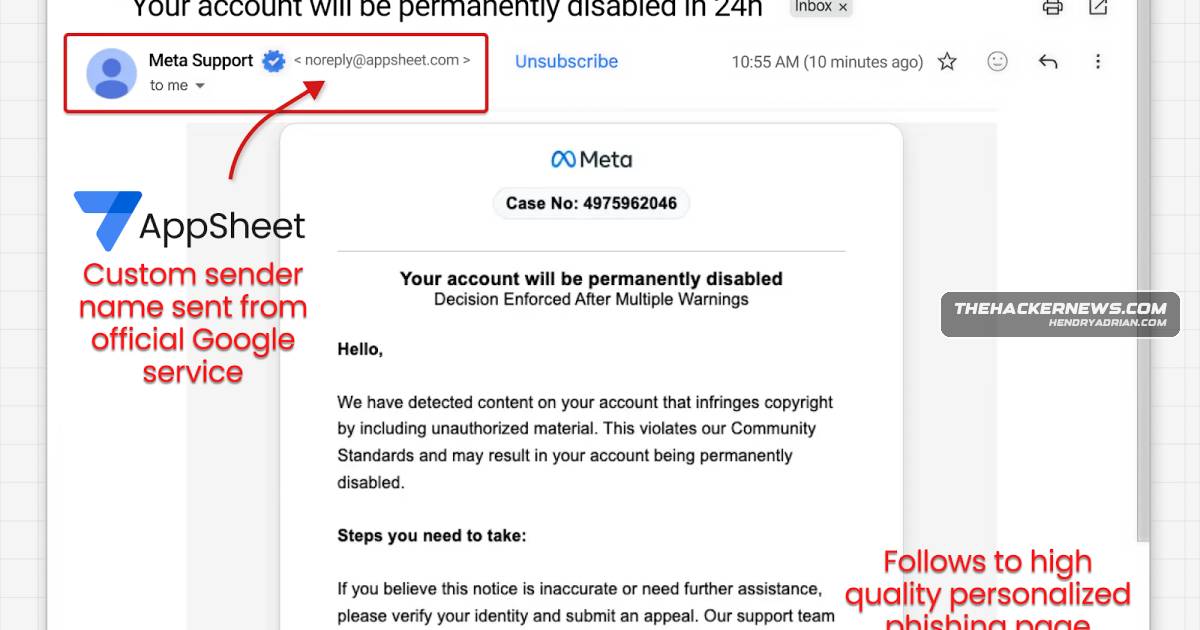
Guardio says the Vietnamese-linked AccountDumpling operation abuses Google AppSheet emails and varied phishing lures to steal Facebook credentials, 2FA codes and ID photos; associated Telegram channels held about 30,000 victim records.

May 1, 2026
Security News · cyberscoop.com

Five Allied Agencies Urge Safer Deployment of AI Agents

Cybersecurity agencies from five countries issued guidance on agentic AI risks, urging organizations to apply existing security frameworks, limit access, use cryptographic identities and require human approval for high-impact actions.

May 1, 2026
Security News · thehackernews.com

Cordial and Snarky Spider Use Vishing to Steal Data from SaaS Environments

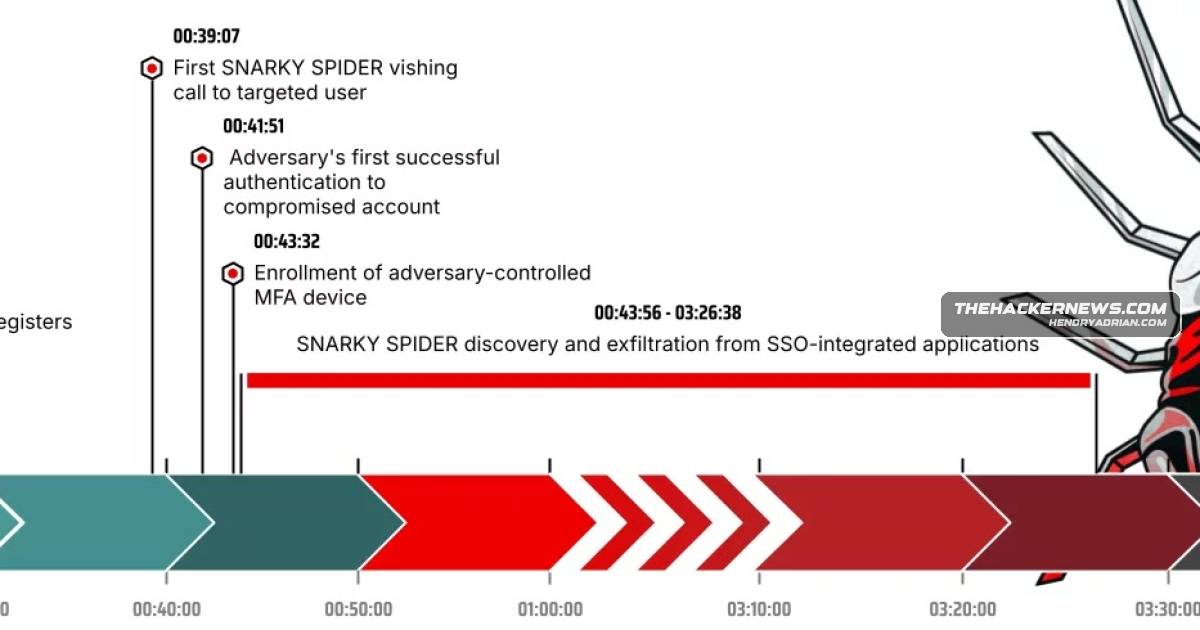
Researchers report that Cordial Spider and Snarky Spider use vishing and SSO-themed AiTM pages to steal credentials and MFA codes, then move through connected SaaS services to exfiltrate data for extortion.

May 1, 2026
Security News · bleepingcomputer.com

Microsoft Fixes Misrendered Remote Desktop Security Warnings in Windows

Microsoft’s optional KB5083631 preview update fixes Remote Desktop security warnings that could render incorrectly on multi-monitor systems with mixed scaling. The warnings were introduced in April 2026 updates to restrict risky resource redirections.

May 1, 2026
Security News · bleepingcomputer.com

Criminal IP Integrates Exposure Intelligence Into Securonix ThreatQ

Criminal IP and Securonix announced an integration that enriches ThreatQ IP indicators with exposure context, including maliciousness scores, VPN/proxy detection, open ports and vulnerability insights.

May 1, 2026
PreviousPage 107 of 159 Next
© 2026 cyber.hendryadrian.com