
Cordial and Snarky Spider Use Vishing to Steal Data from SaaS Environments
Summary
Researchers report that Cordial Spider and Snarky Spider use vishing and SSO-themed AiTM pages to steal credentials and MFA codes, then move through connected SaaS services to exfiltrate data for extortion.
Key points
- Cordial Spider and Snarky Spider are linked to rapid data-theft and extortion campaigns focused on SaaS environments.
- The groups reportedly use vishing to direct targets to SSO-themed adversary-in-the-middle phishing pages that capture credentials and MFA codes.
- Attackers register new devices, remove existing ones, and create inbox rules to suppress security notifications and maintain access.
- After obtaining elevated access, attackers reportedly search Google Workspace, HubSpot, SharePoint, and Salesforce for valuable files and reports.
- CrowdStrike says compromised identity-provider access can provide entry to multiple connected SaaS applications through one authenticated session.
- Unit 42 and RH-ISAC assessed with moderate confidence that CL-CRI-1116 is associated with The Com; they reported targeting of retail and hospitality since February 2026.
Article Details
- Event Type
- Cybercrime campaign involving vishing, SSO-themed adversary-in-the-middle phishing, and SaaS account abuse.
- Impact
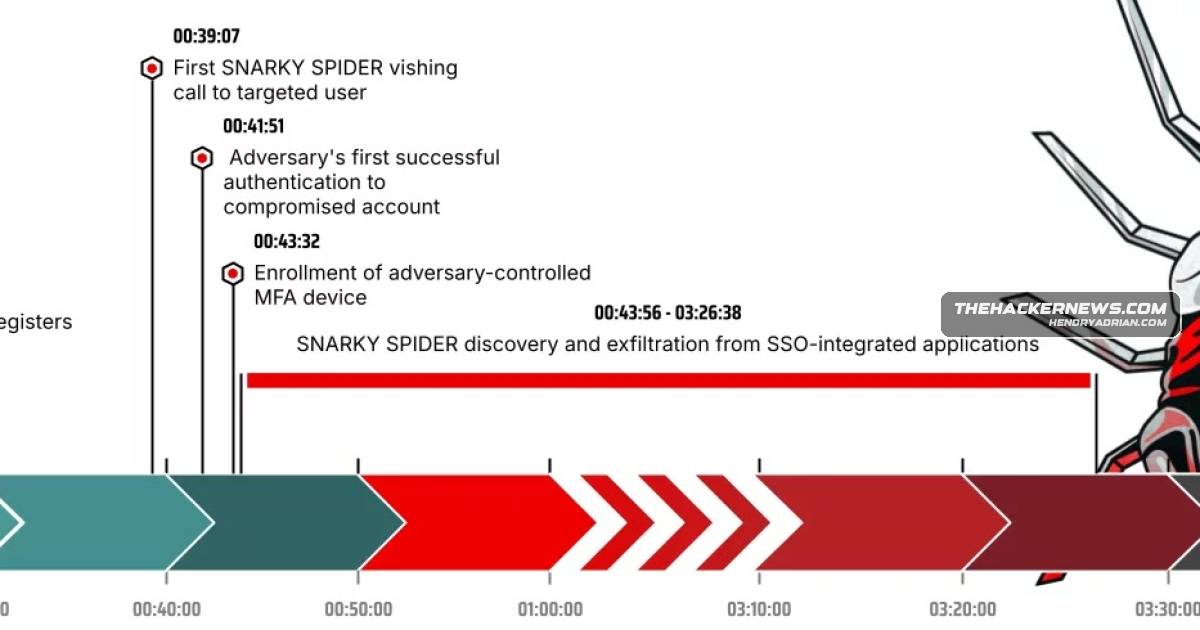
- Cordial Spider and Snarky Spider are reported to steal credentials and MFA codes, register devices to maintain access, suppress device-registration alerts, and move across connected SaaS applications to find and exfiltrate high-value data. Snarky Spider is reported to begin exfiltration in under an hour. The activity creates detection challenges by operating largely within trusted SaaS environments and leaving minimal forensic traces.
MITRE ATT&CK
T1078 · Valid AccountsThe reported activity uses stolen credentials and authenticated sessions to access identity providers and connected SaaS applications.T1098.005 · Device RegistrationThe groups reportedly register new devices and remove existing devices to bypass MFA and maintain access to compromised accounts.T1564.008 · Email Hiding RulesThe groups reportedly configure inbox rules to delete automated notifications about unauthorized device registration.T1566.004 · Spearphishing VoiceThe groups reportedly use vishing, including calls impersonating IT help desk personnel, to direct victims to phishing pages.
People
Cuong DinhNamed as a researcher who reported that CL-CRI-1116 activity targeted retail and hospitality organizations using vishing and phishing login sites to steal credentials.Lee ClarkNamed as a researcher who reported that CL-CRI-1116 activity targeted retail and hospitality organizations using vishing and phishing login sites to steal credentials.Matt BradyNamed as a researcher who reported that CL-CRI-1116 activity targeted retail and hospitality organizations using vishing and phishing login sites to steal credentials.
Threat Actors
BlackFileIdentified in the article as an alias of Cordial Spider, which is reported to conduct rapid SaaS-focused data-theft and extortion campaigns.Cordial SpiderReportedly conducts rapid data-theft and extortion campaigns targeting SaaS environments. The article identifies BlackFile, CL-CRI-1116, O-UNC-045, and UNC6671 as aliases.O-UNC-025Identified in the article as an alias of Snarky Spider, which is reported to conduct rapid SaaS-focused data-theft and extortion campaigns.O-UNC-045Identified in the article as an alias of Cordial Spider, which is reported to conduct rapid SaaS-focused data-theft and extortion campaigns.ShinyHuntersMandiant reportedly described the two clusters’ tactics as consistent with extortion-themed attacks carried out by ShinyHunters; the article does not establish that ShinyHunters conducted these specific campaigns.SNARKY SPIDERReportedly conducts rapid data-theft and extortion campaigns targeting SaaS environments and can begin exfiltration in under an hour. The article identifies O-UNC-025 and UNC6661 as aliases.UNC6661Identified in the article as an alias of Snarky Spider, which is reported to conduct rapid SaaS-focused data-theft and extortion campaigns.UNC6671Identified in the article as an alias of Cordial Spider, which is reported to conduct rapid SaaS-focused data-theft and extortion campaigns.
Vendors
CrowdStrikewhere they capture authentication data and pivot directly into SSO-integrated SaaS applications,” CrowdStrike’s Counter Adversary Operations said in a report.Googlesuppress alert emails, and pivot via compromised identity providers to exfiltrate high-value data from Google Workspace, HubSpot, SharePoint, and Salesforce.HubSpotand pivot via compromised identity providers to exfiltrate high-value data from Google Workspace, HubSpot, SharePoint, and Salesforce.MandiantIn a report published back in January 2026, Google-owned Mandiant revealed that the two clusters represent an expansion in threat activity that employs tactics consistent with extortion-themed attacks carried out by theMicrosoftenvironments to look for high-value files and business-critical reports in Google Workspace, HubSpot, Microsoft SharePoint, and Salesforce, and then exfiltrate data of interest to infrastructure under its control.Palo Alto NetworksAs recently as last week, Palo Alto Networks Unit 42 and Retail & Hospitality Information Sharing and Analysis Center (RH-ISAC) assessed with moderate confidence that the attackers behind CL-CRI-1116 are also mostSalesforceidentity providers to exfiltrate high-value data from Google Workspace, HubSpot, SharePoint, and Salesforce.
Products
Google Workspacealert emails, and pivot via compromised identity providers to exfiltrate high-value data from Google Workspace, HubSpot, SharePoint, and Salesforce.HubSpotand pivot via compromised identity providers to exfiltrate high-value data from Google Workspace, HubSpot, SharePoint, and Salesforce.Microsoft SharePointpivot via compromised identity providers to exfiltrate high-value data from Google Workspace, HubSpot, SharePoint, and Salesforce.Salesforceidentity providers to exfiltrate high-value data from Google Workspace, HubSpot, SharePoint, and Salesforce.
Industries
HospitalityAs recently as last week, Palo Alto Networks Unit 42 and Retail & Hospitality Information Sharing and Analysis Center (RH-ISAC) assessed with moderate confidence that the attackers behind CL-CRI-1116 are also mostRetailAs recently as last week, Palo Alto Networks Unit 42 and Retail & Hospitality Information Sharing and Analysis Center (RH-ISAC) assessed with moderate confidence that the attackers behind CL-CRI-1116 are also most