
China-Linked Campaigns Target Asian Governments, Polish Organizations, Journalists and Activists
Summary
Trend Micro says SHADOW-EARTH-053 exploited Exchange and IIS flaws to target government and defense organizations across Asia and Poland. Citizen Lab separately documented China-linked phishing campaigns targeting journalists and activists.
Key points
- Trend Micro attributes SHADOW-EARTH-053 to a China-aligned threat cluster active since at least December 2024, targeting government and defense organizations across Asia and Poland.
- The campaign exploits known flaws in internet-facing Exchange and IIS systems, deploys Godzilla web shells, and stages ShadowPad through DLL sideloading.
- Reported tools include AnyDesk, IOX, GOST, Wstunnel, RingQ, Mimikatz, a custom RDP launcher, and Sharp-SMBExec.
- In at least one reported case, React2Shell (CVE-2025-55182) facilitated delivery of a Linux version of Noodle RAT; GTIG linked that attack chain to UNC6595.
- Citizen Lab documented GLITTER CARP and SEQUIN CARP phishing campaigns targeting journalists and activists, using impersonation to seek credentials or third-party OAuth access.
- Trend Micro recommends promptly patching Exchange and IIS systems, or using IPS/WAF virtual patching where immediate patching is not feasible.
Article Details
- Event Type
- China-aligned espionage and phishing campaigns targeting government, defense, journalists, and activists
- Impact
- SHADOW-EARTH-053 reportedly compromised internet-facing Exchange and IIS systems, deployed web shells and ShadowPad implants, and targeted government and defense organizations across Asia and Poland. Separate phishing campaigns sought access to email accounts of journalists and activists through credential harvesting and OAuth-token social engineering.
MITRE ATT&CK
T1021.001 · Remote Desktop ProtocolThe campaign used a custom RDP launcher for lateral movement.T1021.002 · SMB/Windows Admin SharesThe campaign used Sharp-SMBExec, a C# implementation of SMBExec, for lateral movement.T1056.003 · Web Portal CaptureThe phishing campaigns used credential-harvesting pages to obtain account credentials.T1190 · Exploit Public-Facing ApplicationSHADOW-EARTH-053 exploited vulnerabilities in internet-facing Exchange and IIS systems to gain initial access.T1505.003 · Web ShellThe campaign deployed Godzilla web shells for persistent access.T1528 · Steal Application Access TokenTargets were socially engineered into granting access through third-party OAuth tokens.T1566 · PhishingGLITTER CARP and SEQUIN CARP conducted phishing campaigns impersonating known individuals and technology-company security alerts.T1574.002 · DLL Side-LoadingShadowPad implants were launched through DLL side-loading of legitimate signed executables.
CVE
People
Threat Actors
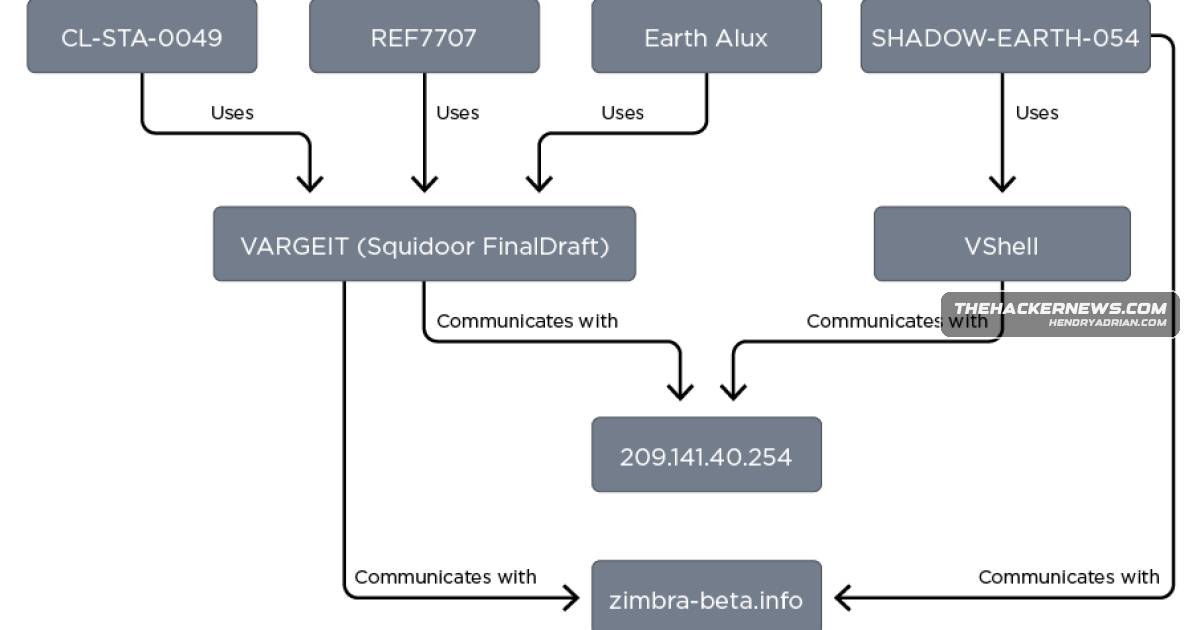
GLITTER CARPA China-affiliated cluster reported to conduct phishing against activists, journalists, and the ICIJ, including credential-harvesting activity.SEQUIN CARPA China-affiliated cluster reported to target journalists and civil-society members through phishing and impersonation; its main target included ICIJ journalist Scilla Alecci.SHADOW-EARTH-053Trend Micro attributes the reported espionage campaign to this cluster, which exploited Exchange and IIS vulnerabilities and deployed Godzilla web shells and ShadowPad implants.SHADOW-EARTH-054Described as a related intrusion set that had previously compromised organizations also targeted by SHADOW-EARTH-053; the article says there is no evidence of direct operational coordination.UNC6595The Google Threat Intelligence Group linked this group to the attack chain involving distribution of a Linux version of Noodle RAT; the article does not establish that it conducted the wider SHADOW-EARTH-053 campaign.UTA0388Described as a separate group that delivered HealthKick using different phishing tactics while specific organizations were also targeted by the GLITTER CARP AiTM phishing kit; the nature of any relationship is unknown.
Malware
GodzillaThe actors exploit N-day Exchange and IIS vulnerabilities, deploy Godzilla web shells and DLL sideloading, use tunneling tools and credential-stealing utilities, and Citizen Lab separately identified GLITTER CARP andHealthKickorganizations using both the AiTM phishing kit (GLITTER CARP, UNK_SparkyCarp) and the delivery of HealthKick using different phishing tactics by a separate group (UNK_DropPitch).” This indicates some level ofNoodleRATShadowPad backdoors are staged via DLL sideloading and delivered using AnyDesk, with additional use of IOX, GOST, Wstunnel, RingQ, and Noodle RAT variants.ShadowPadand defense organizations across South, East, and Southeast Asia and Poland, using web shells and ShadowPad implants.
Products
AnyDeskShadowPad backdoors are staged via DLL sideloading and delivered using AnyDesk, with additional use of IOX, GOST, Wstunnel, RingQ, and Noodle RAT variants.Internet Information Services (IIS)“The group exploits N-day vulnerabilities in internet-facing Microsoft Exchange and Internet Information Services (IIS) servers (e.g., ProxyLogon chain), then deploys web shells (Godzilla) for persistent access andMicrosoft ExchangeAttackers exploit N-day vulnerabilities in internet-facing Microsoft Exchange and IIS servers to drop Godzilla web shells for persistence.
Tools
GOSTAlso put to use are open-source tunneling tools like the IOX, GO Simple Tunnel (GOST), and Wstunnel, as well as RingQ to pack malicious binaries and evade detection.IOXShadowPad backdoors are staged via DLL sideloading and delivered using AnyDesk, with additional use of IOX, GOST, Wstunnel, RingQ, and Noodle RAT variants.MimikatzTo facilitate privilege escalation, SHADOW-EARTH-053 has been found to use Mimikatz, while lateral movement is accomplished using a custom remote desktop protocol (RDP) launcher and C# implementation of SMBExec known asRingQShadowPad backdoors are staged via DLL sideloading and delivered using AnyDesk, with additional use of IOX, GOST, Wstunnel, RingQ, and Noodle RAT variants.Sharp-SMBExecusing a custom remote desktop protocol (RDP) launcher and C# implementation of SMBExec known as Sharp-SMBExec.WstunnelShadowPad backdoors are staged via DLL sideloading and delivered using AnyDesk, with additional use of IOX, GOST, Wstunnel, RingQ, and Noodle RAT variants.
Countries
ChinaResearchers disclosed a China-aligned espionage campaign tracked as SHADOW-EARTH-053 that has targeted government and defense organizations across South, East, and Southeast Asia and Poland, using web shells andIndiaTargets of the campaigns include Pakistan, Thailand, Malaysia, India, Myanmar, Sri Lanka, and Taiwan.MalaysiaTargets of the campaigns include Pakistan, Thailand, Malaysia, India, Myanmar, Sri Lanka, and Taiwan.MyanmarTargets of the campaigns include Pakistan, Thailand, Malaysia, India, Myanmar, Sri Lanka, and Taiwan.PakistanTargets of the campaigns include Pakistan, Thailand, Malaysia, India, Myanmar, Sri Lanka, and Taiwan.Polandthat has targeted government and defense organizations across South, East, and Southeast Asia and Poland, using web shells and ShadowPad implants.Sri LankaTargets of the campaigns include Pakistan, Thailand, Malaysia, India, Myanmar, Sri Lanka, and Taiwan.TaiwanTargets of the campaigns include Pakistan, Thailand, Malaysia, India, Myanmar, Sri Lanka, and Taiwan.ThailandTargets of the campaigns include Pakistan, Thailand, Malaysia, India, Myanmar, Sri Lanka, and Taiwan.
Industries
Civil societyundertaken by two distinct China-affiliated threat actors targeting and impersonating journalists and civil society, including Uyghur, Tibetan, Taiwanese, and Hong Kong diaspora activists.Defensea China-aligned espionage campaign tracked as SHADOW-EARTH-053 that has targeted government and defense organizations across South, East, and Southeast Asia and Poland, using web shells and ShadowPad implants.GovernmentResearchers disclosed a China-aligned espionage campaign tracked as SHADOW-EARTH-053 that has targeted government and defense organizations across South, East, and Southeast Asia and Poland, using web shells andsemiconductorGLITTER CARP, besides conducting broad-scale phishing attacks, has been tied to phishing campaigns targeting the Taiwanese semiconductor industry.