
Malicious PyTorch Lightning 2.6.3 Package Delivered Credential-Stealing Payload
Summary
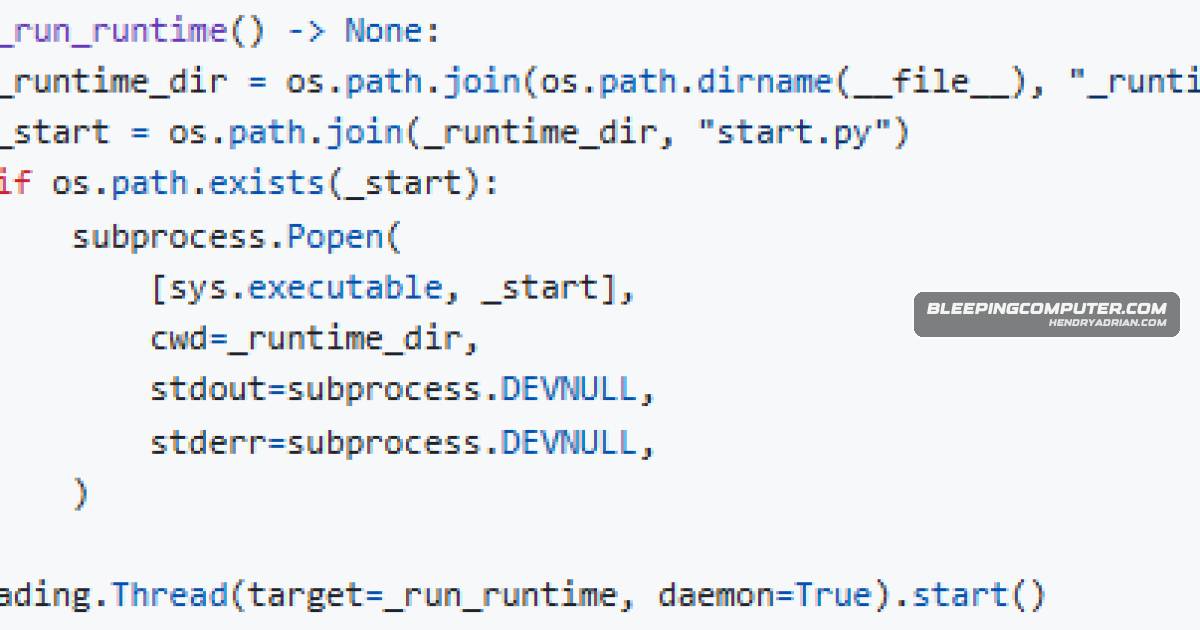
PyTorch Lightning 2.6.3 on PyPI ran a credential-stealing payload on import. Microsoft Defender detected and blocked activity affecting a small number of devices; the package was reverted to 2.6.1, and users are advised to rotate secrets.
Key points
- The compromised lightning==2.6.3 package triggered a hidden execution chain when imported.
- A background process downloaded Bun v1.3.13 and ran an 11.4 MB obfuscated JavaScript payload named router_runtime.js.
- Microsoft Defender identifies the payload as ShaiWorm and says it detected and prevented the activity.
- The payload targeted environment files, API keys, GitHub tokens, browser data, and cloud credentials; it also supported arbitrary system commands.
- Microsoft telemetry indicated activity on a small number of devices, contained to a narrow set of environments.
- Lightning AI reverted the package to version 2.6.1 and is investigating the release-pipeline compromise and auditing recent releases.
- Users who imported version 2.6.3 are advised to rotate all secrets.
Article Details
- Event Type
- Software supply-chain compromise involving a malicious PyTorch Lightning package published on PyPI.
- Impact
- The lightning==2.6.3 release executed a credential-stealing JavaScript payload on import. It targeted .env files, API keys, secrets, GitHub tokens, browser data, and cloud credentials, and supported arbitrary system command execution. Microsoft reported that Defender detected and blocked the activity, which affected a small number of devices. Lightning AI reverted the package to version 2.6.1; users who imported the compromised release were advised to rotate their secrets.
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe JavaScript payload was described as heavily obfuscated.T1059.007 · JavaScriptThe package used Bun to execute a JavaScript payload.T1105 · Ingress Tool TransferA background process downloaded Bun and the payload.T1552.001 · Credentials In FilesThe payload targeted credentials and secrets stored in .env files.
Malware
Vendors
Lightning AIMicrosoft telemetry shows the impact was limited to a small number of devices, and Lightning AI reverted the package to version 2.6.1.MicrosoftMicrosoft Defender detected and blocked the routine (identified as ShaiWorm), the package was reverted to 2.6.1, and users who imported the compromised release are advised to rotate all secrets.
Products
BunA background process downloaded Bun v1.3.13 and executed an 11.4 MB obfuscated JavaScript payload (router_runtime.js).Microsoft Defender Antimalware PlatformMicrosoft Defender detected and blocked the routine (identified as ShaiWorm), the package was reverted to 2.6.1, and users who imported the compromised release are advised to rotate all secrets.PyTorch LightningA malicious PyTorch Lightning package (lightning==2.6.3) published on PyPI delivered a credentialâstealing JavaScript payload that executed automatically on import and spawned a background process.