
CloudZ RAT Plugin Pheno Hijacks Microsoft Phone Link to Steal SMS and OTPs
Summary
Cisco Talos reports that CloudZ’s Pheno plugin can access Phone Link’s local SQLite database to steal SMS and OTP messages. A fake ScreenConnect update deploys loaders that install the RAT and establish persistence.
Key points
- Pheno monitors for active Microsoft Phone Link sessions and accesses the application’s local SQLite database, which may contain SMS and OTP messages.
- The reported activity could expose mobile messages through the Windows host without compromising the mobile device.
- The infection chain begins with a fake ScreenConnect update that drops a Rust loader, followed by a .NET loader that installs CloudZ RAT.
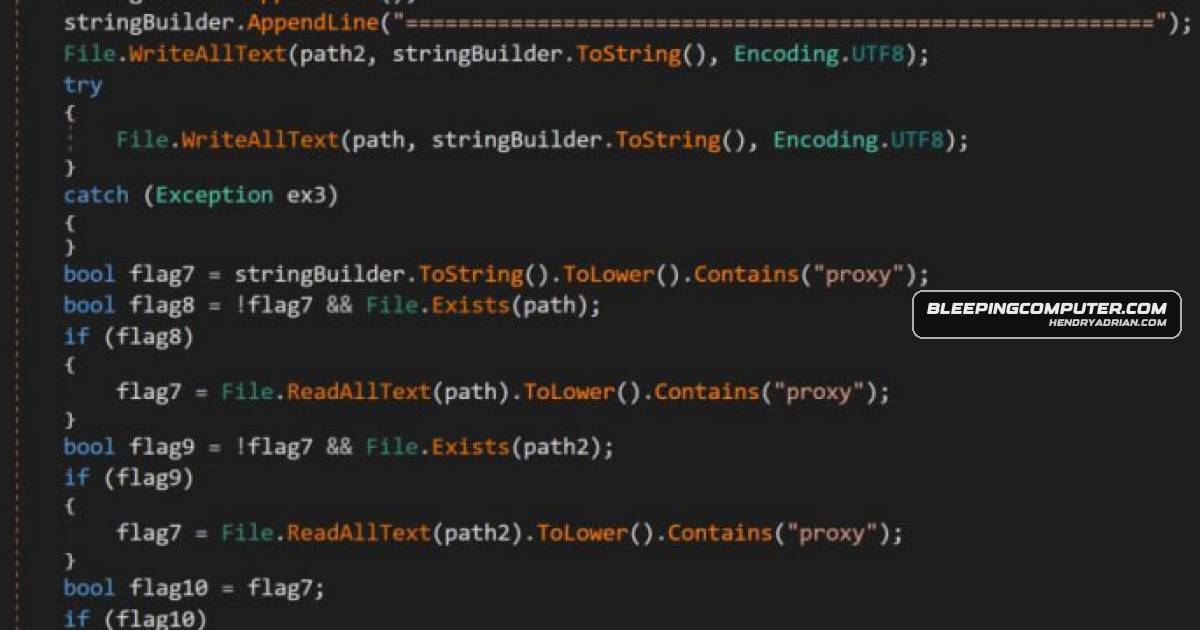
- The .NET loader uses time-based delays and checks for analysis tools and VM- or sandbox-related strings.
- CloudZ can access browser-stored data, manage files, execute shell commands, record the screen, and manage plugins.
- Cisco Talos says CloudZ rotates among three hardcoded user-agent strings and uses anti-caching headers for C2 communications.
- Cisco Talos published indicators of compromise and recommends avoiding SMS-based OTPs in favor of authenticator apps or phishing-resistant hardware keys.
Article Details
- Event Type
- CloudZ RAT intrusion using the Pheno plugin to abuse Microsoft Phone Link
- Impact
- Pheno monitors active Phone Link sessions and accesses the local SQLite database, which may contain SMS and one-time passcodes. This could expose sensitive messages without compromising the connected mobile device. Researchers believe the threat actor intended to steal credentials and temporary passcodes; the intrusion was active since at least January.
MITRE ATT&CK
T1005 · Data from Local SystemPheno accesses the local Phone Link SQLite database to obtain SMS and OTP messages.T1053.005 · Scheduled TaskThe .NET loader establishes persistence by creating a scheduled task.T1059 · Command and Scripting InterpreterCloudZ can execute shell commands.T1113 · Screen CaptureCloudZ can start screen recording.
Malware
CloudZResearchers uncovered a new CloudZ RAT plugin called Pheno that hijacks Microsoft Phone Link on Windows to steal SMS and one-time passcodes from a target’s mobile messages without compromising the device.PhenoResearchers uncovered a new CloudZ RAT plugin called Pheno that hijacks Microsoft Phone Link on Windows to steal SMS and one-time passcodes from a target’s mobile messages without compromising the device.
Products
Microsoft Phone LinkResearchers uncovered a new CloudZ RAT plugin called Pheno that hijacks Microsoft Phone Link on Windows to steal SMS and one-time passcodes from a target’s mobile messages without compromising the device.ScreenConnectThe intrusion chain uses a fake ScreenConnect update to deploy Rust and .NET loaders with anti-analysis checks, and Cisco Talos published IoCs and mitigation guidance.