cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3800 articles

Security News · opensourcemalware.com

OpenSourceMalware Show #3 Covers Lazarus Git Hooks, Antrea Compromise and Active cPanel Exploitation

The episode discusses Lazarus Group’s use of Git hooks, the contested Antrea project compromise, Dirty Frag Linux privilege escalation, active cPanel exploitation, and why interpreted-language malware can evade sandboxes.
May 7, 2026
Security News · wiz.io

Wiz Challenges Customers to Eliminate Critical Code Issues with AI Security Tools

Wiz is challenging customers to eliminate critical code issues with available fixes, promoting AI coding guardrails, code visibility, agentic remediation, and workflows to help teams reach zero.

May 7, 2026
Security News · securityweek.com

XBOW Raises $35 Million to Expand Its Autonomous Offensive Security Platform

XBOW announced a $35 million extension to its Series C, bringing total funding above $270 million. The company says its AI platform autonomously tests applications for vulnerabilities and provides reproducible proof of findings.

May 6, 2026
Security News · cybersecuritypulse.net

AI Agent Deletes PocketOS Production Data as Roundup Covers Crypto Theft and Security Flaws

A weekly roundup covers an AI agent deleting PocketOS production data, TRM Labs’ report of $577M in DPRK-linked crypto theft, critical cPanel and GitHub flaws, and new defensive logging and account-security offerings.

May 6, 2026
Security News · bleepingcomputer.com

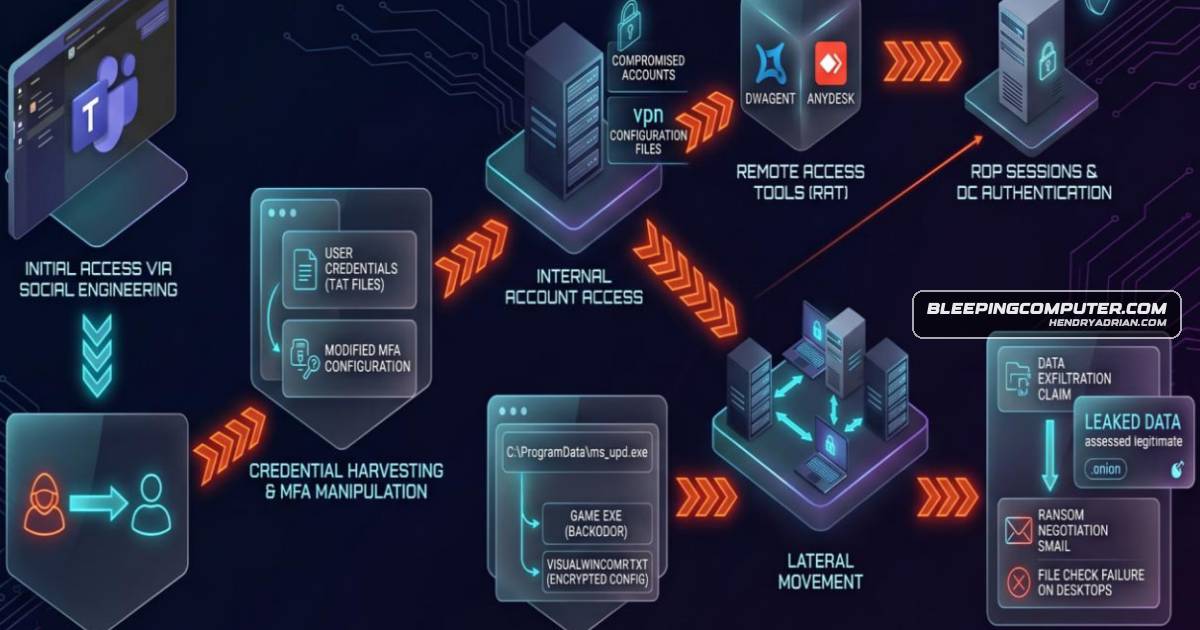
MuddyWater Used Chaos Ransomware as Espionage Decoy, Rapid7 Says

Rapid7 says an intrusion it investigated used Chaos ransomware as cover for suspected MuddyWater espionage, with Microsoft Teams social engineering, credential theft, MFA manipulation and remote-access tools. Attribution is moderate-confidence.

May 6, 2026
Security News · securityweek.com

Romanian Suspect Extradited to US Over Alleged VoIP Vishing Scheme

Gavril Sandu was extradited from Romania to the US to face bank fraud charges over an alleged 2009–2010 scheme involving hacked business VoIP systems, vishing, cloned payment cards and cash withdrawals.

May 6, 2026
Security News · securityweek.com

CISA Urges Critical Infrastructure Operators to Prepare Isolation and Recovery Plans

CISA launched CI Fortify, urging U.S. critical infrastructure operators to prepare for prolonged isolation from external networks and strengthen recovery through system documentation, backups, restoration rehearsals and manual-operation plans.

May 6, 2026
Security News · securityweek.com

Oracle Adds Monthly Security Updates for Critical Vulnerabilities

Oracle will add monthly Critical Security Patch Updates alongside its quarterly releases, starting May 28. Oracle-managed cloud services will receive updates automatically; self-managed customers must apply them.

May 6, 2026
Security News · elastic.co

Elastic Announces Weighted Entity Watchlists for Security Risk Scoring

Elastic says Security v9.4 will add named, weighted watchlists for users, hosts, and services, feeding organizational context into entity risk scores. Lists can be managed manually or populated through integrations and APIs.

May 6, 2026
Security News · therecord.media

ESET Links Android BirdCall Campaign to APT37, Targeting Koreans in China

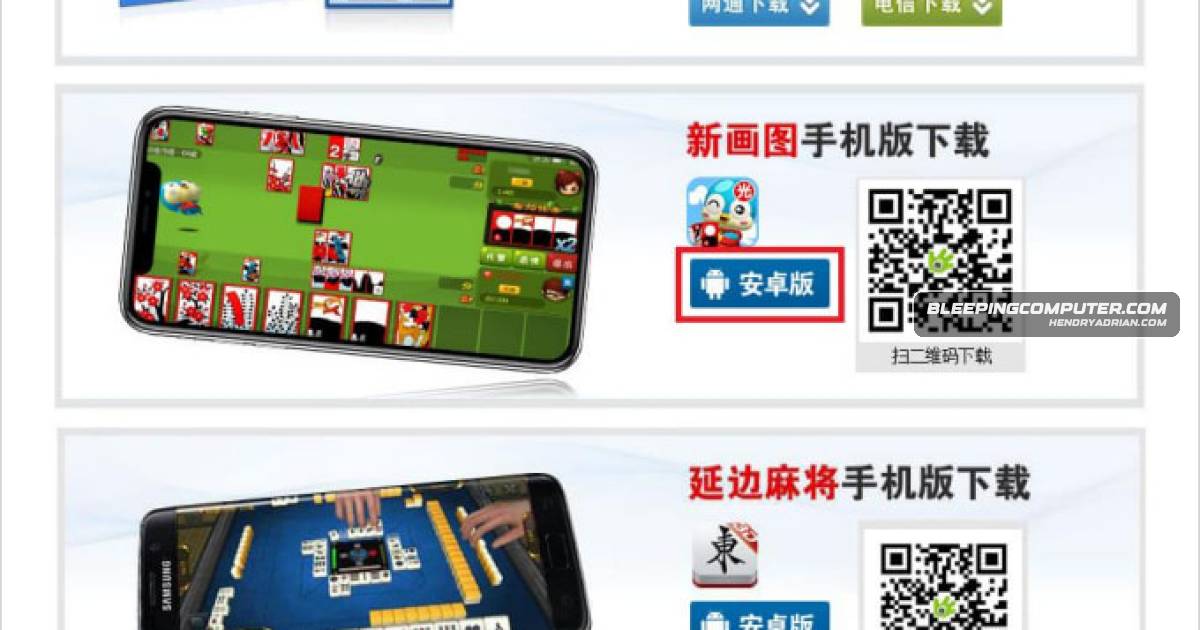
ESET attributed an Android BirdCall campaign to APT37, which hid the backdoor in Sqgame card-game updates distributed outside Google Play. The malware stole device data and recorded audio; researchers found seven versions and said the update package is no longer harmful

May 6, 2026
Security News · cyberscoop.com

CISA Urges Critical Infrastructure to Prepare for Months-Long Isolation Under CI Fortify

CISA’s CI Fortify initiative will assess critical infrastructure and help operators plan to maintain essential services for weeks to months while disconnected from IT and third-party connections, with isolation and recovery planning as key measures.

May 5, 2026
Security News · bleepingcomputer.com

Trojanized DAEMON Tools Installers Deliver Backdoors in Ongoing Supply-Chain Attack

Kaspersky says trojanized, digitally signed DAEMON Tools installers infected thousands across 100+ countries since April 8; about a dozen high-value systems received second-stage payloads, including QUIC RAT. The campaign is ongoing.

May 5, 2026
Security News · therecord.media

Ransomware Negotiator Deniss Zolotarjovs Sentenced to 102 Months in U.S. Prison

Deniss Zolotarjovs was sentenced to 102 months after pleading guilty to money laundering and wire fraud. Prosecutors say he helped ransomware groups extort more than 53 companies, causing $56 million in losses.

May 5, 2026
Security News · therecord.media

FTC Proposes Settlement Restricting Kochava’s Sale of Sensitive Location Data

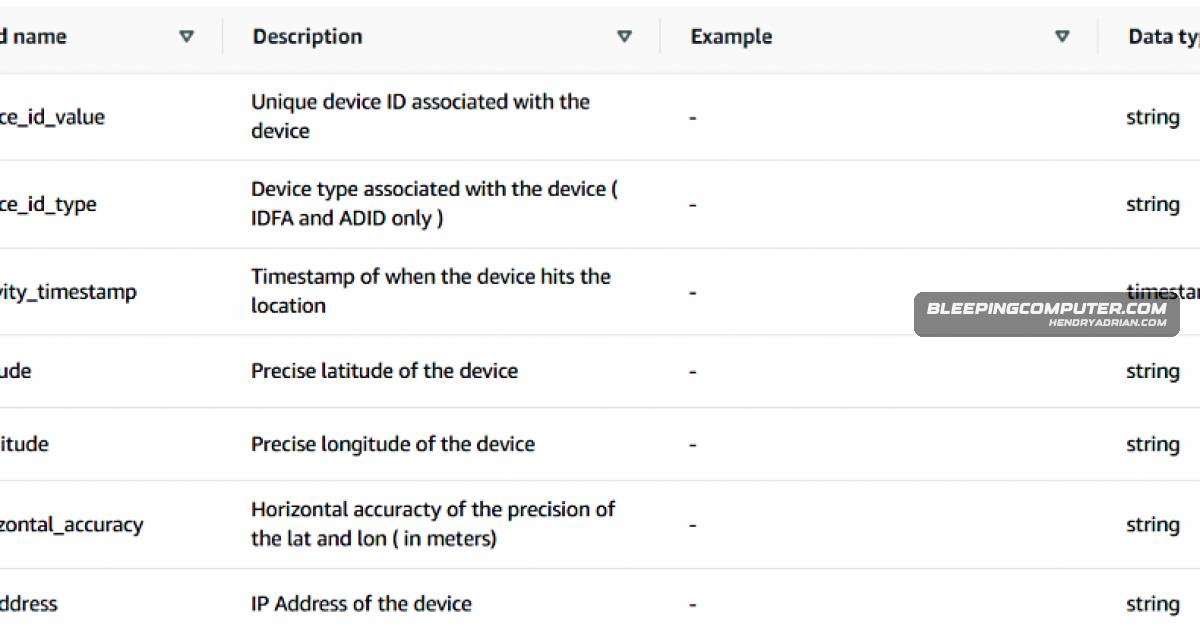
A proposed FTC settlement would bar Kochava and its subsidiary from selling or sharing sensitive location data without explicit consent. It also requires consent and supplier programs, retention limits, and consumer access and withdrawal options; court approval is still

May 5, 2026
Security News · thehackernews.com

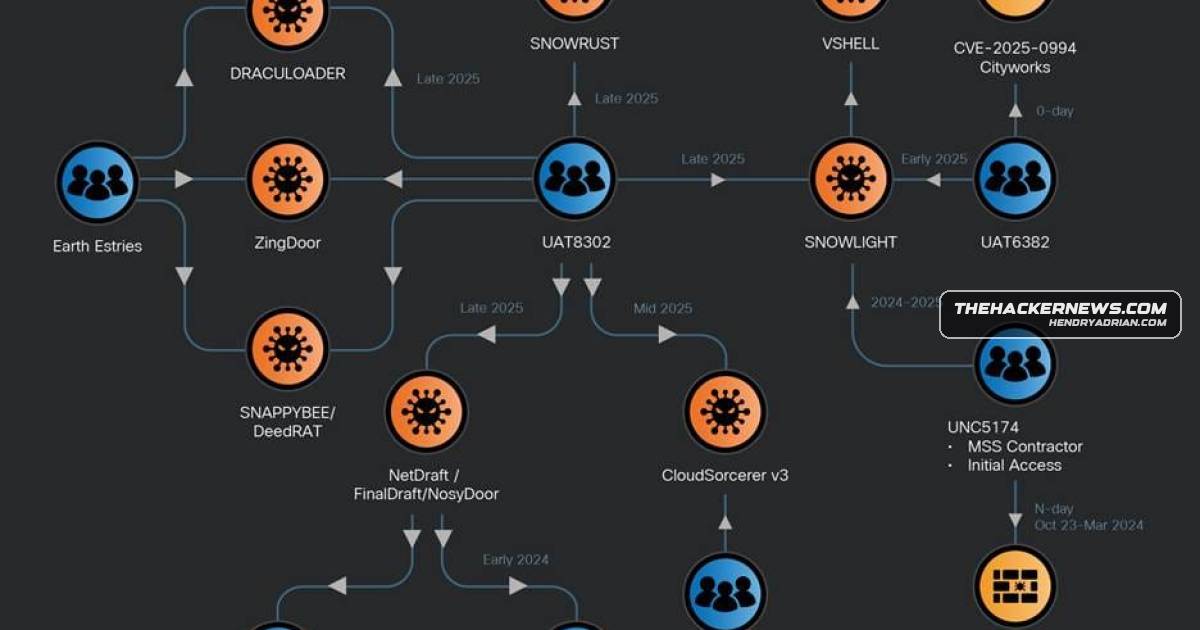
Cisco Talos Tracks China-Nexus UAT-8302 Campaign Targeting Government Agencies

Cisco Talos attributes attacks on South American and southeastern European government entities to China-nexus APT UAT-8302, which deploys NetDraft, CloudSorcerer and VShell; initial access is suspected to involve web-application exploits.

May 5, 2026
Security News · cyberscoop.com

Latvian National Sentenced to 102 Months for Ransomware Extortions

Deniss Zolotarjovs was sentenced to 102 months for helping a ransomware organization pressure victims. Authorities say the crew extorted nearly $16 million in confirmed ransom payments and targeted more than 54 companies.

May 5, 2026
Security News · cyberscoop.com

CISA Says AI Automation Is Boosting Security Operations and Mission Support

CISA officials say AI automation is helping security analysts triage threats faster and supporting customer response and data migration. They cite legacy workflows, data-platform gaps and the need for transparent AI governance as adoption challenges.

May 5, 2026
Security News · thehackernews.com

Kaspersky Reports Trojanized DAEMON Tools Installers Delivering Backdoor and QUIC RAT

Kaspersky reports that DAEMON Tools installers were trojanized from April 8, 2026. The signed installers delivered malware, with a backdoor and QUIC RAT reaching a limited number of targets.

May 5, 2026
Security News · bleepingcomputer.com

Google Restructures Android and Chrome Bug Bounties, Offering Up to $1.5 Million

Google is increasing top rewards for difficult Android and Chrome exploits while reducing payouts for some flaws it says AI makes easier to find. It also narrowed submission priorities and reported $17.1 million in 2025 payouts.

May 5, 2026
Security News · bleepingcomputer.com

FTC Settlement Would Bar Kochava From Selling Location Data Without Consent

A proposed FTC order would bar Kochava and subsidiary Collective Data Solutions from selling precise location data without affirmative consent. It also requires consent checks, sensitive-location safeguards, consumer controls, incident reporting, and data-deletion rules

May 5, 2026
Security News · securityweek.com

Microsoft Reports Phishing Campaign Using Compliance Lures and AiTM Attacks

Microsoft observed more than 35,000 phishing attempts targeting users at roughly 13,000 organizations. The campaign uses compliance-themed PDFs and CAPTCHA pages before AiTM phishing to capture authentication tokens and access accounts.

May 5, 2026
Security News · wiz.io

Wiz Introduces a Unified Platform for Penetration-Test Findings

Wiz’s public-preview feature centralizes findings from bug bounty programs, external audits, internal tests, and AI assessments, then maps them to cloud resources to support prioritization, ownership, reporting, and remediation tracking.

May 5, 2026
Security News · justice.gov

Ransomware Group Enforcer Sentenced to 102 Months for Extortion Role

Deniss Zolotarjovs was sentenced to 102 months for helping a Russia-based ransomware organization extort victims. DOJ documents describe his use of stolen sensitive data and estimate the group’s losses likely reached hundreds of millions of dollars.

May 5, 2026
Security News · bleepingcomputer.com

APT37 Uses Trojanized Android Games to Deliver BirdCall Spyware

ESET says APT37 delivered at least seven versions of its Android BirdCall backdoor through trojanized APKs on sqgame[.]net, targeting users in China’s Yanbian region and collecting messages, contacts, location, screenshots, audio, and files.

May 5, 2026
PreviousPage 106 of 159 Next
© 2026 cyber.hendryadrian.com