cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1293 articles

Security Insights · malwareinfo.app

Ransomware Recovery Requires More Than Decrypting Files

A ransomware guide explains how data theft, credential compromise, and backup damage can outlast encryption, and covers recovery opportunities, evidence preservation, incident response, and resilient backup preparation.
Sep 7, 2026
Security Insights · elastic.co

Elastic argues SIEM vendors should provide free, complete, real-time telemetry access

Elastic argues that extra fees, partial exports, and batch delays for SIEM telemetry can create vendor lock-in and hinder incident response. It urges buyers to assess export cost, data completeness, and latency.

Sep 5, 2026
Security Insights · matthewrosenquist.substack.com

Suspected Identity-Verification Breach Exposes 153 Million IDs, Fuels Calls for Data-Retention Limits

A suspected breach put 153 million identity documents from North American victims up for sale. The author argues companies should purge documents after verification and calls for regulations to limit retention.

Sep 4, 2026
Security Insights · gendigital.com

Gen Says AI Cyber Defense Must Extend to Consumers

Gen argues that AI-enabled threats make consumer protection essential to collective cyber defense, advocating defensive AI, trust layers for autonomous agents, shared intelligence, and open standards.

Sep 4, 2026
Security Insights · cyble.com

GCC Cyber Rules Put Breach Detection Speed at the Center of Compliance

The article says GCC regulations impose short incident-notification timelines and argues that continuous threat intelligence can help enterprises detect breaches sooner and document when they were identified.

Sep 4, 2026
Security Insights · aikido.dev

Guide Compares Trivy Alternatives and Cites Two 2026 Supply-Chain Attacks

Aikido's vendor-authored guide compares six Trivy alternatives and their coverage, prioritization and remediation. It reports two 2026 supply-chain compromises involving Aqua CI credentials and recommends pinning GitHub Actions to commit SHAs and limiting CI secrets.

Sep 4, 2026
Security Insights · morphisec.com

Trusted Software Packages Are Becoming a Ransomware Delivery Vector

The article explains how self-propagating worms can use trusted npm and PyPI packages to run malicious code during installation, steal credentials, and spread, arguing that provenance checks should be complemented by controls that prevent execution.

Sep 4, 2026
Security Insights · arcticwolf.com

Why Incomplete IT Asset Inventories Create Security Blind Spots

The article explains how fragmented, stale asset inventories leave devices outside security controls and vulnerability scanning. It recommends continuously aggregating and deduplicating data across existing tools, while also promoting Arctic Wolf’s asset management and

Sep 3, 2026
Security Insights · cyberbuilders.substack.com

Three Cybersecurity Areas Where AI Could Help Companies Build Defensible Businesses

The article argues that cybersecurity companies can use AI to build lasting value through context-rich decision systems, expert services scaled with AI, and products for emerging security challenges such as AI agents.

Sep 3, 2026
Security Insights · cyble.com

Supply-Chain Attacks Exploit Blind Spots in Vendor Security

The article explains how compromises at vendors and software suppliers can affect downstream organizations, reviews MOVEit and GoAnywhere incidents, and argues for continuous vendor visibility and software component transparency.

Sep 3, 2026
Security Insights · decodedsecurity.com

How Network Scanners Turn an IP Address Into Vulnerability Findings

An explainer follows a vulnerability scan from host discovery and port and service identification through security checks and evidence collection, showing how network visibility and authenticated access shape findings and why teams must assess and remediate them.

Sep 3, 2026
Security Insights · wiz.io

Wiz Advocates Finding Vulnerabilities Before Code Reaches Production

Wiz argues that fixing vulnerabilities during development can reduce remediation effort and prevent production exposure, recommending security checks from coding sessions through CI/CD build gates.

Sep 3, 2026
Security Insights · jamf.com

Enterprise AI Agents’ Cyber Capabilities Make Governance and Access Controls Critical

Examples involving Copilot, Slack AI, GitHub workflows and coding agents show how trusted AI systems can expose data or alter production systems. The article argues for least privilege, independent monitoring and deterministic authorization.

Sep 3, 2026
Security Insights · huntress.com

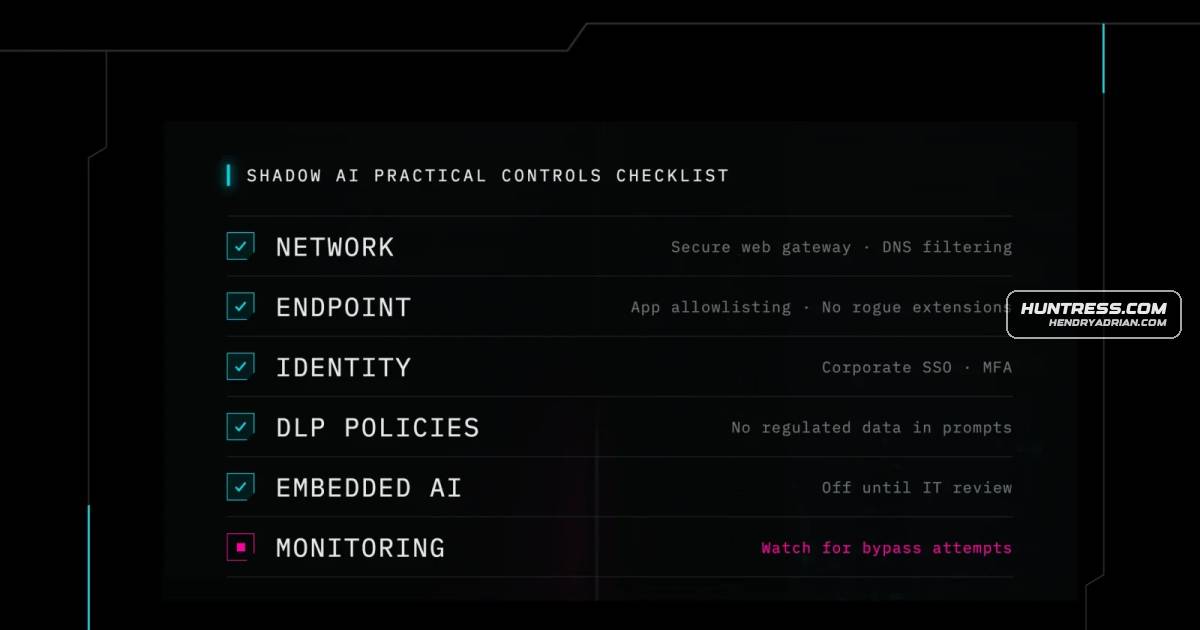
Shadow AI Poses Data-Exposure Risks for Financial Services Firms

Unsanctioned AI use in financial services can expose sensitive customer data and create privacy and compliance risks. The article recommends visibility, approved tools, clear policies, and controls such as DLP, SSO, and activity monitoring.

Sep 3, 2026
Security Insights · huntress.com

Managed vs. Unmanaged EDR: How to Choose the Right Approach

The article explains how managed and unmanaged EDR differ, outlining their trade-offs and questions organizations can consider when choosing based on internal security expertise, staffing, and resources.

Sep 3, 2026
Security Insights · reversinglabs.com

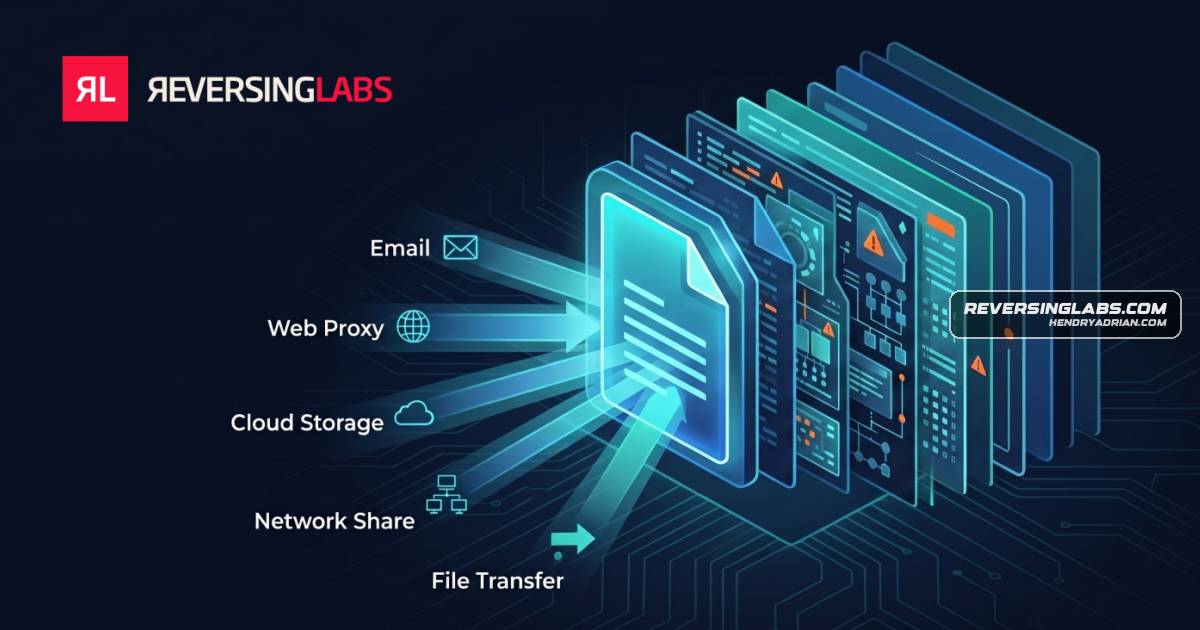
Guide Compares 2026 Enterprise File-Scanning Tools for Malware Protection

A buyer’s guide compares six enterprise file-scanning platforms by analysis depth, throughput, file-type coverage, ingestion channels and deployment, and explains how to evaluate static scanning versus detonation-based detection.

Sep 3, 2026
Security Insights · acronis.com

A Playbook for Hardening Remote Access Tools in SMBs

Acronis outlines ways SMBs and MSPs can reduce risk from abused remote access tools, including RDP, ScreenConnect, MeshAgent and VNC, with guidance on hardening, monitoring and controlling installations.

Sep 3, 2026
Security Insights · aikido.dev

Burp Suite vs. ZAP: Comparing Web Application Testing Workflows

Aikido compares Burp Suite Professional, ZAP, and its AI pentesting product across manual testing, authentication, automation, validation, and cost. The comparison uses product documentation, not hands-on benchmarks.

Sep 2, 2026
Security Insights · team-cymru.com

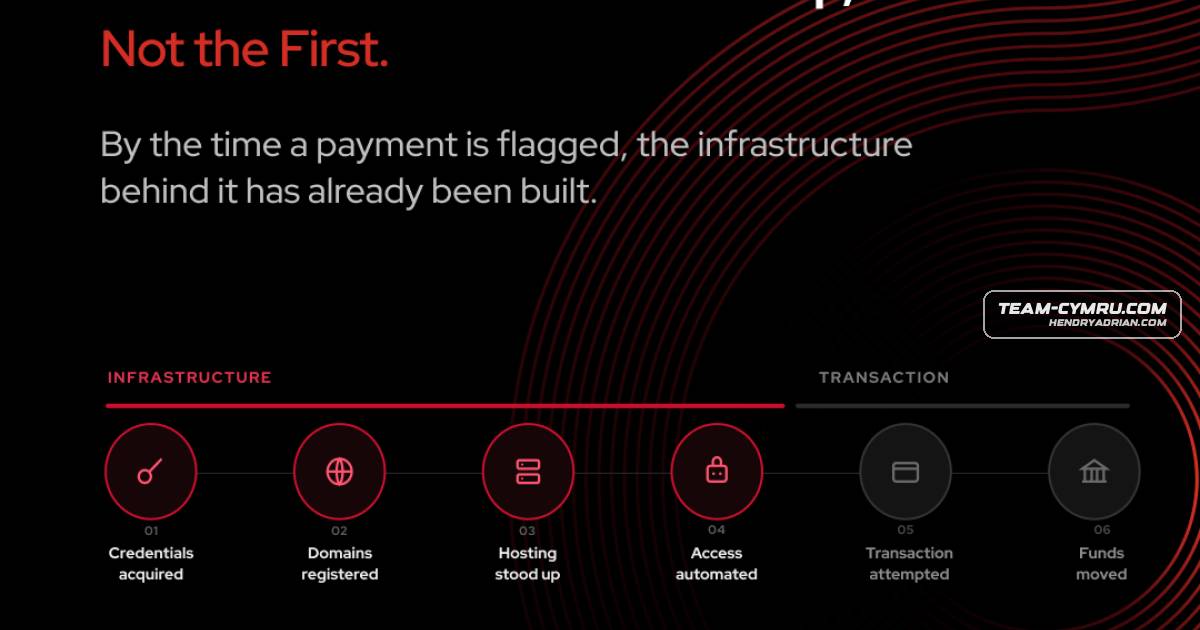
Fraud Defense Should Start Before the Transaction, Team Cymru Says

Team Cymru argues that fraud teams can detect and disrupt operations earlier by tracing infrastructure, targeting, and account compromise instead of relying mainly on transaction-level signals.

Sep 2, 2026
Security Insights · arcticwolf.com

Attack Surface Management: A Practical Guide to Continuous Asset Visibility

Attack surface management (ASM) continuously inventories assets, prioritizes exposures beyond CVEs, and verifies remediation. Arctic Wolf argues that integrating existing tools can reveal unmanaged assets and control gaps missed by periodic scans.

Sep 1, 2026
Security Insights · toxsec.com

AI Agents Could Make Obscure, Insecure Applications Easier to Find

AI agents may make it cheaper to explore unfamiliar applications, exposing weaknesses that once went unnoticed. A gym-booking agent reportedly bypassed booking limits and cancelled another user’s reservation, while research found widespread security flaws in vibe-coded,

Sep 1, 2026
Security Insights · reliaquest.com

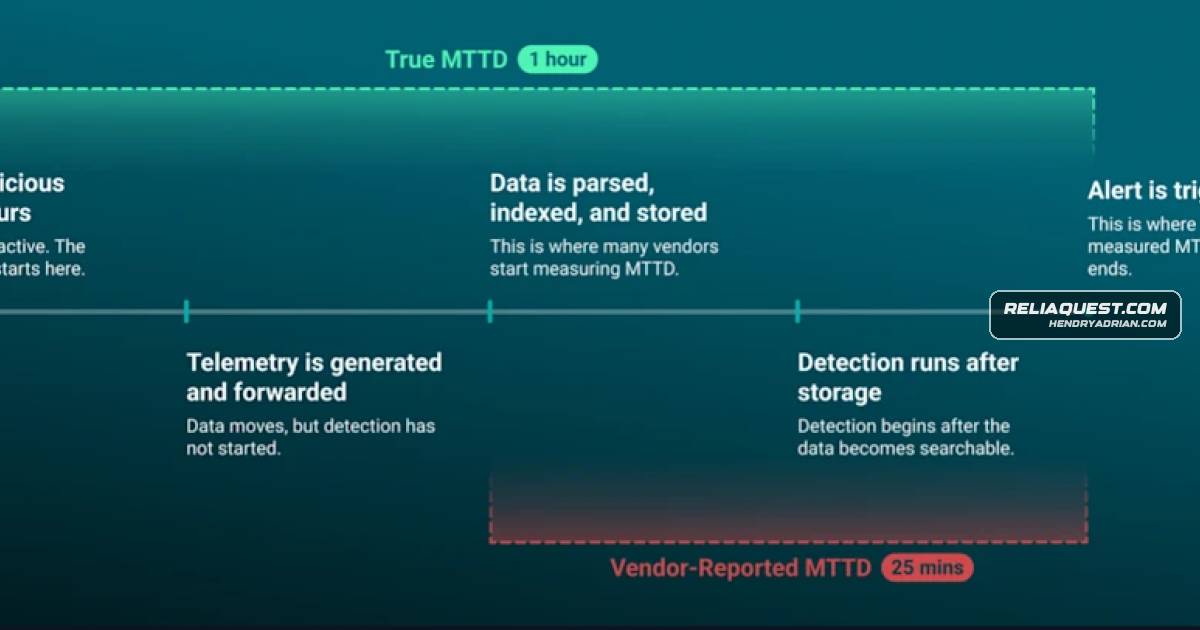
Why Security Vendors’ MTTD Metrics May Understate Detection Delays

The article argues that MTTD can look faster when its clock starts only after logs are processed. It recommends measuring from the first observable suspicious event until an alert is triggered, consistently across security tools.

Sep 1, 2026
Security Insights · aikido.dev

DSPM Tools Compared: Code-Based and Storage-Based Approaches to Data Exposure

The article compares code-based and storage-based DSPM tools, explaining their different approaches to finding sensitive-data exposure, their tradeoffs, and the limits of each. It reviews Aikido Security, Cyera, Varonis, Wiz, and Orca.

Sep 1, 2026
Security Insights · malwareinfo.app

Malware Explained: Types, Risks, Prevention and Incident Response

A comprehensive guide explains malware types, how infections spread and cause harm, and practical steps for prevention and response, including isolating suspected devices, protecting evidence, restoring from trusted backups and reviewing exposed accounts.

Sep 1, 2026
PreviousPage 15 of 54 Next
© 2026 cyber.hendryadrian.com