cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1292 articles

Security Insights · arcticwolf.com

Arctic Wolf argues AI-driven threats require faster cyber defenses

Arctic Wolf argues defenders must adapt faster as attackers adopt AI, citing incident and survey findings. It recommends patched endpoints, phishing-resistant MFA and removing standing admin privileges.
Sep 15, 2026
Security Insights · abstract.security

Where In-Stream Detection Fits in a Modern SecOps Strategy

An explainer argues that running single-event and short-window detections in data pipelines can reduce detection delays and expand coverage, while SIEMs and federated queries remain useful for longer lookbacks and other needs.

Sep 15, 2026
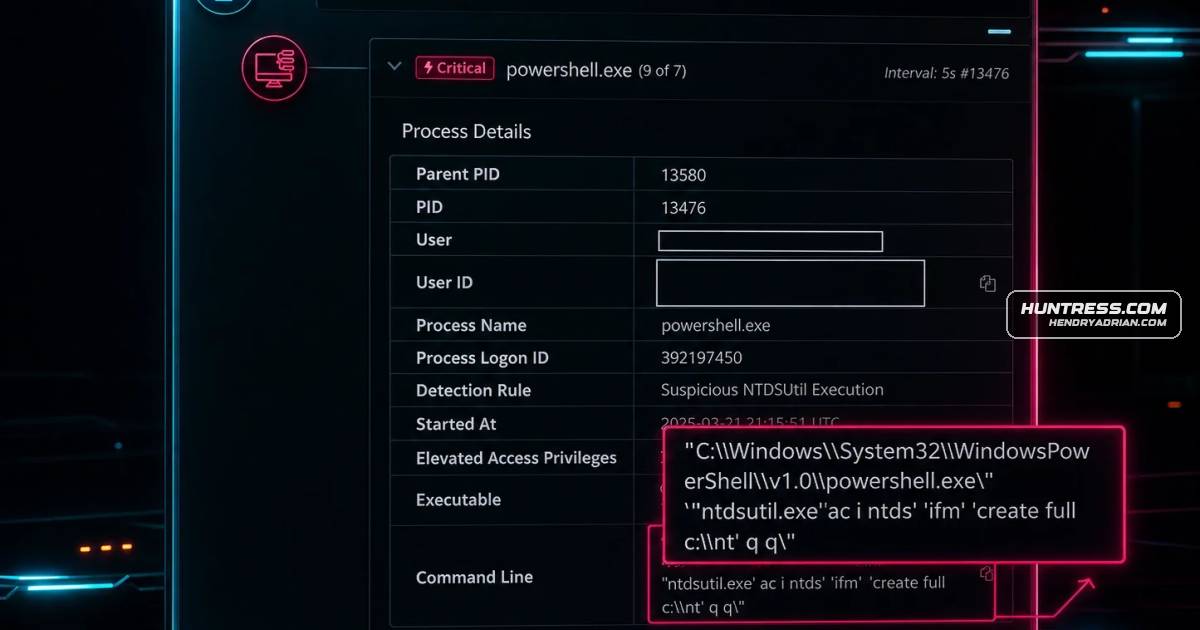
Security Insights · huntress.com

How Reduced Staffing Changes Security and IT Change Risks

Reduced staffing can limit an organisation’s ability to test changes, monitor systems, respond to incidents, and recover. The article advises weighing the risks of acting versus delaying, confirming available capabilities, and preparing escalation and recovery plans.

Sep 15, 2026
Security Insights · securityweek.com

CISOs Face Security Risks as AI Agents Gain Access to Enterprise Systems

Team8’s CISO says AI agents can create unintended risks when they have broad access or unclear instructions. He recommends building guardrails into development while preserving business utility.

Sep 14, 2026
Security Insights · thehackernews.com

How to Evaluate a Unified Security Platform With a One-Incident Test

The article recommends testing a security platform by running a representative incident from detection through clean recovery, measuring handoffs, console switches, response times and whether key workflows work in the planned configuration.

Sep 14, 2026
Security Insights · thehackernews.com

Stop Trying to Control AI Behavior; Restrict What AI Agents Can Access

AI agents can expose or misuse credentials available on developer endpoints. The article argues for mapping their access, understanding credential permissions, removing unnecessary secrets, and limiting authority to reduce potential impact.

Sep 14, 2026
Security Insights · aikido.dev

Dependabot vs. Renovate: Dependency Security and the Limits of Auto-Updates

A vendor comparison of Dependabot and Renovate outlines their platform and configuration tradeoffs, and argues that automatic upgrades can introduce risk. It promotes reachability analysis and fixes that avoid forced upgrades.

Sep 14, 2026
Security Insights · recordedfuture.com

How Proactive Threat Intelligence Helps Security Teams Act Earlier

Proactive threat intelligence uses external threat activity and organizational context to help security teams prioritize vulnerabilities, investigate exposure, and guide threat hunting before risks develop into incidents.

Sep 14, 2026
Security Insights · bitsight.com

13 Cybersecurity Frameworks, Standards and Regulations Explained

An explainer distinguishes 13 cybersecurity frameworks, standards, attestations, and regulations, outlining their scope and requirements and offering steps for mapping obligations to controls and maintaining ongoing risk management.

Sep 11, 2026
Security Insights · securityweek.com

Bishop Fox CEO Vinnie Liu on His Path from NSA Red Teamer to Ethical Hacker

Bishop Fox CEO Vinnie Liu discusses his early interest in computers, NSA red-team work beginning at 17, and later roles in penetration testing and company leadership. He reflects on hacker intent and the difference between exploration and harm.

Sep 10, 2026
Security Insights · cyble.com

How Infostealer Logs Turn Stolen Credentials Into Marketplace Listings

The article explains how infostealers harvest credentials and session data, which are then aggregated, enriched, and sold. It urges security teams to monitor exposure earlier in the pipeline rather than relying only on marketplace or breach alerts.

Sep 10, 2026
Security Insights · helpnetsecurity.com

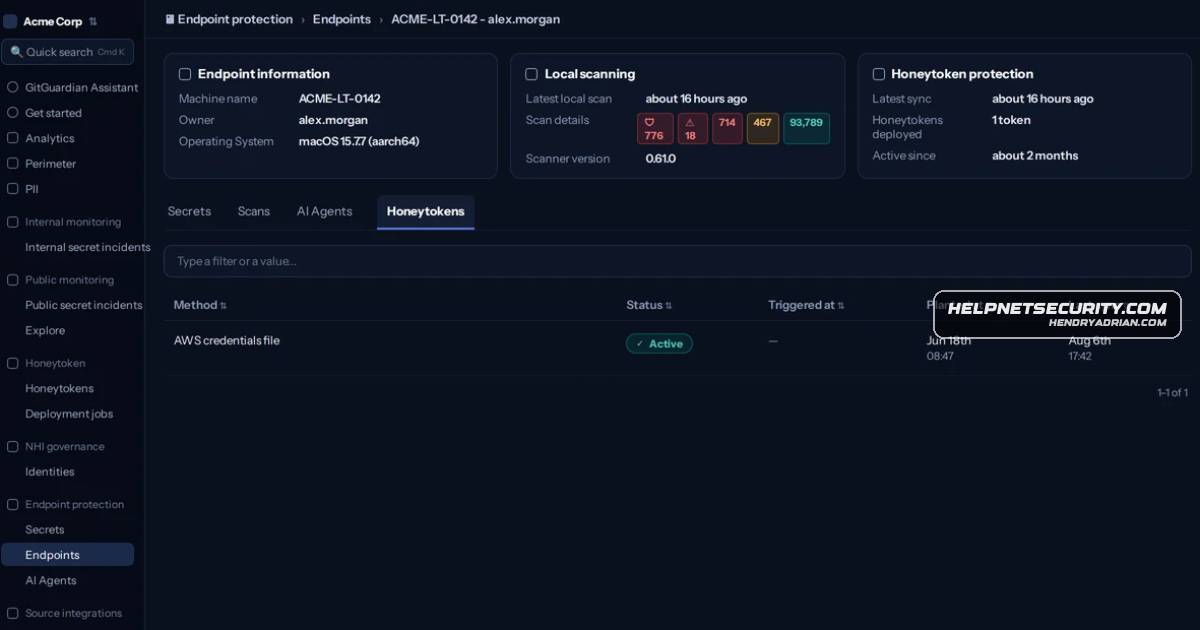
GitGuardian Uses MDM to Deploy Honeytokens Across Developer Endpoints

GitGuardian describes using MDM to deploy and replace honeytokens across developer laptops, alerting teams when a decoy credential is used. The article says the current tokens are AWS credentials and notes that deception detects use, not theft.

Sep 10, 2026
Security Insights · aikido.dev

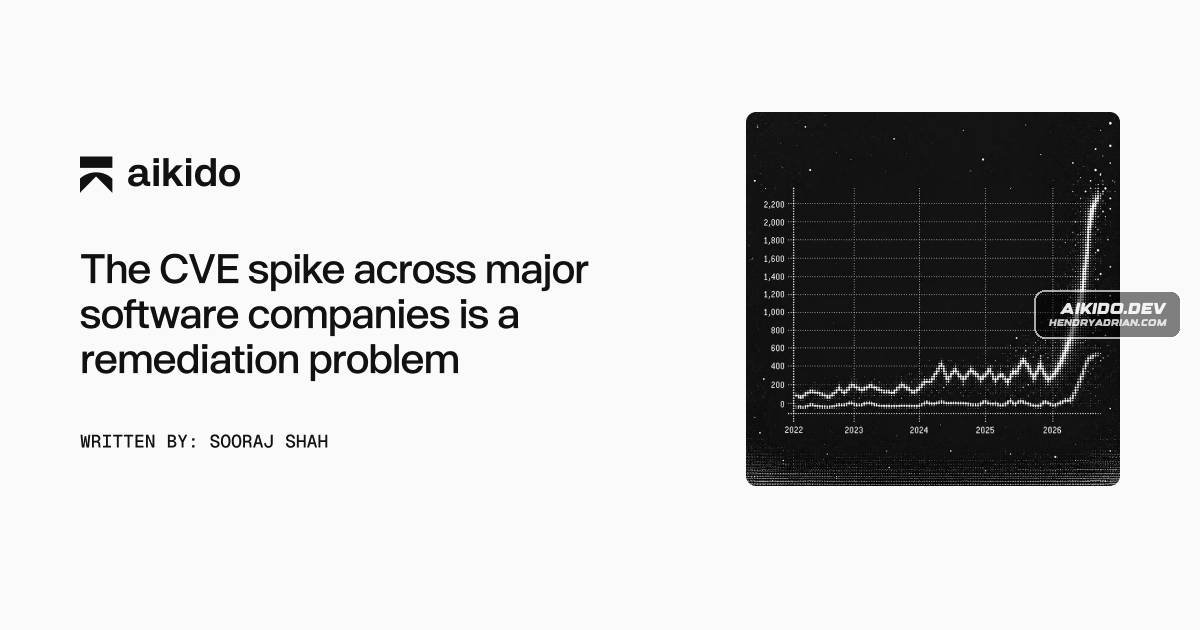
CVE Surge Shifts Focus to Vulnerability Remediation

The article argues that rising CVE counts may reflect faster vulnerability discovery, while remediation is the larger bottleneck: NIST’s backlog grew, and Verizon found only 26% of confirmed, actively exploited flaws fully patched in 2025.

Sep 10, 2026
Security Insights · huntress.com

Password Reuse and Weak Credentials Remain Widespread, Huntress Statistics Show

Huntress compiles password-security statistics showing widespread reuse and weak credentials, alongside growing password-manager and passkey adoption. It recommends long, unique passwords, secure storage, MFA, and phishing awareness.

Sep 10, 2026
Security Insights · huntress.com

2026’s Most Common Passwords Include “123456” and “admin,” Huntress Warns

A guide based on NordPass data lists the most common passwords and explains how weak or reused credentials enable brute force, password spraying, and credential stuffing. It recommends unique passphrases, MFA, and password managers.

Sep 10, 2026
Security Insights · huntress.com

How Attackers Steal Credentials—and How to Reduce the Risk

Huntress explains how phishing, infostealers, credential dumping and password attacks expose credentials, how attackers use stolen access, and how layered controls can help prevent and detect misuse.

Sep 10, 2026
Security Insights · recordedfuture.com

Why Cybersecurity AI Agents Need Structured, Trustworthy Context

The essay argues that cybersecurity AI agents depend on structured, current, and trustworthy operational knowledge—not just capable models—to make reliable decisions. It emphasizes provenance, verification, preserved investigative state, efficiency, and portability.

Sep 10, 2026
Security Insights · threatfabric.com

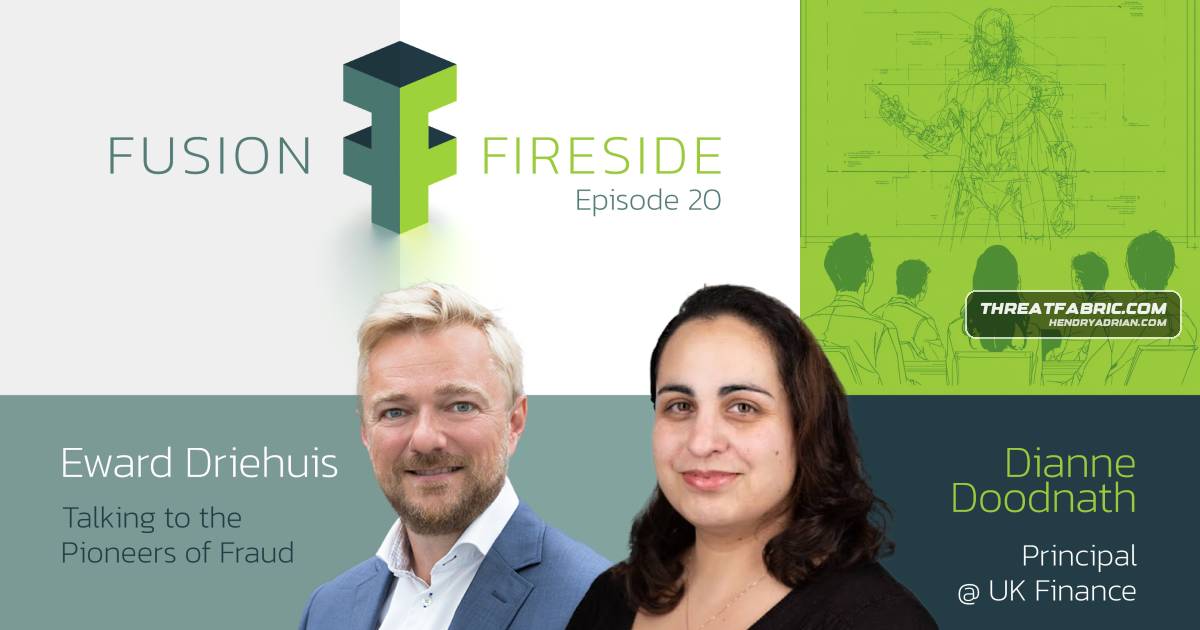
UK Finance’s Dianne Doodnath on Collaboration to Combat Fraud

UK Finance’s Dianne Doodnath discusses how cross-sector collaboration, consumer awareness, and better fraud data can help address social engineering, mobile threats, and other evolving scams.

Sep 9, 2026
Security Insights · securityweek.com

Hidden Instructions in Documents Can Hijack AI Agents

Hidden instructions in documents and other content can manipulate AI agents that process them, potentially causing actions with users’ privileges. Bowbridge recommends scanning content before agents consume it.

Sep 8, 2026
Security Insights · cyberscoop.com

Waco’s Water Network Shows Why Utilities Need Clear Cybersecurity Ownership

Drawing on Waco’s experience, the author argues that utilities should assign network-wide accountability, inventory cellular-connected equipment, and use microsegmentation to protect water systems. Project Watershed 250 offers Texas utilities assessments and hardening.

Sep 8, 2026
Security Insights · thehackernews.com

How Trusted Execution Environments Can Protect Data Processed by AI Agents

AI agents may expose sensitive data while processing it in memory. The article explains how trusted execution environments and remote attestation can limit host access, while noting their security boundaries and residual risks.

Sep 8, 2026
Security Insights · helpnetsecurity.com

How Ransomware Groups Research Victims and Negotiate Demands

Intel 471’s Dave Ross explains how ransomware groups research victims, set demands, use test decryptions, divide negotiation roles, and apply multi-extortion tactics, alongside the value of pre-incident planning.

Sep 8, 2026
Security Insights · aikido.dev

Jason Haddix Says AI Pentesting Will Reshape Human Testers’ Workflows

Jason Haddix argues AI pentesting can expand testing coverage but depends on human-developed methodology. Aikido cites testing benchmarks and a Doyensec evaluation reporting 49 verified vulnerabilities, while surveyed security leaders report gaps in manual testing.

Sep 8, 2026
Security Insights · helpnetsecurity.com

ToolHive Isolates MCP Servers and Adds Policy and Provenance Controls

ToolHive runs MCP servers in isolated containers and offers policy controls, provenance checks, and gateway features. Identity enforcement and audit logging require integration with an identity provider; its browser-based cloud UI is retired.

Sep 7, 2026
PreviousPage 14 of 54 Next
© 2026 cyber.hendryadrian.com