Fraud Defense Should Start Before the Transaction, Team Cymru Says
Summary
Team Cymru argues that fraud teams can detect and disrupt operations earlier by tracing infrastructure, targeting, and account compromise instead of relying mainly on transaction-level signals.
Key points
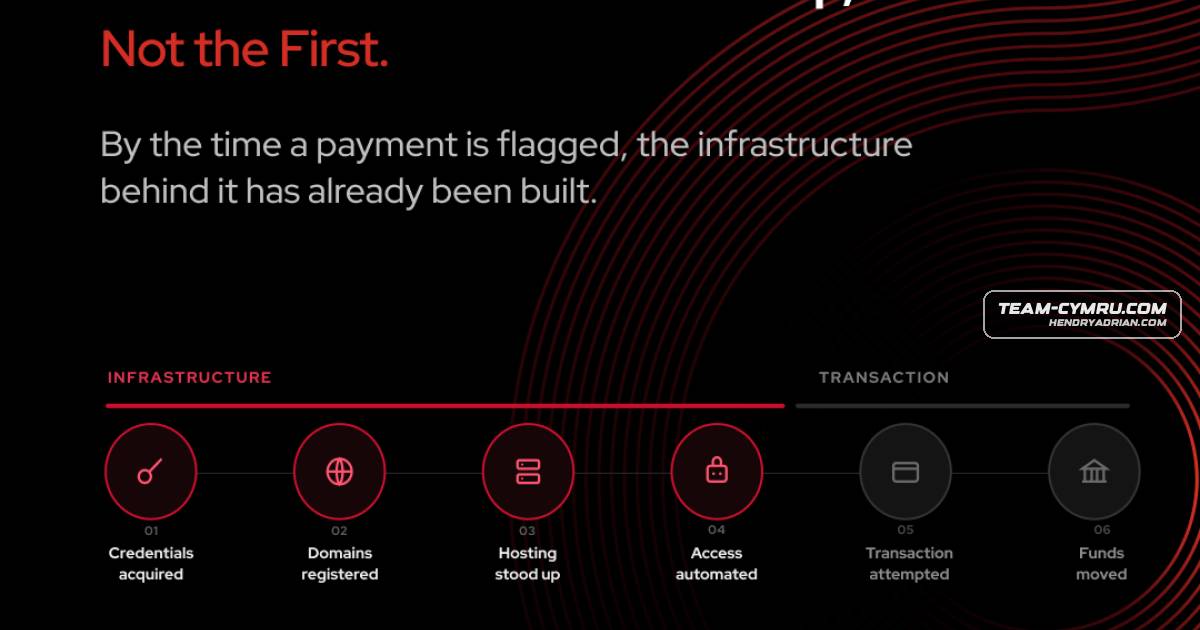
- The article describes fraud as a sequence that begins with infrastructure and targeting before account compromise and monetization.
- It argues that transaction-level detection often engages too late, after fraud infrastructure has been established and accounts may be compromised.
- NetFlow, passive DNS, BGP routing, IP and domain analysis, certificate data, and malware intelligence can help investigators map fraud-related infrastructure and activity.
- Team Cymru says infrastructure-level visibility can reveal links between campaigns and operators that transaction-level systems may treat as isolated events.
- The company says its Pure Signal Command platform combines investigation workflows with APIs and MCP integration.
- Team Cymru says it supports development of the FT3 fraud taxonomy and practitioner communities working on shared fraud intelligence.
Article Details
- Topic
- Infrastructure intelligence for detecting fraud before transactions occur
People
Vendors
Products
Fraud Defense IntelligenceThat gap, between where fraud is detected and where it actually originates, is the problem Team Cymru's Fraud Defense Intelligence work is built to close.Pure Signal Commandthat made it possible, and forward again into detections, mitigations, and disruption. Our Pure Signal Command platform brings that discovery, understanding, and action into a single investigative workflow,