
Shadow AI Poses Data-Exposure Risks for Financial Services Firms
Summary
Unsanctioned AI use in financial services can expose sensitive customer data and create privacy and compliance risks. The article recommends visibility, approved tools, clear policies, and controls such as DLP, SSO, and activity monitoring.
Key points
- Employees may use unapproved AI tools to analyze customer data, draft communications, or summarize calls, potentially sharing sensitive information outside company controls.
- Financial services firms face heightened exposure because they handle sensitive data and have complex regulatory obligations.
- The article says blocking AI outright may encourage employees to bypass restrictions or use personal devices.
- Recommended controls include inventorying AI use, vetting tools, and setting clear acceptable-use policies.
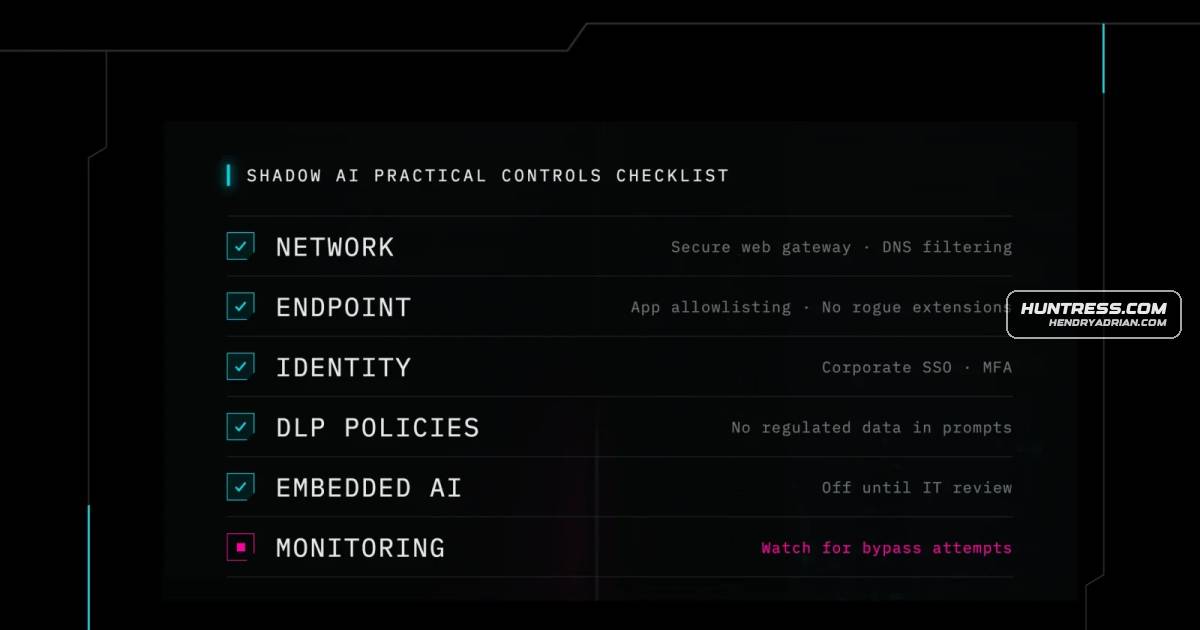
- Suggested technical measures include web and DNS filtering, application allowlisting, corporate SSO and MFA, and DLP controls.
- Organizations are advised to monitor AI-related traffic and endpoint activity and provide ongoing employee education and review of AI tools.
Article Details
- Topic
- Shadow AI governance and risk management in financial services
Products
ChatGPTwith customer data and so they decide to upload this data into a public Generative AI model like ChatGPT. They prompt ChatGPT to analyse the data. Now your organisation's customer data has found itself into aMicrosoft CopilotThe usual obvious tools are out there: ChatGPT, Microsoft Copilot. But we've moved past just prompt tools over the last few years to a huge number of AI meeting and writing tools amongst other virtual assistants and