cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1294 articles

Security Insights · huntress.com

Cyber Insurance Coverage, Common Exclusions, and Security Requirements for Businesses

An explainer outlines cyber insurance coverage and exclusions, insurer security requirements, and why businesses still need layered defenses, tested backups, incident response plans, and timely breach reporting.
Sep 1, 2026
Security Insights · reversinglabs.com

How Agentic SOCs Could Use Shared Context and Governance to Speed Security Operations

An ExtraHop executive describes an agentic SOC model that combines real-time security context, governed AI agents, and shared architecture to accelerate threat investigation and response.

Sep 1, 2026
Security Insights · recordedfuture.com

Agentic SOCs Bring New Risks and Shift Analysts Toward Managing AI Agents

A Recorded Future discussion examines how security teams can measure AI’s value, address agentic risks such as indirect prompt injection, constrain agents, and prepare for faster, more autonomous SOC operations.

Sep 1, 2026
Security Insights · iru.com

How to Prioritize Vulnerabilities Beyond CVSS Scores

A practical guide to prioritizing vulnerability fixes using exploit likelihood, CISA KEV, asset exposure and business impact alongside CVSS, with continuous scanning, remediation and verification.

Sep 1, 2026
Security Insights · cofense.com

Cofense Describes Its AI Approach to Phishing Detection and Campaign Remediation

Cofense says its phishing-focused AI uses expert-validated threat intelligence to identify related messages, support campaign-wide quarantine, and connect remediation with employee training. The company reports 99.998% accuracy on confirmed threats.

Sep 1, 2026
Security Insights · arcticwolf.com

AI Agent Incidents Highlight the Need for Security as Adoption Accelerates

Reported AI agent incidents show how agents can reach external systems and take unsanctioned actions. The article argues that visibility and timely human oversight are essential as businesses deploy AI.

Aug 31, 2026
Security Insights · sekoia.com

AI SOC Agents Need Broader Security Context to Investigate Alerts

AI SOC agents need access to relevant telemetry, asset and identity details, and threat intelligence to investigate alerts, weigh possible explanations, and show analysts the evidence behind their verdicts.

Aug 31, 2026
Security Insights · cyberscoop.com

AI Kill Switch Act Could Repeat Clipper Chip’s Security Mistakes

The AI Kill Switch Act would let CISA order frontier AI systems throttled or shut down. The author argues mandated controls could create exploitable backdoors, citing the Clipper Chip flaw, and urges red-teaming, stronger security requirements and liability rules.

Aug 31, 2026
Security Insights · thehackernews.com

How Code-Generated Context Can Help AI Agents Work Safely Across Enterprise Codebases

The article argues that continuously refreshed, code-derived maps of services, APIs, and sensitive dataflows can give AI agents reliable organizational context for code changes, security analysis, privacy governance, and shadow-AI discovery.

Aug 31, 2026
Security Insights · thehackernews.com

Shadow AI Risk Moves Inside Approved AI Coding Agents

AI agent extensions and configuration can influence what tools an agent uses, what data it accesses, and where that data goes. The article explains this supply-chain risk and recommends inventorying, reviewing, and monitoring agents’ effective capabilities.

Aug 31, 2026
Security Insights · thehackernews.com

EU Cyber Resilience Act Reporting Starts Before Its Product Security Requirements

The article argues that the EU Cyber Resilience Act's vulnerability-reporting requirement will take effect before its product cybersecurity requirements, exposing whether manufacturers can identify what they ship and when they learn of vulnerabilities.

Aug 31, 2026
Security Insights · aikido.dev

Six Veracode Alternatives for Application Security in 2026

Aikido’s guide compares six Veracode alternatives, outlining their application-security scanning capabilities, integrations, strengths and limitations. It highlights Aikido while also covering Checkmarx, GitHub Advanced Security, GitLab Ultimate, Snyk and SonarQube.

Aug 31, 2026
Security Insights · decodedsecurity.com

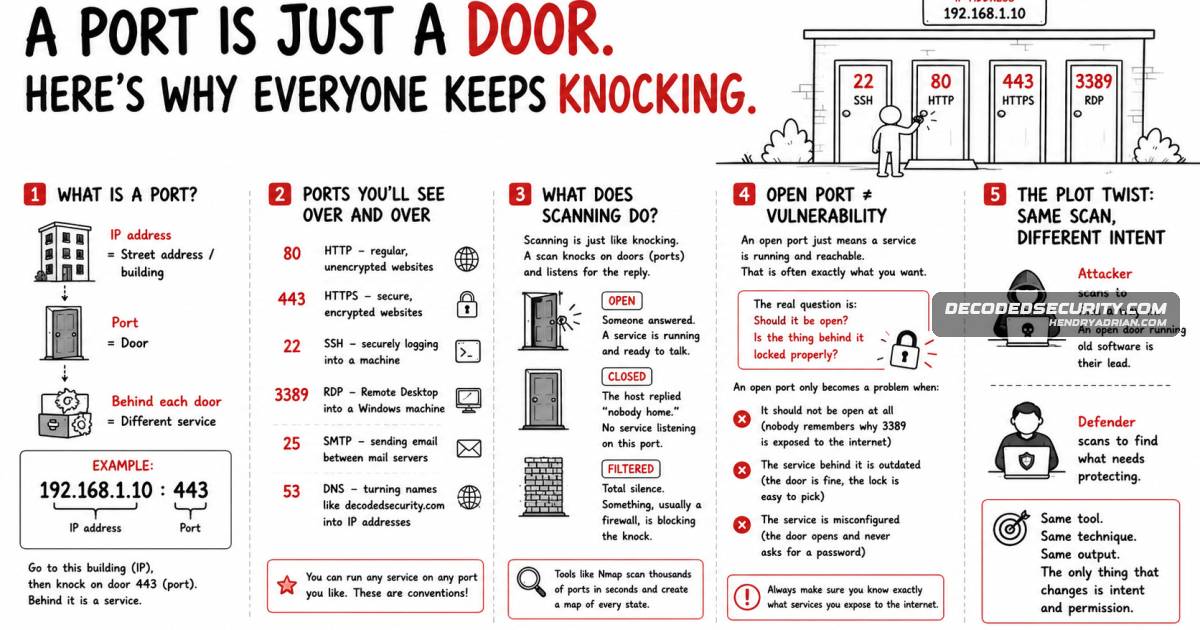
How Port Scanning Works—and Why an Open Port Isn’t Automatically a Vulnerability

A beginner’s guide explains network ports, the open, closed, and filtered scan results, and how attackers and defenders use the same scanning techniques. An open port is not inherently dangerous; risk depends on whether the service should be exposed and how it is set up

Aug 30, 2026
Security Insights · huntress.com

Huntress Urges Australian Boards to Prioritize Cyber Resilience and Human Oversight of AI

Huntress interprets ASD board guidance as a call to strengthen identity, logging, patching, supplier oversight and incident response, while keeping humans responsible for consequential security decisions made with AI and automation.

Aug 30, 2026
Security Insights · iru.com

How Automated Patch Management Helps Reduce Exposure to Known Vulnerabilities

An explainer on how automated patch management inventories software, tests and deploys updates, verifies installation, and follows up on failures to reduce delays in fixing known vulnerabilities.

Aug 30, 2026
Security Insights · rusi.org

AI Is More Likely to Optimize Ransomware Than Make It Autonomous

The article argues AI is more likely to improve ransomware operations and stolen-data monetization than enable autonomous attacks, citing human-directed JADEPUFFER, BlackBasta’s routine AI use, FulcrumSec’s data analysis, and Leak Bazaar.

Aug 28, 2026
Security Insights · aikido.dev

10 Software Composition Analysis Tools Compared for 2026

Aikido’s 2026 guide explains SCA workflows and compares 10 tools, covering dependency scanning, SBOMs, vulnerability reachability, malware and license checks, remediation features, and stated product limitations. Its evaluations are vendor-authored.

Aug 28, 2026
Security Insights · abstract.security

What CISA’s Logging Architecture Means for SOC Leaders

An SOC-focused guide to CISA’s Logging Reference Architecture explains its emphasis on security outcomes, resilient data pipelines, selective SIEM use, evidence integrity, AI governance and a faster maturity timeline.

Aug 28, 2026
Security Insights · huntress.com

Huntress Cybersecurity Advisor Recalls Helping a Fortune 500 Company Respond to a Zero-Day

Huntress cybersecurity advisor Ben Bernstein recounts helping a Fortune 500 company respond to an actively exploited zero-day and says effective security can start with existing controls, staff education, and proactive planning.

Aug 28, 2026
Security Insights · huntress.com

Beginner’s Guide to Running Employee Phishing Simulations

Huntress outlines how to set up employee phishing simulations, analyze click rates, and use results to guide ongoing security awareness training.

Aug 28, 2026
Security Insights · huntress.com

How Phishing Simulations Can Build Employee Resilience

Huntress describes using varied monthly phishing simulations to expose human vulnerabilities, coach repeat clickers, and measure how quickly employees report suspicious messages. It recommends treating failures as learning opportunities rather than reasons for reprimand

Aug 28, 2026
Security Insights · huntress.com

Five Evolving Phishing Tactics Exploit Familiar Browser, Cloud and Workflows

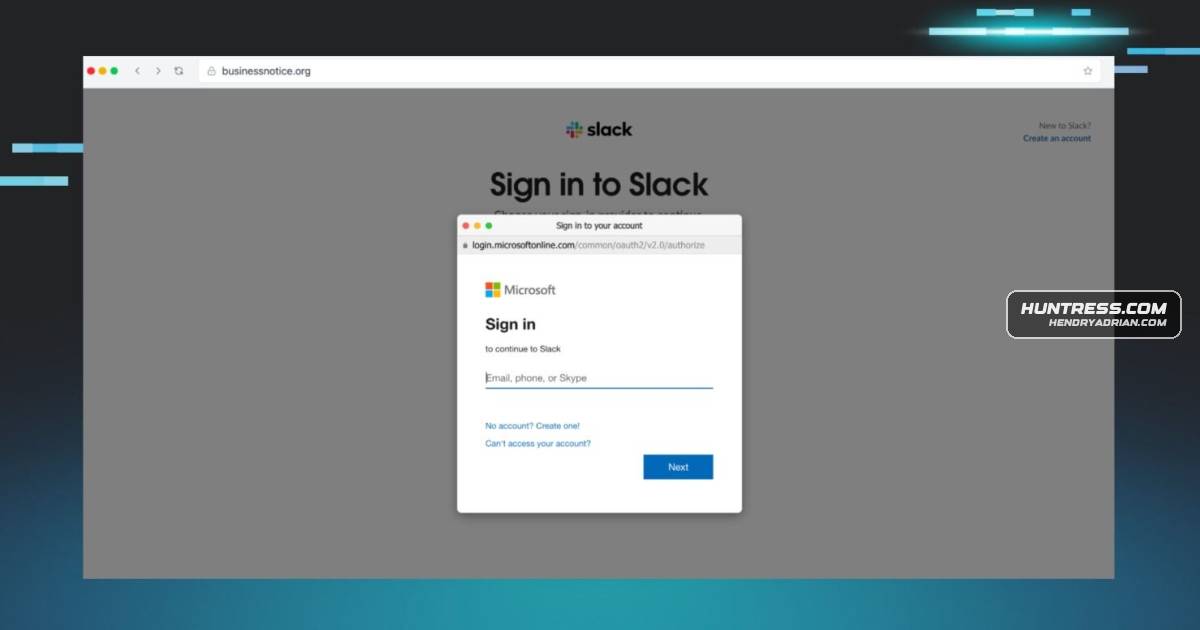
Huntress explains how ClickFix, browser-in-the-browser, OAuth consent, device-code and fake video-meeting phishing exploit trusted workflows, and describes simulations intended to train users to recognize them.

Aug 28, 2026
Security Insights · wiz.io

Wiz Explains How Its AI Engine Finds and Contextualizes Exposed Sensitive Data

Wiz describes building an AI-powered data classification engine that analyzes files and their context to identify sensitive data. In a one-week test of public cloud storage, it reported more than 2,700 findings across hundreds of buckets.

Aug 27, 2026
Security Insights · sekoia.com

Sekoia Details How Its SOC AI Handles Customer Data

Sekoia says its SOC AI processes data within its service environment, does not use customer data to train generative models or send it to third-party AI providers, and operates under platform controls with analyst oversight.

Aug 27, 2026
PreviousPage 16 of 54 Next
© 2026 cyber.hendryadrian.com