cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1292 articles

Security Insights · darkowl.com

Encryption Explained: How It Protects Data—and How Threat Actors Misuse It

An explainer on encryption, its symmetric and asymmetric forms, uses in protecting data, misuse by ransomware operators and infostealers, and enterprise practices such as strong algorithms and secure key management.

Sep 24, 2026
Security Insights · cyberbuilders.substack.com

Bruce Schneier: AI Expands Hacking Beyond Code, Making Integrity a Central Security Challenge

A commentary on Bruce Schneier’s DEF CON talk argues that AI broadens hacking beyond software, amplifies its speed and scale, and makes data integrity a central security challenge as AI systems affect real-world decisions.

Sep 24, 2026
Security Insights · helpnetsecurity.com

How to Limit Sensitive Data Exposure from AI Agents

Nol8 CEO Kelly Herrell recommends mapping AI agents’ data paths and enforcing runtime policies to control what sensitive information agents can access, receive, and disclose.

Sep 24, 2026
Security Insights · aikido.dev

CodeQL Alternatives: Comparing SAST Tools and Their Trade-offs

A vendor-authored guide compares six CodeQL alternatives, weighing setup, cross-file analysis, finding noise, workflow, coverage, and cost. It highlights CodeQL database-build limitations and promotes Aikido while discussing competing tools.

Sep 24, 2026
Security Insights · darkreading.com

How to Build and Migrate to a SASE Security Framework

A six-stage guide to SASE adoption recommends assessing infrastructure, piloting in controlled environments, migrating workloads gradually, redesigning policies, training teams, and continuously reviewing security and performance.

Sep 24, 2026
Security Insights · levelblue.com

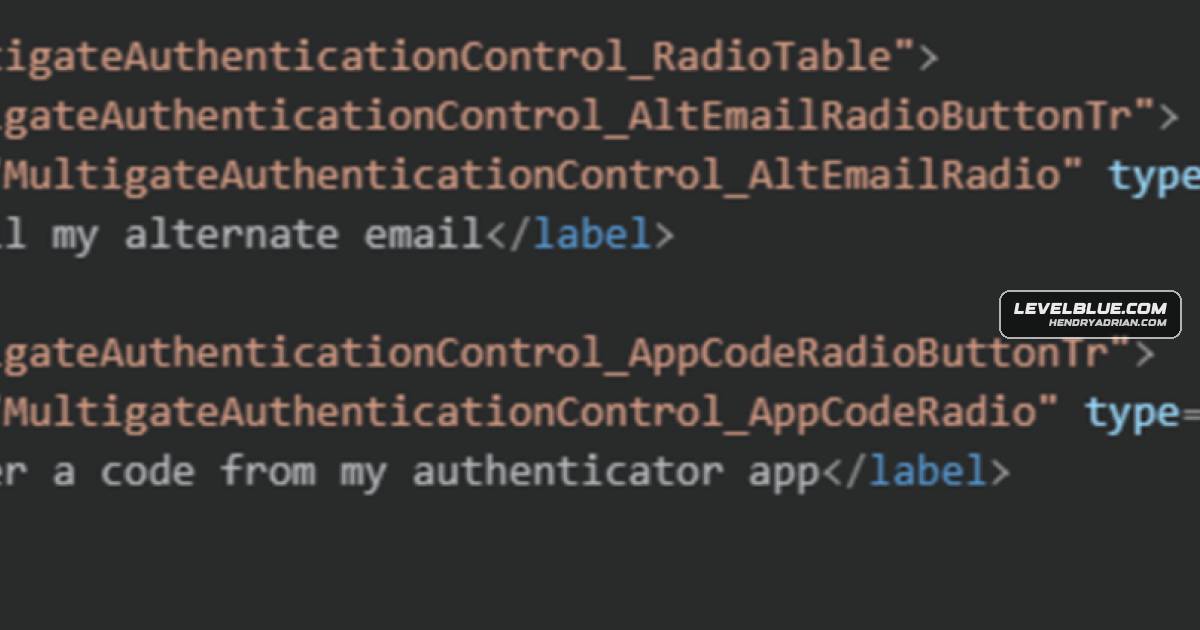
Microsoft SSPR Portal Can Reveal Accounts and Registered Authentication Methods

The article explains how Microsoft’s public SSPR portal can expose whether accounts exist and, for some users, their registered reset methods. It describes the risks, limitations, an automation tool, and defensive measures.

Sep 23, 2026
Security Insights · cyberscoop.com

Op-Ed Proposes AI Assurance Compact to Safeguard Critical Infrastructure

Auburn University’s McCrary Institute leaders propose an AI Assurance Compact focused on capability, control and continuity, including independent evaluations, incident reporting and tested fallback plans for critical systems.

Sep 23, 2026
Security Insights · rapid7.com

How DAST Validates Application Risk at Runtime

Rapid7 explains how dynamic application security testing can reproduce and validate weaknesses in running applications, helping teams prioritize exposure and provide developers with evidence for remediation.

Sep 23, 2026
Security Insights · helpnetsecurity.com

Scamwise Checks Messages, Websites and Phone Numbers for Signs of Fraud

A hands-on review found Scamwise flagged a phishing email, assessed a legitimate website as safe, and gave an indeterminate result for a phone number. The service explains its verdicts, but they are not guarantees.

Sep 23, 2026
Security Insights · reliaquest.com

Five Uses for Agentic Red Teaming Beyond Point-in-Time Testing

The article explains five uses for continuous, AI-agent-driven red teaming: mapping attack paths, validating detections, testing identity blast radius, retesting pentest findings, and emulating threat actors.

Sep 23, 2026
Security Insights · securonix.com

ISO/IEC 42001 Calls for Ongoing Governance as AI Agents Enter Production

Securonix argues that ISO/IEC 42001 governance must continue after AI deployment, with clear ownership, reassessed risks, access controls, monitoring, audit trails and recovery measures as agents and their capabilities change.

Sep 23, 2026
Security Insights · aikido.dev

Cyber Resilience Act: Reporting Deadlines and Compliance Guidance

The article explains the CRA’s mandatory reporting deadlines, who must report exploited vulnerabilities or severe incidents, how the Single Reporting Platform works, and upcoming standards ahead of full compliance in 2027.

Sep 23, 2026
Security Insights · malwareinfo.app

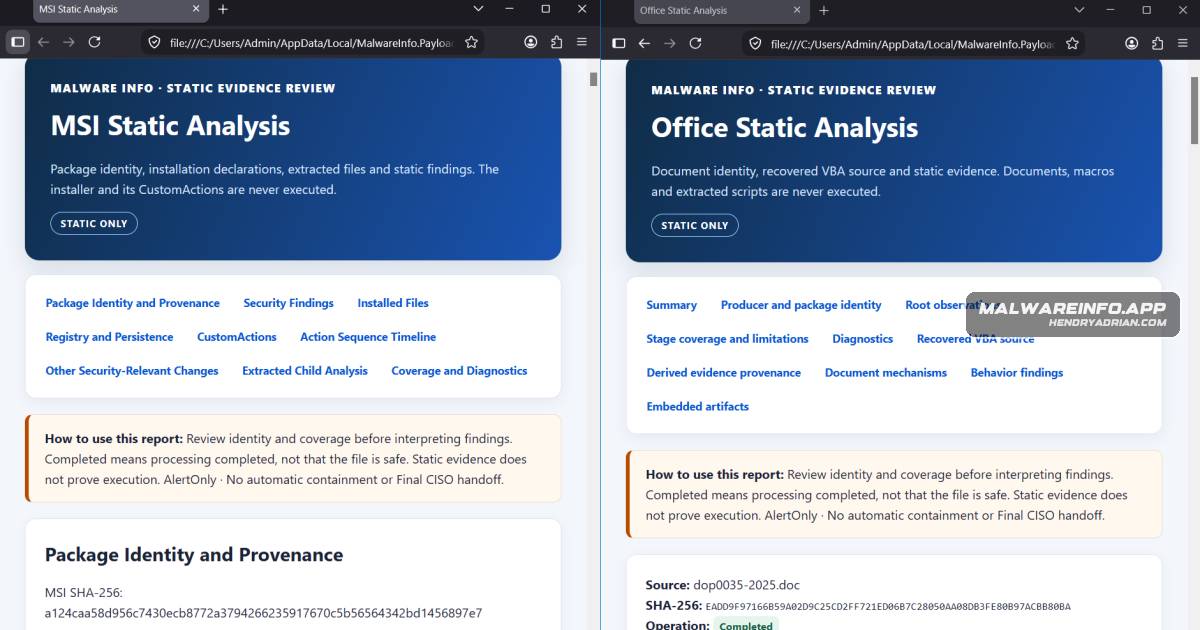
Static Analysis of MSI and Legacy Word Files Reveals Installer and Macro Behavior

A static-analysis walkthrough extracts five files from a fake GlobalProtect MSI and recovers VBA from an encrypted Word document, showing configured installer actions and a staged macro chain while distinguishing source evidence from execution.

Sep 23, 2026
Security Insights · reversinglabs.com

Flat Security Budgets Are Being Reallocated to AI, Agent Visibility and Token Costs

Organizations are shifting existing cybersecurity budgets toward AI security and agentic SOCs. The article highlights growing needs for agent visibility and identity controls, and warns that inefficient agents can drive up compute costs through excess reasoning and tool

Sep 23, 2026
Security Insights · cofense.com

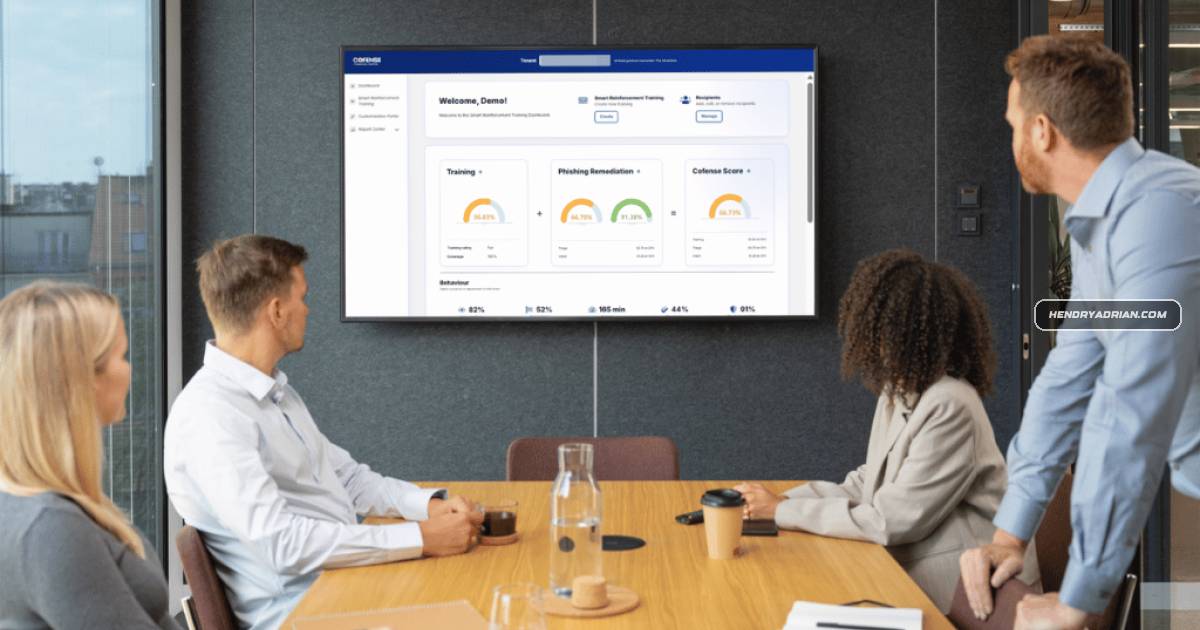
Cofense Says Phishing Training Should Measure Behavior Change, Not Compliance

Cofense argues that phishing defense should measure employees’ ability to recognize threats and connect that competency with real-world phishing and remediation signals, rather than relying on training completion or risk scores alone.

Sep 23, 2026
Security Insights · matthewrosenquist.substack.com

ShinyHunters Allegedly Hacks Clop Site and Demands Ransom

The author says ShinyHunters hacked a dark-web site associated with the Clop group, claims to have stolen data, and is demanding a ransom, and reflects on the impact of cybercriminal groups targeting one another.

Sep 22, 2026
Security Insights · hackingarticles.in

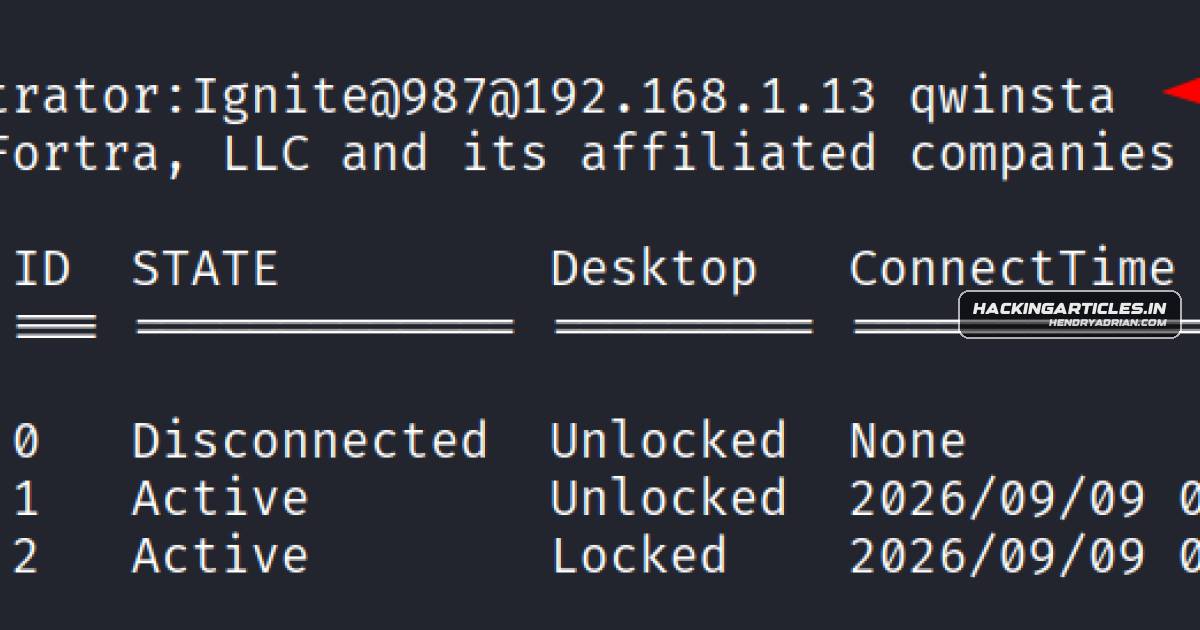
Using Impacket’s tstool to Control Windows Sessions and Hijack RDP Sessions

A hands-on walkthrough shows how Impacket’s tstool uses MSRPC to enumerate and control Windows sessions, hijack an RDP session, and authenticate with hashes, Kerberos keys, or tickets, followed by mitigation advice.

Sep 22, 2026
Security Insights · cybersecuritypulse.net

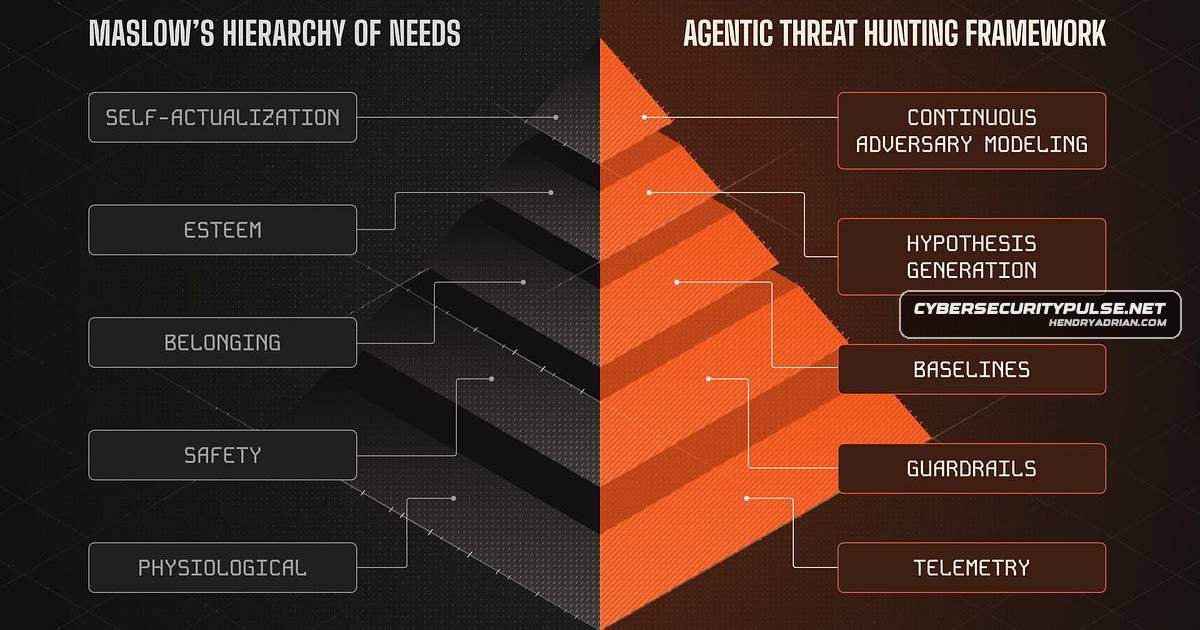
Why SOCs Need Strong Foundations Before Deploying Agentic Threat Hunting

The article argues that AI agents amplify gaps in SOC telemetry, context, baselines, and safeguards. It outlines a staged approach to agentic threat hunting, emphasizing reliable data and bounded actions before increasing autonomy.

Sep 22, 2026
Security Insights · zimperium.com

Zimperium: Agentic AI Lowers the Barrier to Mobile App Attacks

Zimperium argues agentic AI can lower the skill and time needed to reverse-engineer mobile apps, bypass protections, automate app interactions and scale fraud, while relying on existing attack techniques rather than a new vulnerability class.

Sep 22, 2026
Security Insights · matthewrosenquist.substack.com

Commentary Urges International Limits on Misuse of Autonomous AI Weapons

Matthew Rosenquist warns that autonomous AI weapons, including cyber variants, could be deliberately used against civilians, societies, and critical infrastructure, and urges international policymakers to establish boundaries before such capabilities scale.

Sep 21, 2026
Security Insights · securityweek.com

Comcast CISO Noopur Davis on Career Growth, Calm Leadership and Burnout

Comcast Global CISO Noopur Davis describes her unplanned path from software development into cybersecurity leadership and shares views on business alignment, calm crisis management, cohesive teams, and giving staff time off after intense work.

Sep 21, 2026
Security Insights · picussecurity.com

How Security Validation Can Support India’s DPDPA Compliance

A practical guide to India's DPDPA security duties explains safeguards, breach reporting, monitoring and audit requirements, and how security validation can help organizations test controls and document improvements.

Sep 21, 2026
Security Insights · thehackernews.com

Enterprise Mobile AI Brings Data Governance and Device-Security Trade-Offs

The article outlines enterprise security questions for mobile AI, including where data is processed, who controls cloud use, whether AI is tied to managed identities, and whether devices can be trusted.

Sep 21, 2026
Security Insights · thehackernews.com

Building an AI-Era Risk Program Beyond ISO 27001 Certification

OneTrust CISO Tim Mullen argues that ISO 27001 should be a foundation, not the finish line, for AI-era risk management. He recommends connecting risk decisions to business context, standardizing before automating, and continuously monitoring control effectiveness.

Sep 21, 2026
PreviousPage 12 of 54 Next
© 2026 cyber.hendryadrian.com