Static Analysis of MSI and Legacy Word Files Reveals Installer and Macro Behavior
Summary
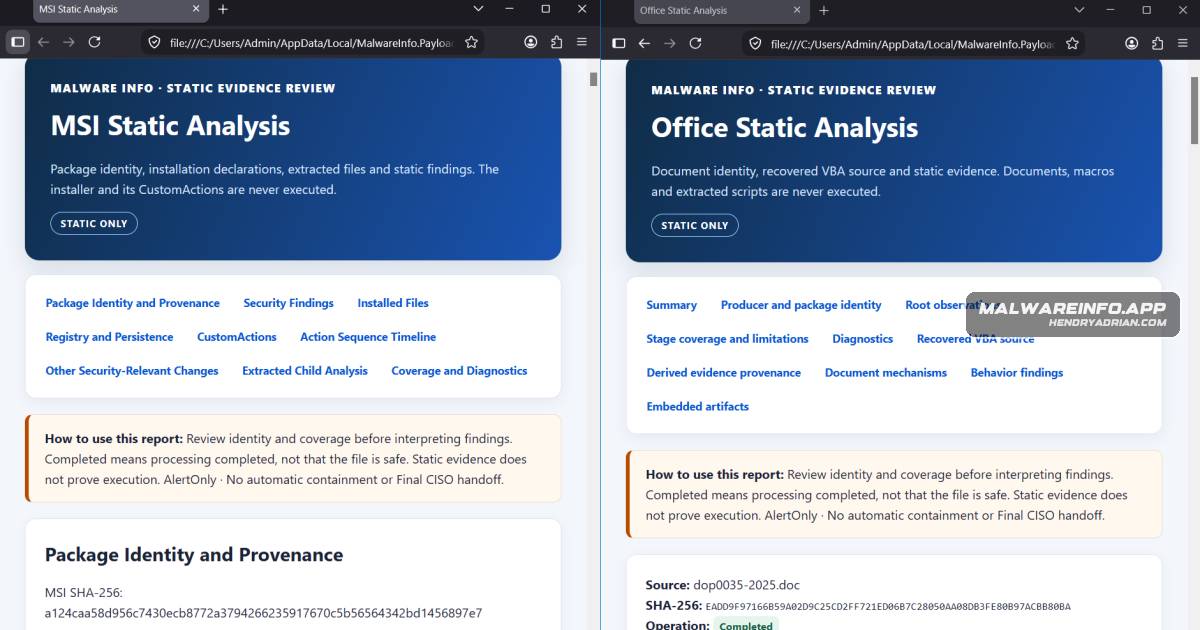
A static-analysis walkthrough extracts five files from a fake GlobalProtect MSI and recovers VBA from an encrypted Word document, showing configured installer actions and a staged macro chain while distinguishing source evidence from execution.
Key points
- The GlobalProtect MSI yielded five files with recorded hashes and provenance; its configuration includes a CustomAction, RunOnce entries, and upgrade-removal behavior, but the report does not establish that the installer ran.
- Static analysis recovered two VBA modules from an encrypted legacy Word document, including a Document_Open auto-execution procedure.
- Recovered VBA describes reconstructing DellHeuristics.zip from form data, writing Startup-folder scripts, unpacking files, and creating a scheduled task; execution and successful reconstruction were not confirmed.
- The macro prepares an HTTP request to hxxps://edmsvpn[.]gov[.]en-mm[.]com/lang=mm, and the document contains an external relationship to hxxps://edmsvpn[.]gov[.]en-mm[.]com/favicon.ico; no server response or payload download was established.
- The analysis was static-only: neither sample nor its code was executed, and no observed infrastructure was contacted.
- Coverage was Partial in both cases; the Word analysis did not support VBA P-code comparison, so it could not assess VBA stomping.
Article Details
- Topic
- Static extraction and analysis of evidence from MSI installers and legacy Word documents, illustrated by a fake GlobalProtect installer and a document containing staged VBA logic.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 33d696728101c9caf6ebb215ba176bbb94e5cc16218b574029b622fd6e3bee8c | SHA-256 of GlobalProtect.exe extracted from the deceptive installer. |
| SHA256 | a124caa58d956c7430ecb8772a3794266235917670c5b56564342bd1456897e7 | SHA-256 of the deceptive GlobalProtect.msi installer identified in a fake GlobalProtect campaign targeting Myanmar. |
| SHA256 | eadd9f97166b59a02d9c25cd2ff721ed06b7c28050aa08db3fe80b97acbb80ba | SHA-256 of the encrypted legacy Word document associated with the DellHeuristics delivery chain. |
| URL | hxxps[:]//edmsvpn[.]gov[.]en-mm[.]com/favicon.ico | External relationship recorded in the Office report for the suspicious document. |
| URL | hxxps[:]//edmsvpn[.]gov[.]en-mm[.]com/lang=mm | URL requested by the recovered VBA in the suspicious document; the article identifies it as network-related document evidence. |
MITRE ATT&CK
T1053.005 · Scheduled TaskRecovered batch content contains a command to create a scheduled task that runs DellHeuristics.exe every five minutes.T1059.005 · Visual BasicRecovered VBA and generated batch/VBS stages use scripting to continue the document's execution chain.T1105 · Ingress Tool TransferThe recovered macro prepares an HTTP GET request to a specified URL; the article notes that a payload download is not confirmed.T1547.001 · Registry Run Keys / Startup FolderRecovered VBA writes a VBS file into the current user's Startup folder for persistence.
Products
GlobalProtectGlobalProtect.msi, a deceptive installer previously examined in our investigation of a fake GlobalProtect campaign targeting Myanmar; andMalwareINFO Pro Payload & Memory AnalyzerOur earlier introduction to MalwareINFO Pro Payload & Memory Analyzer focused mainly on Portable Executable files and retained memory artifacts.