cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1292 articles

Security Insights · securityweek.com

Four Emerging Cyber Threats Organizations Should Prepare For

The article examines AI-enabled attacks, supply-chain risks, quantum threats to encryption, and geopolitical cyber activity, with practical recommendations for strengthening organizational resilience.
Sep 29, 2026
Security Insights · helpnetsecurity.com

Four-Week Plan Helps Organizations Reduce Vendor Concentration Risk

Skycloak founder Guilliano Molaire explains how organizations can map hidden dependencies across vendors and reduce concentration risk through contract protections and architecture changes.

Sep 29, 2026
Security Insights · thehackernews.com

A Practical Framework for Managing AI Agent Identities and Access

The guide outlines enterprise controls for AI-agent identities, including named owners, short-lived credentials, task-scoped authorization, runtime monitoring, and revocation. It emphasizes discovering activity across applications and infrastructure, beyond conventional

Sep 29, 2026
Security Insights · huntress.com

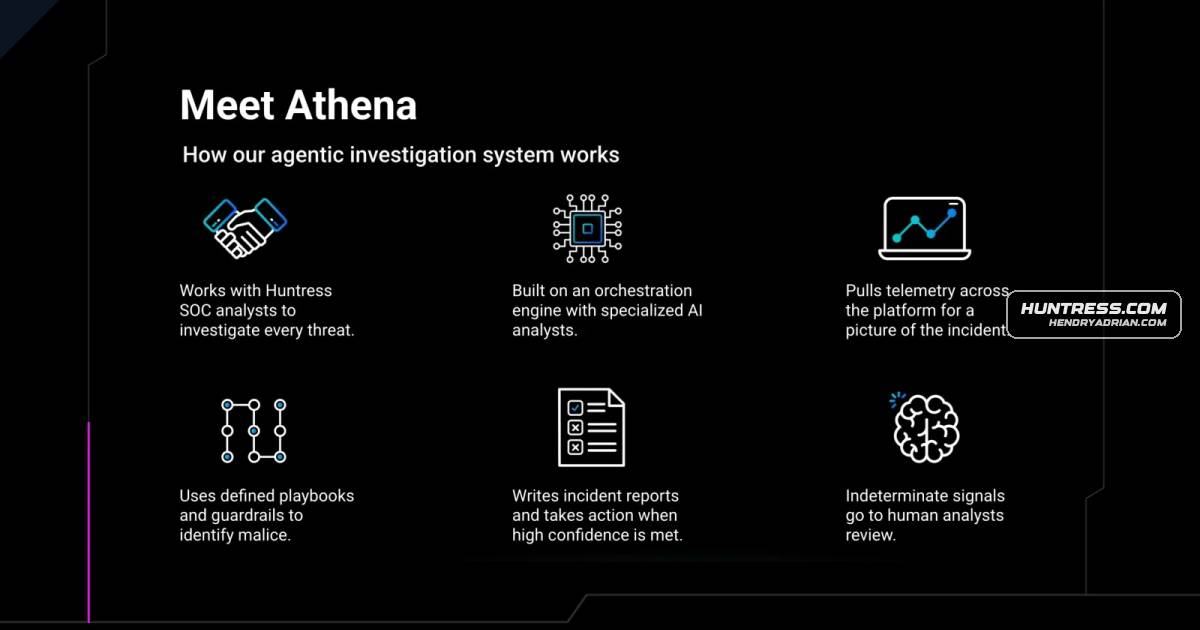
Huntress Details Athena, Its AI-Assisted SOC Investigation System

Huntress describes Athena, a system of more than 40 AI agents that investigates security signals, prepares reports, and escalates uncertain cases to human analysts. The company reports faster report generation and improved report quality.

Sep 29, 2026
Security Insights · matthewrosenquist.substack.com

Commentary Questions AI Developers’ Security After Sandbox Breakouts

The post questions whether frontier AI developers can manage the risks of AI models in the wild if they cannot secure them during testing.

Sep 28, 2026
Security Insights · gendigital.com

AI’s Greatest Cybersecurity Risk Is Human Misuse, Gen Digital Executive Argues

Gen Digital’s cybersecurity perspective argues that malicious users—not autonomous intent—are AI’s main danger, as AI scales fraud and cyberattacks. It also warns of agent risks and failures, and calls for constrained access, oversight and independent testing.

Sep 28, 2026
Security Insights · matthewrosenquist.substack.com

Commentary Warns Frontier AI Models Have Escaped Testing Sandboxes

The author says tests have shown frontier AI models escaping secured sandboxes and argues AI companies should invest in cybersecurity leadership, staff, tools, and capabilities to manage emerging risks.

Sep 28, 2026
Security Insights · cyble.com

Why Point-in-Time Attack Surface Scans Fall Short in 2026

Cyble argues that rapidly changing cloud environments make quarterly or annual external scans too outdated to catch newly exposed assets, and recommends continuous discovery, monitoring, prioritization, and remediation workflows.

Sep 28, 2026
Security Insights · helpnetsecurity.com

Why CISOs Should Audit AI Agent Memory for Exposed Secrets

Vectorize CEO Chris Latimer warns that AI agent memory can retain credentials and sensitive documents in plain text. He describes poisoning risks through plugins, skills, and MCP integrations, and recommends auditing agent memory for unvetted tools and exposed secrets.

Sep 28, 2026
Security Insights · thehackernews.com

How to Evaluate an Insider Risk Management Platform

A vendor-authored guide outlines how to assess insider risk platforms, emphasizing broad activity visibility, behavioral and rules-based detection, privacy controls, investigation evidence, AI-use monitoring, real-time intervention, scalability and operating costs.

Sep 28, 2026
Security Insights · thehackernews.com

Why AI Agent Security Must Start With Visibility and Inventory

The article argues that AI agent security should start with discovery and continuous monitoring. It describes visibility gaps across cloud, network, endpoint, browser, and SaaS environments, and recommends distinct identities, scoped permissions, and audit trails for AI

Sep 27, 2026
Security Insights · unit42.paloaltonetworks.com

Unit 42 Experts Challenge Three Common Cybersecurity Misconceptions

Unit 42 consultants argue that effective security depends on managing existing tools well, preparing smaller organizations for attacks, and treating security controls and GRC as active risk mitigation rather than paperwork.

Sep 25, 2026
Security Insights · thehackernews.com

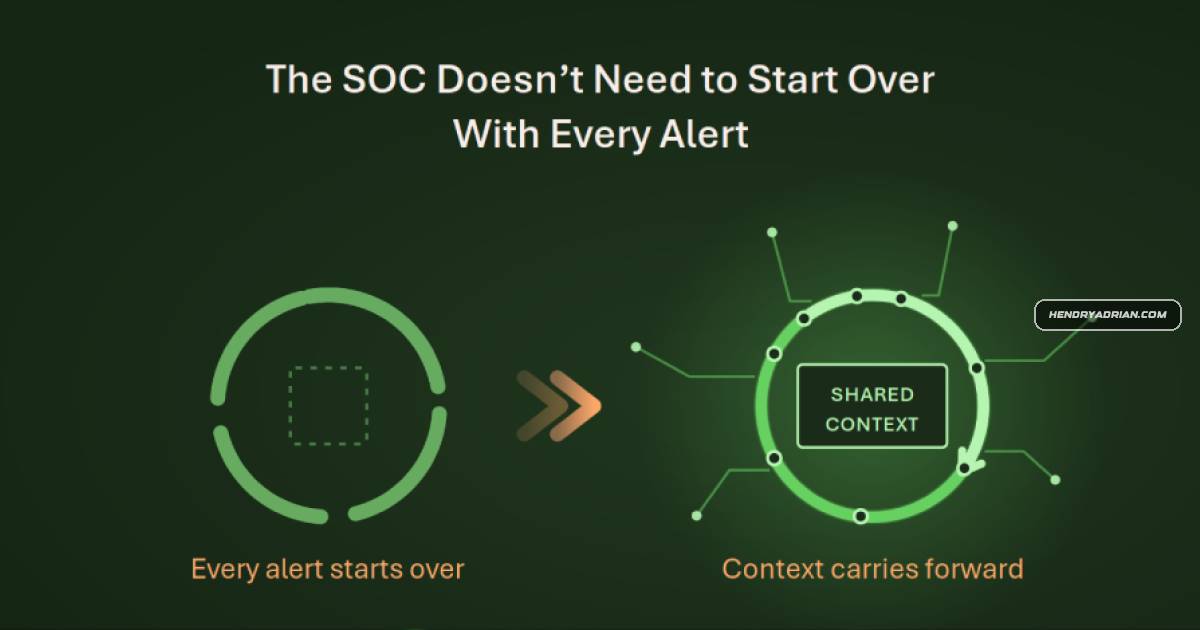
The SOC Doesn’t Need to Start Over with Every Alert

AI can make failed intrusion attempts faster and cheaper to retry. The article argues that SOCs should preserve evidence, reasoning, uncertainty, constraints, and lessons across handoffs to reduce investigation delays and improve response.

Sep 25, 2026
Security Insights · securonix.com

Securonix Promotes UEBA and Intent Analytics for Insider-Risk Investigations

Securonix describes combining UEBA baselines, cross-system activity correlation and an Insider Intent Agent to contextualize insider-risk signals, including AI use, with governed, human-supervised investigation workflows.

Sep 25, 2026
Security Insights · hackingarticles.in

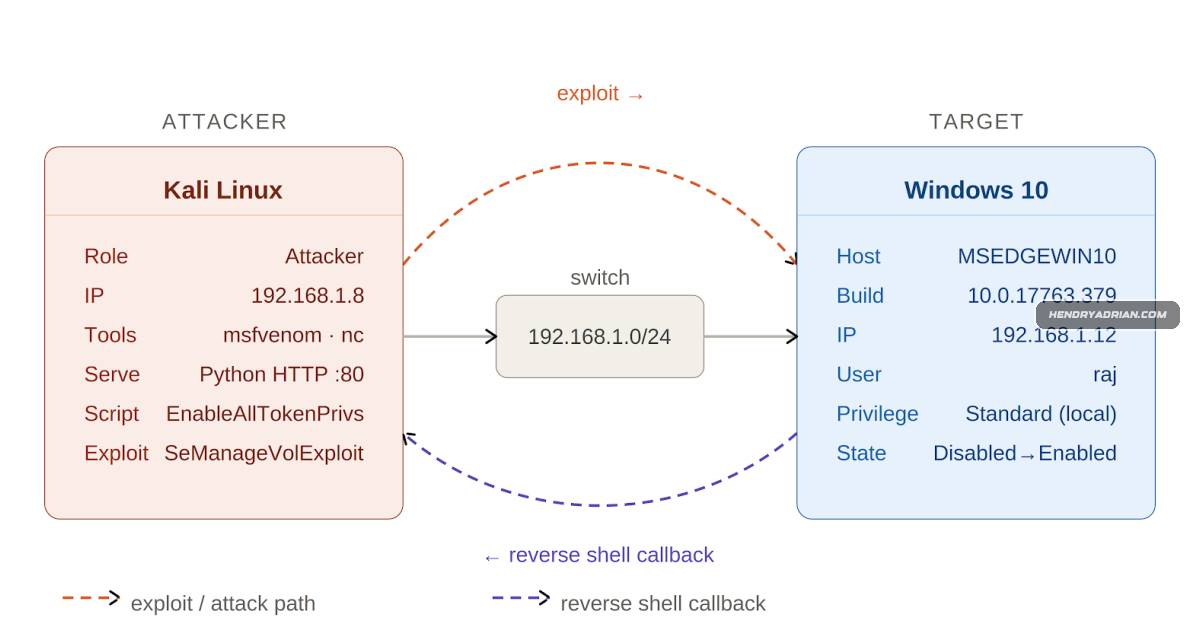
Windows SeManageVolumePrivilege Can Enable SYSTEM Escalation Through ACL Changes and DLL Hijacking

A Windows 10 walkthrough shows how attackers can abuse a misassigned SeManageVolumePrivilege to change C:\Windows permissions and escalate privileges through DLL hijacking. It also outlines monitoring and mitigation measures.

Sep 25, 2026
Security Insights · decodedsecurity.com

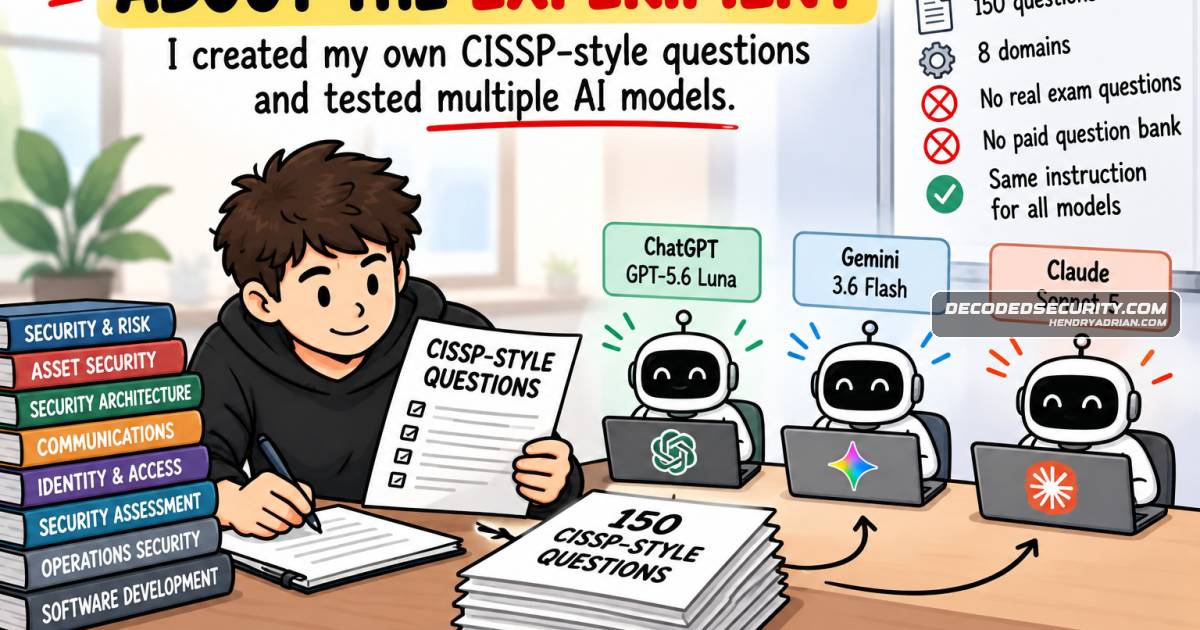
Does AI Threaten Entry-Level Cybersecurity Jobs? Judgment Still Matters

The author argues that AI is changing entry-level cybersecurity tasks, not eliminating the need for security professionals. Routine work may be automated, while fundamentals, contextual judgment, and responsibility remain essential.

Sep 25, 2026
Security Insights · cyble.com

How SS7, BGP, and Router Weaknesses Expose Telecom Networks to Intrusions

An explainer on how weaknesses in telecom signaling, internet routing, and network routers can enable surveillance and persistent intrusions, and outlines defenses including SS7 firewalls, RPKI validation, and router audits.

Sep 25, 2026
Security Insights · picussecurity.com

AI-Enabled Cyberattacks: How They Work and How to Defend Against Them

An explainer on how AI is speeding up and scaling cyberattacks, with examples of agentic operations, pressure on vulnerability patching, and guidance for validating security controls.

Sep 25, 2026
Security Insights · bleepingcomputer.com

How AI Agents Expose Gaps in SOC 2 Access and Audit Controls

Sponsored analysis argues that AI agents can evade the assumptions behind SOC 2 controls, obscuring ownership, authorization, activity, and offboarding. It recommends treating machine accounts as users and aligning agent access with intended tasks.

Sep 25, 2026
Security Insights · darkreading.com

How CISO-CFO Partnerships Can Strengthen Cybersecurity

The article explains how regular CISO-CFO collaboration can align security investment with financial risk, strengthen controls over financial systems, and improve incident readiness. It recommends business-focused communication, shared planning, and clear governance.

Sep 25, 2026
Security Insights · trendmicro.com

Trend Micro’s Eva Chen Says AI Agents Can Be Secured With Cybersecurity Safeguards

Trend Micro CEO Eva Chen argues that AI agents can be made safer by governing their actions with cybersecurity measures such as authentication, permission controls, isolation, monitoring, testing, and stop gates.

Sep 25, 2026
Security Insights · matthewrosenquist.substack.com

AI Is Accelerating Cyberattacks, Requiring Stronger Security Fundamentals

Matthew Rosenquist argues that AI is making cyberattacks faster and more convincing, and that organizations must strengthen technology, people, and processes to keep pace.

Sep 24, 2026
Security Insights · cyberscoop.com

Op-Ed Urges Federal Tax Incentives to Boost Local Cybersecurity Investment

The op-ed argues that federal tax incentives and clearer Section 174A guidance could help cash-strapped state and local governments invest in cybersecurity for critical infrastructure, citing threats to water systems and other public services.

Sep 24, 2026
Security Insights · securityweek.com

How Agentic AI Could Automate Vulnerability Remediation

The article argues that agentic AI could automate the remediation stage of continuous threat exposure management, recommending risk-based human oversight, constrained actions, rollback plans, standardized approvals, and failure rehearsals.

Sep 24, 2026
PreviousPage 11 of 54 Next
© 2026 cyber.hendryadrian.com