Using Impacket’s tstool to Control Windows Sessions and Hijack RDP Sessions
Summary
A hands-on walkthrough shows how Impacket’s tstool uses MSRPC to enumerate and control Windows sessions, hijack an RDP session, and authenticate with hashes, Kerberos keys, or tickets, followed by mitigation advice.
Key points
- Impacket’s tstool remotely uses Windows Terminal Services interfaces over MSRPC, requiring valid credentials and network access but no installed agent or dropped binary.
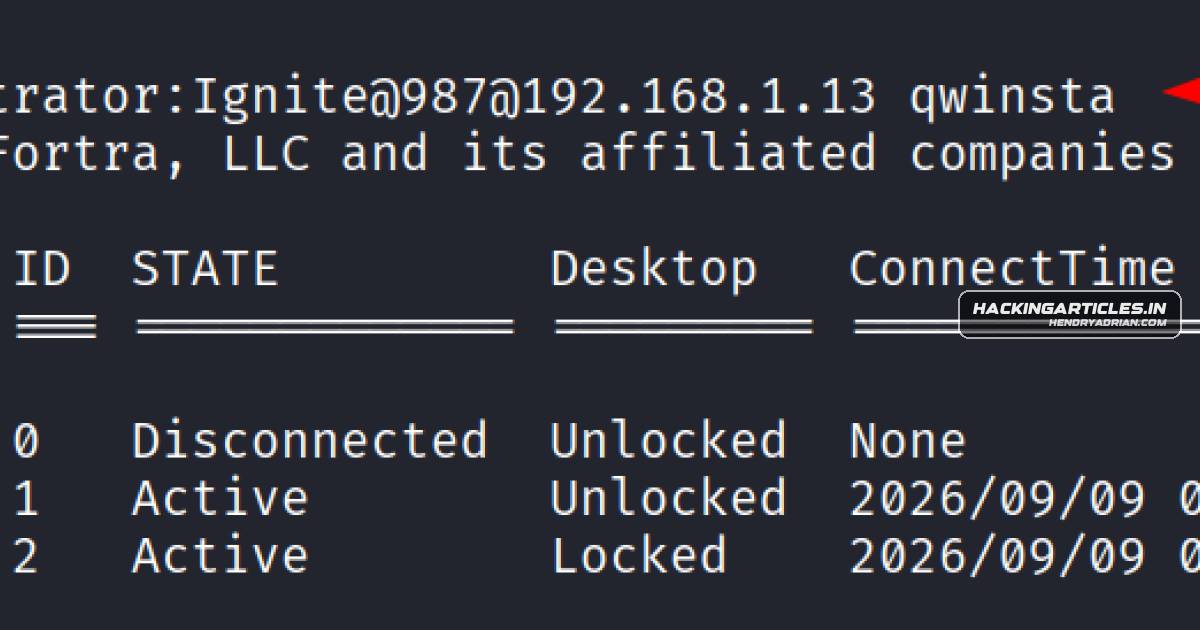
- The walkthrough demonstrates session and process enumeration, remote process termination, session disconnect and logoff, host reboot, and user messaging.
- With sufficient privileges, tscon can redirect an active user’s RDP session to an administrator’s session, giving interactive access without learning the user’s password.
- The tool supports NTLM hash, Kerberos AES key, and cached-ticket authentication, demonstrated against a domain controller.
- Recommended defenses include least privilege, restricting RDP logon rights and remote control, using RestrictedAdmin or Remote Credential Guard, and limiting network access to domain controllers.
- The article advises monitoring Terminal Services MSRPC activity and relevant Windows session, logoff, shutdown, and process-termination events.
Article Details
- Topic
- Using impacket-tstool to enumerate and control Windows Terminal Services sessions, including RDP session hijacking and authentication with recovered credentials
MITRE ATT&CK
T1057 · Process DiscoveryUses tasklist to enumerate processes running on the remote host.T1550.002 · Pass the HashAuthenticates to the target with an NTLM hash using Pass-the-Hash.T1550.003 · Pass the TicketAuthenticates using a cached Kerberos ticket through Pass-the-Ticket.T1563.002 · RDP HijackingUses tscon to attach a user's active RDP session to an operator-controlled session.
Vendors
Products
Active DirectoryThat combination makes it valuable for post-exploitation reconnaissance, lateral movement, and session hijacking across Active Directory estates.Microsoft WindowsTerminal Services, better known today as Remote Desktop Services, governs every interactive and remote session on a Windows host.Remote Desktop ServicesTerminal Services, better known today as Remote Desktop Services, governs every interactive and remote session on a Windows host.