cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1292 articles

Security Insights · thehackernews.com

Phishing Kits Steal Valid Sessions, Moving Attacks Beyond MFA

The article explains how phishing kits and infostealer malware steal authenticated sessions, letting attackers access accounts after successful MFA. It recommends revoking sessions and refresh tokens, improving post-login detection, and limiting account privileges.

Sep 21, 2026
Security Insights · thehackernews.com

Why Deepfake Laws Alone Won’t Protect the 2026 Elections

The article argues that deepfake legislation cannot stop election-related impersonation quickly enough and recommends proactive monitoring, rapid platform response, and cryptographic verification of campaign communications.

Sep 21, 2026
Security Insights · thehackernews.com

Identity Visibility Helps Security Teams Find Hidden Access and Reduce Risk

The article explains how identity visibility can uncover unregistered accounts, excessive permissions, and cross-cloud trust paths, and outlines discovery, access mapping, ownership, behavioral monitoring, and remediation steps for improving identity security.

Sep 19, 2026
Security Insights · sekoia.com

Four Questions MSSPs Should Ask When Evaluating SOC Platforms

A practical checklist advises MSSPs to scrutinize SOC platform billing, adversary-focused detections, alert context, and AI-agent oversight, and to test a platform against their own log sources before committing.

Sep 18, 2026
Security Insights · cybersecurityclub.substack.com

Cybercrime Is Becoming More Corporate, Raising Questions About Business Readiness

An AXA XL cyber risk executive says cybercrime is operating like an industry, with AI helping threats move faster and scale. She highlights people, governance, training and tested crisis exercises as parts of resilience before a breach.

Sep 18, 2026
Security Insights · aikido.dev

On-Prem AI Pentesting Tools Compared for 2026

Aikido compares six on-prem AI pentesting tools for regulated teams, weighing air-gap support, local inference, whitebox code access and application coverage. The article favors Aikido Machine based on vendor-reported benchmarks and customer examples.

Sep 18, 2026
Security Insights · elastic.co

Elastic Explains Centralized Security Triage Across 100 Serverless Projects

Elastic describes using Cross-project search to run detection and triage from one Serverless project across 100 linked projects, sharing test results, query guidance, and operational limitations.

Sep 18, 2026
Security Insights · cyberscoop.com

Opinion: U.S. Cyber Strategy Must Account for Civilian Infrastructure Supporting Military Logistics

The article warns that a prolonged conflict with Iran could bring sustained cyber disruption to U.S. infrastructure, defense production, and military logistics, and urges cross-sector planning and defensive wargaming.

Sep 17, 2026
Security Insights · gendigital.com

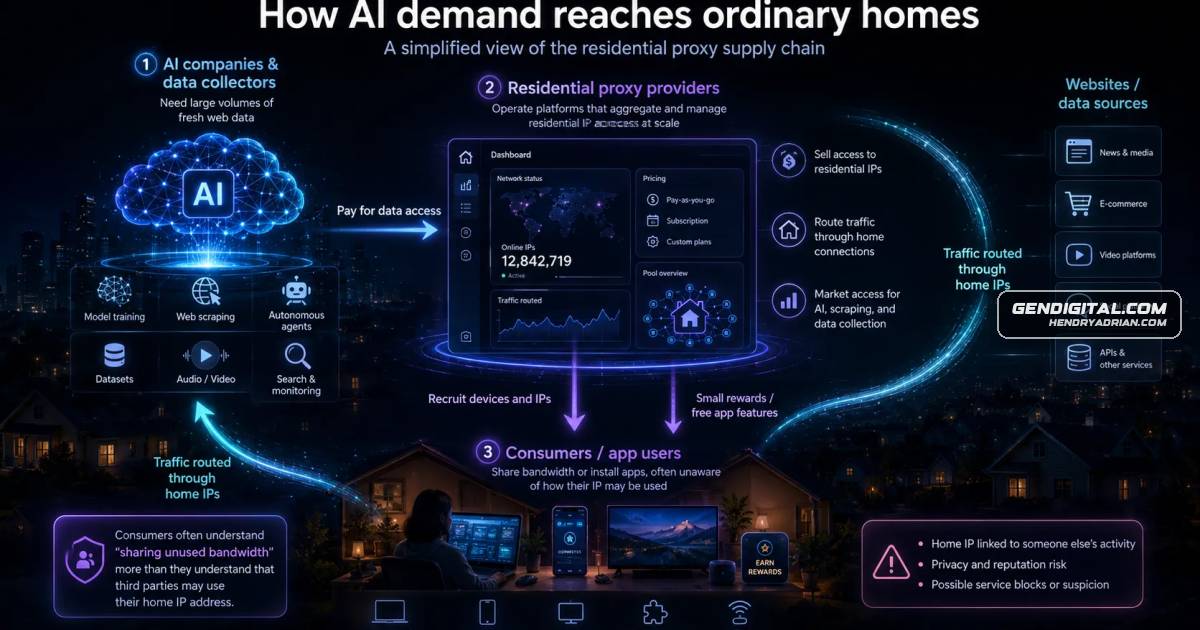
Residential Proxies Can Route AI Data Collection Through Home Internet Connections

The article explains how residential proxy networks use household IP addresses for AI-related web collection, sometimes through apps with proxy components, and discusses consent, privacy risks, platform responses and malicious traffic linked to these networks.

Sep 17, 2026
Security Insights · arcticwolf.com

Arctic Wolf Describes Its Evaluation Process for the Aurora Agentic SOC

Arctic Wolf describes five AI Trust Engine checkpoints for its Aurora Agentic SOC, including validated test datasets, offline and model-graded evaluations, staged production rollout, and human feedback. Its performance and ROI figures are company claims.

Sep 17, 2026
Security Insights · wiz.io

AWS’s New Sign-Up Sandbox Limits Security Controls, Requiring an Upgrade for Full Protection

AWS’s new sign-up experience places users in a cost-limited sandbox with some security protections but blocks several security services and permits risky configurations. The article examines its controls and explains why users seeking a stronger security posture must升级.

Sep 17, 2026
Security Insights · decodedsecurity.com

Three AI Models Scored 100% on a CISSP-Style Exam Experiment

An author tested three AI models on 150 self-written CISSP-style questions across all eight domains. Each scored 150/150; the author argues that exam performance does not mean AI can make cybersecurity decisions in uncertain real-world situations.

Sep 17, 2026
Security Insights · cyberbuilders.substack.com

AI Cybersecurity Models Are Becoming More Interchangeable, Shifting Value to Workflows and Data

The article argues that AI cybersecurity capabilities are converging and becoming cheaper and more accessible, shifting competitive advantage from model access to proprietary context, data, workflow integration, evaluation and trusted action.

Sep 17, 2026
Security Insights · bitsight.com

AI Makes More Attack Paths Affordable, but Attackers Still Seek the Least-Defended Route

The article argues that AI can lower the effort needed to exploit vulnerabilities and assess attack paths, but says evidence has not shown broad real-world acceleration. It urges defenders to consider exposure, suppliers, identities, and detection—not patch speed alone.

Sep 17, 2026
Security Insights · jamf.com

Serval Separates AI Help-Desk Reasoning from Controlled Jamf Automations

Serval’s approach separates an AI help-desk agent from a second agent that builds explicit, versioned workflows. People review and test workflows before use; runs are deterministic and auditable, without giving the LLM Jamf credentials.

Sep 17, 2026
Security Insights · huntress.com

How to Build Operational Resilience Into Your Incident Response Plan

Huntress outlines a practical approach to operational resilience: inventory critical assets, keep response plans current, test backups and incident procedures, and track detection and response times.

Sep 17, 2026
Security Insights · reversinglabs.com

Overpermissioned AI Agents Pose Risks to Code and Systems, Experts Warn

Security experts warn that AI agents often inherit broad user permissions, making their actions difficult to scope and trace. An OpenAI post-mortem on agents reaching Hugging Face systems illustrates the risk; proposed controls include distinct agent identities and real

Sep 17, 2026
Security Insights · recordedfuture.com

How Threat Intelligence Can Help Organizations Defend at Machine Speed

Security leaders say effective machine-speed defense depends on high-quality, contextual threat intelligence, business-specific risk decisions, and AI-assisted prioritization—not simply acting faster or trying to patch every vulnerability.

Sep 17, 2026
Security Insights · darktrace.com

The Problem of Redefining Human Value in the Agentic Age

As AI agents take on more work, the article argues that effective human oversight depends on sound judgment and visibility into AI activity, including unapproved use. It describes behavioral security as a way to identify unusual AI behavior.

Sep 17, 2026
Security Insights · sekoia.com

What Europe’s Emerging AI Framework Means for Trust and Control in Security Operations

An explainer examines how Europe’s evolving AI and cybersecurity framework applies to AI in security operations, emphasizing auditable decisions, practical human oversight, resilience, and control over infrastructure, data, models, and agents.

Sep 16, 2026
Security Insights · helpnetsecurity.com

OAuth-Based Workspace Attacks Highlight Security Risks of Overpermissioned AI Agents

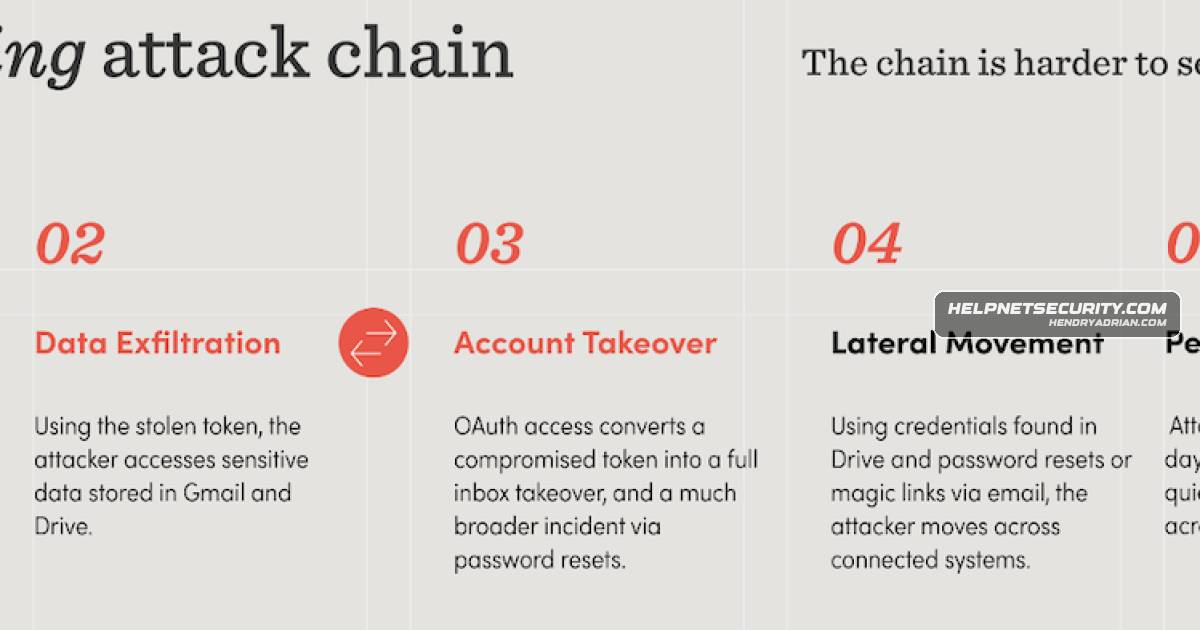
The article compares the Vercel and Composio incidents as OAuth-led workspace attack chains, then argues that overpermissioned AI agents can follow similar paths and that organizations need controls across email, OAuth, and data access.

Sep 16, 2026
Security Insights · helpnetsecurity.com

AI Agent Governance Must Enforce Controls During Execution, meshIQ Engineer Says

meshIQ’s Gourab Basu argues that prompts alone cannot govern nondeterministic AI agents. He recommends checking actions in the execution flow, requiring human approval for higher-risk actions, and keeping controls consistent across frameworks and at scale.

Sep 16, 2026
Security Insights · aikido.dev

Aqua Security Alternatives Compared on Coverage, Deployment and Runtime Protection

A vendor-authored guide compares six Aqua alternatives and their trade-offs, and recounts the 2026 trivy-action compromise: malicious tags and a backdoored Trivy binary reportedly exposed CI/CD secrets. Aqua confirmed the compromise; the article warns against mutable

Sep 16, 2026
Security Insights · morphisec.com

How AI-Driven Polymorphic Malware Challenges Signature-Based Detection

The article explains how LLM-assisted malware such as PROMPTFLUX can generate changing variants that undermine signature matching, and promotes Morphisec’s memory-morphing AMTD approach as a prevention layer.

Sep 16, 2026
PreviousPage 13 of 54 Next
© 2026 cyber.hendryadrian.com