cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

624 articles

Detection & Defense · huntress.com

Least-Privilege Practices Can Reduce the Impact of Compromised Accounts

Huntress recommends reducing unnecessary admin access, separating admin accounts from everyday email and browsing, reviewing sensitive-data permissions, and making access reviews part of routine processes to limit the impact of compromised credentials.

Sep 28, 2026
Detection & Defense · darkreading.com

Treat AI Agents as Privileged Users and Audit Their Access, Opinion Says

The article warns that AI agents using overprivileged service accounts and long-lived tokens can bypass human access controls and cause operational or data-impacting failures. It recommends isolated identities, least privilege, logging, regular reviews, and rapid-cont

Sep 28, 2026
Detection & Defense · darkreading.com

How HR Teams Can Spot and Stop North Korean IT Worker Scams

North Korean operatives are using fake remote-work applications to earn income and gain access to companies. The article outlines warning signs and recommends training recruiters and improving screening and escalation processes.

Sep 25, 2026
Detection & Defense · darkreading.com

AI Agent Sandbox Incidents Highlight the Need for Forensic Readiness

Commentary argues that AI-agent sandbox escapes are better understood as access-control or containment failures than rogue behavior. It urges organizations to preserve trustworthy, comprehensive records so agent activity can be reconstructed and verified.

Sep 25, 2026
Detection & Defense · picussecurity.com

Webinar Shows How to Validate Defenses Against AI-Accelerated Exploits

Picus Security’s on-demand webinar demonstrates continuous, signal-driven validation to prioritize exploitable vulnerabilities and assess whether security controls can block a newly disclosed CVE.

Sep 24, 2026
Detection & Defense · wazuh.com

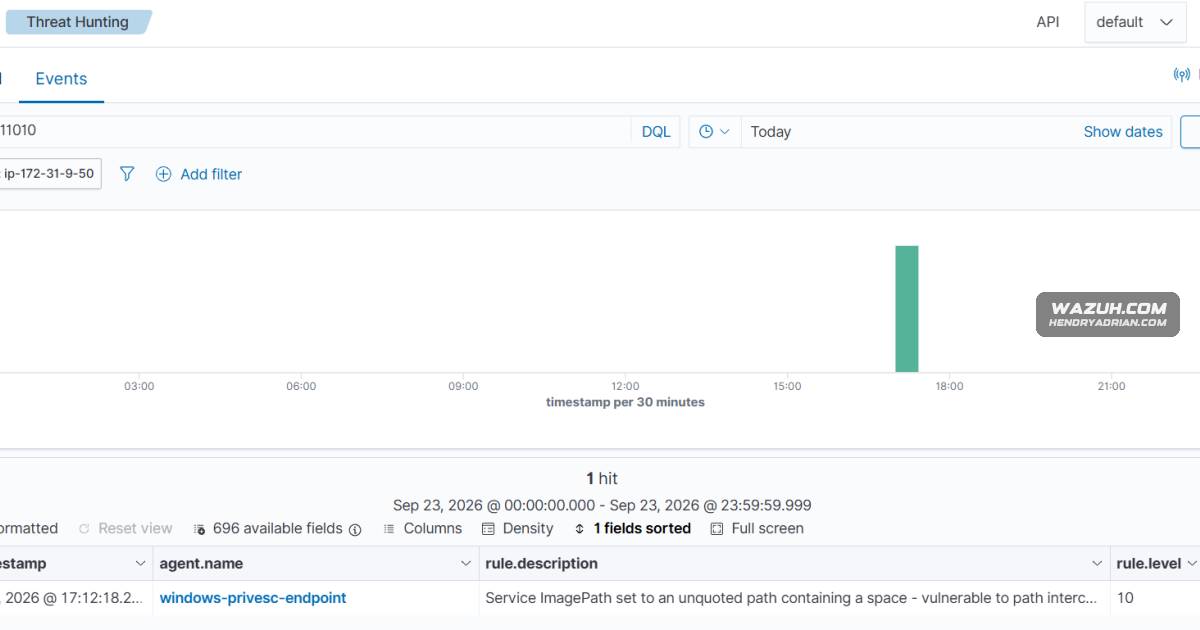
Wazuh Demonstrates Detection of Common Windows Privilege Escalation Techniques

Wazuh demonstrates Sysmon-based detections for Windows privilege escalation risks, including weak service permissions, unquoted service paths, AlwaysInstallElevated, DLL staging, and SYSTEM-level execution from non-standard directories.

Sep 24, 2026
Detection & Defense · levelblue.com

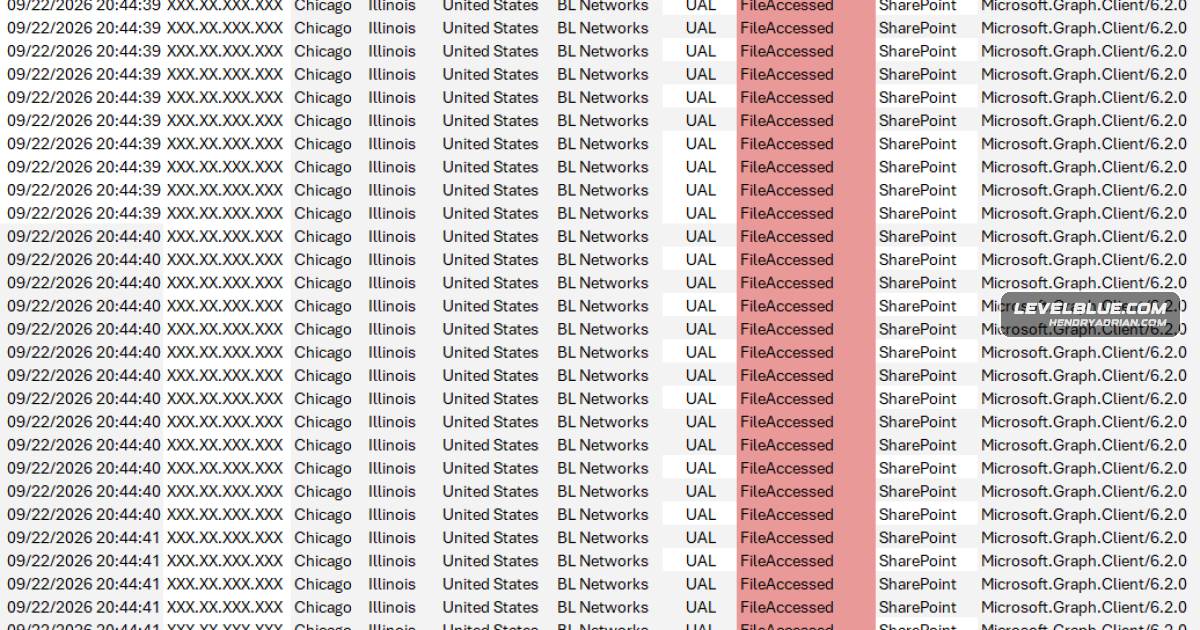
Microsoft 365 File Retrieval May Appear as “FileAccessed,” Not “FileDownloaded”

Controlled testing found that file content retrieved from Microsoft 365 can generate a “FileAccessed” audit event without “FileDownloaded.” Investigators should assess access methods and surrounding evidence before ruling out acquisition.

Sep 24, 2026
Detection & Defense · cisa.gov

FBI and CISA Urge Critical Infrastructure Operators to Secure Third-Party ICS Access

FBI and CISA guidance recommends least privilege, secure contracts, monitored remote access and recovery planning for third-party ICS integrators, citing a 2025 intrusion in which actors staged customer-related files for presumed exfiltration.

Sep 24, 2026
Detection & Defense · cloud.google.com

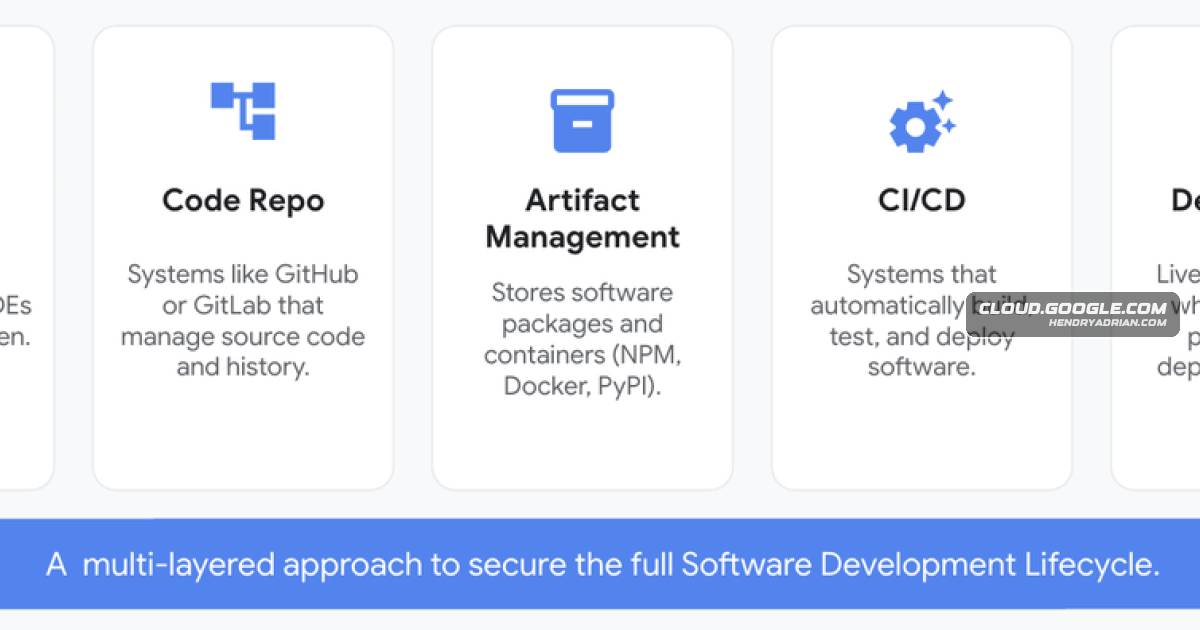
Google Cloud and Mandiant outline safeguards for hardening CI/CD pipelines

Google Cloud and Mandiant provide a defense-in-depth blueprint for securing developer endpoints, code repositories, artifacts, CI/CD pipelines, and production deployments against software supply chain threats.

Sep 24, 2026
Detection & Defense · ic3.gov

FBI and CISA Urge Critical Infrastructure Operators to Secure Third-Party ICS Access

An FBI and CISA fact sheet advises critical infrastructure operators on assessing and reducing risks from third-party ICS integrators, citing a 2025 intrusion at an industrial automation company where actors prepared about 800 files for presumed exfiltration.

Sep 23, 2026
Detection & Defense · bleepingcomputer.com

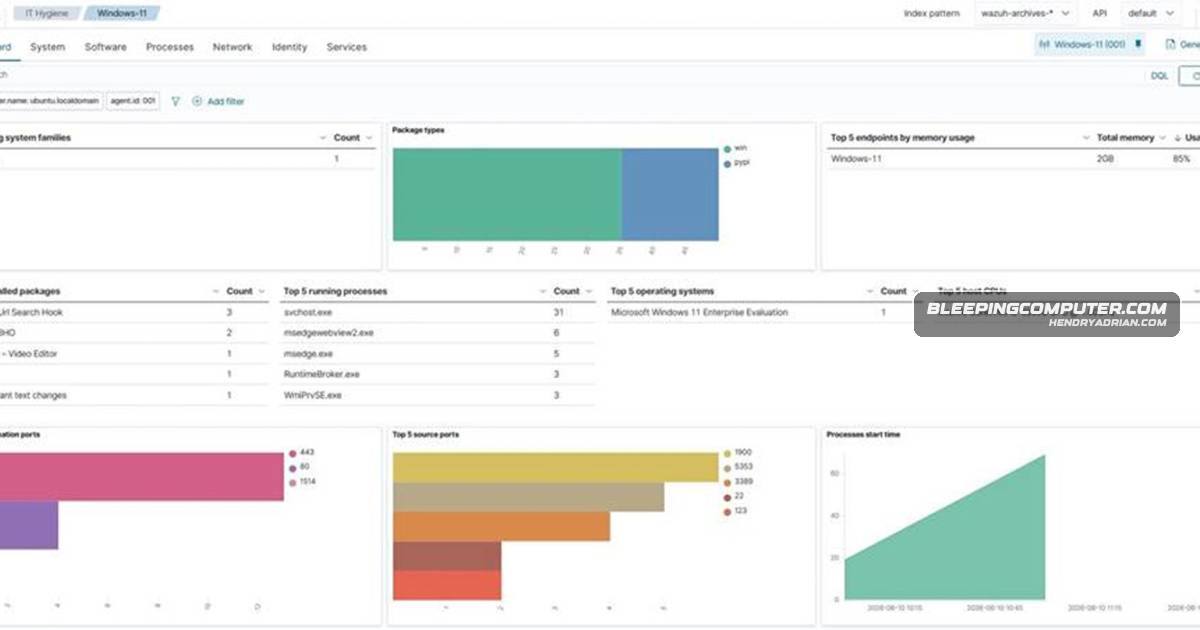
Wazuh Shows How Endpoint Inventory Can Reveal Shadow IT Gaps

A sponsored Wazuh article explains how endpoint inventory, agentless monitoring, and enrollment status can help security teams find unmanaged devices, unauthorized software, and gaps that network scans may miss.

Sep 22, 2026
Detection & Defense · elastic.co

Elastic Outlines a Plan-First Method for Cloud Threat Emulation

Elastic outlines a cloud threat-emulation lifecycle: define scope, model the threat and victim environment, execute with realistic identities, verify real telemetry and detection coverage, document findings, and clean up resources.

Sep 22, 2026
Detection & Defense · cyber.gov.au

North Korean WaterPlum Uses Fake Job Offers to Target IT Professionals

A joint agency advisory says WaterPlum, also known as Contagious Interview, uses fake recruiting and coding tests to infect IT professionals and steal credentials and cryptocurrency. It details the activity, a Japanese hiring case and defenses.

Sep 22, 2026
Detection & Defense · abstract.security

How Threat Modeling and In-Stream Detection Can Make SIEM Monitoring More Cost-Effective

The article recommends using organizational threat models to prioritize SIEM detections and data collection, and compares running detections in SIEMs, security tools, or data pipelines to balance cost, response speed, visibility, and analyst workflow.

Sep 22, 2026
Detection & Defense · aws.amazon.com

AWS Shows How to Normalize Bedrock Guardrail Events for SOC Analysis

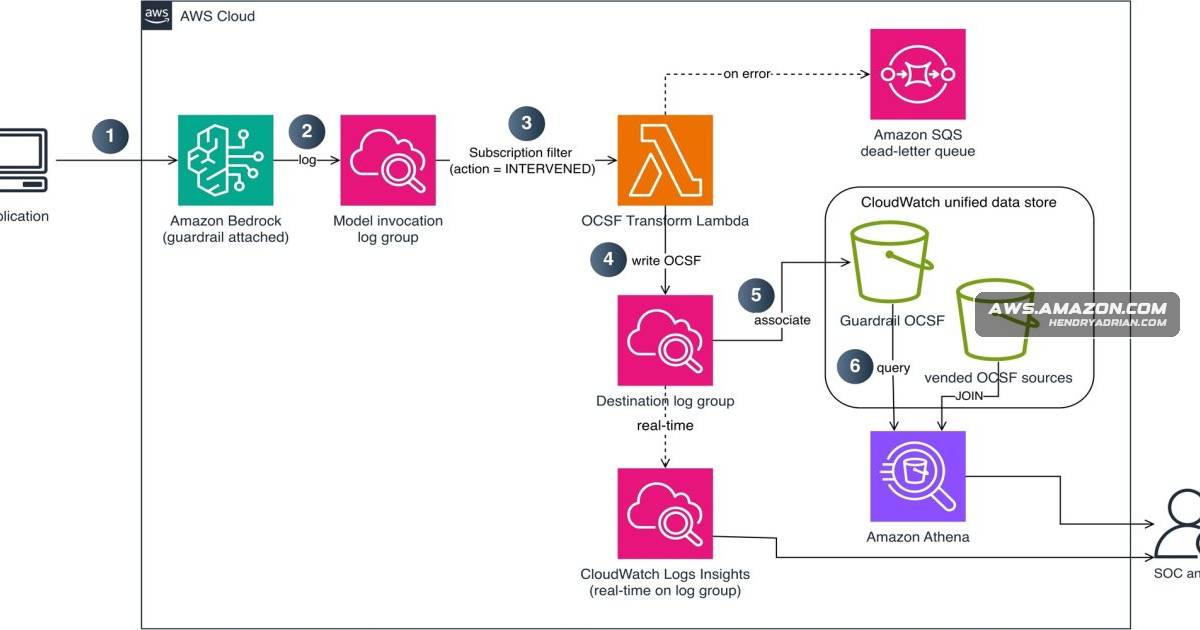
AWS details a pipeline that converts Amazon Bedrock Guardrails interventions into OCSF Detection Finding records in CloudWatch’s unified data store, enabling Athena correlation with CloudTrail and VPC Flow Logs and real-time queries in Logs Insights.

Sep 21, 2026
Detection & Defense · forcepoint.com

OWASP Flags Unbounded AI Inference as a Runaway-Cost Risk

The article explains OWASP’s LLM06:2026 Unbounded Consumption risk, how agents can drive runaway inference costs, and why enforced budgets, circuit breakers, and monitoring are needed.

Sep 21, 2026
Detection & Defense · unit42.paloaltonetworks.com

Unit 42 Urges SOCs to Correlate Activity Across Attack Surfaces

Unit 42 says attacks often span multiple environments, creating visibility gaps when security tools operate separately. It recommends cross-domain correlation, threat hunting, and continual improvement of SOC detections and response workflows.

Sep 17, 2026
Detection & Defense · wiz.io

Wiz Details AI-Agent Detection Pipeline Using Model Logs and Runtime Telemetry

Wiz describes a detection pipeline that analyzes AI-agent input and output logs, then correlates findings with cloud and runtime activity to identify malicious behavior. Bedrock invocation-log support is in private preview for Wiz Defend customers.

Sep 17, 2026
Detection & Defense · wazuh.com

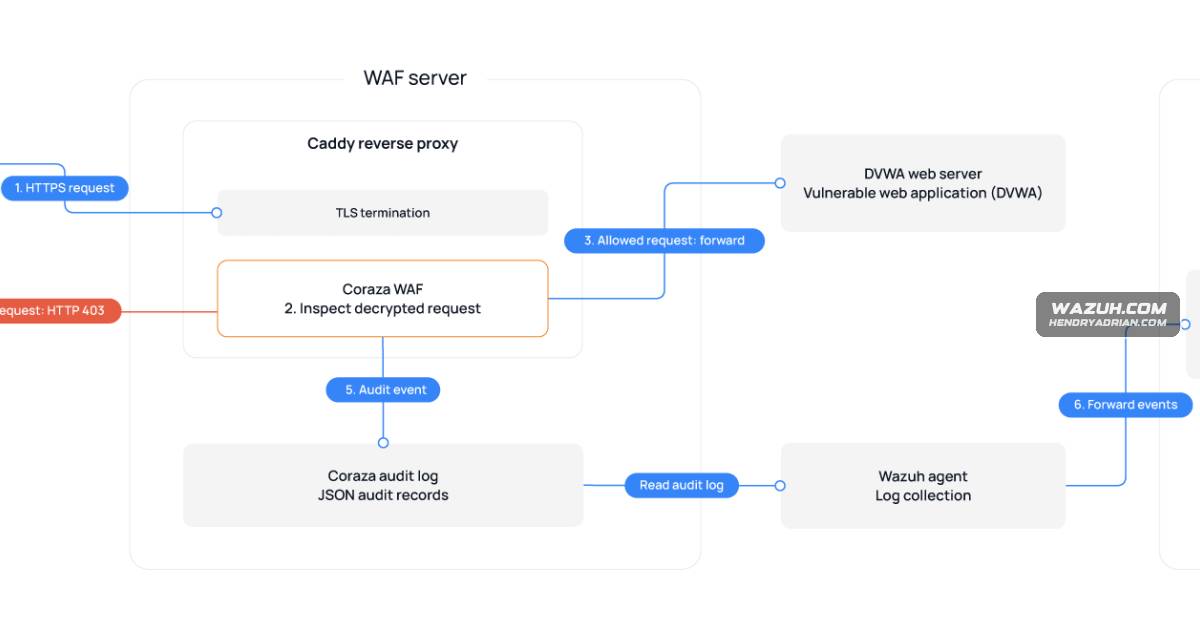
Wazuh Tutorial Shows How to Monitor Coraza WAF Events and Detect Web Attacks

The tutorial configures Caddy with Coraza and Wazuh to inspect web requests, collect WAF audit logs, detect common attacks and repeated activity, and monitor WAF configuration changes.

Sep 17, 2026
Detection & Defense · securityweek.com

CISA Guidance Outlines How to Deploy Cyber Decoys in Critical Infrastructure

CISA released guidance for critical infrastructure organizations on using cyber decoys to detect and observe adversaries, collect threat intelligence, and strengthen detection and response through a three-phase deployment process.

Sep 17, 2026
Detection & Defense · jamf.com

How to Build a Security Control Plane to Contain Enterprise AI Agents

The article outlines layered controls for enterprise AI agents, including capability inventories, isolated execution, network restrictions, and ongoing governance. It stresses that sandboxing alone cannot constrain actions taken with authorized credentials and APIs.

Sep 17, 2026
Detection & Defense · bitsight.com

How Bitsight Uses AI to Speed Internet-Wide Vulnerability Exposure Discovery

Bitsight describes using AI-assisted product fingerprinting, internet-wide scans, and asset mapping to identify likely vulnerability exposure, then applying scans and exploitation forecasts to help defenders prioritize investigation and patching.

Sep 16, 2026
Detection & Defense · securitylabs.datadoghq.com

Datadog Guide Shows How to Hunt for Threats in GitHub Audit Logs

Datadog shares GitHub audit-log queries and investigation guidance to help identify compromised accounts and tokens, secret enumeration, private repository discovery, and bulk source-code collection.

Sep 16, 2026
Detection & Defense · bleepingcomputer.com

Safer Patch Automation Uses Staged Rollouts and Stop Criteria

Sponsored guidance recommends staged patch rollouts, predefined success and stop criteria, and human oversight for critical systems to help organizations patch faster without spreading faulty updates across their environments.

Sep 14, 2026
PreviousPage 10 of 26 Next
© 2026 cyber.hendryadrian.com