Wazuh Tutorial Shows How to Monitor Coraza WAF Events and Detect Web Attacks
Summary
The tutorial configures Caddy with Coraza and Wazuh to inspect web requests, collect WAF audit logs, detect common attacks and repeated activity, and monitor WAF configuration changes.
Key points
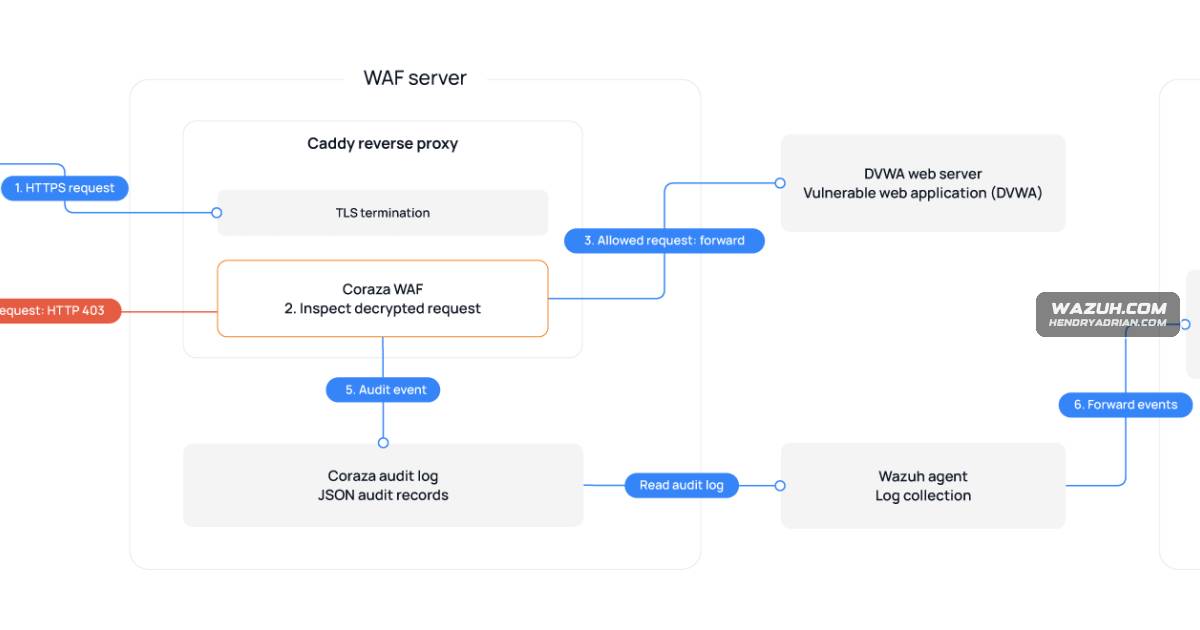
- The demonstration places Coraza with the OWASP Core Rule Set in Caddy, inspecting HTTPS requests before they reach a DVWA web server.
- Coraza audit logs are forwarded to Wazuh for centralized analysis; Wazuh also monitors /etc/caddy for configuration changes.
- Custom rules detect SQL injection, cross-site scripting, path traversal or local file inclusion, and command injection attempts.
- A correlation rule alerts on repeated attack detections from the same source within a short period.
- The tutorial simulates attack requests and WAF configuration changes, then shows how to review resulting alerts in the Wazuh dashboard.
Article Details
- Defense Focus
- Block malicious web requests before they reach backend applications and centrally detect web attacks, repeated suspicious requests, and WAF configuration changes.
- Detection Methods
- Inspect decrypted HTTPS requests before reverse proxying them to the backend; evaluate OWASP CRS matches and interrupt transactions that reach the configured anomaly-score threshold.
- Parse JSON WAF audit records and match attack-sqli, attack-xss, attack-lfi, and attack-rce tags in the messages field to detect SQL injection, cross-site scripting, path traversal or local file inclusion, and remote command execution attempts.
- Include transaction.request.uri, transaction.client_ip, and transaction.is_interrupted in attack alerts to identify the requested resource, source address, and blocking outcome.
- Correlate six web_attack alerts sharing transaction.client_ip within 60 seconds to flag repeated activity consistent with automated attack tooling.
- Use real-time file integrity monitoring to detect file additions, modifications, and deletions under /etc/caddy.
- Filter dashboard events with rule.groups:coraza and inspect decoded event fields to investigate generated alerts.
- Data Sources
- JSON WAF audit events from /var/log/coraza/audit.json, including transaction details and matched-rule messages.
- File integrity monitoring events and reported content changes for /etc/caddy.
- Rule Types
- Custom XML detection rules using JSON decoding, parent-rule relationships, PCRE2 field matching, and alert groups.
- Frequency and timeframe correlation rules keyed on transaction.client_ip.
- File integrity monitoring rules matching configuration paths and file addition, modification, or deletion events.
- SecLang configuration directives and OWASP CRS inspection rules.
- Dashboard event-filter query using rule.groups:coraza.
- Defensive Actions
- Place WAF inspection before backend forwarding and enable blocking with SecRuleEngine On.
- Enable relevant-transaction JSON audit logging and configure the endpoint agent to collect /var/log/coraza/audit.json.
- Enable real-time monitoring with content-change reporting for /etc/caddy.
- Restrict backend HTTP access to the WAF server and deny other connections to port 80.
- Run the reverse proxy as a dedicated service account and restrict configuration-file permissions.
- Rotate audit logs daily and retain a rolling 14-day history.
- Install and reload the custom detection rules, then validate them with controlled injection, traversal, repeated-request, and configuration-change tests.
- Review matching dashboard alerts and decoded transaction fields to investigate suspicious requests and configuration changes.
MITRE ATT&CK
T1189 · Drive-by CompromiseThe article assigns this ID to its cross-site scripting detection rule, tested with a script-bearing request parameter; it does not demonstrate a browser compromise.T1190 · Exploit Public-Facing ApplicationThe article maps rules detecting SQL injection, path traversal or local file inclusion, and remote command execution attempts against the demonstration web application to this ID.T1562.001 · Disable or Modify ToolsThe article maps WAF configuration additions, modifications, and deletions to this ID and explains that an attacker with WAF-server access could weaken the ruleset or disable enforcement; the demonstrated changes are controlled tests.T1595 · Active ScanningThe article maps six web-attack alerts from the same client IP within 60 seconds to this ID, describing the pattern as consistent with automated attack tooling.
Vendors
Products
CaddyWe use Caddy as the reverse proxy and the coraza-caddy module to add Coraza inspection.CorazaCoraza is an open source WAF engine written in Go that provides ModSecurity-compatible rule processing and supports the OWASP CRS.DVWAIn this setup, Caddy runs on the WAF server, Coraza inspects incoming requests before Caddy forwards allowed traffic to the DVWA web server, and Wazuh collects Coraza audit events.UbuntuAn Ubuntu 24.04 endpoint that acts as the WAF server, installed with:WazuhWazuh complements Coraza by collecting and analyzing WAF audit events, correlating them with other security telemetry, and generating events for malicious requests and configuration changes.
Tools
curlAny Linux endpoint with curl installed, acting as the attacker endpoint.Uncomplicated Firewall (UFW)Allow HTTP access only from the WAF server, using the Uncomplicated Firewall (UFW).xcaddyWe use xcaddy to build a custom Caddy binary with the coraza-caddy module, then install it at /usr/local/bin/caddy.