
ConsentFix Uses Familiar Microsoft 365 Sign-In Steps to Steal Session Tokens
Summary
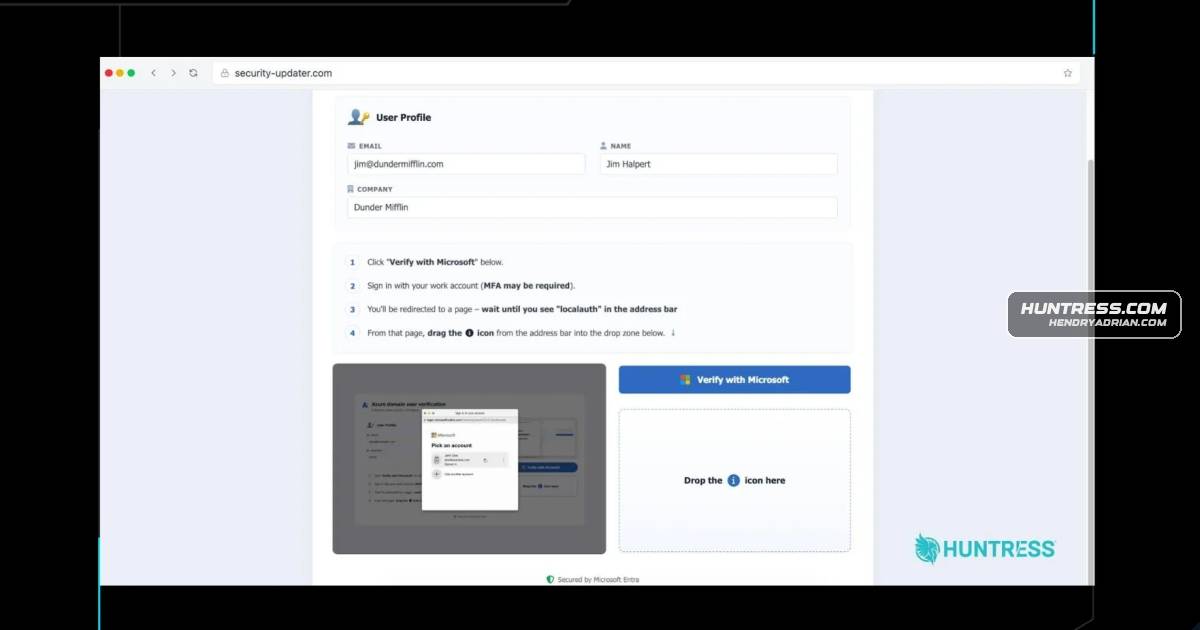
ConsentFix tricks Microsoft 365 users into dragging a localhost callback link into a browser, exposing OAuth tokens that can let attackers access email, OneDrive, Teams, and other resources without a password.
Key points
- ConsentFix uses phishing lures and a lookalike Microsoft sign-in flow to capture OAuth tokens when users drag a localhost callback link into a browser.
- Captured tokens can give attackers access to Microsoft 365 email, OneDrive, Teams, and other resources, bypassing the usual password and MFA steps.
- A public cybercrime forum post in early March 2026 reportedly shared a step-by-step ConsentFix tutorial, working code, infrastructure screenshots, and a video walkthrough.
- The reported infrastructure used services including Cloudflare Pages, workers[.]dev, Pipedream webhooks, Dropbox, and DocSend.
- The article recommends pausing before following prompts to press keyboard shortcuts or drag links, and watching for suspicious PowerShell activity and sign-ins from unusual locations.
Article Details
- Topic
- ConsentFix phishing abuses Microsoft 365 OAuth consent flows to steal session tokens, building on the ClickFix social-engineering technique.