cyber.hendryadrian.com
Login
Navigation
HomeDashboardWeekly Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

YouTube

Curated cybersecurity video content, discussions, interviews, presentations, and educational material from YouTube.

328 articles

YouTube · Jack Rhysider

ThreatLocker Interviews Explore Default-Deny Security and Ransomware Recovery

In a ThreatLocker-sponsored episode, IT practitioners recount ransomware recovery and a hospital intrusion using purchased VPN credentials, illustrating application allowlisting, MFA and the risks of connected networks.
Dec 23, 2025
YouTube · CYBERWOX

Cybersecurity Engineers Assess TikTok Career Advice

Two cybersecurity engineers assess social media career advice, discussing coding requirements, salary expectations, entry-level pathways and hands-on security training.

Dec 19, 2025
YouTube · Hexacon

Apple Details SPTM and MIE Security Advances, Raises Bug Bounty Awards

Apple security engineering chief Ivan Krstić outlined formal verification for cryptography, the SPTM replacement for PPL, and MIE memory protections. He also announced higher Apple Security Bounty awards, including up to $2 million for zero-click exploit chains.

Dec 18, 2025
YouTube · CYBERWOX

TryHackMe Advent of Cyber 2025: Web Attack Forensics with Splunk

Day demonstrates using Splunk and Sysmon in a TryHackMe Advent of Cyber 2025 lab to investigate a simulated web attack, correlate Apache logs and process events, decode Base64 payloads, and identify command execution and whoami reconnaissance.

Dec 15, 2025
YouTube · Loi Liang Yang

AWS Security Hub GA: Features, Pricing, and Setup Walkthrough

A tutorial of AWS Security Hub’s general-availability release covers how it aggregates security findings, correlates exposures, and supports vulnerability and posture management, account coverage, dashboards, automation, integrations, and cross-region aggregation.

Dec 7, 2025
YouTube · Dr Josh Stroschein - The Cyber Yeti

Using Unique Patterns to Find the EIP Offset in a 32-Bit Buffer Overflow

A tutorial demonstrates using a pattern.py script to fuzz a 32-bit program, identify an access violation, find the EIP overwrite offset, and verify the 740-byte offset against the stack layout in IDA.

Dec 4, 2025
YouTube · CYBERWOX

How IT and Help Desk Experience Can Lead to Cybersecurity Roles

Cybersecurity professionals explain how help desk and IT experience can transfer into security roles, highlighting communication, documentation, technical skills, security-focused resumes, hands-on projects, and professional visibility.

Nov 28, 2025
YouTube · Hexacon

Hexacon 2025 Opening: Renaud Feil on AI, Offensive Security and Ethics

Hexacon opening speaker Renaud Feil discusses how AI and automation may change vulnerability research, why practitioners should retain hands-on code-analysis skills, and the ethical responsibilities of offensive security work.

Nov 24, 2025
YouTube · Hexacon

HEXACON Researchers Explain Firefox Promise Exploit Leading to Renderer Code Execution

Tao Yan and Edouard Bochin explain a six-year-old Firefox Promise.allSettled flaw and its exploitation through garbage collection and type confusion. Their Firefox 138 demo disabled the sandbox because the exploit was renderer-only.

Nov 24, 2025
YouTube · Hexacon

Redis Lua Use-After-Free Exploit Enables 0-Click RCE at Pwn2Own

At HEXACON 2025, Benny Isaacs and Neil Braha explain how they exploited a Redis Lua use-after-free for 0-click RCE at Pwn2Own Berlin. Redis had disclosed a patch, and they withheld a PoC while organizations upgrade.

Nov 24, 2025
YouTube · Hexacon

MediaTek Wi-Fi Research Demonstrates Remote Code Execution via Beacon Flaw

A Hexacon talk details reverse engineering of MediaTek Wi-Fi 6/7 firmware and kernel-module flaws, including unauthenticated frame injection and a beacon-triggered buffer overflow demonstrated for remote code execution. The presenter says all discussed issues have been.

Nov 24, 2025
YouTube · Hexacon

Researchers Demonstrate Mac OS Privilege Escalation and Sandbox Escape in CVE-2025-24277

At Hexacon 2025, Csaba Fitzl and Gergely Kalman demonstrated how a race condition in Mac OS OS analytics helperd could enable local privilege escalation and a sandbox escape. Apple patched the issue with entitlement and symlink-handling checks.

Nov 24, 2025
YouTube · Hexacon

Researcher Reports USB and NFC Flaws in Hardware Wallet, Criticizes Bug Bounty Response

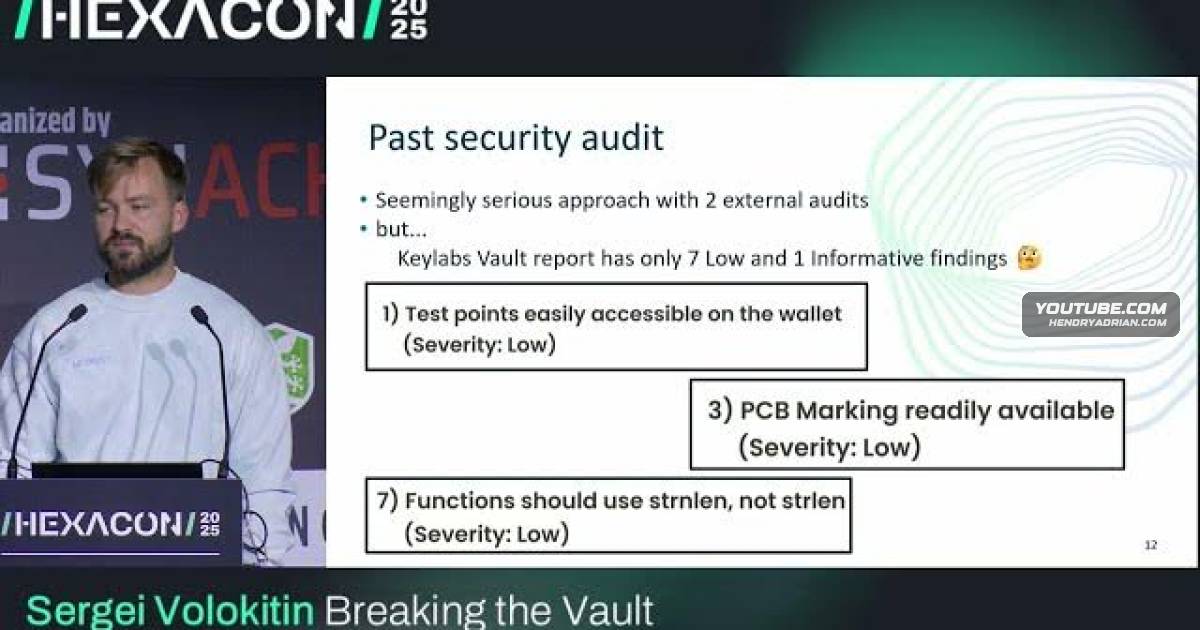
Sergei Volokitin says a USB buffer overflow in a Cyper rock hardware wallet let him extract a PIN and 24-word root seed. He says the vendor fixed the bug two days after his report, but took 186 days to respond; he also found an unchecked NFC APDU overflow.

Nov 24, 2025
YouTube · Hexacon

Linux io_uring Race Enables Kernel Privilege Escalation in kernelCTF Demo

Pumpkin explains a Linux io_uring race in buffer upgrades that can cause a use-after-free and map arbitrary kernel memory, then demonstrates privilege escalation in kernelCTF. The fix allocates a new buffer object instead of reusing one.

Nov 24, 2025
YouTube · Hexacon

Hexacon 2025: Quentin Salingue Explains Apple Secure Enclave Security

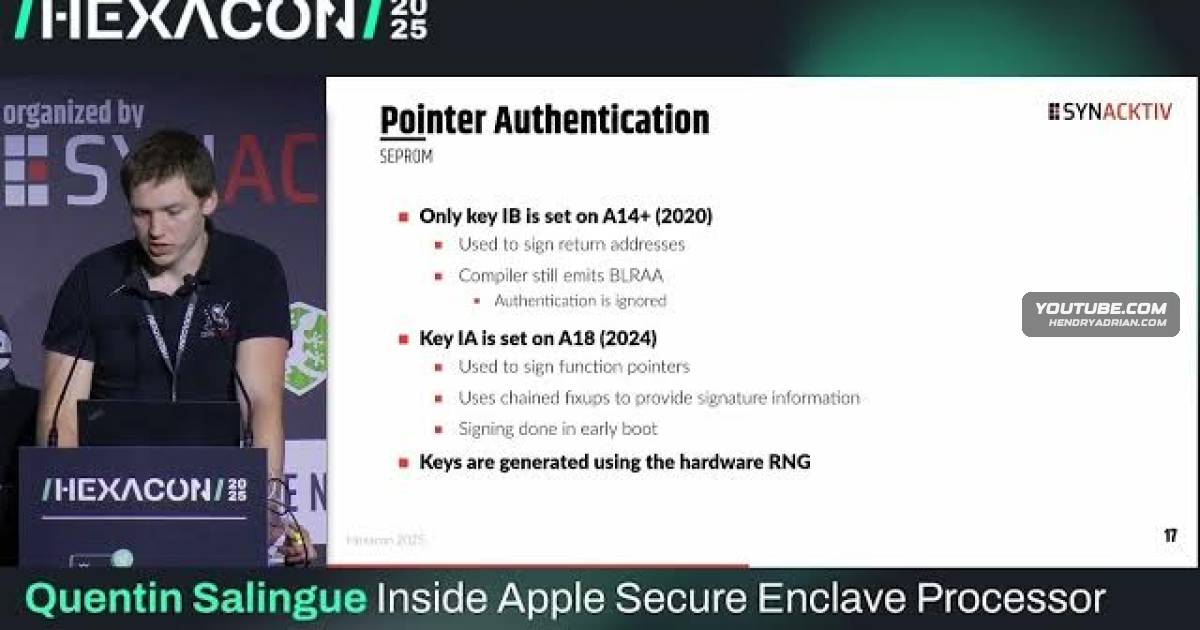
Quentin Salingue’s talk examines Apple Secure Enclave architecture and its protections, including pointer authentication, firmware patching and the trusted boot monitor. He explains how signed firmware and execution checks add layers of defense.

Nov 24, 2025
YouTube · Hexacon

ReVault Research Demonstrates Dell Control Vault Firmware Compromise and Windows Login Bypass

At HEXACON 2025, Philippe Laulheret demonstrated how flaws in Dell Control Vault enable persistent firmware modification, fingerprint login bypass and Windows SYSTEM access through a compromised security chip.

Nov 24, 2025
YouTube · Hexacon

Researchers Detail VirtualBox Guest-to-Host Exploit That Won Pwn2Own 2025

A team describes VirtualBox VGA and network-device flaws used to build a guest-to-host exploit. The speaker reports adapting it for Pwn2Own 2025, where the team won the virtualization category.

Nov 24, 2025
YouTube · Hexacon

Windows SMB Reflection Flaw Can Yield SYSTEM Access; SMB Signing Mitigates Attack

Wilfried Bécard describes NTLM and Kerberos reflection against Windows SMB that can yield SYSTEM-level access when SMB signing is not required. He says Microsoft’s June patch blocks the coercion path and recommends enabling SMB signing.

Nov 24, 2025
YouTube · Hexacon

HEXACON Researchers Demonstrate Linux Kernel Exploitation Through Red-Black Tree Manipulation

William Liu and Savino Dicanosa explain how a Linux traffic scheduler bug becomes a root exploit through red-black tree manipulation, including a variant that bypasses experimental kernelCTF mitigations.

Nov 24, 2025
YouTube · Hexacon

HEXACON Researchers Detail Android Bluetooth Exploit for a Heap Overflow Fixed in 2023

HEXACON speakers described exploiting an Android Bluetooth heap overflow fixed in 2023 to obtain shells without user interaction. Tests on Xiaomi and Samsung devices showed low reliability, with repeated attempts taking roughly two to five minutes.

Nov 24, 2025
YouTube · Hexacon

HEXACON Researchers Demonstrate NVIDIA GPU Driver Exploit Escaping Azure Containers

At HEXACON 2025, IBM X Force researchers demonstrated an NVIDIA GPU driver exploit that escaped a container on Azure serverless GPU compute and obtained a root shell on the host, exposing risks from shared-kernel isolation.

Nov 24, 2025
YouTube · Not the Situation Room

Cloudflare Outage, Holiday Fraud Risks and Wind-Farm Crypto-Mining Case

The hosts discuss Cloudflare’s outage, which the company attributed to a database-permissions change rather than a cyberattack, share holiday fraud precautions, and report a wind-farm manager’s punishment for secretly installing crypto-mining equipment.

Nov 21, 2025
YouTube · CYBERWOX

Cybersecurity Career Lessons on Detection, Threat Intelligence, and Scaling Security

Security engineer Day shares lessons from security work: ship a useful first-pass IOC-based cloud detection during a monitored crypto-mining campaign, refine it later, model cloud threats at scale, prioritize intelligence by organizational impact, and document repeatab

Nov 21, 2025
YouTube · CYBERWOX

Cybersecurity Engineering Archetypes: Skills for Five Roles

The video outlines skills for five cybersecurity engineering archetypes: guardian, architect, mercenary, researcher, and diplomat, from detection and secure design to research and cross-functional communication.

Nov 17, 2025
PreviousPage 12 of 14 Next
© 2026 cyber.hendryadrian.com