
Redis Lua Use-After-Free Exploit Enables 0-Click RCE at Pwn2Own
· 25:14 · Watch on YouTube ↗
Summary
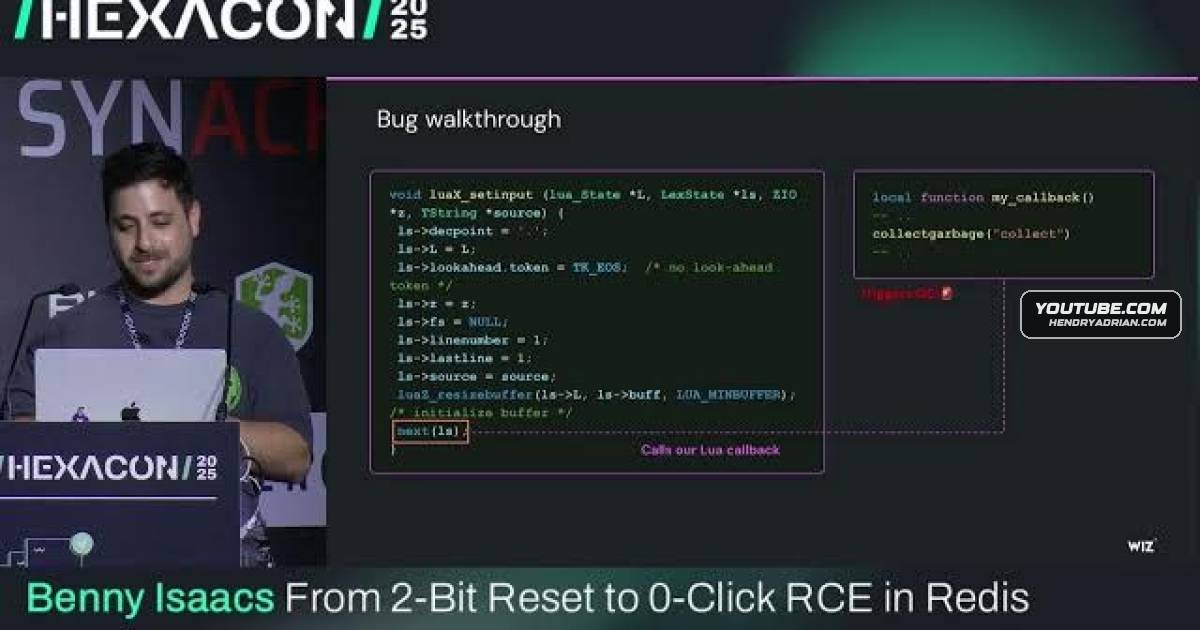
At HEXACON 2025, Benny Isaacs and Neil Braha explain how they exploited a Redis Lua use-after-free for 0-click RCE at Pwn2Own Berlin. Redis had disclosed a patch, and they withheld a PoC while organizations upgrade.
Key points
- Benny Isaacs and Neil Braha said they discovered and exploited the Redis vulnerability during Pwn2Own in Berlin, earning a $40,000 prize.
- The bug involves Lua's load function: garbage collection freed a source string still referenced by lexer state on the native stack, creating a use-after-free.
- The exploit triggered a later garbage-collection mark operation that reset two bits in the freed string's memory.
- Heap shaping let the researchers reclaim that memory with a Lua table, corrupt its node pointer, and create fake Lua objects.
- They described using an address leak and forged objects to perform absolute reads and gather pointers needed to bypass the pointer guard.
- A forged C closure triggered a chain that called system; the live demonstration obtained a remote shell running as the Redis user.
- The speaker said Redis had disclosed a patch and that the researchers withheld a PoC while organizations upgraded.
Article Details
- Topics
- [00:36] Redis vulnerability background and Pwn2Own discovery
- [02:11] Lua's sandbox and the load function callback
- [04:00] Lua garbage collection and the use-after-free
- [13:30] Two-bit memory corruption and heap shaping
- [17:13] Address leakage, fake objects, and absolute reads
- [21:16] Forged C closure and exploit chain to system
- [23:10] Live demonstration of a remote shell
- [24:33] Patch disclosure and withholding a PoC