
ReVault Research Demonstrates Dell Control Vault Firmware Compromise and Windows Login Bypass
· 45:39 · Watch on YouTube ↗
Summary
At HEXACON 2025, Philippe Laulheret demonstrated how flaws in Dell Control Vault enable persistent firmware modification, fingerprint login bypass and Windows SYSTEM access through a compromised security chip.
Key points
- The researcher said the findings affect Control Vault 3 and 3 plus, estimating that tens of millions of laptops contain these devices; suspected exposure in older firmware was not verified on hardware.
- Forged session objects and an arbitrary-free primitive enabled heap manipulation, which was chained with a stack overflow to execute code in the security chip's firmware.
- The demonstration extracted device-specific cryptographic keys and used them to modify protected flash data and install researcher-signed firmware.
- The application firmware lacked a signature check at boot. Demonstrated firmware changes persisted through reboots and would remain after a Windows reinstall.
- Modified fingerprint verification firmware accepted an arbitrary finger stimulus and bypassed the Windows login screen when fingerprint authentication was enabled.
- Malicious firmware responses also enabled exploitation of the Windows biometric service, demonstrated by launching a SYSTEM shell.
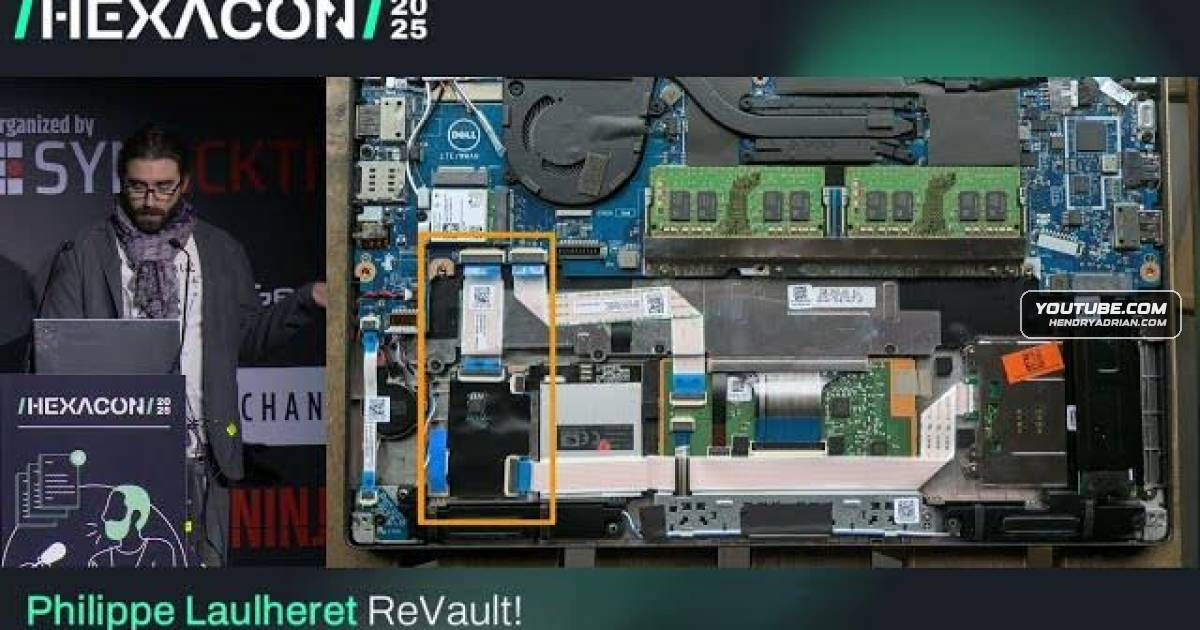
- The talk described both post-compromise and physical-access scenarios, including opening a laptop and connecting directly to the board's internal USB interface.
Article Details
- Topics
- [00:33] Control Vault architecture, affected laptop families and research scope
- [08:27] Firmware, update and Windows attack surfaces and exploitation mitigations
- [11:55] Reverse engineering and decrypting the application firmware
- [15:56] Forged sessions, arbitrary free and chained firmware code execution
- [24:04] Device-key extraction and persistent firmware modification
- [31:04] Bypassing fingerprint authentication with modified firmware
- [32:37] Exploiting host-side response handling and the Windows biometric service
- [43:04] Physical-access attack scenarios and disclosure status
MITRE ATT&CK
T1068 · Exploitation for Privilege EscalationModified firmware supplied crafted responses that exploited the Windows biometric service, demonstrating escalation to a SYSTEM shell.T1542.002 · Component FirmwareThe researcher demonstrated persistent modification of the Control Vault peripheral firmware, which survives reboots and is independent of Windows reinstallation.