
Hexacon 2025: Quentin Salingue Explains Apple Secure Enclave Security
· 22:20 · Watch on YouTube ↗
Summary
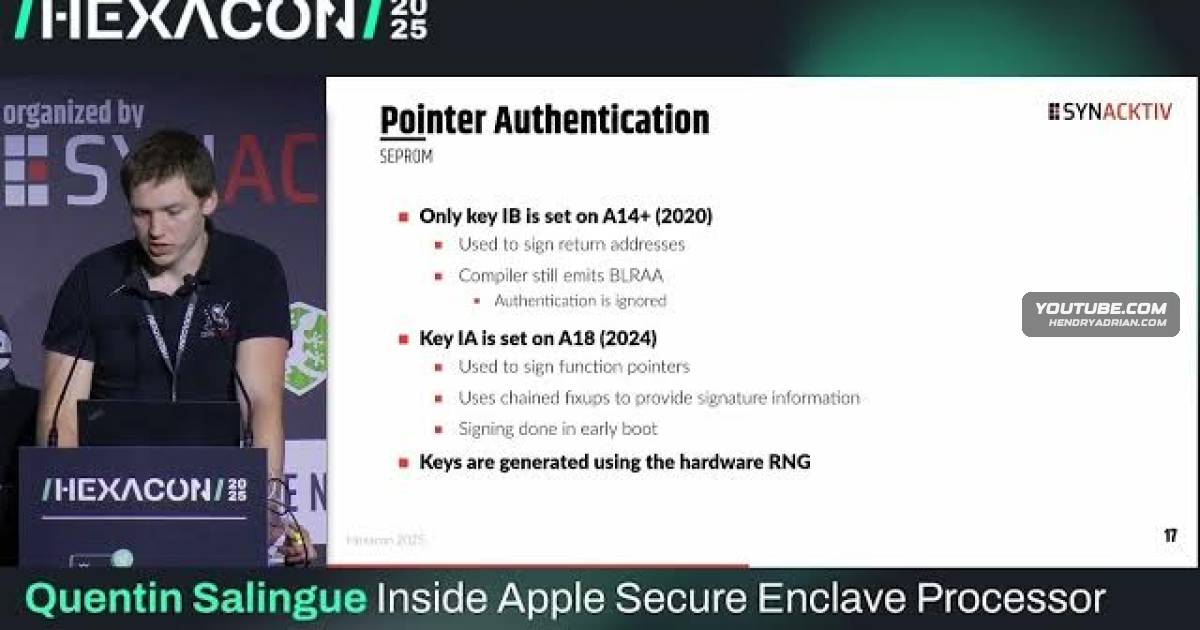
Quentin Salingue’s talk examines Apple Secure Enclave architecture and its protections, including pointer authentication, firmware patching and the trusted boot monitor. He explains how signed firmware and execution checks add layers of defense.
Key points
- The talk outlines the Secure Enclave’s architecture, including its kernel, userland, drivers and interprocess communication.
- The presenter describes a 2020 integer-overflow vulnerability that exposed unprotected memory and enabled arbitrary firmware upload on some iPhones.
- Pointer authentication signs pointers and verifies them before use; the talk describes its use to protect return addresses and function pointers.
- A firmware patch mechanism introduced with the A17 generation can apply patches to otherwise immutable ROM, with updates validated similarly to firmware.
- The trusted boot monitor restricts executable memory ranges, so changing page tables alone cannot make arbitrary code executable.
- The monitor’s newer version checks signed device and firmware properties, including hashes, before allowing patch code to execute.