
CISA Orders Federal Agencies to Patch Actively Exploited FortiClient EMS Flaw by April 9
Summary
CISA ordered federal agencies to patch FortiClient EMS against CVE-2026-35616 by April 9. Fortinet says the flaw is being exploited and released hotfixes for EMS 7.4.5 and 7.4.6.
Key points
- CVE-2026-35616 is a pre-authentication API access-control bypass that could let unauthenticated attackers execute code or commands through crafted requests.
- Fortinet says the vulnerability has been exploited in the wild and released emergency hotfixes for FortiClient EMS 7.4.5 and 7.4.6; it advised upgrading to 7.4.7 when available.
- CISA added the flaw to its Known Exploited Vulnerabilities catalog and ordered FCEB agencies to patch by April 9 under BOD 22-01.
- CISA urged organizations beyond federal agencies to prioritize patching.
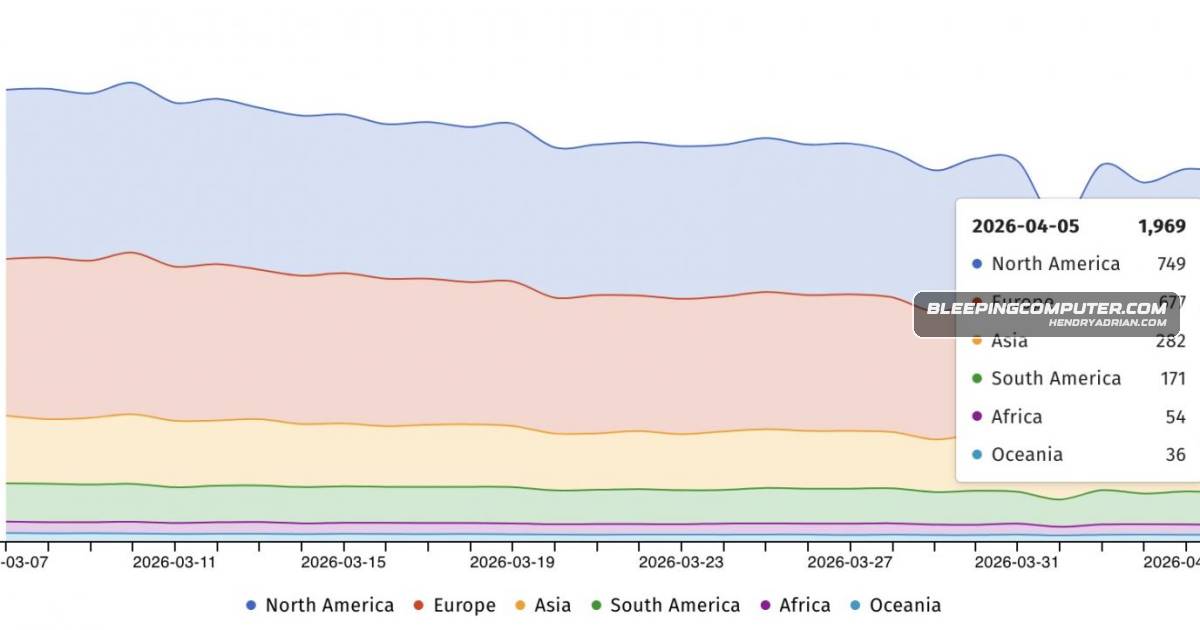
- Shadowserver tracks nearly 2,000 FortiClient EMS instances exposed online, including more than 1,400 IPs in the U.S. and Europe; the article says how many are patched or vulnerable is unknown.
Article Details
- Vulnerability Types
- Pre-authentication API access bypass
- Improper access control
- Affected Versions
- FortiClient EMS 7.4.5
- FortiClient EMS 7.4.6
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Apply the Fortinet hotfix for FortiClient EMS 7.4.5 or 7.4.6, or upgrade to 7.4.7 when available.