cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · bleepingcomputer.com

Cisco patches critical Webex SSO flaw and requires customers to upload a new SAML certificate

Cisco patched four critical flaws, including Webex SSO CVE-2026-20184, which could let unauthenticated attackers impersonate users. SSO customers must upload a new SAML certificate; Cisco reports no evidence of exploitation.
Apr 16, 2026
Vulnerability & Exploit · thehackernews.com

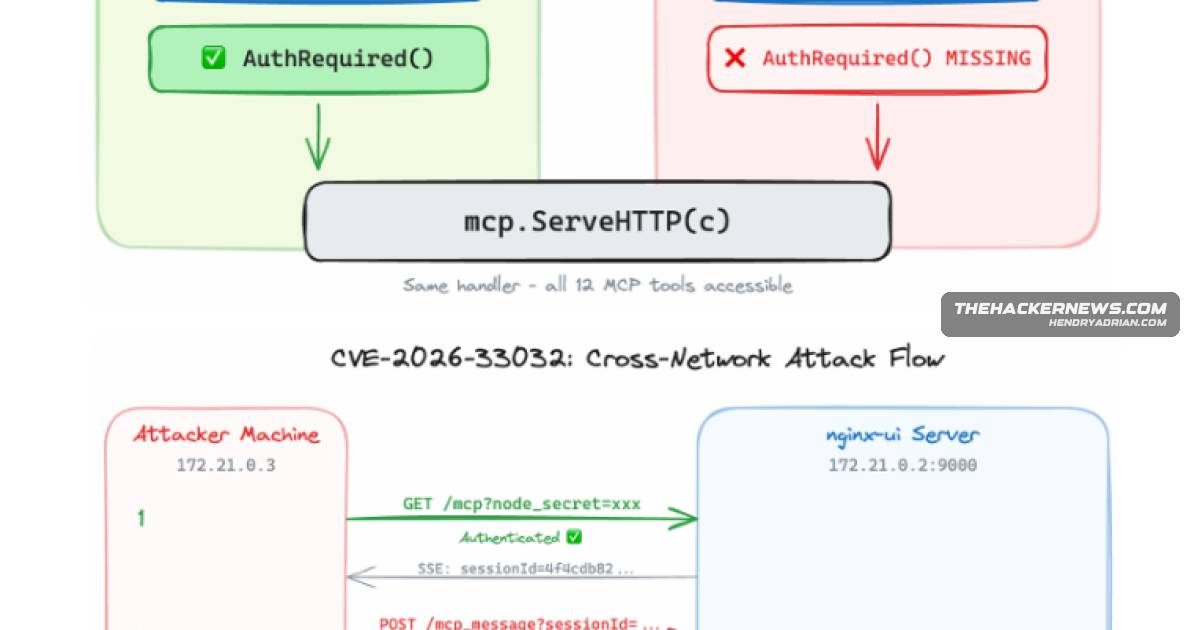
Critical nginx-ui Flaw Enables Unauthenticated Nginx Takeover; Patch Available

CVE-2026-33032 (CVSS 9.8) lets unauthenticated network attackers invoke nginx-ui MCP tools through /mcp_message, potentially altering Nginx configurations. Version 2.3.4 fixes it; Recorded Future listed it among March’s actively exploited flaws, but details were not yet

Apr 16, 2026
Vulnerability & Exploit · bleepingcomputer.com

Actively Exploited nginx-ui Flaw Enables Unauthenticated Server Takeover

CVE-2026-33032 lets unauthenticated attackers invoke nginx-ui MCP tools through /mcp_message to alter and reload Nginx configuration. Active exploitation and public PoCs are reported; users should upgrade to 2.3.6 or apply the fix.

Apr 16, 2026
Vulnerability & Exploit · securityweek.com

Exploited Nginx UI Vulnerability Enables Unauthenticated Server Takeover

CVE-2026-33032 in Nginx UI enables unauthenticated server takeover and was reported exploited in the wild. More than 2,600 exposed instances were found; the flaw is patched in version 2.3.4, but attack details are not public.

Apr 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Adds Windows Task Host Flaw to Actively Exploited Vulnerability Catalog

CISA added CVE-2025-60710, a Windows Task Host link-following flaw enabling local SYSTEM privilege escalation, to its actively exploited catalog and gave FCEB agencies two weeks to remediate. Microsoft patched it in November 2025 but has not confirmed exploitation.

Apr 15, 2026
Vulnerability & Exploit · thecyberexpress.com

Ivanti Neurons ITSM Flaws Could Preserve Sessions and Expose Session Data

Ivanti Neurons for ITSM versions 2025.3 and earlier are affected by flaws that could preserve access after account deactivation or expose limited session data via stored XSS. Ivanti says it has no evidence of exploitation.
Apr 15, 2026
Vulnerability & Exploit · thehackernews.com

Composer Fixes Two Perforce Driver Flaws That Enable Command Execution

Two Composer Perforce VCS driver flaws, CVE-2026-40176 and CVE-2026-40261, could enable arbitrary command execution. Fixed releases are 2.9.6 and 2.2.27; Packagist disabled Perforce source metadata as a precaution.

Apr 14, 2026
Vulnerability & Exploit · thecyberexpress.com

Kali Forms RCE Vulnerability Exploited in Attacks; Patch Available

The Kali Forms WordPress plugin (versions through 2.4.9) was reportedly exploited for unauthenticated RCE via manipulated form placeholders. Version 2.4.10 patches the flaw; security telemetry recorded over 312,200 blocked attempts.

Apr 14, 2026
Vulnerability & Exploit · thehackernews.com

ShowDoc CVE-2025-0520 Flaw Actively Exploited to Deploy Web Shells

VulnCheck reports active exploitation of ShowDoc CVE-2025-0520, an unauthenticated file-upload flaw that enables PHP web-shell deployment and remote code execution. A web shell was observed on a U.S. honeypot; versions before 2.8.7 are affected.

Apr 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

wolfSSL Flaw Could Allow Forged Certificates to Be Accepted

CVE-2026-5194 lets vulnerable wolfSSL builds accept undersized digests during signature verification, potentially allowing forged certificates to be trusted. wolfSSL fixed the flaw in version 5.9.1.

Apr 13, 2026
Vulnerability & Exploit · bleepingcomputer.com

Adobe Patches Acrobat Zero-Day Exploited Through Malicious PDFs

Adobe patched CVE-2026-34621, a zero-day reportedly exploited since at least December. Malicious PDFs can bypass Acrobat’s sandbox and use privileged JavaScript APIs to read and exfiltrate local files; Adobe lists fixed versions.

Apr 13, 2026
Vulnerability & Exploit · thehackernews.com

Adobe Patches Actively Exploited Acrobat Flaw CVE-2026-34621

Adobe patched CVE-2026-34621, a prototype pollution flaw in Acrobat and Acrobat Reader that can enable arbitrary code execution. Adobe acknowledged active exploitation and released fixes for affected Windows and macOS versions.

Apr 13, 2026
Vulnerability & Exploit · bleepingcomputer.com

Critical Marimo RCE Exploited Within 10 Hours of Disclosure

Sysdig reports that attackers exploited Marimo’s unauthenticated CVE-2026-39987 WebSocket flaw within 10 hours of disclosure, accessing credentials. Marimo released version 0.23.0 and recommends restricting access and rotating exposed secrets.

Apr 12, 2026
Vulnerability & Exploit · securityweek.com

Adobe Patches Actively Exploited Acrobat and Reader Zero-Day CVE-2026-34621

Adobe patched CVE-2026-34621, an actively exploited Acrobat and Reader flaw that can enable code execution. Researchers traced exploitation to at least November 2025; Adobe updated the CVSS score from 9.6 to 8.6.

Apr 12, 2026
Vulnerability & Exploit · securityweek.com

Juniper Patches Nearly Three Dozen Junos OS and Other Product Vulnerabilities

Juniper patched nearly three dozen vulnerabilities affecting Junos OS and other products. The flaws include a remotely exploitable default password in the Support Insights Virtual Lightweight Collector; Juniper says it is unaware of in-the-wild exploitation.

Apr 10, 2026
Vulnerability & Exploit · securityweek.com

Nine Orthanc DICOM Vulnerabilities Could Cause Crashes, Data Leaks and RCE

Nine vulnerabilities in Orthanc 1.12.10 and earlier could cause crashes, heap-data leaks, memory exhaustion, and potentially remote code execution. Orthanc 1.12.11 fixes the issues.

Apr 10, 2026
Vulnerability & Exploit · securityweek.com

Marimo CVE-2026-39987 Exploited Less Than 10 Hours After Disclosure

Sysdig says attackers exploited Marimo's unauthenticated CVE-2026-39987 RCE 9 hours 41 minutes after disclosure, using a self-built exploit to access and exfiltrate credential files in a honeypot. Versions through 0.20.4 are affected; update to 0.23.0 or newer.

Apr 10, 2026
Vulnerability & Exploit · thecyberexpress.com

GitLab Patches 12 Vulnerabilities, Including High-Severity WebSocket Flaw

GitLab released CE and EE updates fixing 12 vulnerabilities, including CVE-2026-5173, an authenticated WebSocket access-control bypass. Self-managed users should upgrade to 18.10.3, 18.9.5, or 18.8.9.

Apr 10, 2026
Vulnerability & Exploit · securitylabs.datadoghq.com

CVE-2020-8562 Lets DNS Rebinding Bypass Kubernetes API Server Proxy Filter

CVE-2020-8562 lets attackers with Node-creation and API server proxy permissions use DNS rebinding to bypass Kubernetes proxy IP filtering and reach internal services. Minimum DNS TTLs or Konnectivity can mitigate the risk, especially on managed control planes.

Apr 10, 2026
Vulnerability & Exploit · sysdig.com

Sysdig Observes Marimo RCE Exploitation 9 Hours After Disclosure

Sysdig says attackers exploited marimo’s unauthenticated /terminal/ws endpoint 9h 41m after GHSA-2679-6mx9-h9xc was disclosed. In a honeypot, an operator read a simulated .env file; marimo 0.23.0 fixes the flaw.

Apr 10, 2026
Vulnerability & Exploit · thehackernews.com

EngageLab SDK Flaw Could Expose 50 Million Android App Installations

Microsoft said an intent redirection flaw in EngageLab SDK 4.5.4 could let a malicious app access sensitive data in apps using the SDK. Affected apps had over 50 million installations; version 5.2.1 fixes the flaw, with no known exploitation.

Apr 9, 2026
Vulnerability & Exploit · bleepingcomputer.com

Researchers Say Adobe Reader Zero-Day Has Been Exploited Since December

Researchers report that attackers have used crafted PDFs to exploit an unpatched Adobe Reader flaw since at least December, harvesting local data and potentially deploying RCE/SBX stages. Adobe had not issued a patch; users were advised to avoid untrusted PDFs.

Apr 9, 2026
Vulnerability & Exploit · securityweek.com

Adobe Reader Zero-Day May Have Been Exploited Since November, Researcher Says

Researcher Haifei Li says a PDF exploit detected by Expmon may target a zero-day in the latest Adobe Reader. A sample submitted to VirusTotal in November 2025 suggests exploitation for at least four months; Adobe is assessing the report.

Apr 9, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Exploited Ivanti EPMM Flaw by April 11

CISA added Ivanti EPMM flaw CVE-2026-1340 to its KEV catalog and ordered federal agencies to patch by April 11. The article reports exploitation and nearly 950 exposed EPMM IP addresses, but gives no count of unpatched systems.

Apr 8, 2026
PreviousPage 55 of 65 Next
© 2026 cyber.hendryadrian.com