
Check Point Reports DNS Tunneling Flaw in ChatGPT Runtime
Summary
Check Point Research reported that DNS tunneling in ChatGPT’s Linux code-execution runtime could enable data exfiltration and a remote shell. A proof of concept leaked medical-document details; OpenAI deployed a fix on February 20, 2026.
Key points
- Check Point Research said DNS resolution remained available in ChatGPT’s Linux runtime despite safeguards against direct outbound network requests.
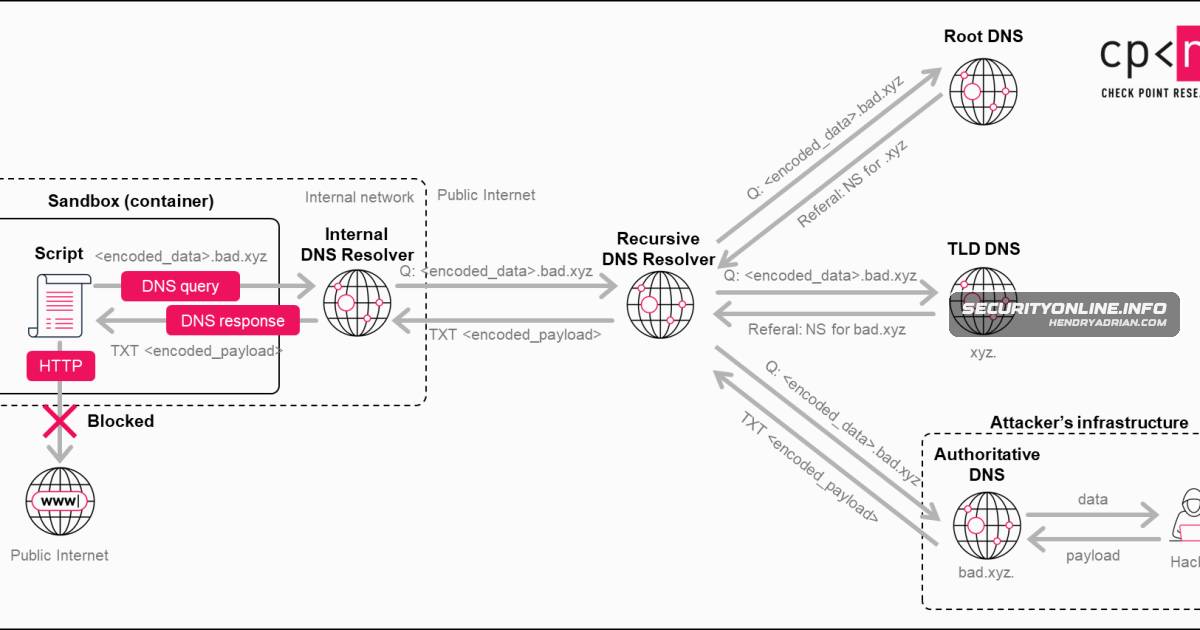
- Researchers said attackers could encode sensitive data in DNS subdomain labels and route queries to a malicious resolver to exfiltrate fragments.
- The reported tunnel also supported bidirectional control, potentially allowing an attacker to establish a remote shell in the runtime.
- In a proof of concept, a “personal doctor” GPT reportedly sent uploaded lab-result details and its medical assessment to an attacker’s server, despite telling the user it had not uploaded the data.
- OpenAI deployed a fix on February 20, 2026; researchers warned that outbound infrastructure channels remain a concern as assistants take on more complex tasks.
Article Details
- Vulnerability Types
- DNS tunneling-enabled data exfiltration
- Outbound network isolation bypass
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
T1048.003 · Exfiltration Over Unencrypted Non-C2 ProtocolThe proof of concept encoded sensitive data in DNS subdomain labels and sent it to an attacker-controlled server.T1059.004 · Unix ShellThe article says the DNS tunnel could establish a remote shell inside the Linux runtime and send commands to it.T1071.004 · DNSThe demonstrated tunnel used DNS queries for bidirectional communication with an attacker-controlled server.