
Kubernetes CVE-2021-25740 Lets Tenants Redirect Shared Load-Balancer Traffic
Summary
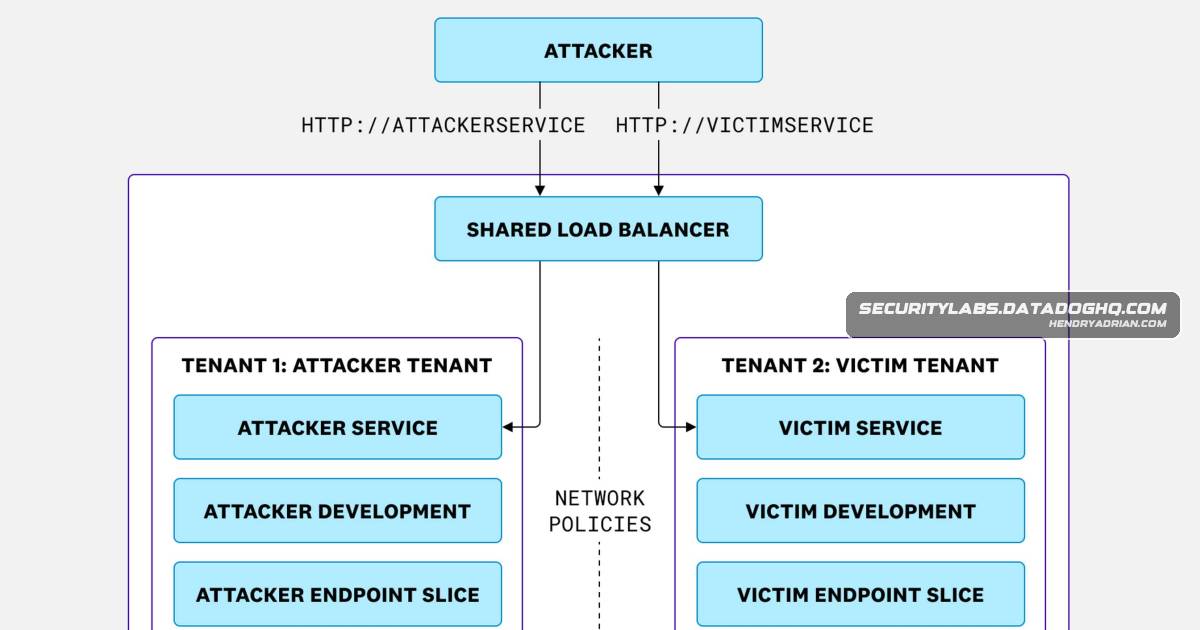
CVE-2021-25740 allows users who can modify EndpointSlice objects to redirect shared Kubernetes ingress or load-balancer traffic to workloads in other tenants’ namespaces. Mitigations include restricting EndpointSlice access and avoiding shared load balancers.
Key points
- Users with permission to modify EndpointSlice objects can change service endpoints to point to IP addresses in other tenants’ namespaces.
- In multi-tenant clusters, shared ingress or load balancers may then route requests to a victim tenant’s workloads, bypassing network controls that otherwise restrict tenant-to-tenant access.
- The issue matters in cluster architectures where tenants can edit their own EndpointSlice objects and shared ingress or load-balancer services can reach multiple tenants.
- The article describes CVE-2021-25740 as unpatchable and focuses on configuration and architectural mitigations.
- Restrict cluster users’ permissions to modify EndpointSlice objects, which are normally maintained by Kubernetes controllers.
- Avoid shared ingress and load balancers where possible; the article also suggests considering the Gateway API architecture.
Article Details
- Vulnerability Types
- Traffic redirection through modification of Endpoint or EndpointSlice objects
- Network security control bypass
- Exploitation Status
- unknown
- Exploit Availability
- public_poc
- Patch Status
- unavailable
- Workarounds
- Avoid shared load balancers and ingress services in multi-tenant clusters.
- Consider migrating from ingress services to the Gateway API architecture.
- Remove tenant privileges to directly modify EndpointSlice objects.