
Ubiquiti Patches Five UniFi OS Flaws, Including Three Maximum-Severity Issues
Summary
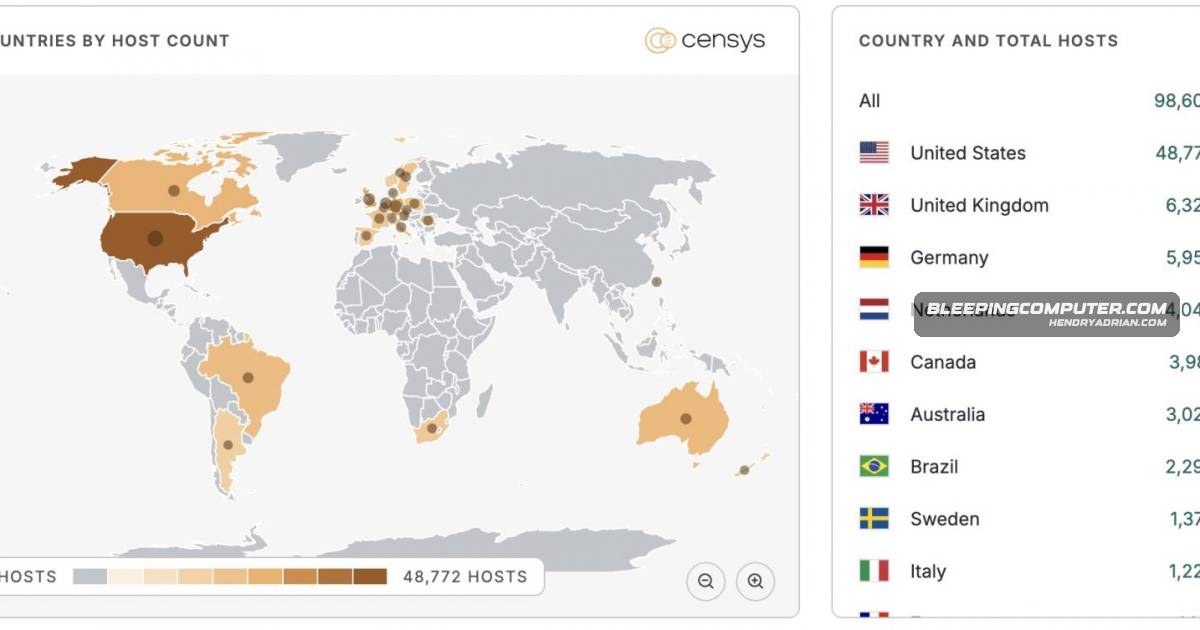
Ubiquiti patched five UniFi OS vulnerabilities, including three maximum-severity flaws involving access control, path traversal and command injection. Censys tracks nearly 100,000 internet-exposed endpoints; in-the-wild exploitation is unknown.
Key points
- CVE-2026-34908 could permit unauthorized changes through improper access control.
- CVE-2026-34909 could allow file access through path traversal.
- CVE-2026-34910 could enable command injection after network access is gained.
- Ubiquiti also patched command injection flaw CVE-2026-33000 and information disclosure flaw CVE-2026-34911.
- The vulnerabilities were reported through Ubiquiti’s HackerOne bug bounty program; the company has not disclosed whether they were exploited in the wild.
- Censys tracks nearly 100,000 internet-exposed UniFi OS endpoints, but the number secured against these flaws is unknown.
Article Details
- Vulnerability Types
- Improper access control
- Path traversal
- Improper input validation
- Command injection
- Information disclosure
- Severity
- Three maximum-severity vulnerabilities, one critical vulnerability, and one high-severity vulnerability
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
CVE-2026-33000Ubiquiti Inc · UniFi OS Server#UniFiOSCVE-2026-34908Ubiquiti Inc · EFG; Ubiquiti Inc · ENVR; +29 more#UniFiOSCVE-2026-34909Ubiquiti Inc · EFG; Ubiquiti Inc · ENVR; +30 more#UniFiOSCVE-2026-34910Ubiquiti Inc · EFG; Ubiquiti Inc · ENVR; +29 more#UniFiOSCVE-2026-34911Ubiquiti Inc · EFG; Ubiquiti Inc · ENVR; +29 more#UniFiOS
Threat Actors
Malware
Vendors
Products
Countries
Russiainstance, in February 2024, the FBI took down Moobot, a botnet of hacked Ubiquiti Edge OS routers used by Russia’s Main Intelligence Directorate of the General Staff (GRU) to proxy malicious traffic in cyberespionageUnited StatesAt the moment, threat intelligence company Censys is tracking nearly 100,000 Internet-exposed UniFi OS endpoints, most of them (nearly 50,000 IP addresses) found in the United States.