
CISA Orders Federal Agencies to Patch Actively Exploited Drupal Flaw
Summary
CISA added Drupal SQL injection CVE-2026-9082 to its Known Exploited Vulnerabilities Catalog and ordered federal agencies to patch. Imperva reported over 15,000 attack attempts across nearly 6,000 sites.
Key points
- CVE-2026-9082 is an unauthenticated SQL injection flaw in Drupal’s database abstraction API affecting PostgreSQL-powered sites.
- Specially crafted requests could lead to information disclosure, privilege escalation, or remote code execution.
- Drupal’s security team released patches and said exploitation attempts had been detected in the wild.
- Imperva reported more than 15,000 attack attempts against nearly 6,000 sites across 65 countries.
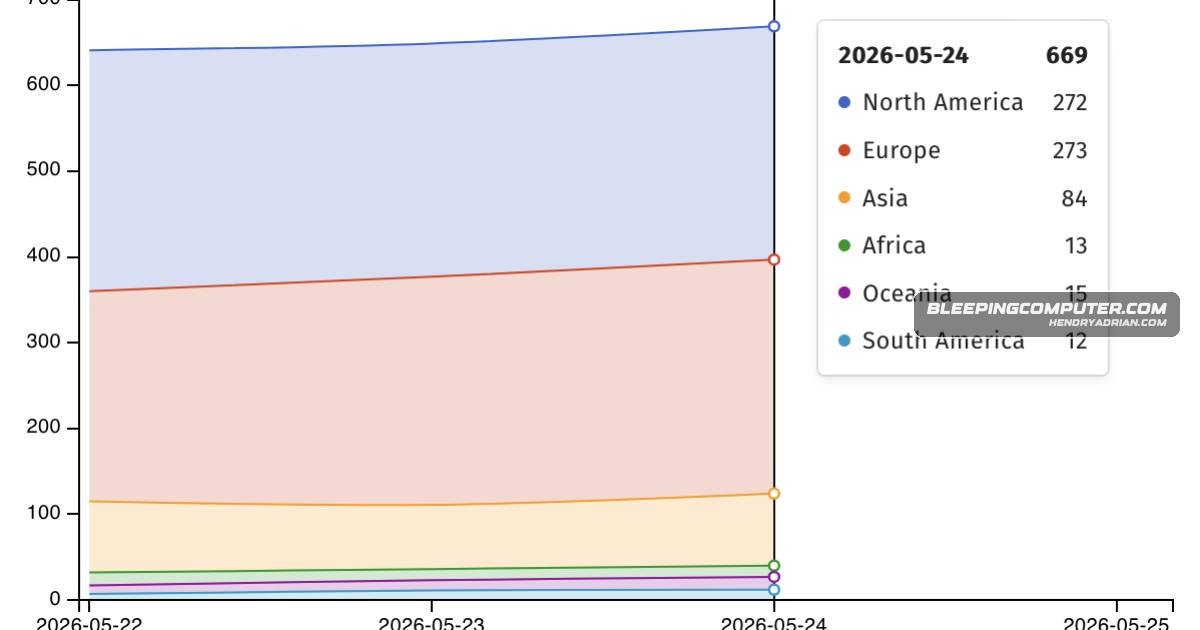
- Shadowserver tracked nearly 670 exposed, unpatched Drupal installations, mostly in North America and Europe.
- CISA added the flaw to its Known Exploited Vulnerabilities Catalog and set a May 27 patch deadline for federal civilian agencies.
- CISA urged other organizations to apply patches promptly.
Article Details
- Vulnerability Types
- Unauthenticated SQL injection
- Severity
- Highly critical (Drupal security team designation)
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Apply mitigations per vendor instructions.
- Discontinue use of the product if mitigations are unavailable.