cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · thehackernews.com

CISA Adds Oracle WebLogic Flaw CVE-2024-21182 to KEV Catalog After Active Exploitation Evidence

CISA added Oracle WebLogic Server flaw CVE-2024-21182 to its KEV Catalog based on evidence of active exploitation. The unauthenticated, network-accessible flaw can expose critical data or server access; FCEB agencies have a June 4, 2026, patch deadline.
Jun 3, 2026
Vulnerability & Exploit · bleepingcomputer.com

Actively Exploited Kirki Flaw Enables WordPress Account Takeovers

Wordfence reports active exploitation of CVE-2026-8206, a Kirki plugin flaw that lets unauthenticated attackers send password reset links to their own email addresses. Versions through 6.0.6 are affected; upgrade to 6.0.7 or disable the plugin.

Jun 2, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited Oracle WebLogic Flaw

CISA added Oracle WebLogic flaw CVE-2024-21182 to its exploited-vulnerabilities catalog and ordered federal agencies to patch by June 4. The flaw affects two versions and can be exploited remotely without authentication.

Jun 2, 2026
Vulnerability & Exploit · securityweek.com

Debug-Mode Flaw in Six Microsoft Android Apps Could Expose Account Tokens

Enclave found a debug-mode flaw in six Microsoft Android apps that could let other apps obtain access tokens. Microsoft confirmed and fixed the flaws, assigning three CVEs; users should update their apps.

Jun 2, 2026
Vulnerability & Exploit · securityweek.com

Google Patches Android Zero-Day and 123 Other Vulnerabilities

Google’s Android update patches 124 vulnerabilities, including CVE-2025-48595, a high-severity Framework privilege-escalation flaw with indications of limited, targeted exploitation. One other patched flaw allows remote code execution.

Jun 2, 2026
Vulnerability & Exploit · securityweek.com

HP Poly VoIP Phone Flaw Enables Root-Level Remote Code Execution

Rapid7 says CVE-2026-0826, a CVSS 9.2 stack overflow in SDP parsing on ICE-enabled HP Poly VoIP phones, can allow root-level RCE via a crafted SIP INVITE. Patches are available; disabling ICE can mitigate.

Jun 2, 2026
Vulnerability & Exploit · cyberscoop.com

Attackers Exploit Palo Alto Networks CVE-2026-0257 to Bypass Firewall Authentication

Rapid7 confirmed active exploitation of CVE-2026-0257, which can let remote attackers bypass authentication on some Palo Alto Networks firewalls. The vendor urged customers to patch or apply mitigations; CISA added the flaw to its KEV catalog.

Jun 1, 2026
Vulnerability & Exploit · securityweek.com

Actively Exploited WP Maps Pro Flaw Enables WordPress Site Takeover

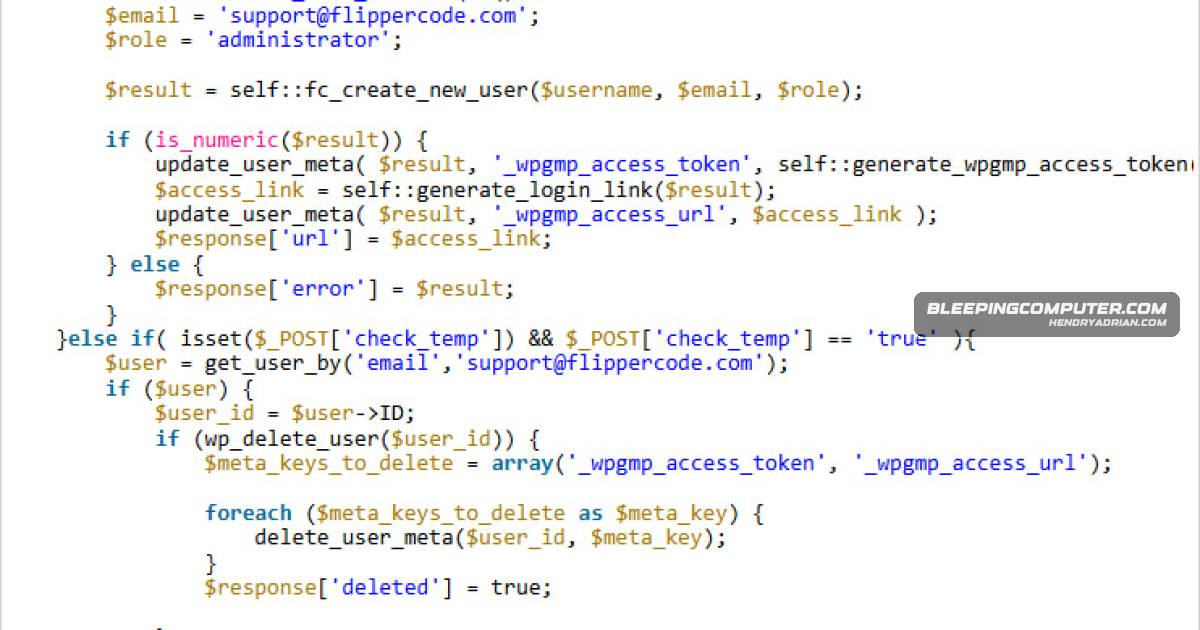
CVE-2026-8732 in WP Maps Pro lets unauthenticated attackers create administrator accounts and take over sites. Defiant says the flaw is being exploited and reports blocking over 1,700 attacks; version 6.1.1 adds a capability check.

Jun 1, 2026
Vulnerability & Exploit · securityweek.com

Belgian Agency Warns of Netlogon Flaw Exploitation; Microsoft Says It Has No Evidence

Belgium’s CCB says attackers are exploiting CVE-2026-41089, a critical Windows Netlogon flaw. Microsoft says it has no supporting evidence. The flaw was patched in May and could allow unauthenticated remote code execution on a domain controller.

Jun 1, 2026
Vulnerability & Exploit · bleepingcomputer.com

Belgium Warns of Active Exploitation of Critical Windows Netlogon Flaw

Belgium’s cybersecurity authority says CVE-2026-41089, a critical Windows Netlogon flaw, is being actively exploited. Microsoft patched it in May 2026; the flaw could enable remote code execution on supported Windows Server domain controllers.

Jun 1, 2026
Vulnerability & Exploit · securityweek.com

CIFSwitch Linux Kernel Flaw Could Give Low-Privileged Users Root Access

CIFSwitch affects Linux’s CIFS subsystem and cifs-utils: crafted key descriptions can lead root-run cifs.upcall to switch namespaces and load attacker-controlled NSS code. Distribution fixes are available; exposure varies by distro.

Jun 1, 2026
Vulnerability & Exploit · securityweek.com

Palo Alto Networks PAN-OS Vulnerability Exploited Four Days After Disclosure

Rapid7 says attackers began exploiting CVE-2026-0257 in PAN-OS four days after disclosure, using forged cookies against GlobalProtect. Palo Alto Networks reports limited attempts; patches are available, and Rapid7 released a PoC and IoCs.

Jun 1, 2026
Vulnerability & Exploit · bleepingcomputer.com

WP Maps Pro Flaw Exploited in Attempts to Create WordPress Admin Accounts

CVE-2026-8732 lets unauthenticated attackers create WordPress administrator accounts through WP Maps Pro 6.1.0 and older. Defiant reported blocking over 3,600 exploit attempts in 24 hours; version 6.1.1 fixes the flaw.

May 31, 2026
Vulnerability & Exploit · bleepingcomputer.com

CIFSwitch Linux Flaw Can Give Local Attackers Root on Multiple Distributions

CIFSwitch lets local unprivileged attackers forge CIFS authentication requests and potentially gain root through a vulnerable cifs-utils workflow. A kernel patch validates request origins; disabling CIFS or user namespaces can reduce exposure.

May 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

Palo Alto Warns CVE-2026-0257 Is Being Exploited to Bypass GlobalProtect Authentication

Palo Alto says CVE-2026-0257 is being exploited against unpatched GlobalProtect devices. Rapid7 reports successful exploitation at multiple customers using forged authentication override cookies; admins should patch or disable the feature.

May 30, 2026
Vulnerability & Exploit · securityweek.com

PoC Published for Critical Flowise RCE Vulnerability

Obsidian Security published PoC code for CVE-2026-40933, which can trigger command execution when a crafted chatflow is imported into vulnerable self-hosted Flowise instances. Flowise Cloud is reportedly unaffected.

May 30, 2026
Vulnerability & Exploit · thehackernews.com

CVE-2026-0257 Authentication Bypass in PAN-OS Exploited in the Wild

Palo Alto Networks reports limited exploit attempts against unpatched devices, while Rapid7 observed successful exploitation in customer environments. CVE-2026-0257 can enable unauthorized GlobalProtect VPN connections; urgent patching or temporary mitigations are urged

May 30, 2026
Vulnerability & Exploit · thehackernews.com

Researchers Detail ChatGPhish, a Phishing Risk in ChatGPT Web Summaries

Researchers say ChatGPhish can make ChatGPT render attacker-controlled links and auto-fetch images from summarized pages, potentially exposing user metadata and presenting phishing content. The article also surveys attacks targeting AI coding agents and other AI tools.

May 30, 2026
Vulnerability & Exploit · securityweek.com

Chrome 148 Update Fixes 151 Vulnerabilities, Including 22 Critical Flaws

Google's Chrome 148 update fixes 151 vulnerabilities, including 22 critical flaws. The article lists patched versions for Windows, macOS, and Linux and says many critical issues involve use-after-free bugs.

May 29, 2026
Vulnerability & Exploit · rapid7.com

Rapid7 Details Unpatched Gogs RCE via Git Rebase Argument Injection

Rapid7 reports a critical argument-injection flaw in Gogs that can let an authenticated user execute commands through the rebase-before-merging workflow. Gogs 0.14.2 and 0.15.0+dev were confirmed affected; no patch was available at publication.

May 29, 2026
Vulnerability & Exploit · thehackernews.com

Rapid7 Discloses Unpatched Gogs RCE Flaw Exploitable by Authenticated Users

Rapid7 disclosed an unpatched Gogs flaw rated CVSS 9.4 that can let authenticated users execute code by injecting the --exec flag through a malicious branch name during rebase merging. It affects supported platforms; Rapid7 released a Metasploit module.

May 29, 2026
Vulnerability & Exploit · bleepingcomputer.com

Gogs Zero-Day Flaw Allows Authenticated Users to Execute Remote Code

Rapid7 says an unpatched argument-injection flaw in Gogs 0.14.2 and 0.15.0+dev lets authenticated non-admin users execute code remotely. Default open registration may let attackers create accounts on exposed servers.

May 28, 2026
Vulnerability & Exploit · securityweek.com

Pretalx Stored XSS Could Compromise Conference Organizers’ Accounts

Researchers disclosed CVE-2026-41241, a stored XSS flaw in Pretalx that could let a registered speaker trigger JavaScript when an organizer searches for a submission. Pretalx patched the vulnerability in version 2026.1.0.

May 27, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited LiteSpeed cPanel Flaw

CISA ordered U.S. federal agencies to patch CVE-2026-48172 by May 29. The actively exploited LiteSpeed cPanel plugin flaw can let unauthenticated attackers run scripts as root; LiteSpeed released updates.

May 27, 2026
PreviousPage 48 of 65 Next
© 2026 cyber.hendryadrian.com