cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · thehackernews.com

Gitea Docker Flaw CVE-2026-20896 Probed After Disclosure; Fix Available

Sysdig observed an initial probing attempt targeting CVE-2026-20896 in Gitea Docker images. The flaw could allow unauthenticated user impersonation when reverse-proxy authentication is enabled; affected versions through 1.26.2 were fixed in 1.26.3.
Jul 6, 2026
Vulnerability & Exploit · bleepingcomputer.com

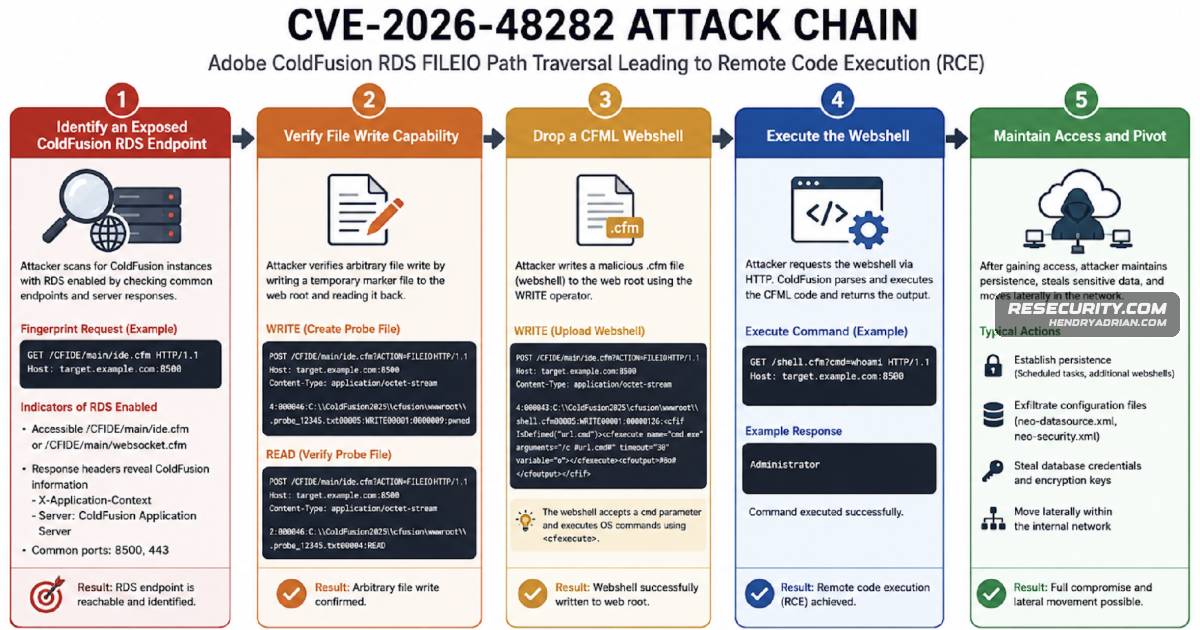
Adobe ColdFusion CVE-2026-48282 Exploited in the Wild

CCCS says attackers are exploiting CVE-2026-48282, a maximum-severity ColdFusion flaw that can enable unauthenticated remote code execution. Adobe released patches; nearly 800 instances are exposed online, though their status is unclear.

Jul 6, 2026
Vulnerability & Exploit · securityweek.com

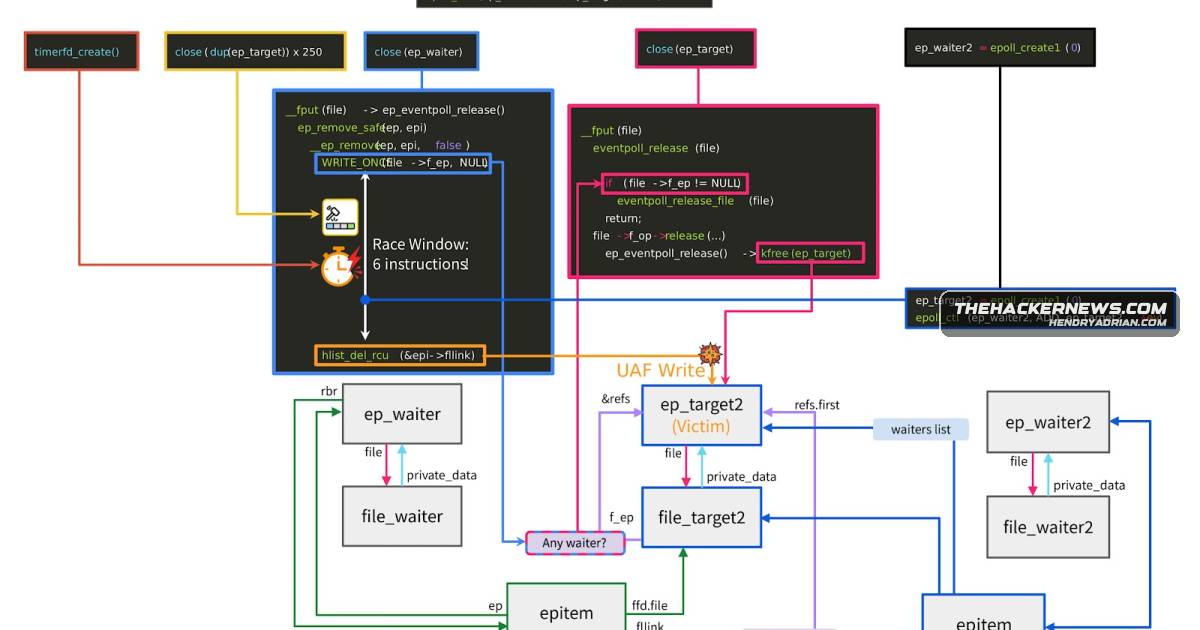
PoC Exploit Released for Linux Bad Epoll Root-Access Vulnerability

A public PoC for Linux kernel vulnerability CVE-2026-46242, Bad Epoll, can leak kernel memory and gain root privileges. Linux distributions based on kernel 6.4 or newer and Pixel 10 devices running kernel 6.6 are affected.

Jul 6, 2026
Vulnerability & Exploit · resecurity.com

Adobe ColdFusion CVE-2026-48282 Enables Unauthenticated File Writes and Potential RCE

Resecurity reports active exploitation of CVE-2026-48282, a ColdFusion RDS FILEIO path-traversal flaw enabling unauthenticated arbitrary file writes and potential RCE. CISA added it to KEV; Adobe fixed it in ColdFusion 2025 Update 10 and 2023 Update 21.

Jul 6, 2026
Vulnerability & Exploit · thehackernews.com

Bad Epoll Linux Kernel Flaw Can Give Local Users Root on Linux and Android

Bad Epoll (CVE-2026-46242) is a Linux kernel use-after-free that can let local users gain root on Linux systems and some Android devices. An exploit reportedly succeeded about 99% in tests; an upstream fix is available.

Jul 3, 2026
Vulnerability & Exploit · thehackernews.com

runZero Discloses Seven FatFs Flaws Affecting Embedded Devices

runZero disclosed seven FatFs vulnerabilities that malformed storage media or firmware files can trigger in embedded devices. Public proof-of-concept material is available; only the GPT-mount issue is fixed upstream, and no attacks had been reported as of July 1.

Jul 3, 2026
Vulnerability & Exploit · securityweek.com

Cursor AI Editor Flaws Could Enable OS-Level Remote Code Execution

Cato reported two critical Cursor flaws, CVE-2026-50548 and CVE-2026-50549, that could enable OS-level RCE through sandbox and symlink bypasses. Both were patched in Cursor 3.0.

Jul 3, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Warns of Active Exploitation of Microsoft SharePoint RCE Flaw

CISA says attackers are exploiting CVE-2026-45659, a SharePoint RCE flaw affecting authenticated users with Site Member permissions. Microsoft released fixes, and CISA added the CVE to its KEV catalog and ordered federal agencies to patch.

Jul 2, 2026
Vulnerability & Exploit · securityweek.com

NetScaler CVE-2026-8451 Exploited Within 24 Hours of Disclosure

Lupovis reports threat actors probed exposed NetScaler appliances and delivered a payload within 24 hours of CVE-2026-8451’s disclosure. The unauthenticated memory-disclosure flaw affects appliances configured as SAML IdP.

Jul 2, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Confirms Active Exploitation of Unified CM Flaw CVE-2026-20230

Cisco confirmed active exploitation of CVE-2026-20230, an unauthenticated SSRF flaw in Unified CM. It recommends upgrading to a fixed release or disabling WebDialer temporarily; Shadowserver tracks over 200 exposed instances.

Jul 2, 2026
Vulnerability & Exploit · securityweek.com

Cisco Confirms Active Exploitation of Unified CM Vulnerability

Cisco says CVE-2026-20230, an SSRF flaw in Unified CM and Unified CM SME, is being exploited. Only appliances with WebDialer enabled are vulnerable; Cisco urges customers to upgrade to a fixed release.

Jul 2, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited SharePoint RCE Flaw to KEV Catalog

CISA added SharePoint Server flaw CVE-2026-45659 to its KEV catalog after finding active exploitation. Microsoft fixed it in May 2026; FCEB agencies are advised to patch by July 4.

Jul 2, 2026
Vulnerability & Exploit · cyberscoop.com

Researchers Observe Exploitation of Critical Oracle E-Business Suite Flaw

Defused researchers observed six attempts to exploit Oracle E-Business Suite flaw CVE-2026-46817 in two hours. The activity came from one IP before a public proof of concept; Shadowserver found about 950 potentially vulnerable instances.

Jul 1, 2026
Vulnerability & Exploit · bleepingcomputer.com

Defused Reports Oracle E-Business Flaw Exploitation as 950 Instances Are Tracked Exposed

Defused reports observing exploitation of CVE-2026-46817, an unauthenticated takeover flaw in Oracle E-Business Suite. Oracle issued a patch in its May 2026 update; Shadowserver tracks about 950 exposed instances, with patched status unknown.

Jul 1, 2026
Vulnerability & Exploit · thehackernews.com

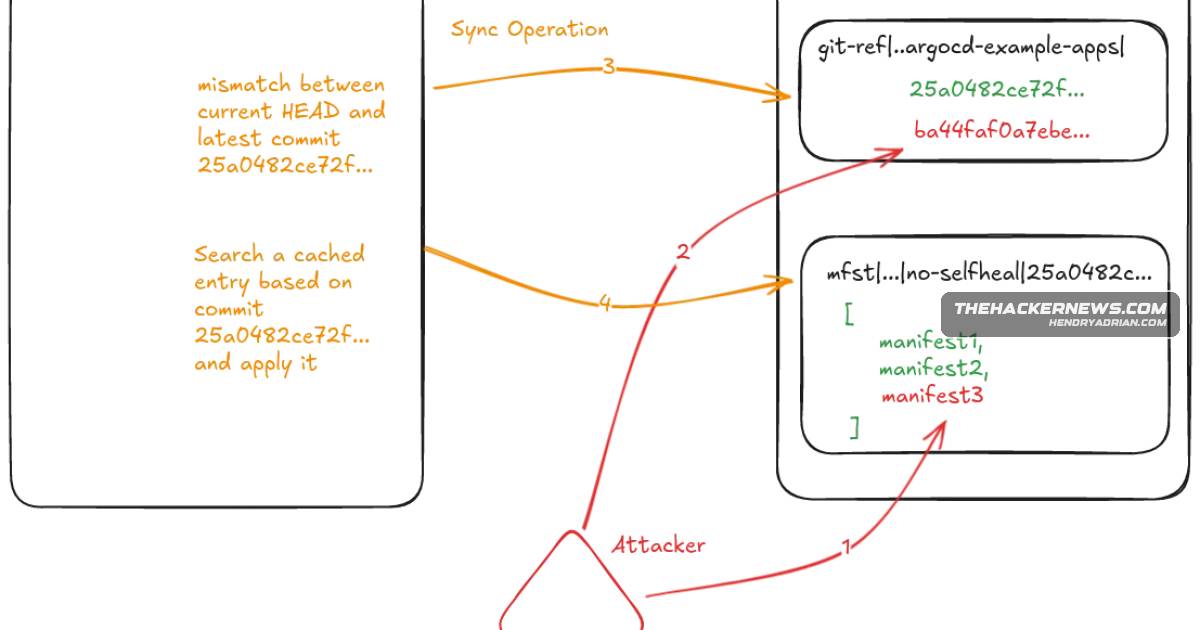
Unpatched Argo CD Flaw Could Enable Code Execution and Kubernetes Cluster Takeover

Synacktiv says an unpatched Argo CD repo-server flaw lets unauthenticated requests execute attacker-controlled scripts if its internal gRPC port is reachable, potentially enabling cluster takeover via Redis cache poisoning. No fix is available; network isolation is the

Jul 1, 2026
Vulnerability & Exploit · thehackernews.com

CVE-2026-8037 LoadMaster Exploitation Attempts Failed, eSentire Reports

eSentire observed failed exploitation attempts beginning June 29, 2026, against CVE-2026-8037 in Progress Kemp LoadMaster. The unauthenticated command-injection flaw has a public PoC; successful exploitation could enable arbitrary command execution.

Jul 1, 2026
Vulnerability & Exploit · securityweek.com

Adobe Patches Critical ColdFusion and Campaign Classic Vulnerabilities

Adobe patched 11 ColdFusion vulnerabilities and one Campaign Classic flaw, including vulnerabilities that could enable code execution. No public exploits are known to Adobe; users are advised to update.

Jul 1, 2026
Vulnerability & Exploit · securityweek.com

Citrix Patches NetScaler Flaws, Including HTTP/2 Bomb Vulnerability

Citrix released NetScaler ADC and Gateway updates addressing six vulnerabilities, including the HTTP/2 Bomb DoS flaw. watchTowr says CVE-2026-8451 can expose restricted memory under specific configuration and request conditions.

Jul 1, 2026
Vulnerability & Exploit · cyberscoop.com

Citrix Patches Six NetScaler Flaws, Including SAML Memory Disclosure Bug

Citrix disclosed six NetScaler ADC and Gateway vulnerabilities. CVE-2026-8451 is a high-severity memory disclosure flaw involving SAML parsing; one HTTP/2-related fix requires a manual configuration change. No confirmed exploitation was reported at disclosure.

Jul 1, 2026
Vulnerability & Exploit · securityweek.com

CISA Says BlueHammer Flaw Used in Ransomware Campaigns

CISA says the BlueHammer Microsoft Defender flaw (CVE-2026-33825) has been used in ransomware campaigns. Huntress reported pre-patch zero-day exploitation; Microsoft has not confirmed in-the-wild exploitation, and the ransomware group is unknown.

Jun 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Says Ransomware Gangs Are Exploiting Windows BlueHammer Flaw

CISA says ransomware gangs are exploiting BlueHammer (CVE-2026-33825), a Microsoft Defender local privilege-escalation flaw previously exploited as a zero-day. Microsoft patched it April 14; CISA added it to KEV and flagged ransomware use.

Jun 30, 2026
Vulnerability & Exploit · securityweek.com

Actively Exploited SimpleHelp OIDC Flaw Enables Malware Delivery

CVE-2026-48558 lets attackers forge OIDC tokens to gain technician access to SimpleHelp servers. An observed attack deployed TaskWeaver and Djinn Stealer. SimpleHelp fixed the flaw in versions 5.5.16 and 6.0 RC2.

Jun 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

Attackers Exploit Critical Oracle E-Business Suite Flaw, Defused Reports

Defused reports observing attempts to exploit CVE-2026-46817, an unauthenticated HTTP takeover flaw in Oracle E-Business Suite's Oracle Payments File Transmission component. Oracle issued a patch in its May 2026 update.

Jun 29, 2026
Vulnerability & Exploit · securityweek.com

DirtyClone Linux Kernel Flaw Can Enable Local Root Access

JFrog details DirtyClone (CVE-2026-43503), a Linux kernel flaw that can enable local privilege escalation. Protection requires the complete chain of fixes; affected systems include some Debian, Fedora and Ubuntu configurations.

Jun 29, 2026
PreviousPage 43 of 65 Next
© 2026 cyber.hendryadrian.com